

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
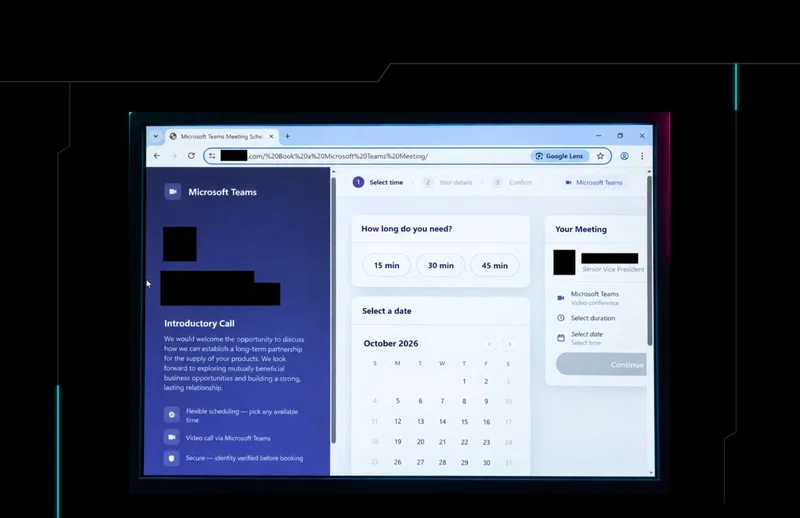
Threat actors used a convincing Microsoft Teams meeting-booking lure to conceal device code phishing and trick victims into authorizing attacker access.
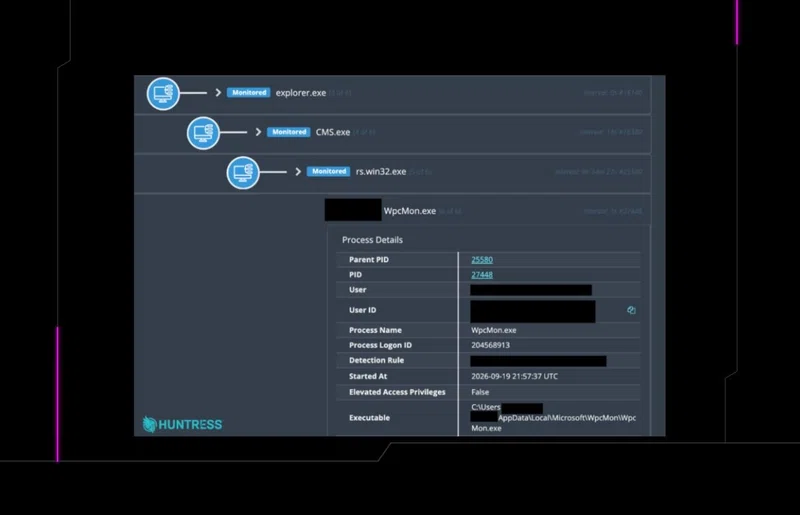
Attackers compromised camera management software to deploy malware, establish persistence, and beacon to C2. Huntress breaks down the attack chain and IOCs.
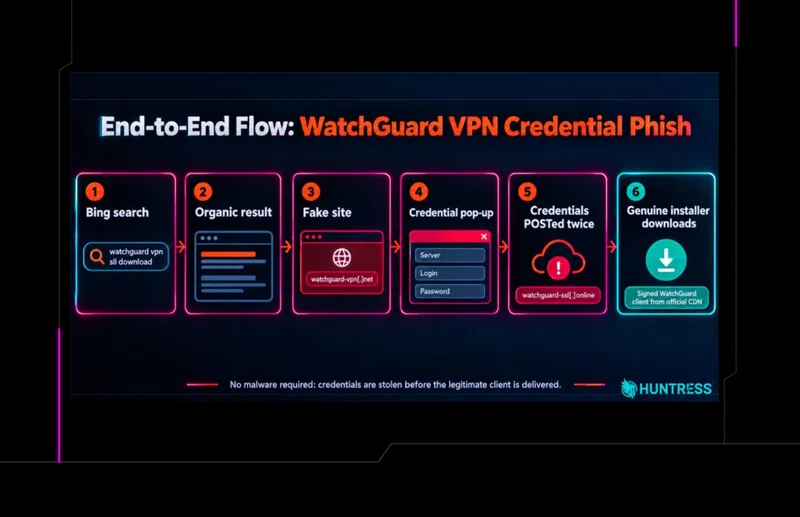
A fake WatchGuard VPN download site steals SSL VPN credentials, then serves the real signed client. Learn how it works and how to spot it.
How Huntress researchers reconstructed an Akira ransomware attack using Registry artifacts, Akira logs, and other post-compromise evidence.
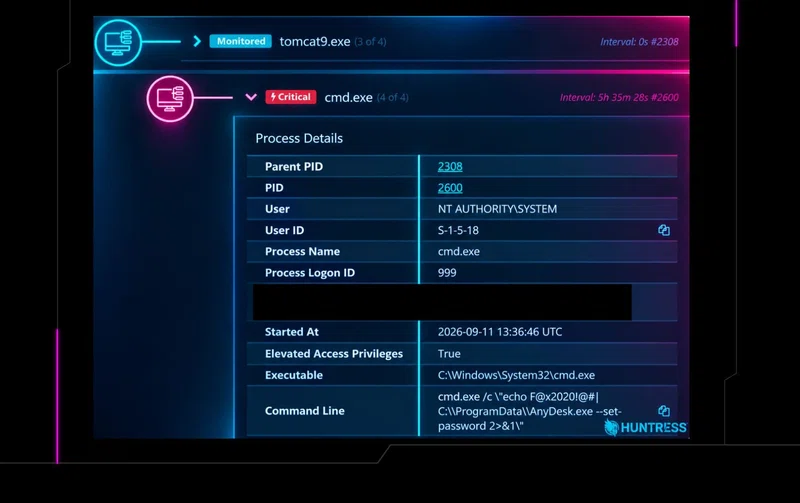
Threat actors exploited Samsung MagicINFO to install AnyDesk, disable Defender, and compile a Monero miner directly on a victim endpoint. Learn the detection signals.
Huntress has recently seen two incidents involving Settra, a ransomware variant that was first publicly reported in June 2026.

Huntress is tracking a pattern across multiple customer environments where rogue ScreenConnect clients repeatedly spawn the Windows Script Host to execute a series of four VBScript files.
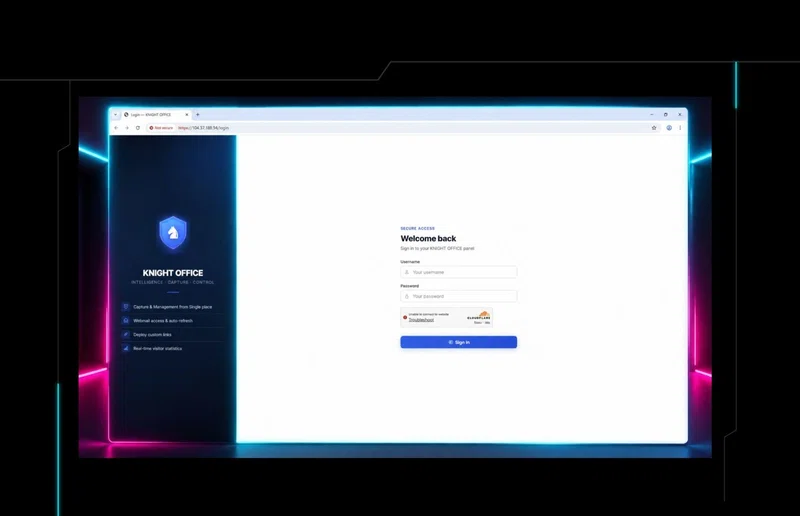
An inside look at Knight Office, a newly discovered AiTM phishing kit featuring custom control panels, Cloudflare Turnstile, and M365 Token theft.
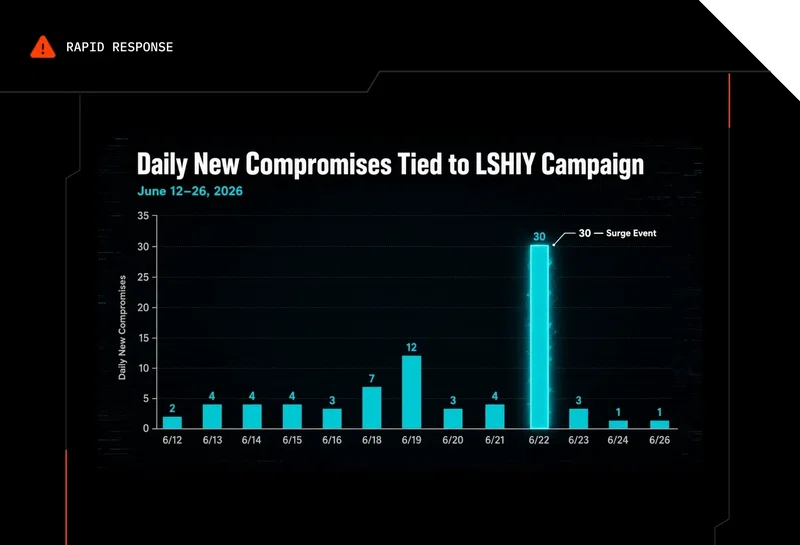
Huntress is seeing an ongoing password spray attack against Microsoft Azure CLI that originates from an IPv6 address range controlled by LSHIY LLC.
Huntress analyzed a credential dumping attack where threat actors disabled Defender, killed monitoring tools, and used Mimikatz to steal credentials.
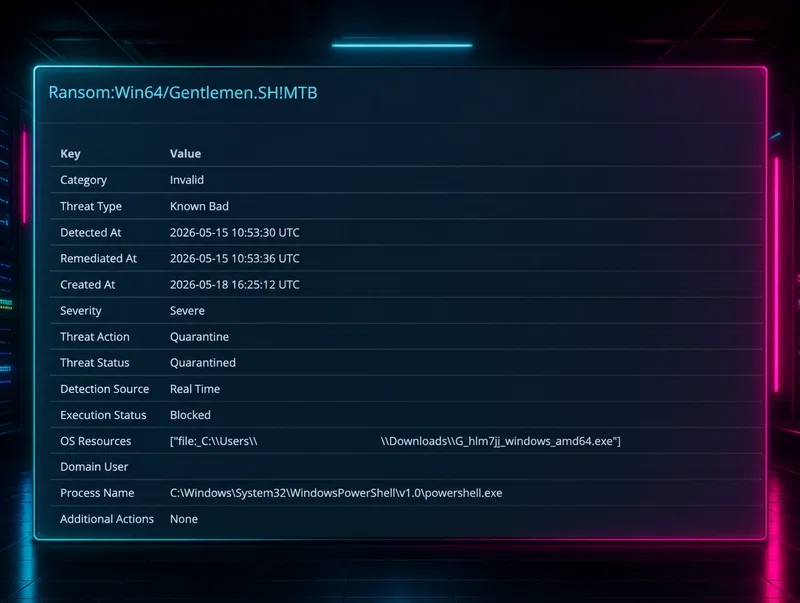
Two recent incidents involving The Gentlemen ransomware show the use of defense evasion tactics, including logs being cleared and attempts to add antivirus exclusions.
A recent investigation into a NightSpire ransomware incident found significant variations in TTPs—including the use of "trucked-in" non-native tools like Chrome Remoting Desktop and MEGASync—which suggests affiliate involvement and demonstrates that IoCs aren't static, regardless of the group's RaaS status.
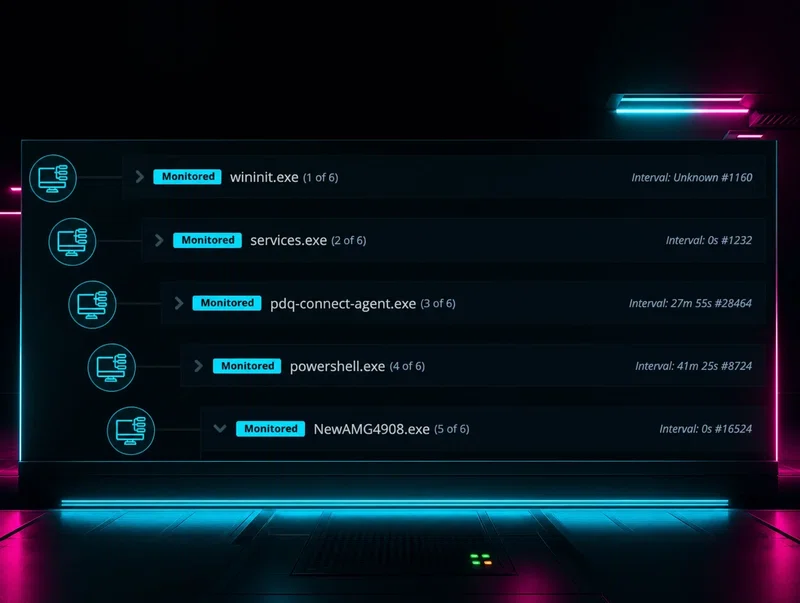
It's not just that attackers abuse RMM tools. They stack multiple ones in the same attack. Huntress documents several incidents where threat actors chained RMM tools for layered persistence.
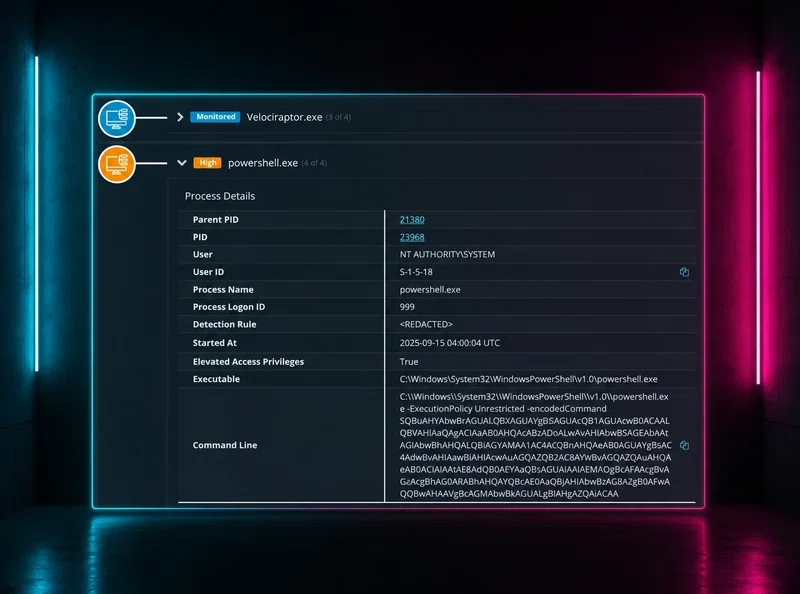
The threat actors from Part I weren't done. Part II tracks what happened after WSUS exploitation put a legitimate forensic tool in the wrong hands and how Huntress responded.
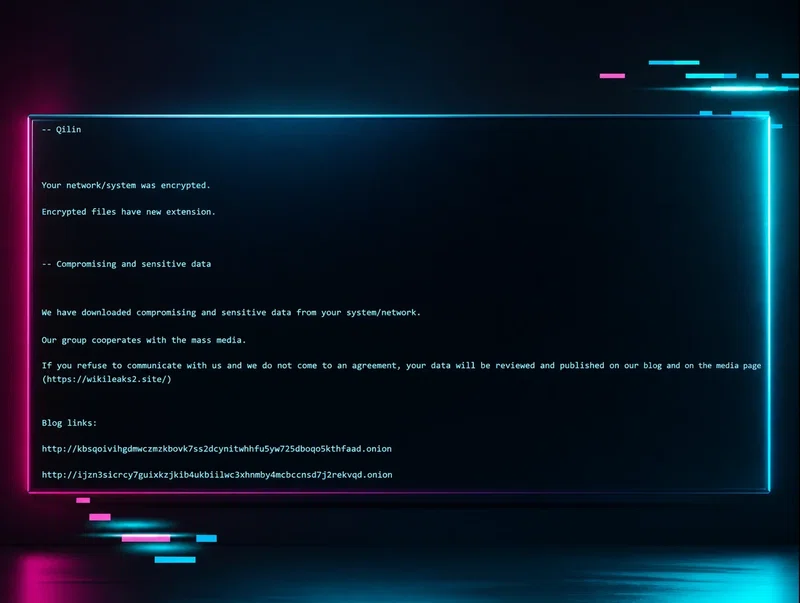
Investigating a Qilin ransomware attack with limited visibility is like piecing together a crime scene through a pinhole. Huntress shows what you can still figure out and what you'll miss.

