
Identity Security
Most breaches don't break in. They log in. Identity Security covers the modern identity attack surface: identity threat detection and response (ITDR), business email compromise, Microsoft 365 compromise, OAuth attacks, credential theft, MFA gaps, and rogue app detection. Learn about both the threats and the Huntress capabilities built to stop them.
The Latest Identity Security Blog Posts

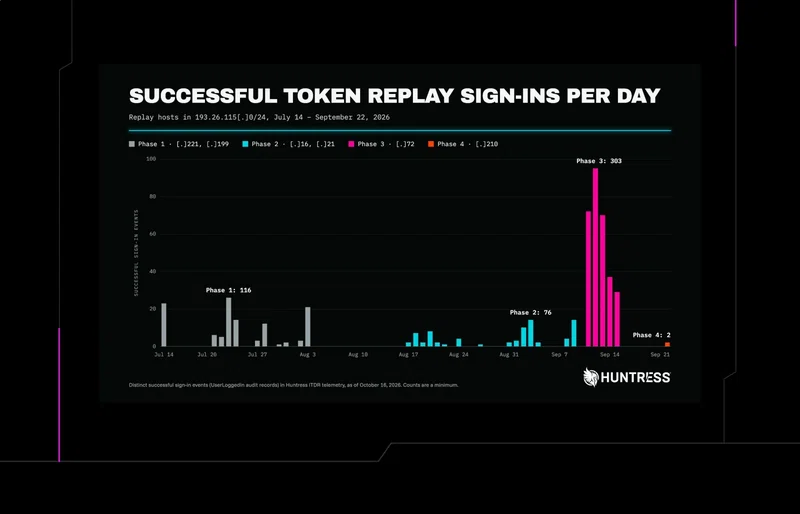
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
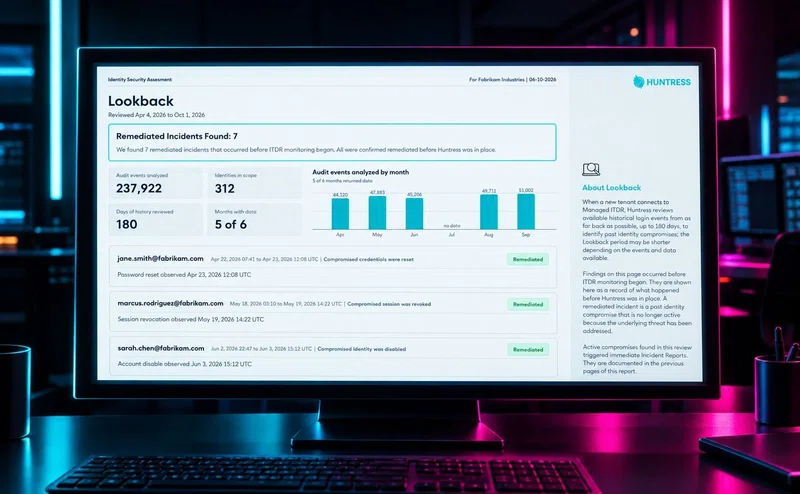
Introducing ITDR Lookback: Find Out Who Was in Your Microsoft 365 Tenant Before You Were
ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Passkeys Raise the Bar. Here’s Where Attackers Can Still Get In.
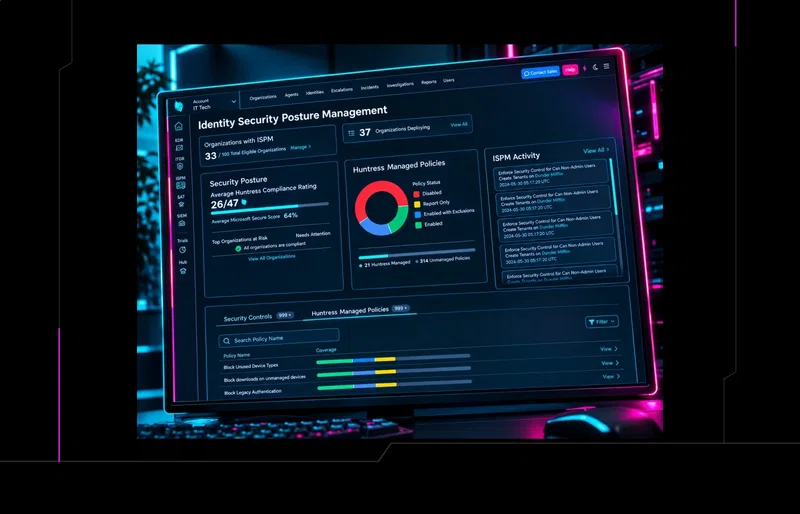
Fully Managed or Modified: Pick How Huntress Hardens Your Microsoft 365 Environment with Managed ISPM
Stealing OAuth Tokens Through Microsoft's Front Door
Inside Knight Office, a New M365 AiTM Phishing Kit
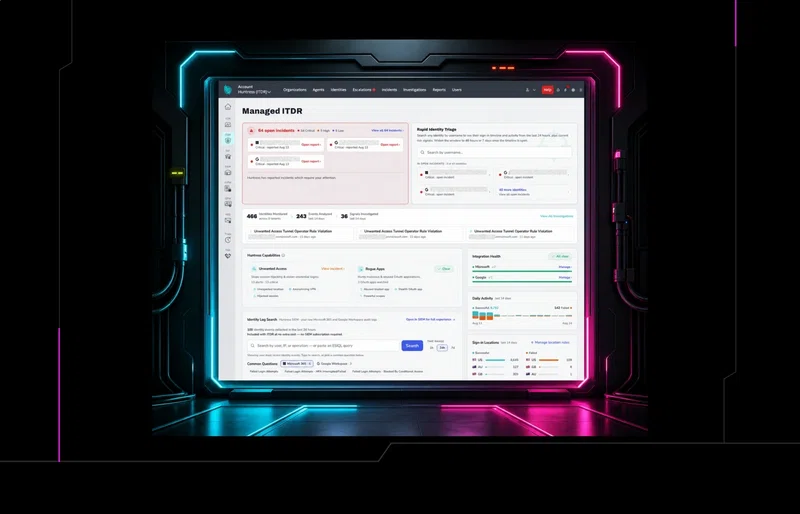
The New Huntress Managed ITDR Dashboard: More Context. Faster Answers.
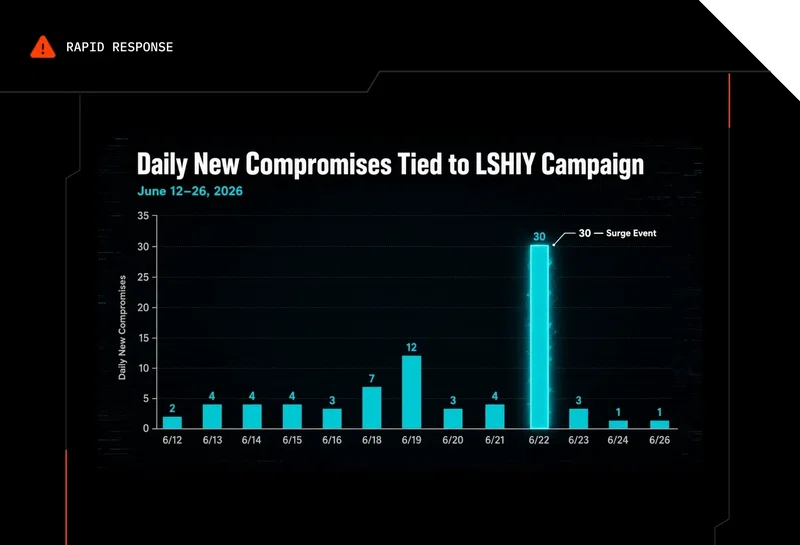
No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
Hook, Line, and Token: Anatomy of the Kali365 / Octopi365 Phishing-as-a-Service Kit
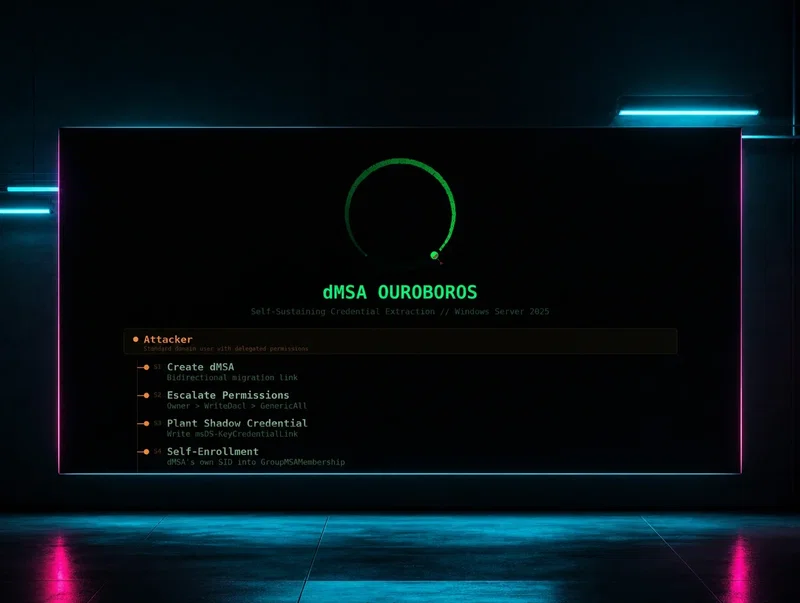
dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025
A fully patched Windows Server 2025 domain is vulnerable to dMSA Ouroboros—a self-sustaining credential extraction technique requiring only standard delegated permissions. Learn how it works, why remediation fails, and how to detect it.
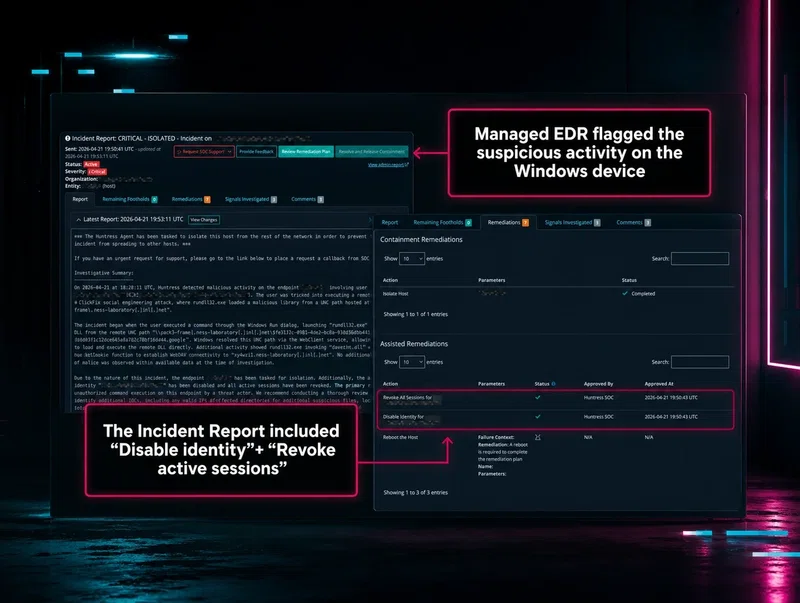
How Unified EDR and ITDR Stop Attacks Before They Spread
Huntress EDR/ITDR Correlations automatically stop infostealer-driven attacks by immediately linking an endpoint compromise to the compromised cloud identity, allowing for a single, coordinated response before stolen credentials can be reused.
