

Microsoft solutions already go far. Huntress takes them further.
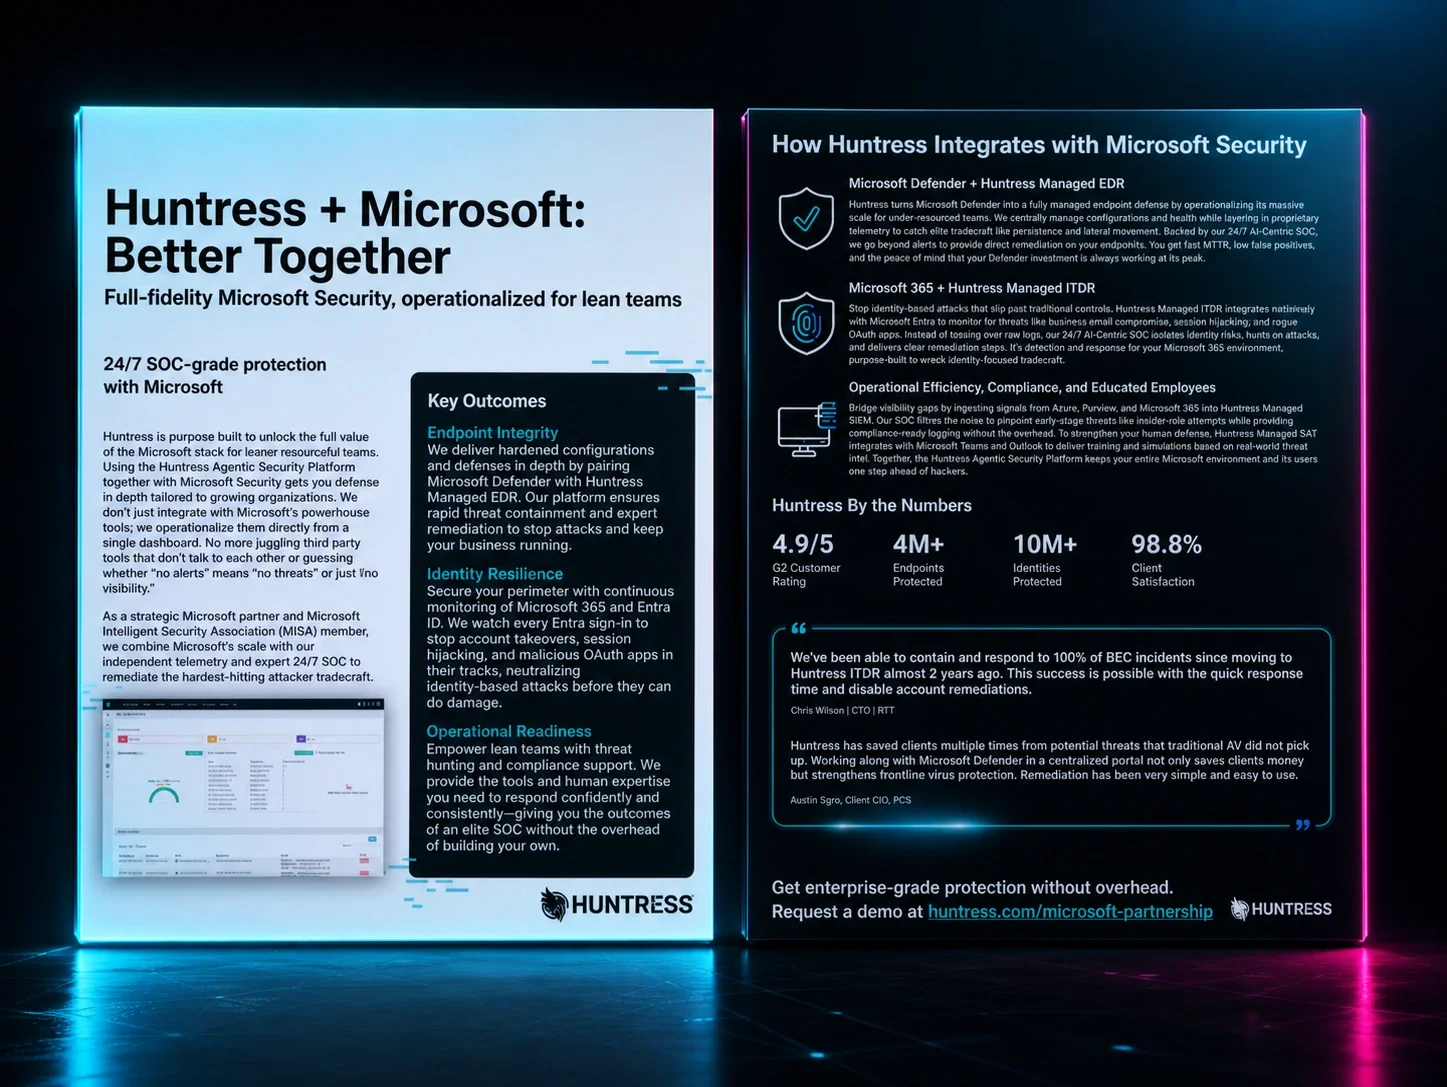
Microsoft environments have more security depth than most teams have had the time or support to fully unlock. Huntress is built to help organizations run Microsoft 365 and Microsoft Security at full power, with tradecraft-focused detection and a 24/7 SOC that strengthens protection without adding more work for teams.
A partner purpose-built to work with Microsoft Security
Huntress is a Microsoft-verified SMB Solution and a proud member of the Microsoft Intelligent Security Association (MISA).
This is a clear reflection of our partnership. Microsoft wants customers to get more from what they’ve built, and Huntress makes that happen.
Microsoft doesn’t build what Huntress builds, and Huntress doesn’t build what Microsoft builds. That’s why the two are designed to work together, unlocking more value from Microsoft environments while giving teams a round-the-clock SOC that can drive response and remediation through to the finish.
Microsoft and Huntress can improve your workflow, no matter who you are
Microsoft solutions come with a lot built in, but many teams don’t have the extra time or resources needed to unlock the full power on their own. That’s where Huntress fits. Built to work alongside Microsoft, Huntress gives MSPs, resellers, and in-house IT teams the operational layer needed to turn Microsoft security signals into action without bolting on a disconnected stack or adding headcount.

Get security coverage that runs without requiring more from a team that's already doing everything else.
Huntress serves as the force multiplier for internal IT, transforming Microsoft Security into an active, SOChuman-led defense that reduces response times and clarifies security postures.

MSPs
Run better security across client environments without scaling up your internal security headcount.
Huntress helps reduce tool sprawl, adds 24/7 SOC coverage, and makes it easier to support Microsoft-based environments at scale.
Resellers
Bridge the gap between owning powerful tools and operating the defense.
Huntress doesn't replace customers’ Microsoft stack, but operationalizes it, allowing them to realize the vision of a consolidated stack.
Why teams add Huntress to Microsoft 365 and Microsoft Security
Microsoft provides strong security signals across endpoints and identities. Huntress builds on those signals by layering in tradecraft-focused telemetry and actively hunting for persistent footholds. We also lay “traps” like ransomware canaries to help surface threats before damage can spread. Plus, our 24/7 AI-centric, human-led SOC investigates, responds, and remediates threats with speed and agility. The result is a stronger Microsoft security operation, not a separate stack bolted on beside it.


How it works
1. Microsoft surfaces rich security signals across endpoints and identities.
Defender, Entra, and Microsoft 365 show you what’s happening across the environment.
2. Huntress starts the hunt. We ingest and enrich those signals, then layer in our own telemetry.
That adds more context around attacker behavior—from actively hunting for persistent footholds to laying traps like ransomware canaries—so threats are exposed before they can do real damage.
3. The Huntress SOC investigates, prioritizes, and remediates, 24/7.
We help teams figure out what matters now and what can wait. When something serious happens, we help drive the response through to the finish, no matter the time of day.
Strengthen Microsoft environments across endpoints, identities, and logs

Endpoint Integrity
Huntress Managed EDR works with Microsoft Defender AV, as well as Defender for Business and Defender for Endpoint, to enhance endpoint coverage and improve visibility. When something needs containment or remediation, teams can move faster.
Managed ESPM hardens Windows endpoints and reduces attack surfaces.

Identity Resilience
Managed ITDR continuously monitors Microsoft 365 and Entra identities, catching account takeover early, uncovering session hijacking, and spotting malicious OAuth apps before they turn into something worse.
Managed ISPM actively hardens Microsoft 365 environments, addressing identity misconfigurations before attackers can use them.
Operational Readiness
Managed SIEM brings together Microsoft 365, Entra, Defender, Azure, and other log sources so teams can spot trouble sooner and respond with more confidence. Long-term searchable log storage also supports audit, insurance, and compliance needs.
Managed SAT brings training and simulations into Microsoft 365 and Teams to teach users to spot scams and phishing before they let attackers into the business.
What Huntress adds to Microsoft licensing
|
Microsoft 365 license |
Business Standard (<300) |
Business Premium (<300) |
ME3 (300+) |
ME5 (300+) |
|---|---|---|---|---|
|
What Microsoft includes |
Core Microsoft productivity tools with light, built-in security support. |
Strong built-in security perimeter capabilities across identity (Entra P1), endpoint (Defender for Business EDR), and device management (Intune P1). |
Built-in security perimeter capabilities across identity (Entra P1), endpoint (MDE P1—less robust than Defender for Business), device management (Intune P1), and information protection. |
Advanced security and compliance capabilities. |
|
Where teams get stuck |
Core business platform—Microsoft 365—is unmonitored and unprotected. |
Lack the capabilities to deploy and manage the stack 24/7, so value goes underutilized. |
Lack the capabilities to deploy and manage the stack 24/7, so value goes underutilized. |
Advanced features still need steady monitoring and follow-through. |
|
What Huntress adds |
Stronger detection and response on top of Microsoft 365, plus an achievable path into a more mature Microsoft security perimeter. |
Additional tradecraft-focused telemetry, and detection and response for Microsoft 365, Defender AV, and Defender for Business, with a 24/7 SOC behind it all. |
Additional tradecraft-focused telemetry, and detection and response for Microsoft 365 and Defender for Endpoint P1, with a 24/7 SOC behind it all. |
A clearer picture of what matters. Less overlap from extra tools. A response layer that helps close the gap between detection and action. |
|
Recommended path |
Business Standard + Huntress → Business Premium + Huntress |
Business Premium + Huntress |
E3 + Huntress |
E5 + Huntress |
Make the Microsoft solutions that are already in place work harder
Microsoft gives teams a powerful platform for secure productivity. Huntress helps them unlock its full value with expert detection and response running around the clock. If you want to see what that looks like in your environment, let's talk.
More good stuff for Microsoft customers
Frequently asked questions
Microsoft provides powerful security controls, and Huntress provides the expert human team to maximize their potential. Defender is a strong prevention layer, but someone still has to tune it, triage what it flags, and respond when something slips through, especially since attackers don't wait for business hours. The Huntress Agentic Platform provides independent telemetry and detections, and always includes our 24/7 SOC that investigates and responds. It supports you wherever you are on your Microsoft security journey—whether managing Defender AV for standard tiers or ingesting Defender alerts for higher tiers like Business Premium, the Defender Suite for Business Premium and Enterprise Defender suites.
Alongside it. Huntress Managed EDR runs with Microsoft Defender Antivirus, Defender for Business, and Defender for Endpoint, and the Huntress Agent can run on the same device. They're layers, not alternatives. Huntress doesn't sell a standalone antivirus engine, so there's no second AV bill. For supported Windows endpoints, Managed Microsoft Defender comes with Managed EDR at no extra Huntress charge.
Key capabilities the Huntress Agentic Platform delivers that enhance your Microsoft security stack with managed protection:
Our own telemetry and detections. The Huntress Agent brings Persistent Footholds detection, Ransomware Canaries, and malicious process behavior monitoring. These aren't Microsoft alerts with a new coat of paint.
SOC investigation. Our analysts work through what the tools surface, decide what's benign and what's malicious, and write up confirmed threats with next steps.
Response that spans endpoint and identity. When an infostealer lands on a laptop, we connect it to the Microsoft 365 identities on that machine, offering remediations to disable the identity before stolen credentials can be replayed or sold..
Maximized Microsoft license activation and utilization. We build features that turn existing Microsoft capabilities into active prevention:
Conditional Access informed by real attacks: For tenants with Entra ID P1 or higher, when Huntress confirms infrastructure used in an identity attack, Huntress Managed ITDR can turn that intelligence into a blocking Conditional Access policy across eligible, opted-in Microsoft 365 tenants, extending protection from one customer to the broader fleet.
More visibility into Entra applications: Also for Entra ID P1+ tenants, Managed ITDR detects suspicious service-principal sign-ins, provides incident details, and can automatically disable compromised applications.
Faster identity risk discovery: ITDR Lookback reviews up to 180 days of sign-in history for newly onboarded Microsoft 365 tenants, and a new Identity Posture Assessment in Managed ISPM gives partners an actionable view of security gaps and recommended next steps to leverage Conditional Access policy to improve posture.
No license upgrades are required to use the Huntress Agentic Platform. Huntress Managed EDR works with the built-in Defender Antivirus on supported Windows endpoints. Similarly, Managed ITDR works for Entra Free users.
When a customer is licensed for Microsoft Security, through Business Premium, Defender Suite for Business Premium, E3, or E5, Huntress leverages the capabilities and signal built into those products to enhance your defense. If you have paid Defender plans deployed and configured in your tenant, our 24/7 SOC ingests those incidents and alerts as rich context for our investigation and response. What you get from Huntress—the agent, our detections, and SOC expertise—complements and elevates your Microsoft investment at every level.
As part of Managed EDR, the Huntress SOC uses alerts and correlated incidents from the Defender Suite to take action and inform investigations:
Microsoft 365 Business Premium includes Defender for Business. Defender for Office Plan 1, Entra ID Plan 1.
Defender Suite for Business Premium includes Defender for Endpoint Plan 2, Defender for Office 365 P2, Defender for Identity, Defender for Cloud Apps, Entra ID Plan 2.
Microsoft 365 E3 includes Defender for Endpoint Plan 1.
Microsoft 365 E5 includes Defender for Endpoint Plan 2, Defender for Office 365 P2, Defender for Identity, Defender for Cloud Apps, Entra ID Plan 2.
It depends on the Defender capability.
What Huntress manages: On supported Windows endpoints, Huntress centrally manages supported Defender Antivirus configurations, exclusions, scans, protections, and detections, across tenants from one console. You also get visibility into Defender health, policy compliance, tamper protection status, risky exclusions, and detection activity. Capabilities vary by operating system.
What Huntress reads, but doesn't manage: Defender for Business and Defender for Endpoint, Defender Suite for Business Premium. We use them as added telemetry for our SOC.
What stays in Microsoft: Your Microsoft licensing and the Defender for Business and Defender for Endpoint consoles. Defender for Office 365, Mobile Threat Defense, and custom detections are outside our current endpoint integration. Huntress works alongside your Microsoft management tools, not in place of them.
On the identity side, Managed ISPM audits and enforces key Entra settings like MFA, Conditional Access, and admin roles.
The Huntress human-led AI-centric 24/7 SOC. For Microsoft Defender Antivirus, Defender for Business, and Defender for Endpoint, our analysts triage qualifying Medium- and High-severity detections. For Microsoft Defender Suite for Business Premium and Defender Suite (fka E5 Security) the Huntress SOC ingests correlated incidents and leverages for investigations. Lower-severity events help give context to an investigation, but they don't become incidents on their own. Triage or ingestion doesn't mean every detection results in a report; that depends on what the investigation finds and whether there's an active threat.
When we confirm malicious activity, we create an incident report with our findings and recommended next steps. We can also take response actions, depending on your product, configuration, available telemetry, and permissions. For Microsoft 365 identities, that can include disabling a compromised account's sign-in, revoking active sessions, and removing malicious inbox rules.
