
Blog Post
AI, Scripts, Operator - Inside the ConnectWise Attack
Microsoft says an AI agent drove the ConnectWise attack. Huntress telemetry is consistent with that: scripted tooling, steered by an operator.
Microsoft says an AI agent drove the ConnectWise attack. Huntress telemetry is consistent with that: scripted tooling, steered by an operator.
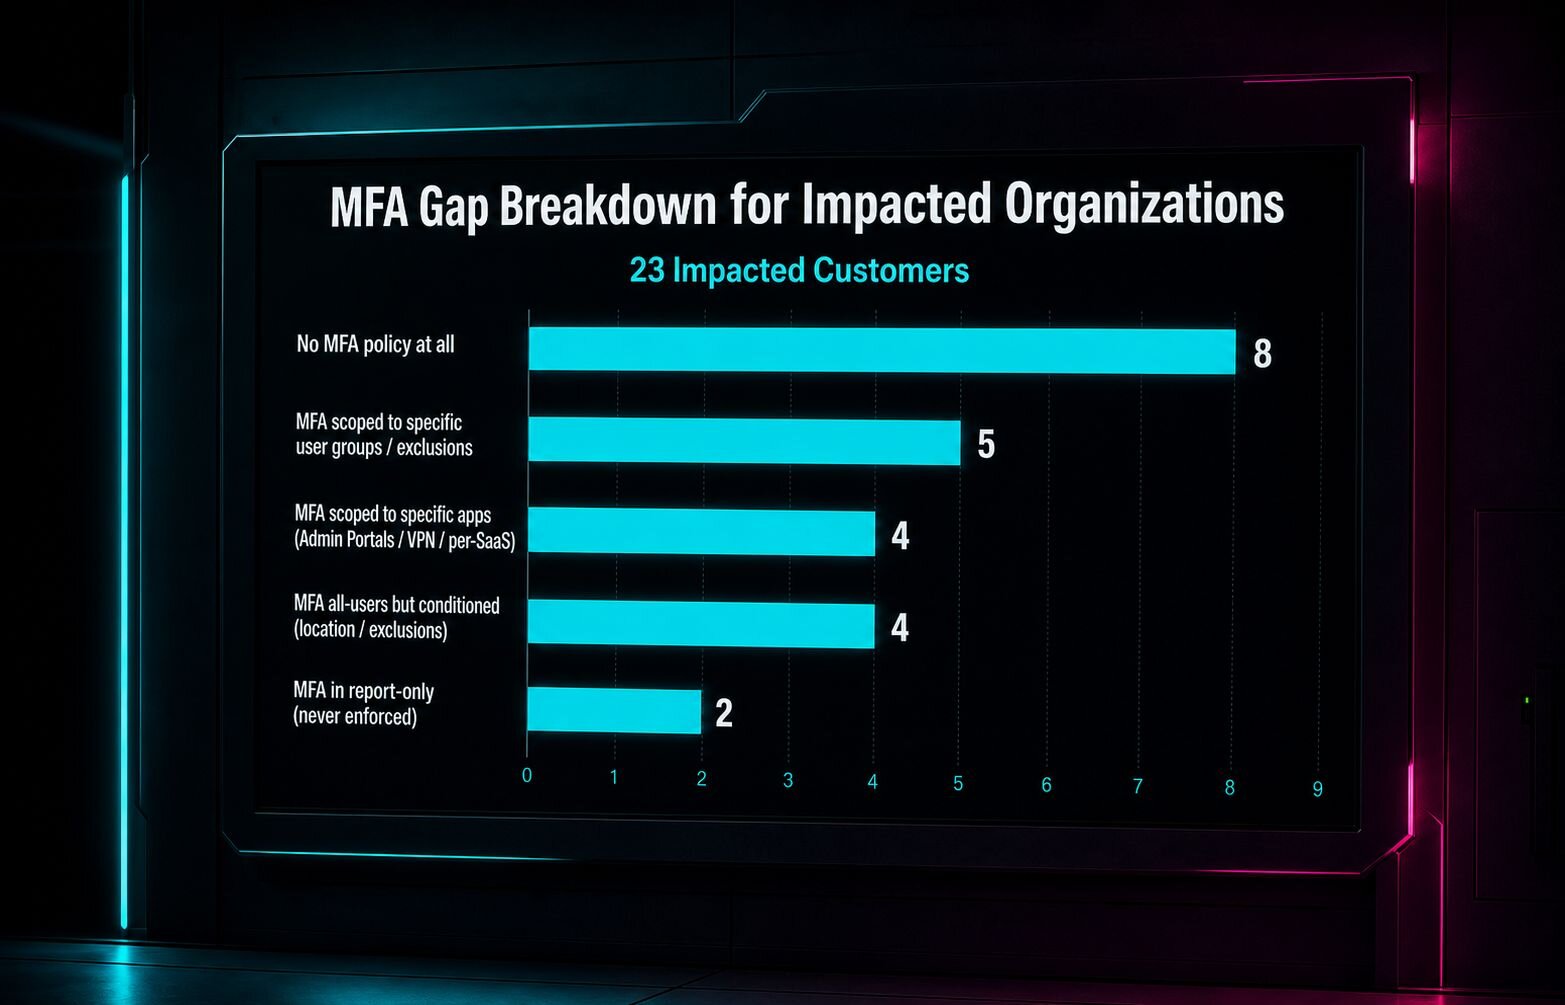
Two Microsoft 365 attacks got through Conditional Access policies that seemed fully configured. Learn what went wrong and how Huntress Managed ISPM catches these gaps first.
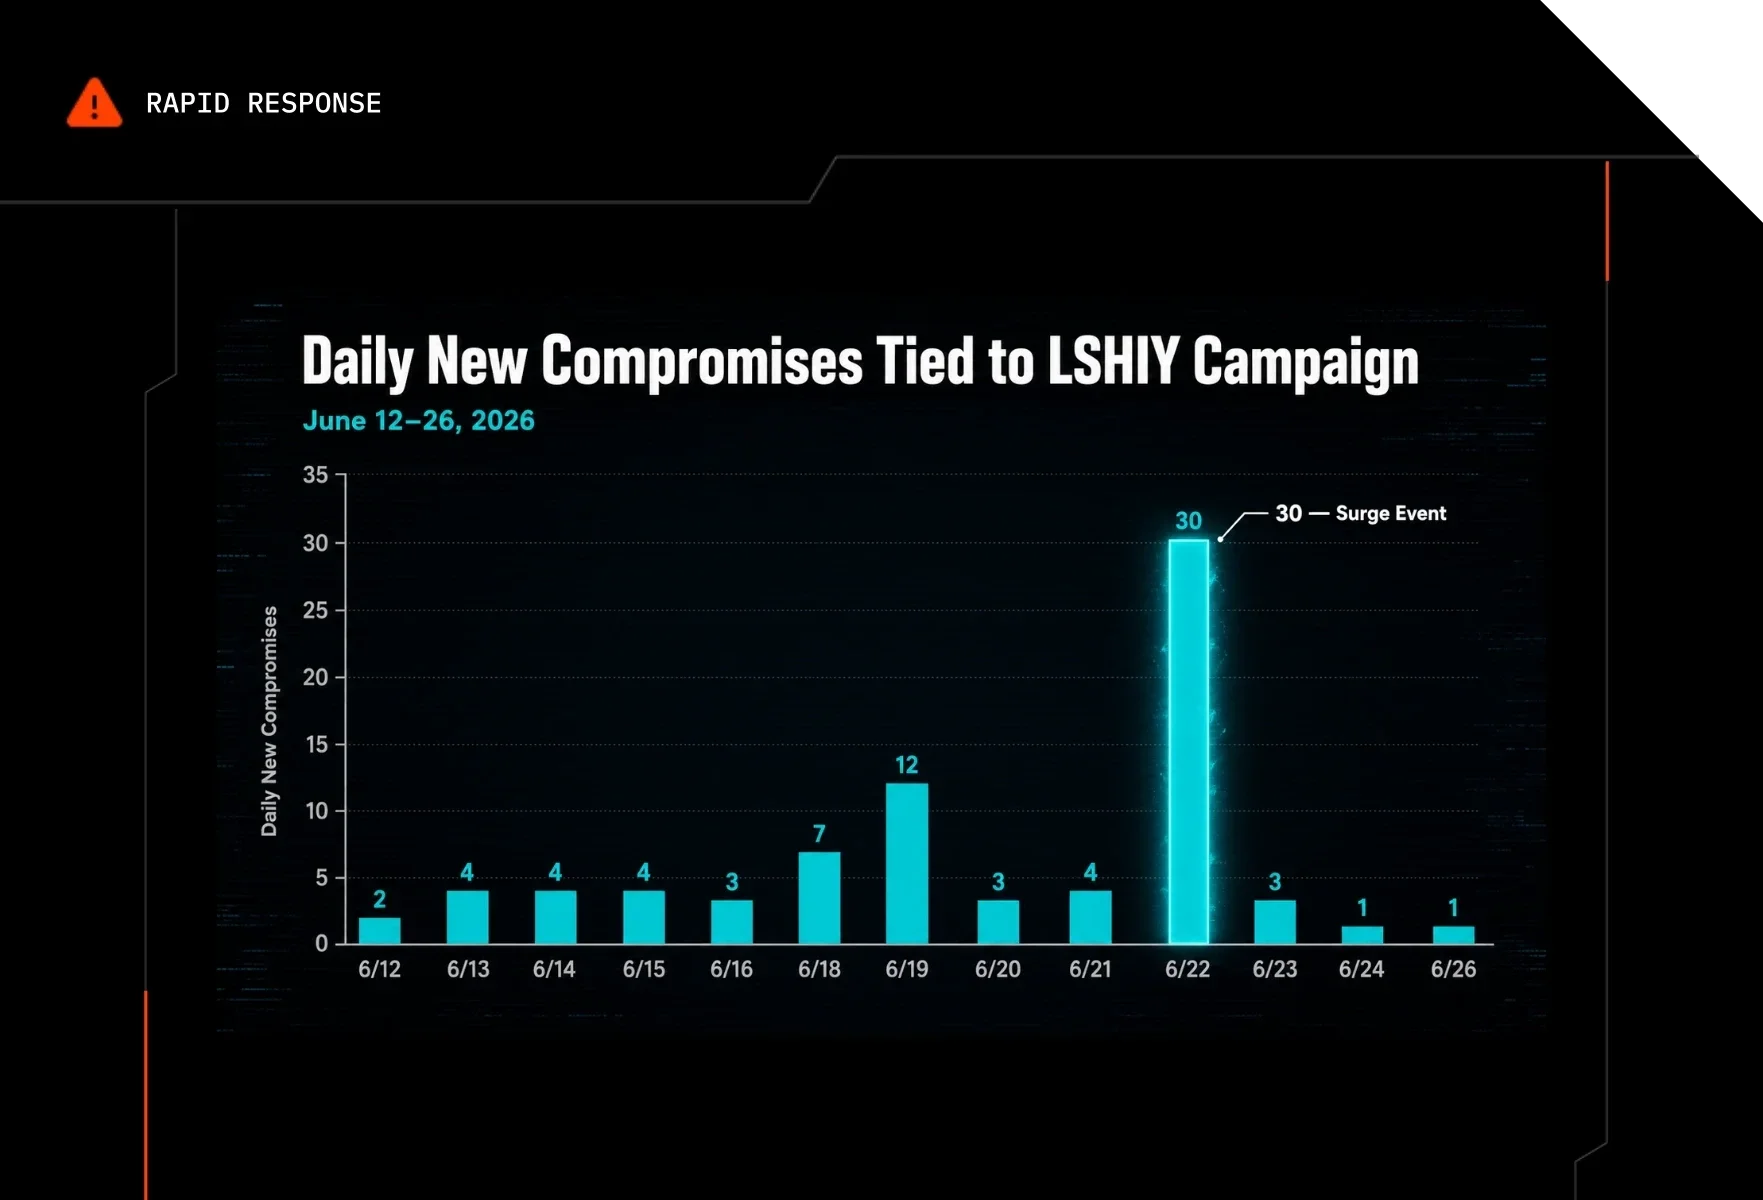
Huntress is seeing an ongoing password spray attack against Microsoft Azure CLI that originates from an IPv6 address range controlled by LSHIY LLC.
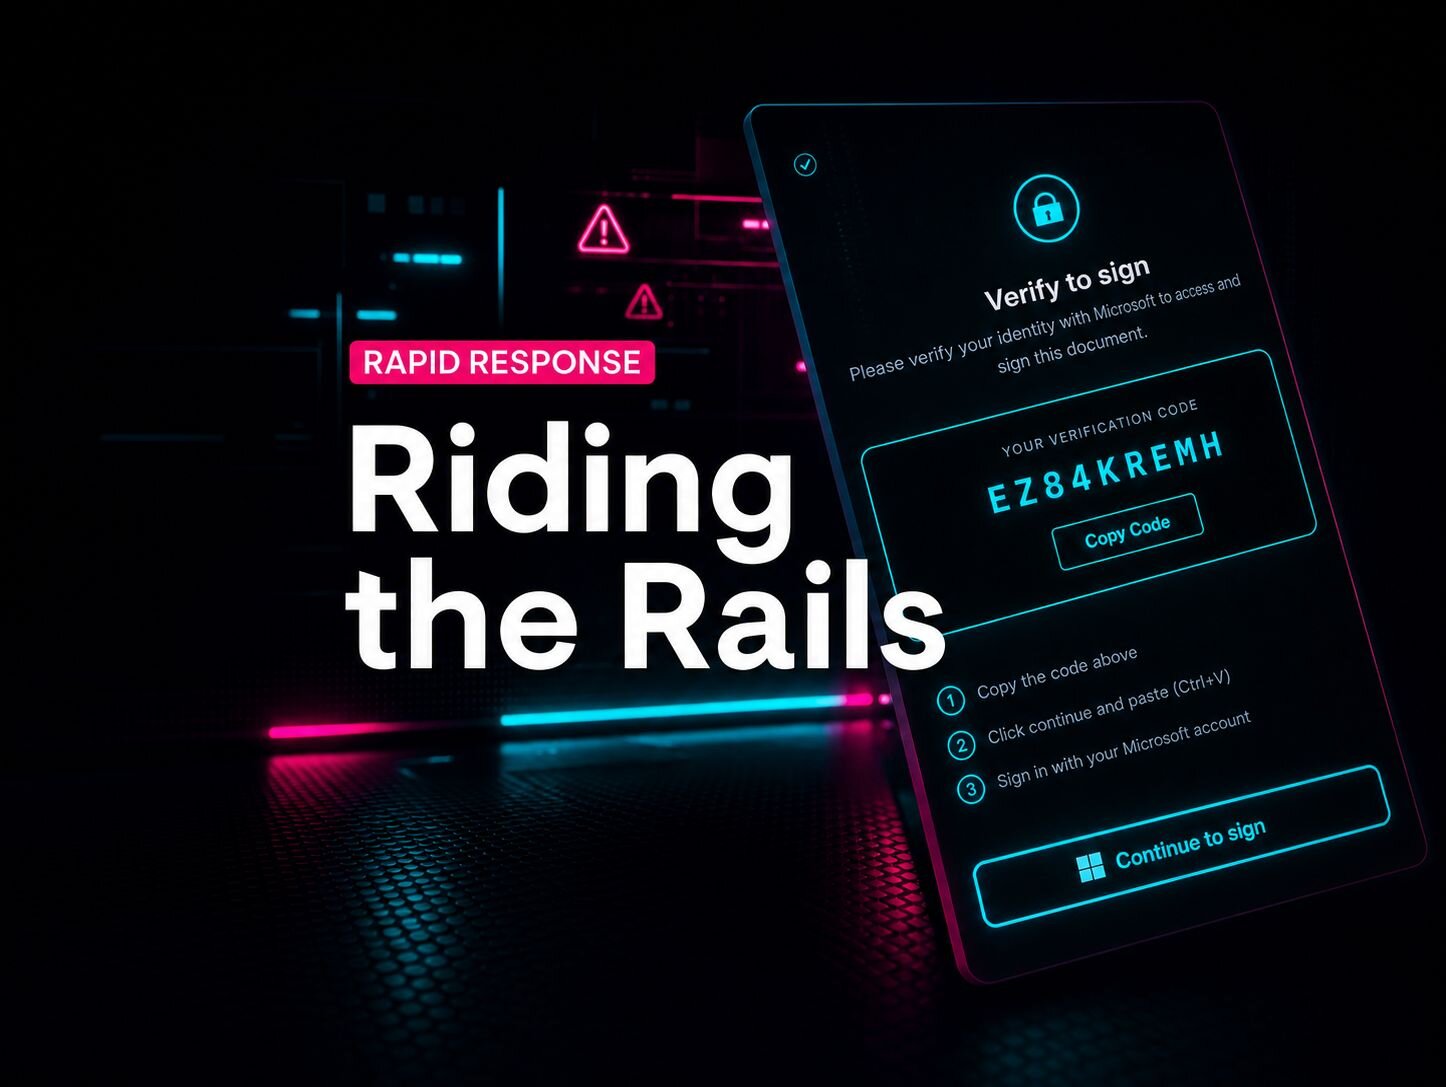
Attackers turned Railway.com's free cloud platform into a Microsoft 365 token-stealing machine, hitting 268+ organizations and 100+ MSPs. Here's the full infrastructure breakdown.
The newest capability in Huntress Managed ITDR, Adversary Infrastructure, turns that one-time fire drill into continuous protection. When our SOC confirms the hosting, relay, or proxy infrastructure behind a compromise in one tenant, our detection engineers validate it against benign traffic. Huntress then deploys a blocking Conditional Access policy to every eligible, opted-in tenant. Attacks from that infrastructure fail at sign-in instead of becoming incidents. One partner’s incident becomes every partner’s protection. We call it herd immunity for identity.
Meet Lookback: the moment a tenant finishes onboarding, Huntress automatically replays up to 180 days of Microsoft 365 login history through the full Unwanted Access detection stack.
This session explores how attackers are evolving their tactics, where organizations remain most vulnerable, and what practical steps businesses can take to strengthen email security as part of a broader cybersecurity strategy.
Join us for an exclusive livestream where we’ll showcase our newest product updates and give you an early look at the changes heading to the platform.
In this session, we’re unveiling the new Managed ITDR powered by our latest capability, Rogue Apps, built from the ground up to protect Microsoft 365 environments without the noise or guesswork.
