


Protect What Matters
Secure endpoints, email, and employees with the power of our 24/7 SOC. Try Huntress for free and deploy in minutes to start fighting threats.
Huntress delivers enterprise-grade protection without the enterprise bloat. Get a 24/7 human-led, AI-centric SOC backed by our agentic security platform, fully managed protection across endpoints and identities. You shouldn't have to choose between great tools and great people. With Huntress, you get both.

Huntress is best described as a broader managed security platform built around managed endpoint detection and response (EDR) and a 24/7 human-led AI-centric Security Operations Center (SOC).
Many managed detection and response (MDR) providers monitor alerts from security tools you already own. Huntress builds, operates, and manages its platform from the initial signal through investigation, response, and remediation. That means your team doesn’t have to manage, tune, and monitor another security tool on their own.
For most environments, yes. We cover the same core outcomes: 24/7 monitoring, threat detection, investigation, and response.
If you’re paying for an enterprise EDR license, an MDR add‑on, and separate professional services for incident response, Huntress consolidates that into a single, more affordable, fully managed package.
Huntress works with Microsoft Defender rather than replacing it. Huntress Managed EDR can work with Microsoft Defender Antivirus, Defender for Business, and Defender for Endpoint to add Huntress telemetry, detection, investigation, and SOC-backed response.
For supported Windows endpoints, Huntress can manage Microsoft Defender Antivirus at no additional Huntress charge when it’s paired with Managed EDR.
Huntress can also run alongside third-party antivirus products. However, Managed Microsoft Defender features require Microsoft Defender to be the active antivirus engine.
Huntress uses straightforward, volume-based pricing: per endpoint for Managed EDR, per identity for Managed Identity Threat Detection and Response (ITDR), per data source for Managed Security Information and Event Management (SIEM), and per learner for Managed Security Awareness Training (SAT).
Core capabilities and 24/7 SOC support are included rather than reserved for a higher management tier. This makes it easier to compare total coverage and predict costs as your environment grows.
Huntress is designed for fast deployment through a lightweight agent, remote monitoring and management (RMM) tools, integrations, and a centralized portal. With the required permissions, an IT administrator can usually deploy the platform in under an hour.
Huntress also provides deployment guidance, coverage validation, integration support, and ongoing management so your team doesn’t have to maintain a complex detection and response system alone.
The Huntress agentic platform includes:
Each managed solution is supported by Huntress’s 24/7 SOC. Customers select the products that match their security needs rather than having to build and operate a disconnected collection of tools.
We integrate with Microsoft, not against it. Huntress works alongside Microsoft Defender to unlock more value from what you already own.
We extend Microsoft’s tooling with:
So instead of choosing “Defender or Huntress,” you use Defender plus Huntress to get better outcomes with less effort.
Most traditional antivirus tools only stop known, signature‑based threats. Most EDRs generate a lot of alerts that still require a human to investigate and respond.
Huntress gives you both: purpose‑built detection plus a 24/7 human SOC that triages, investigates, and responds on your behalf. We typically run alongside your existing stack during a trial so you can compare what we catch before you change anything.
Yes. Huntress gives you documented 24/7 monitoring, incident response, remediation support, and audit‑ready reporting. Those are core elements most cyber insurance carriers and frameworks (like SOC 2, HIPAA, and CMMC) look for.
Huntress won’t make you fully compliant by itself, but we help you satisfy many of the technical and monitoring controls that show up on those checklists and provide evidence when you’re working with auditors or assessors.
The Huntress security platform is built, owned, and operated entirely by our team from first signal through remediation. Predictable pricing with no noise, just meaningful alerts.
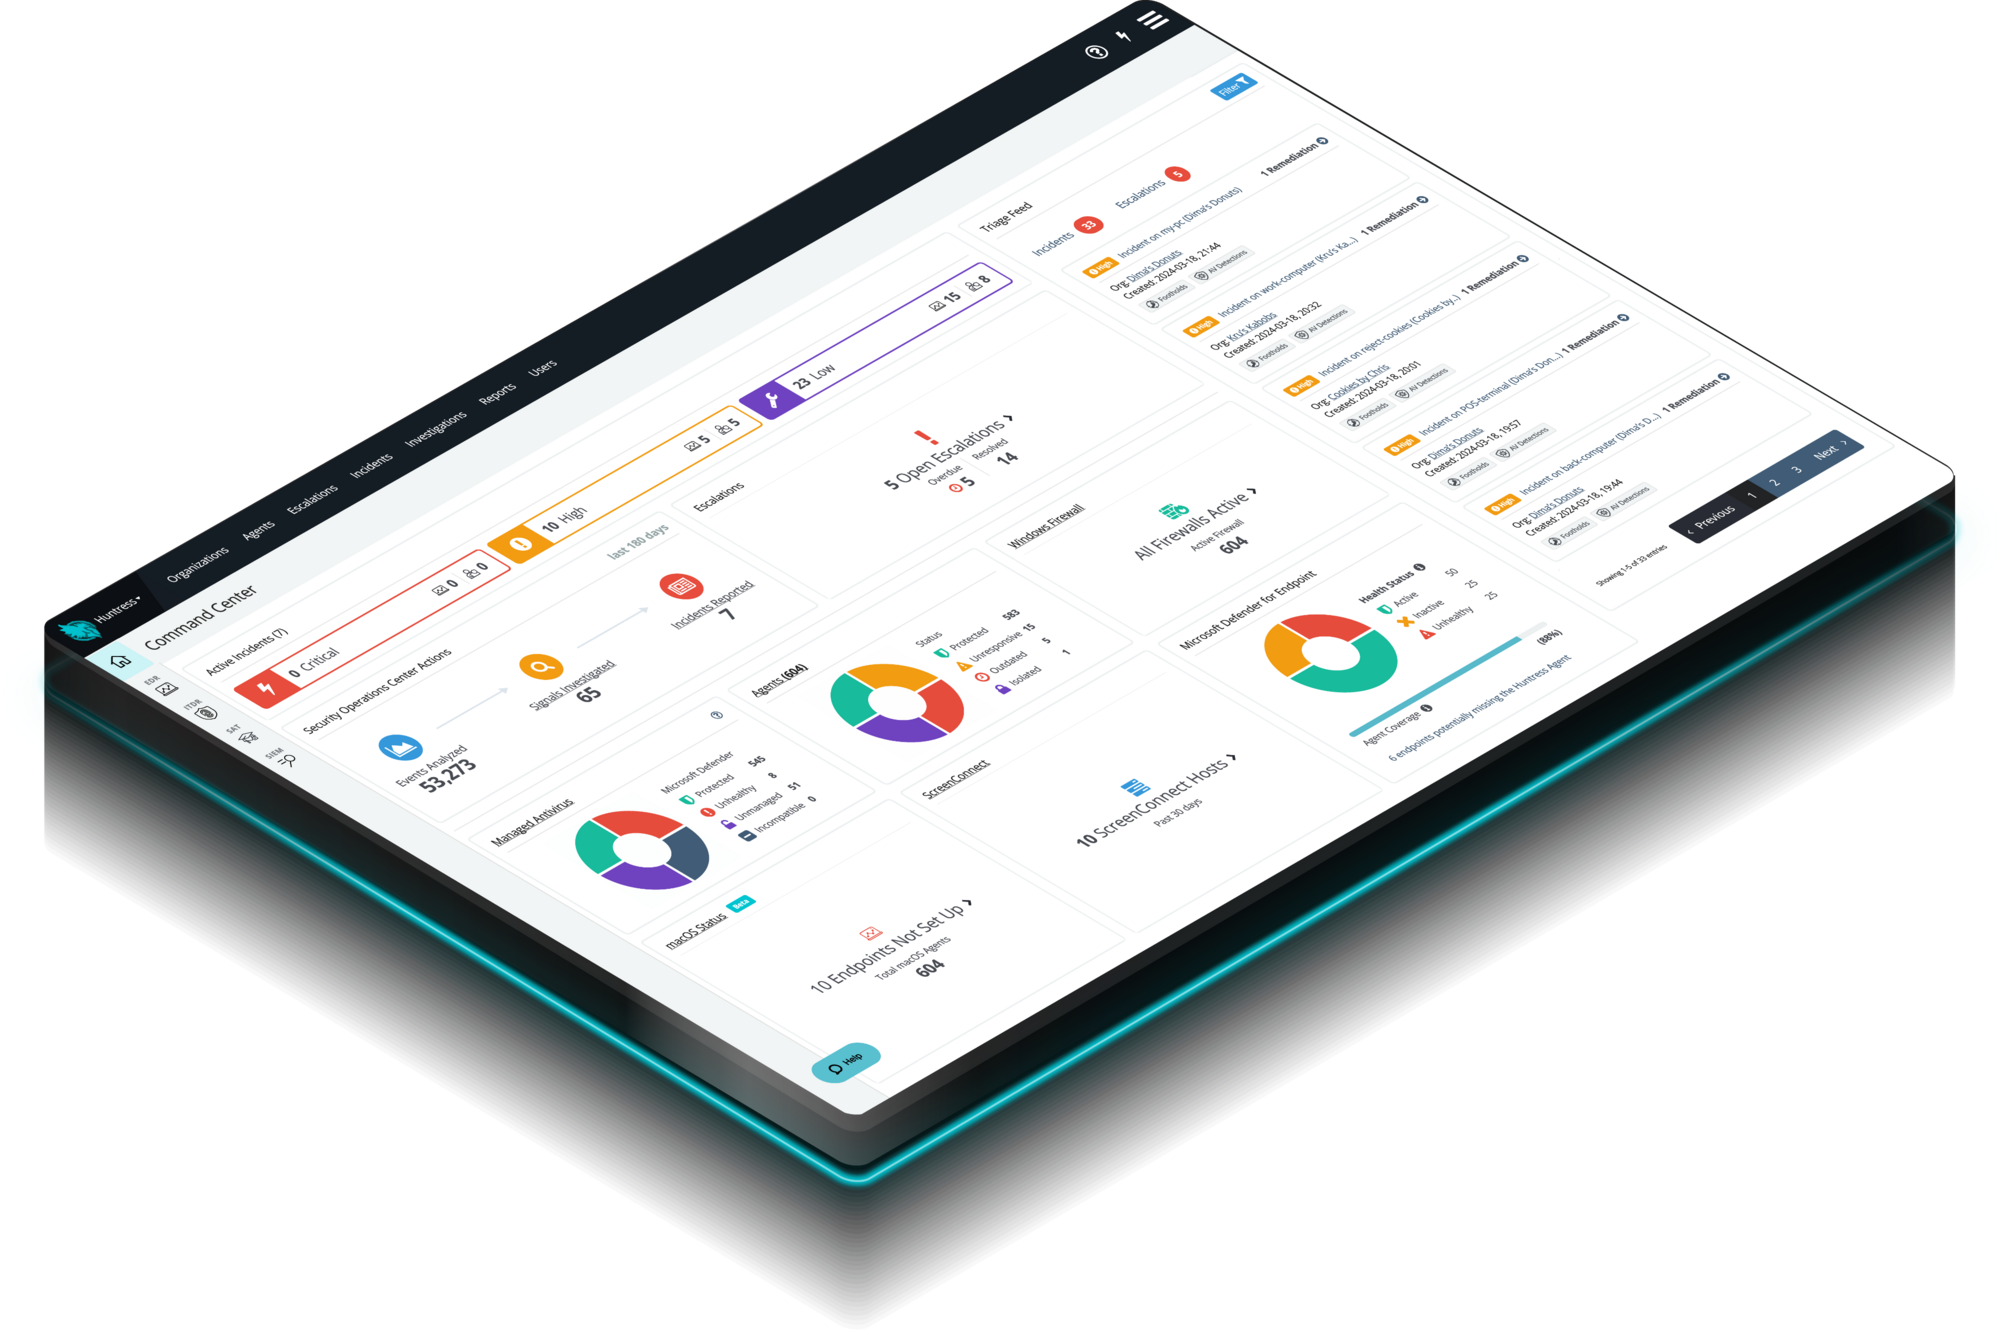

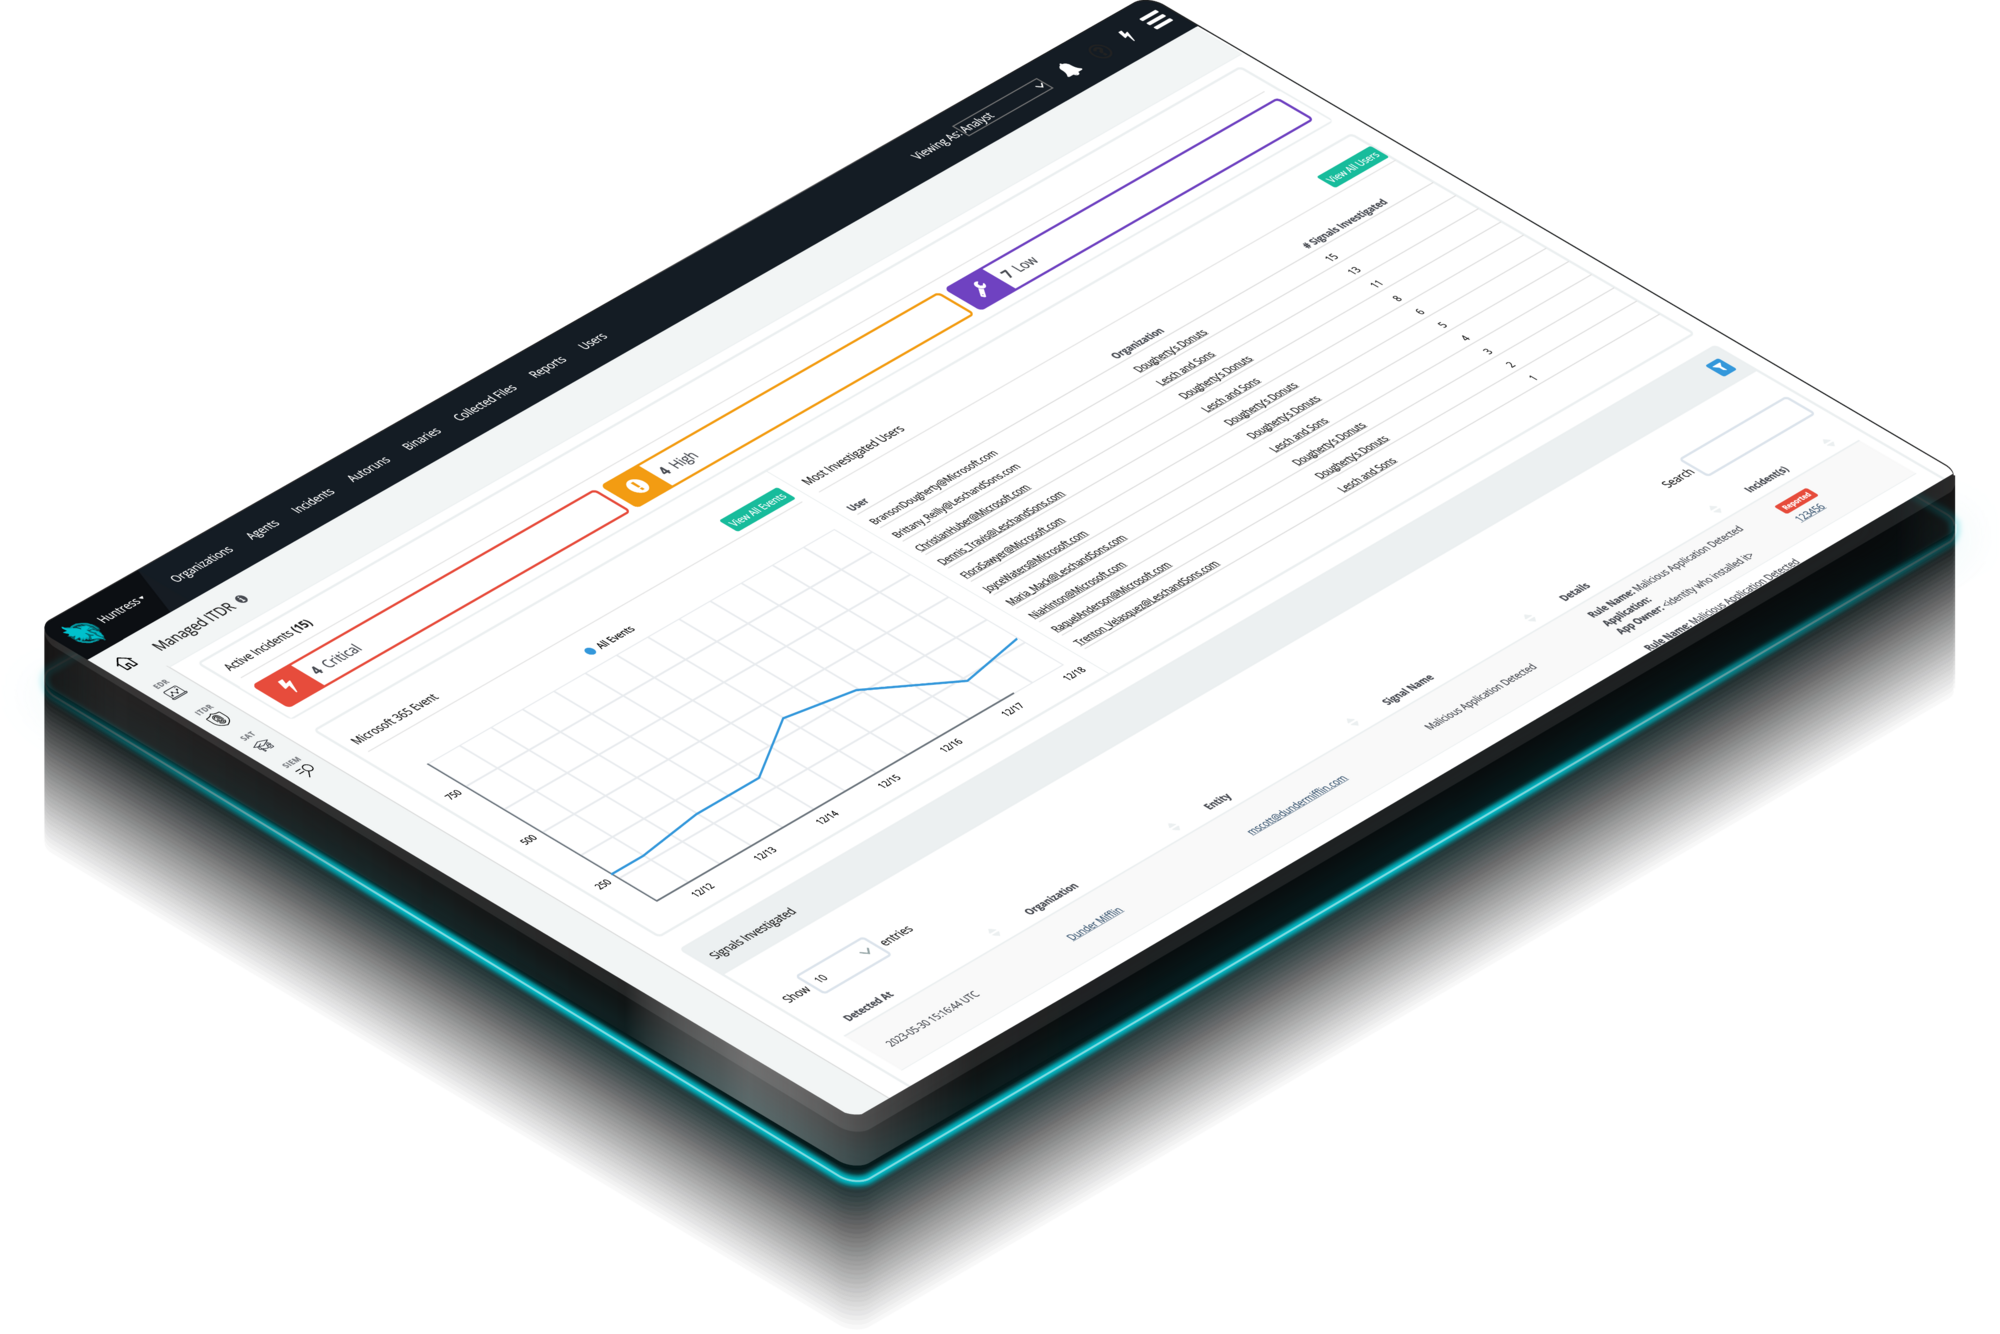
Identity Threat Detection and Response (ITDR)
Finds and stops identity-based threats in Microsoft 365 and Google Workspace—because identity is the new endpoint, and attackers know it. Huntress Managed ITDR is designed to detect, respond to, and resolve critical identity-based threats like account takeovers, business email compromise, unauthorized logins, and more.
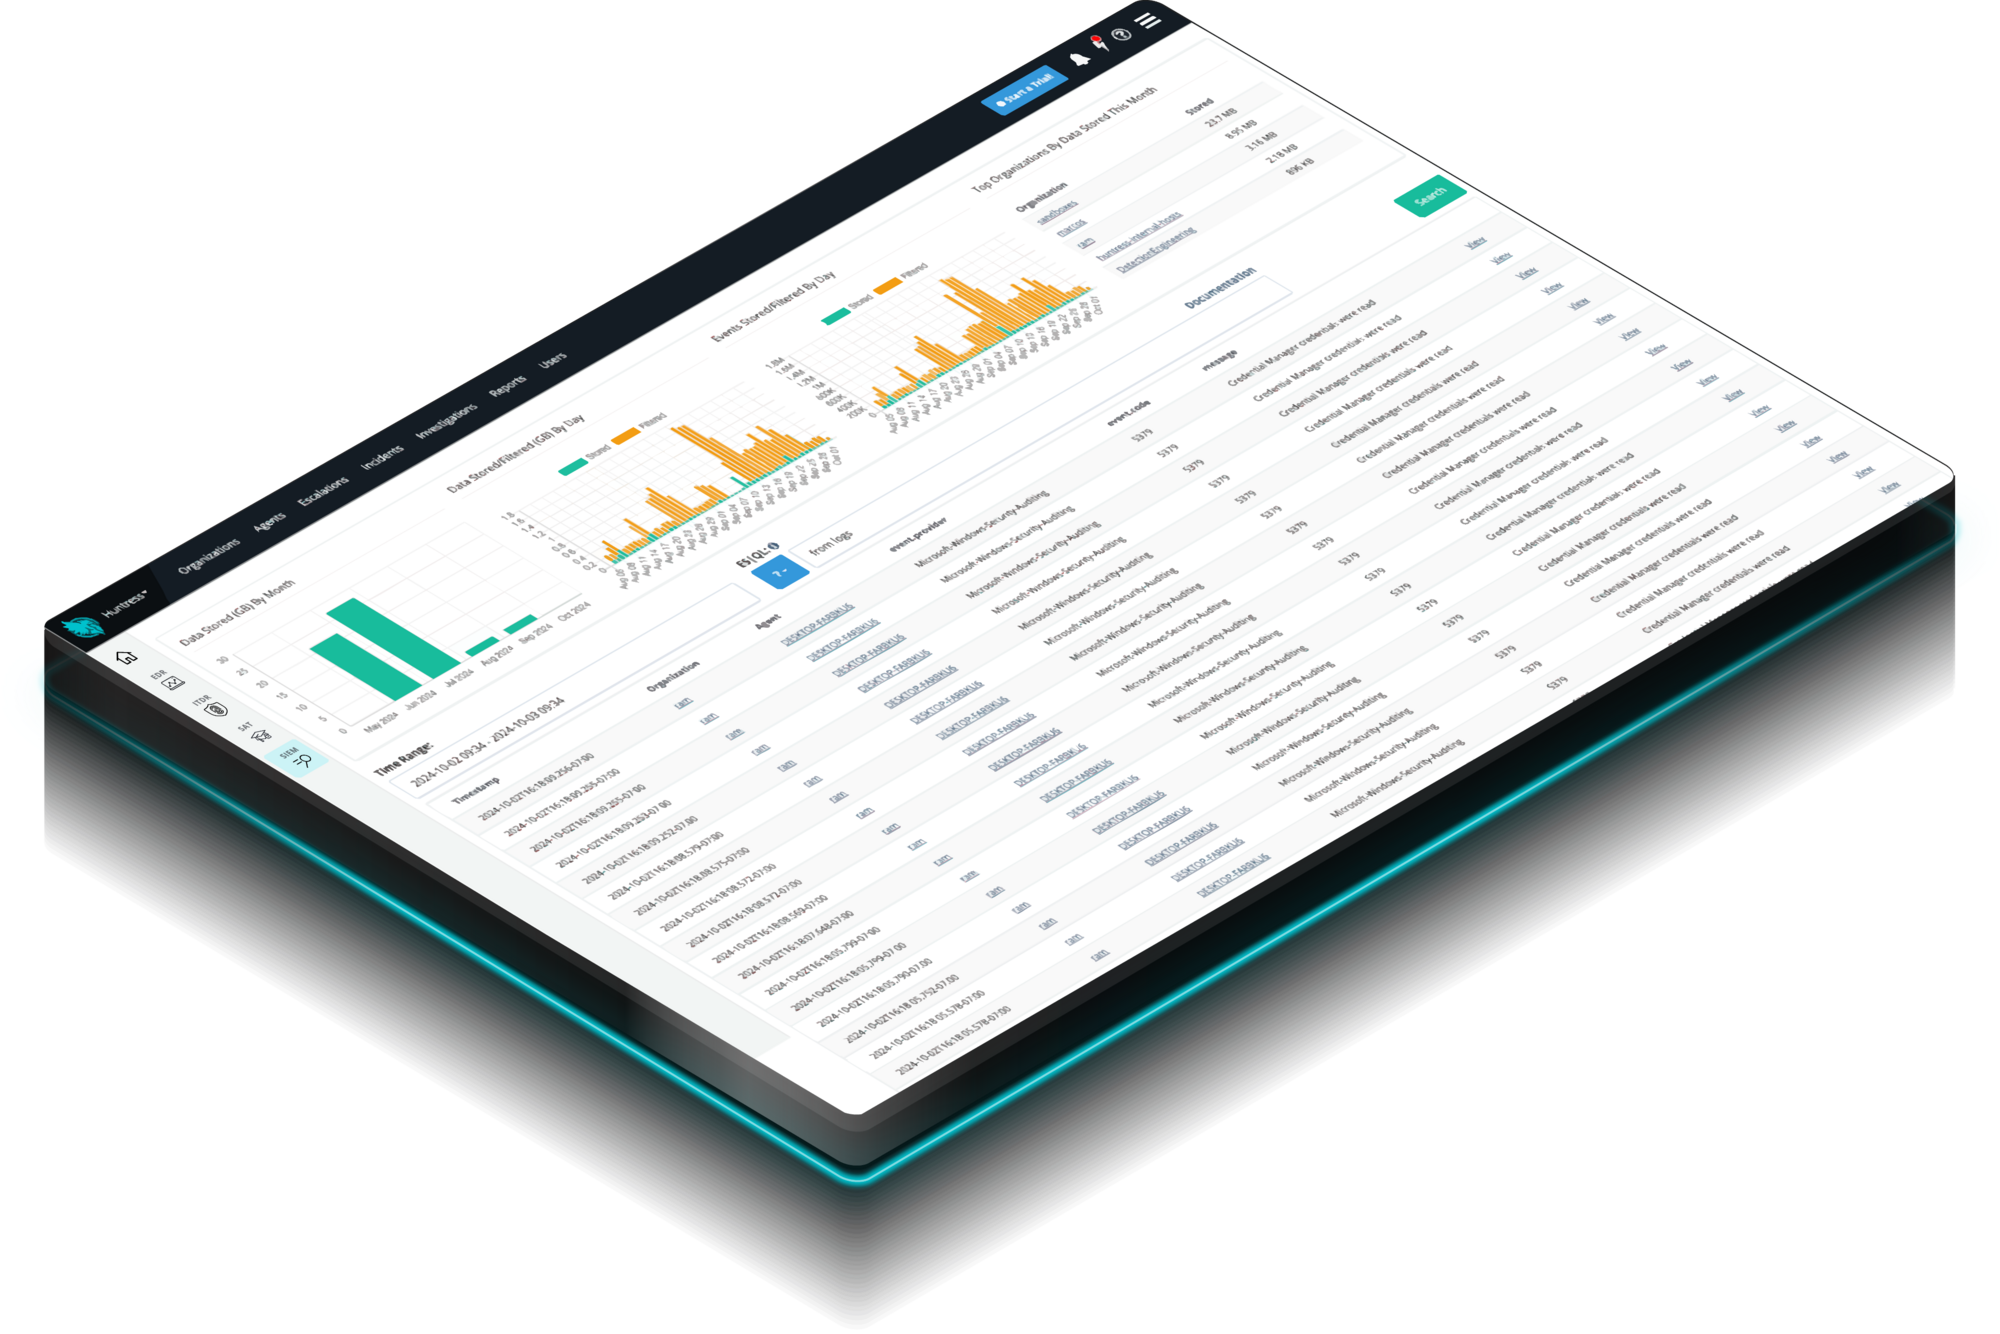
Huntress Managed SIEM takes away the complexity and overhead usually associated with traditional SIEMs, giving you everything you need and nothing you don’t. 24/7 threat response and strengthened compliance, fully managed by SOC experts, at a predictable price.
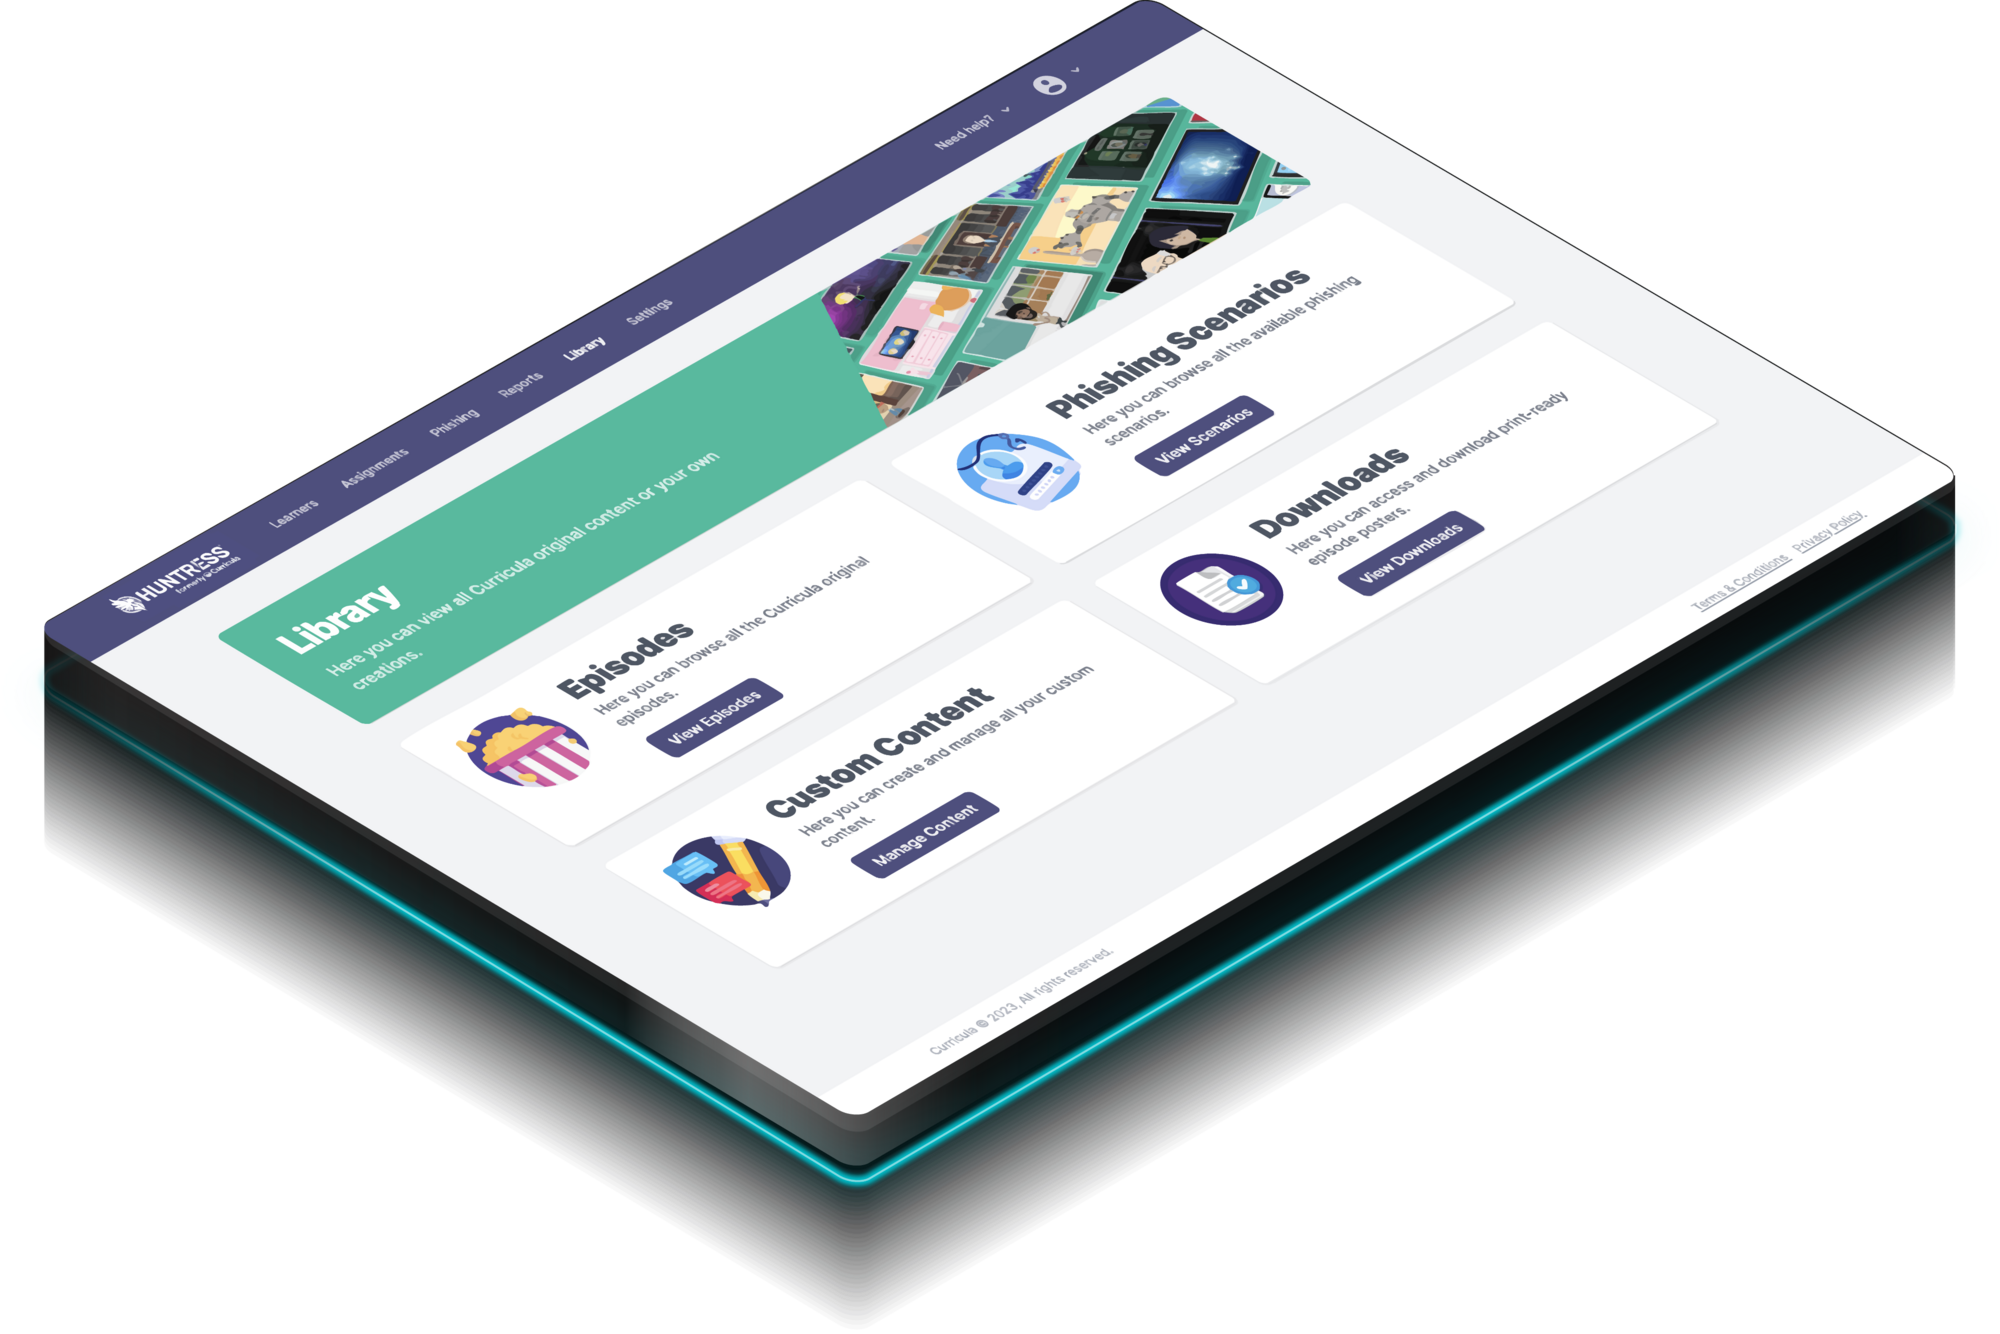
Engaging, expert-backed, personalized training content built on real-world threat intelligence and created by Emmy® Award-winning animators to reduce human risk and build a strong security culture.
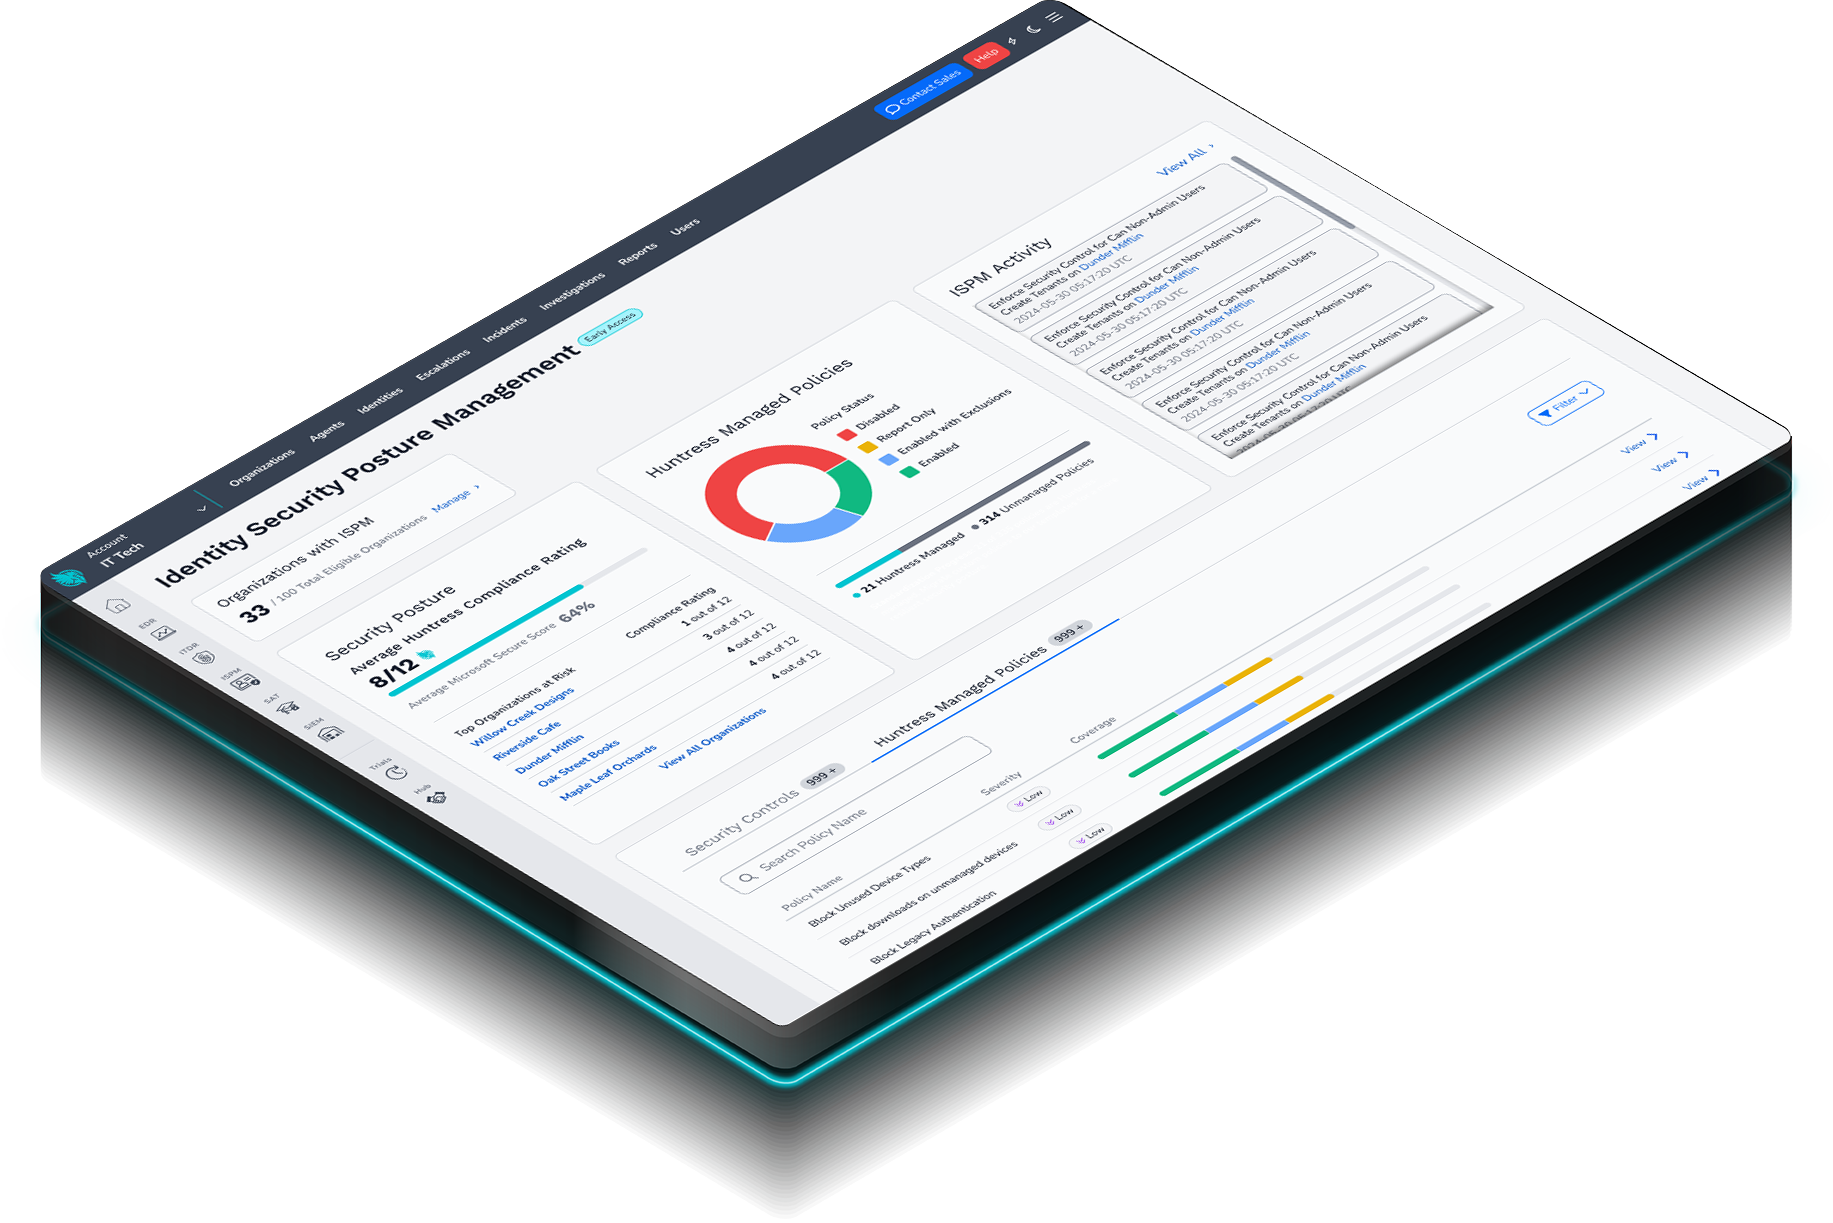
Most hackers don't break in — they just take advantage of messy settings, bad defaults, and accounts with too much access. Huntress Managed Identity Security Posture Management (ISPM) continuously finds and closes misconfigurations, risky access, and policy drift in Microsoft 365 so those attack paths stay closed.
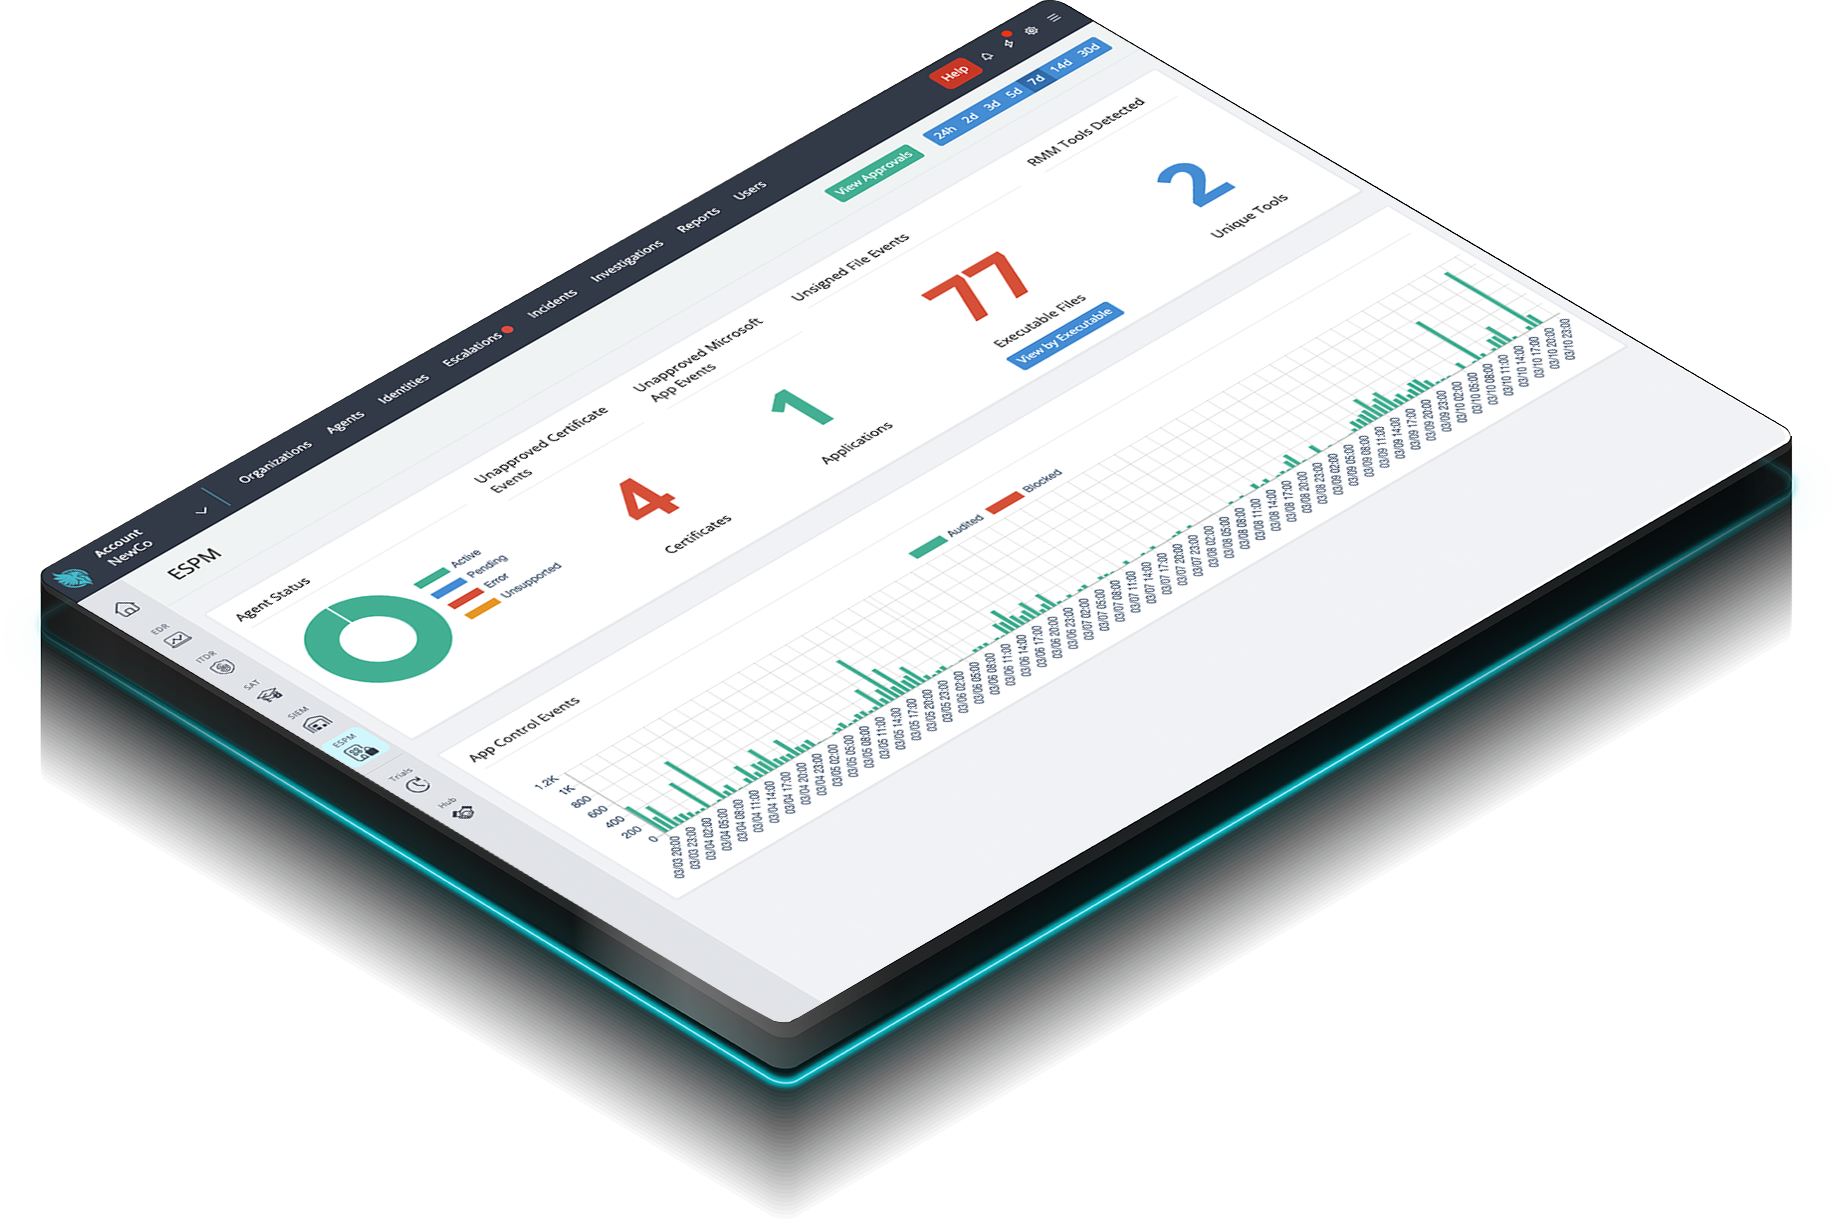
Huntress Endpoint Security Posture Management is proactive security that hardens endpoints to defend against attacks like ransomware and infostealers, and prevent breaches. Get broad endpoint visibility and control over configurations, applications, vulnerabilities, and more in one location and a single solution.

