

Learn how Huntress' Athena brings agentic AI to the SOC, investigating signals end-to-end while human analysts own the final call.
AI is changing cybersecurity. Here's how Huntress uses it.
Artificial intelligence is changing cybersecurity on both sides. Explore how attackers are using AI and how Huntress puts it to work responsibly.

Threat actors use AI to generate sharper phishing lures and automate attacks, stripping much of the manual work out of cybercrime. As AI puts capable attacks in less-capable hands, defenders have to move faster without giving up their own judgment.
At Huntress, we believe AI is a tool to augment human expertise, not replace it. Unlike fully autonomous SOCs, Huntress takes a different approach that combines human insight and judgment with machine speed. You're not buying an algorithm, you're getting an AI-enabled team of experts.
Inside our 24/7 SOC, a proprietary AI-powered investigation system assists with investigating, correlating, and summarizing, while our in-house analysts own the decisions that demand human expertise.

Purpose-built to work alongside our human SOC experts, Athena helps:

by gathering context, connecting telemetry, and drafting incident reports before a human looks at the investigation.

by grouping meaningful behavior across endpoints, identities, logs, and users into a single investigation.

with automation on high-confidence investigations, so the SOC keeps up as the volume of AI-powered attacks grows.

with Huntress analysts owning outcomes and making the calls that take the most careful human judgment.
With Athena, human analysts can spend less time assembling information and more time stopping complex and novel threats.
90%
Reduction in time required to generate incident reports.
61%
Reduction in human analyst time to investigate.
40+
Specialized AI agents working together within Athena to support investigations.
86%
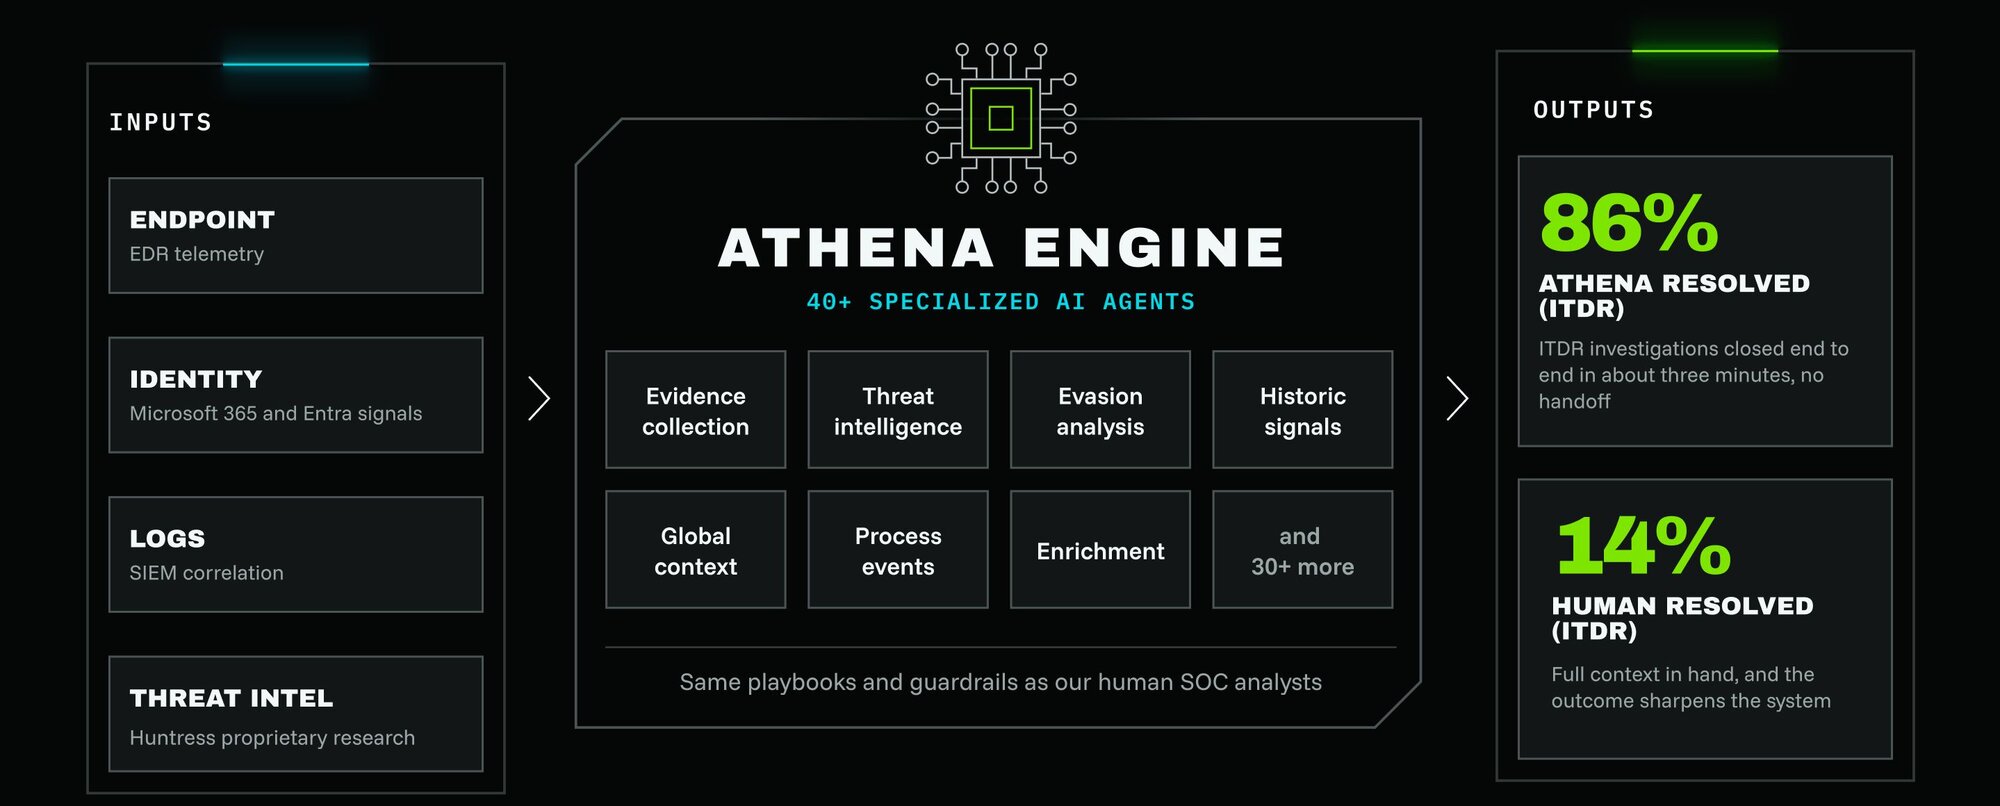
Of ITDR investigations handled end-to-end by Athena.
Signals from across your environment feed a single investigation. More than 40 specialized agents run the same playbooks and guardrails our analysts use, and our analysts own every call the system is not confident enough to make.
Cybercriminals are moving faster than ever, which means you need experts who know what real attacker behavior looks like and how to respond when a threat takes hold.
The Huntress Adversary Tactics team and our 24/7 Security Operations Center (SOC) use AI to handle the repetitive work, so they can focus on the threats that need human judgment. AI does the legwork, but our experts make the calls.
The result is a team that moves faster on real tradecraft and stops threats before they take over your day.
Get ready for anything attackers throw at you…
Learn how Huntress' Athena brings agentic AI to the SOC, investigating signals end-to-end while human analysts own the final call.
Learn how Huntress' AI signal triage and AI-powered SOC triage cut noise before it reaches human analysts. And discover why that matters for response times.
See agentic security operations governance in action: Huntress' AI SOC lets Athena investigate and act autonomously within guardrails our human analysts set.
Our platform combines a suite of powerful managed detection and response tools for endpoints and Microsoft 365 identities, science-backed security awareness training, Managed SIEM, and the expertise of our 24/7 Security Operations Center (SOC).
Lateral movement is what happens after an attacker gains initial access. Rather than staying on one compromised system, they move between endpoints and identities using stolen credentials, remote administration tools, and trusted Windows functionality to reach valuable assets like domain controllers, file servers, and backups.
Attackers typically begin with standard user access, then abuse stolen credentials, software vulnerabilities, misconfigurations, or legitimate administrative tools to obtain elevated permissions. Once they gain administrator privileges, they can disable defenses, access sensitive systems, and move throughout your environment.
Huntress is designed specifically for teams like yours. Our human-led, AI-centric SOC acts as your dedicated extension, providing the necessary expertise and 24/7 coverage without the massive cost or complexity of building or scaling your own security team. We handle the hard parts—from threat hunting investigation, and response, to fully managed security awareness learning plans—and deliver concise, verified actions to your team. This model ensures you get enterprise-grade security outcomes without needing enterprise resources.
Yes.
Huntress was built for exactly this scenario. Managed EDR and Managed ITDR continuously monitor attacker behavior after initial access, while our 24/7 SOC investigates suspicious activity and rapidly responds before attackers can escalate privileges or move throughout your environment.
Our average mean-time-to-respond (MTTR) is under three minutes. Rather than simply generating alerts, our SOC validates malicious activity and begins containment quickly to reduce attacker dwell time.
