

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Huntress has observed a series of strikingly similar intrusions beginning with CitrixBleed 2 exploitation, employing novel local privilege escalation techniques, and ending in Dragonforce ransomware.
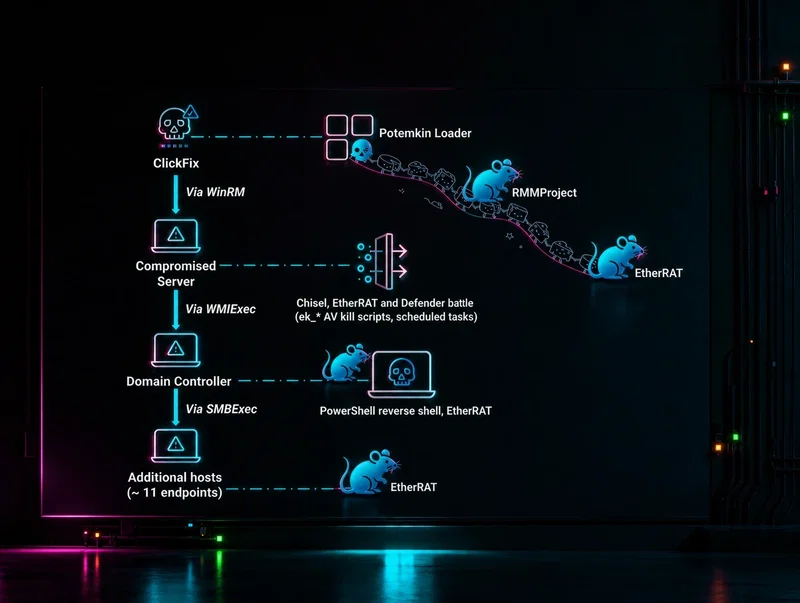
A ClickFix infection drops Potemkin loader and RMMProject RAT, leading to browser theft, hidden remote desktop, and lateral movement across over 11 hosts.
A malspam campaign abusing Google's DoubleClick delivers DesckVB RAT through a five-stage chain that evades detection and blinds Windows telemetry before persisting
Your background is gone, but malware is here. Huntress breaks down BackgroundFix, a new ClickFix social engineering tactic involving CastleLoader, NetSupport RAT, and CastleStealer. Read the analysis.
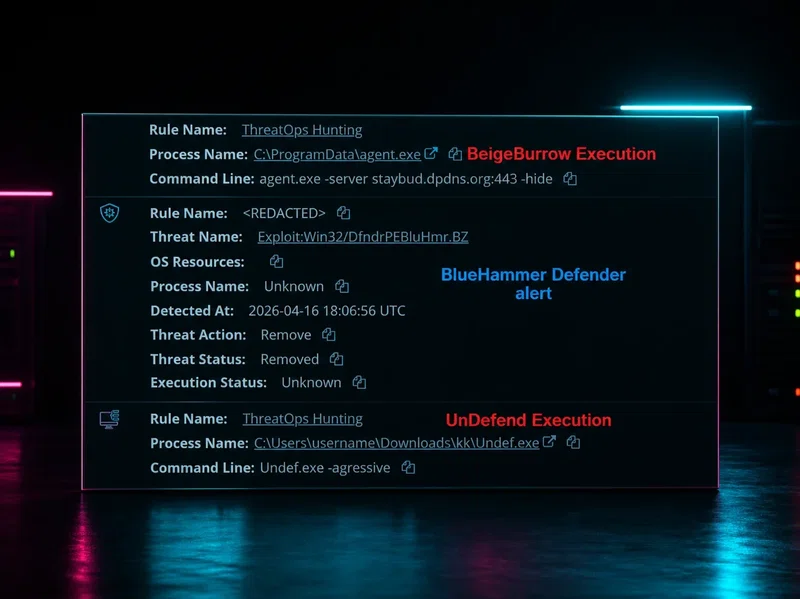
Huntress observed in-the-wild use of Nightmare-Eclipse tooling, including BlueHammer, RedSun, and UnDefend, in a live intrusion involving FortiGate VPN compromise as the initial access, reconnaissance commands, and likely tunneling activity.
Tax season gives attackers a reliable window: millions of users searching under deadline pressure. This malvertising campaign ends with a BYOVD attack that tries to kill your security tools from kernel mode.
A threat actor exploited SolarWinds Web Help Desk, then ran victim triage from a free Elastic Cloud SIEM trial. The infrastructure they left behind told us everything.
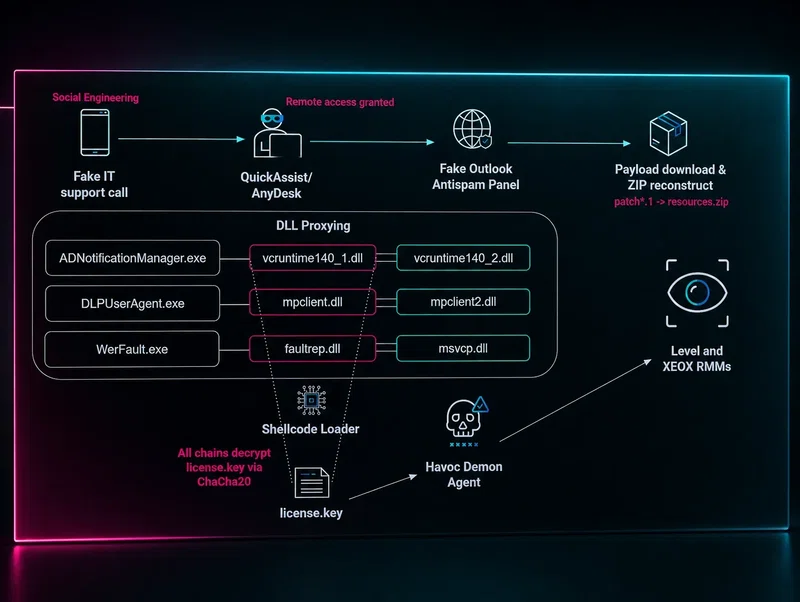
Fake tech support scams used to end with a gift card. Now they end with a modified Havoc C2 framework in your environment, using indirect syscalls to dodge your EDR.
ClickFix delivered the initial access, Matanbuchus did the loading, and a new RAT handled the rest. This February 2026 intrusion has all the ingredients of a campaign that isn't slowing down.
Tools built to monitor employees and support remote workers are being repurposed for ransomware operations. Net Monitor for Employees and SimpleHelp are the latest to be abused — here's how.
Huntress observed active exploitation of SolarWinds Web Help Desk across three customers — with attackers deploying Cloudflare tunnels and Velociraptor for persistence immediately after getting in.
They got in through SonicWall, then deployed a forensic tool's signed driver to kill endpoint security from kernel mode. Huntress disrupted the attack before ransomware deployed. Here's the full breakdown.
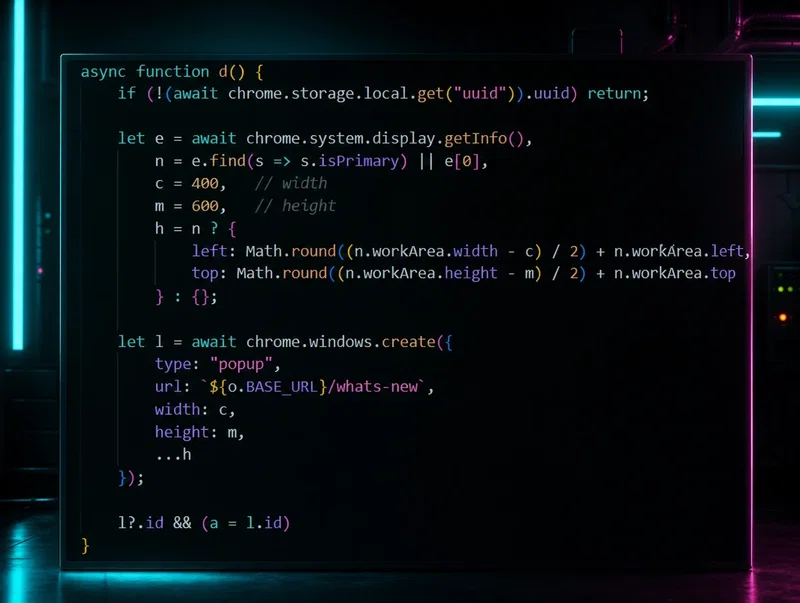
KongTuke built a fake browser extension that tells users their browser crashed and needs a scan. It doesn't. Huntress tracked this campaign back to a threat actor we've been following since 2025.
The AI-powered cyberattack apocalypse didn't happen in 2025. What did happen was quieter and more dangerous: attackers got faster and cheaper at the tradecraft they were already running.
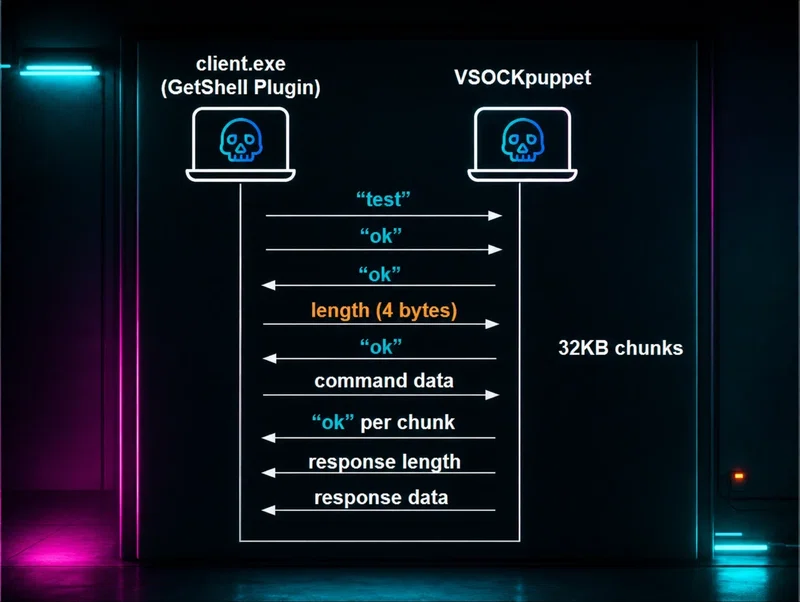
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.

