
Blog Post
When Shadows Turn Hostile: How Attackers Abuse VSS (and How Huntress Catches Them)
Attackers exploit Volume Shadow Copy for credential theft and ransomware defense evasion. See how Huntress spots the difference from routine IT activity.
Attackers exploit Volume Shadow Copy for credential theft and ransomware defense evasion. See how Huntress spots the difference from routine IT activity.
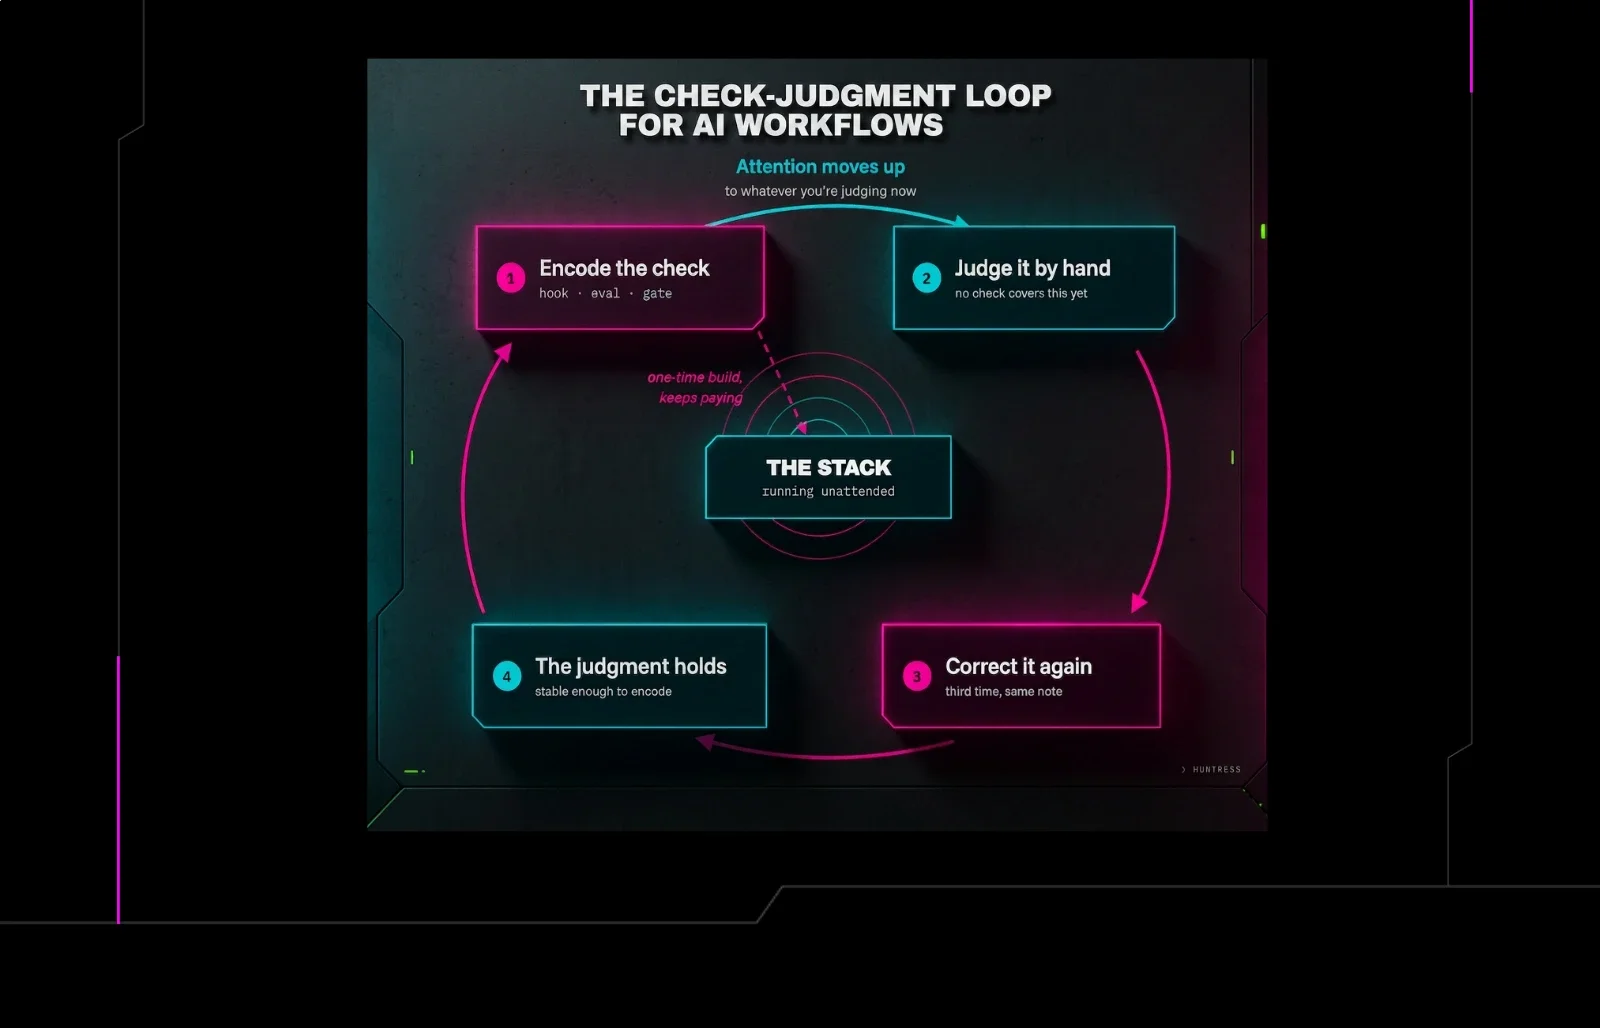
Before delegating work to AI, ask one question: can you check the output? A detection engineer on why verification, not trust, decides what tasks you hand over.
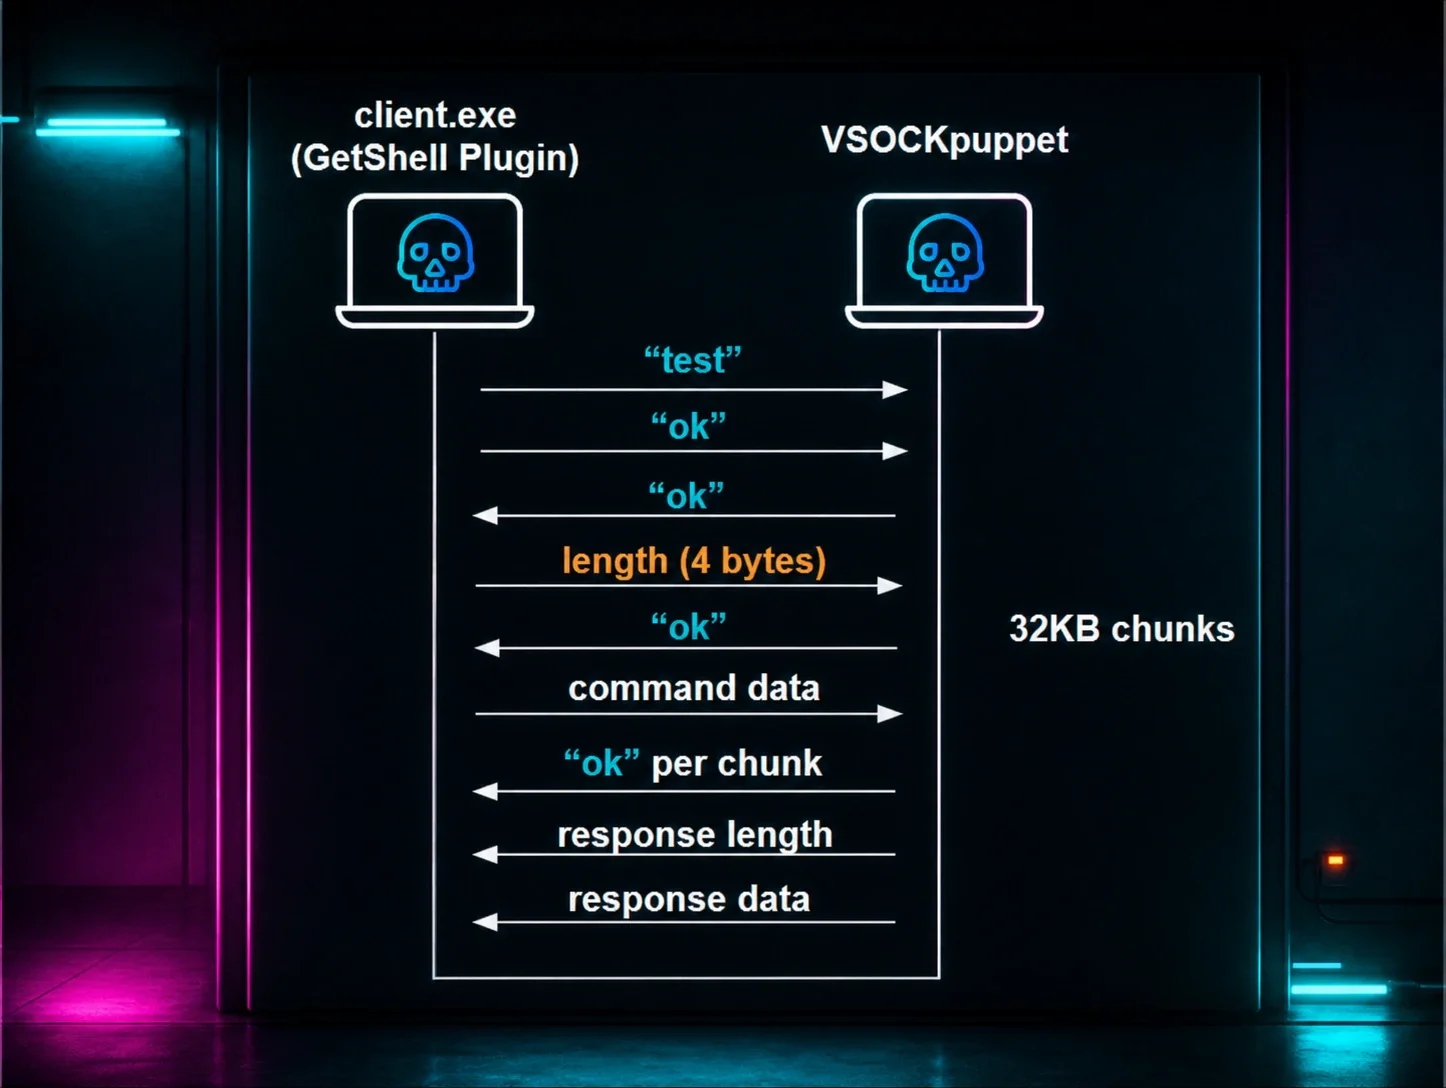
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.
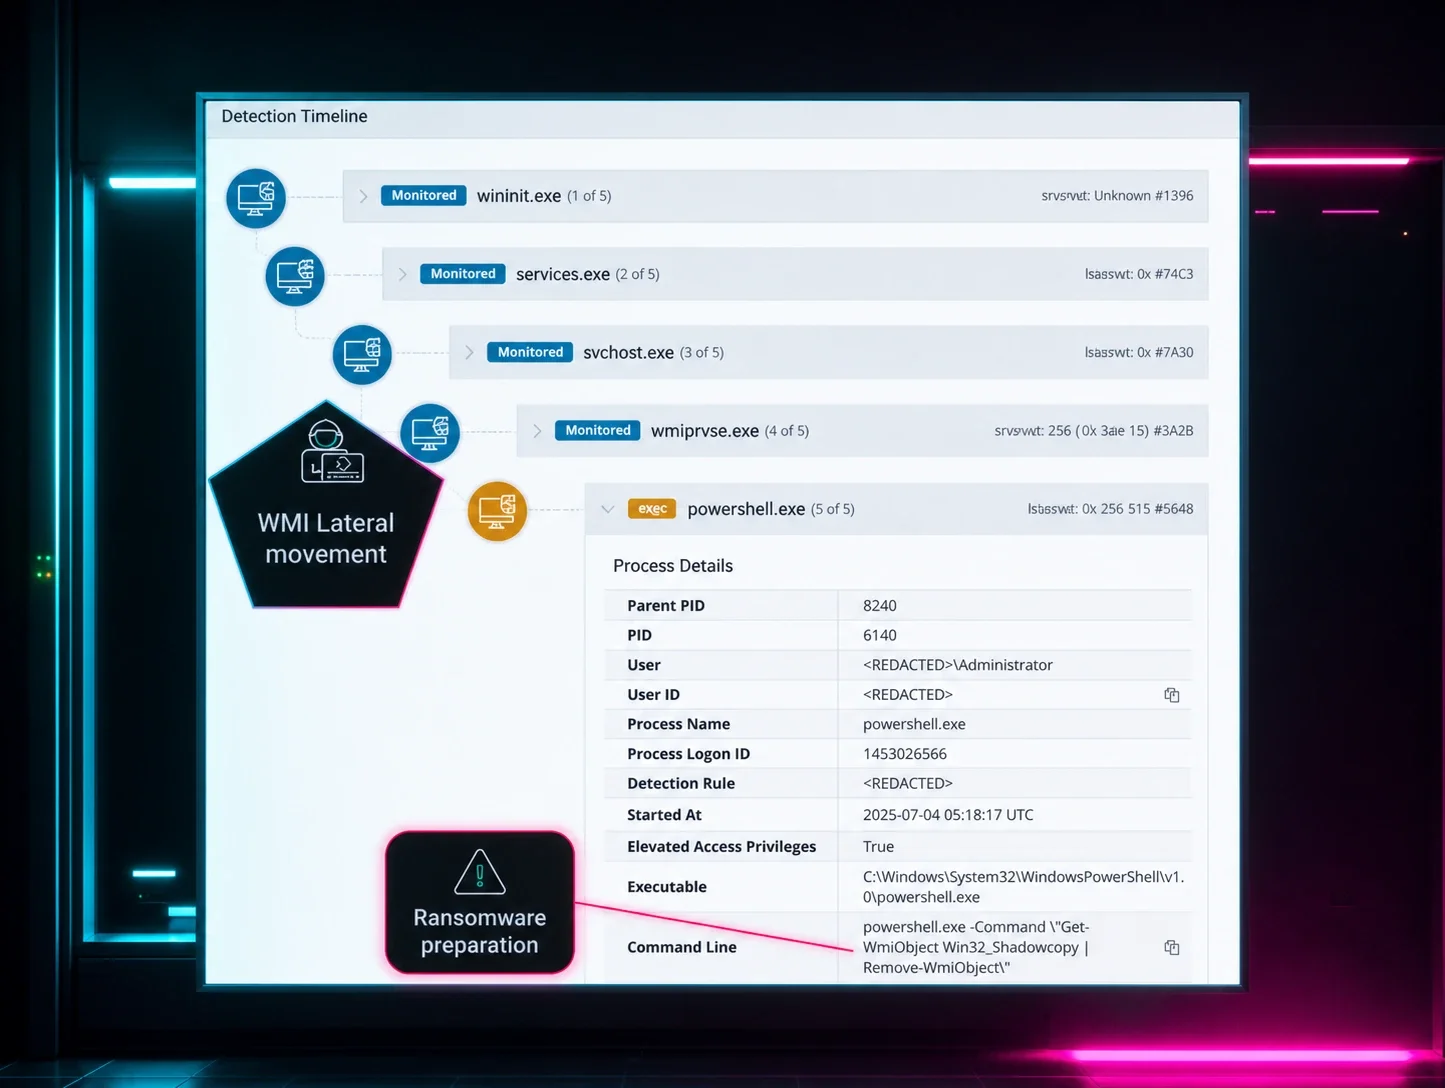
During a ransomware intrusion, Huntress found a script full of clear English comments walking through each step. Old playbooks don't die. Attackers just keep running them.
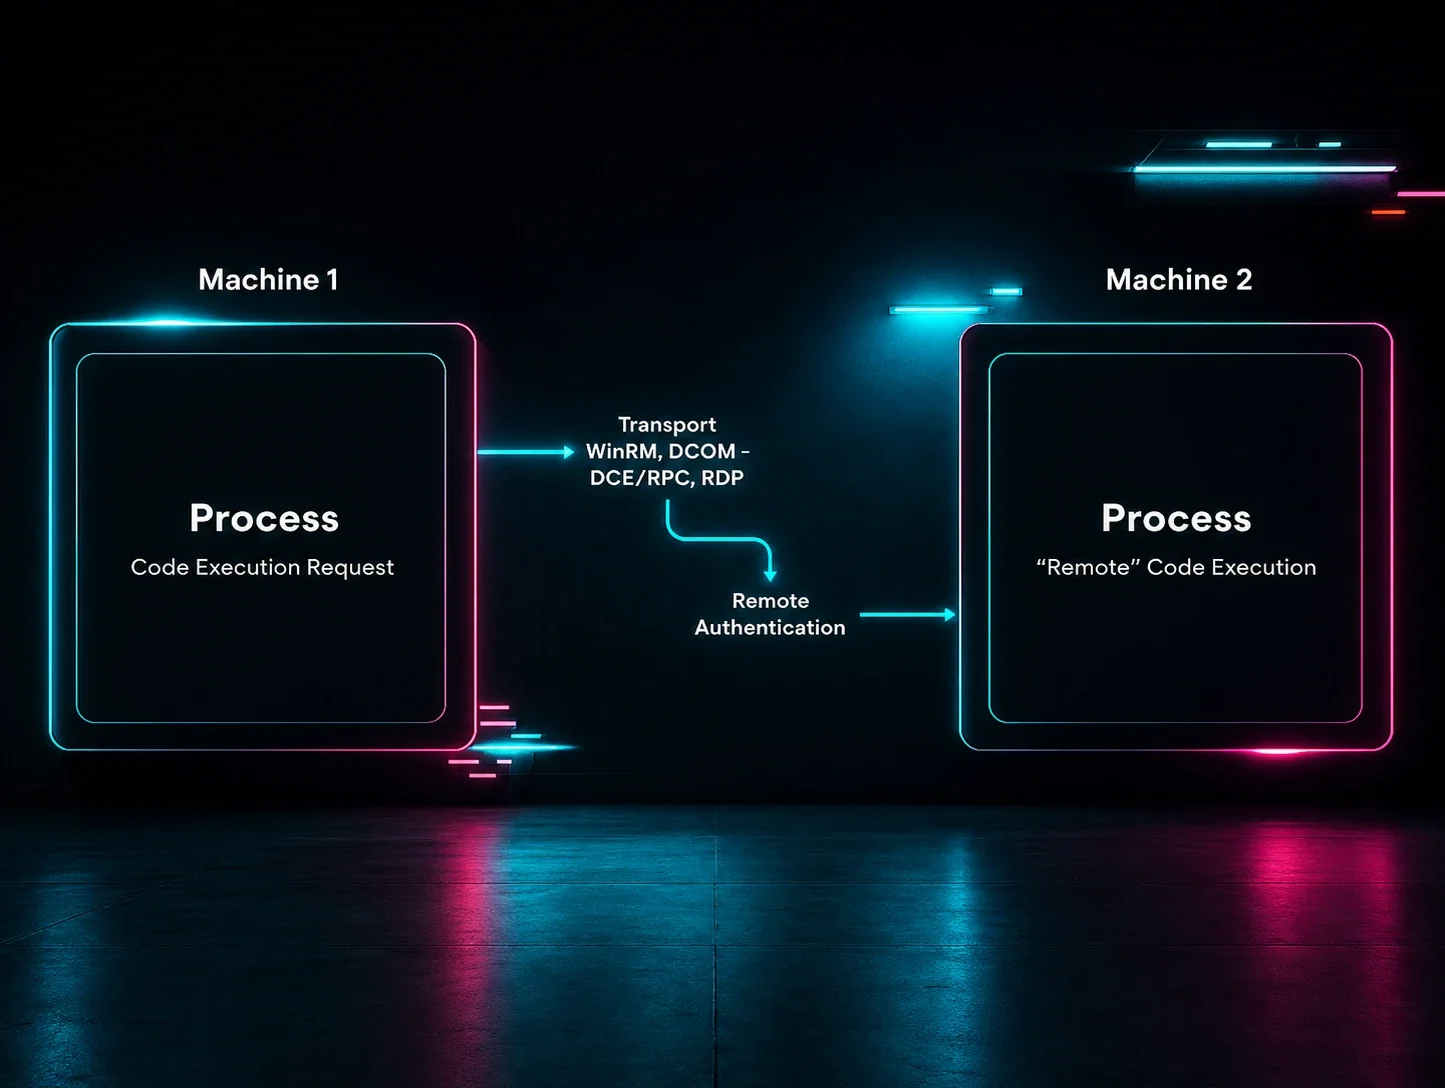
Once attackers are inside, lateral movement is how they deepen a compromise and make removal much harder. Here's exactly how Huntress detects and disrupts it before it spreads.
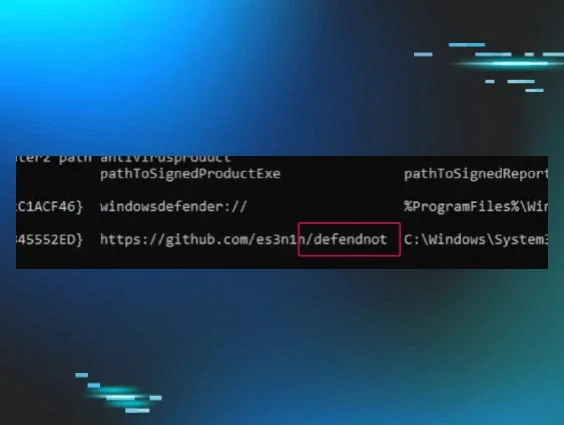
A tool called 'defendnot' disables Windows Defender by registering a fake antivirus through undocumented Windows Security Center APIs. Huntress covers the technique and how to detect it.
The newest capability in Huntress Managed ITDR, Adversary Infrastructure, turns that one-time fire drill into continuous protection. When our SOC confirms the hosting, relay, or proxy infrastructure behind a compromise in one tenant, our detection engineers validate it against benign traffic. Huntress then deploys a blocking Conditional Access policy to every eligible, opted-in tenant. Attacks from that infrastructure fail at sign-in instead of becoming incidents. One partner’s incident becomes every partner’s protection. We call it herd immunity for identity.
