

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.

Threat actors are exploiting AhsayCBS flaws, including CVE-2026-105133 and CVE-2026-105134, to deploy webshells and XMRig cryptominers. Update to 10.3.4 and restrict access now.
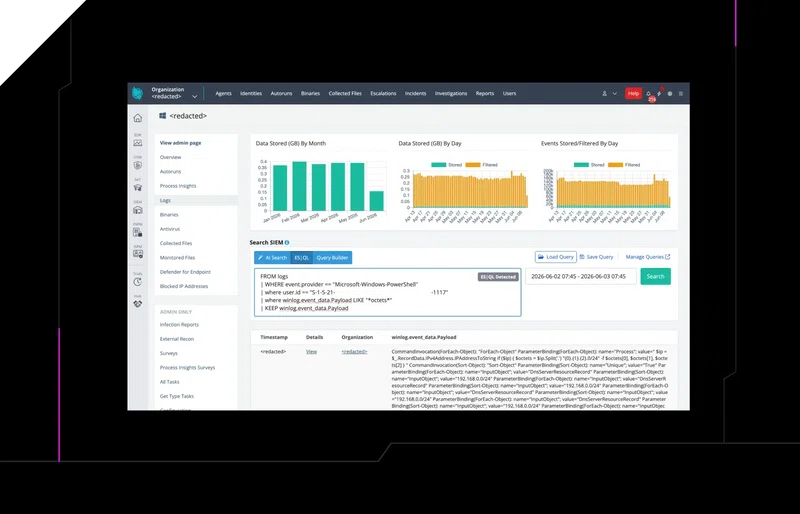
Threat actors are now using AI to generate custom PowerShell scripts for Active Directory attacks. Our team analyzed real vibe-coded malware and what it means for defenders.
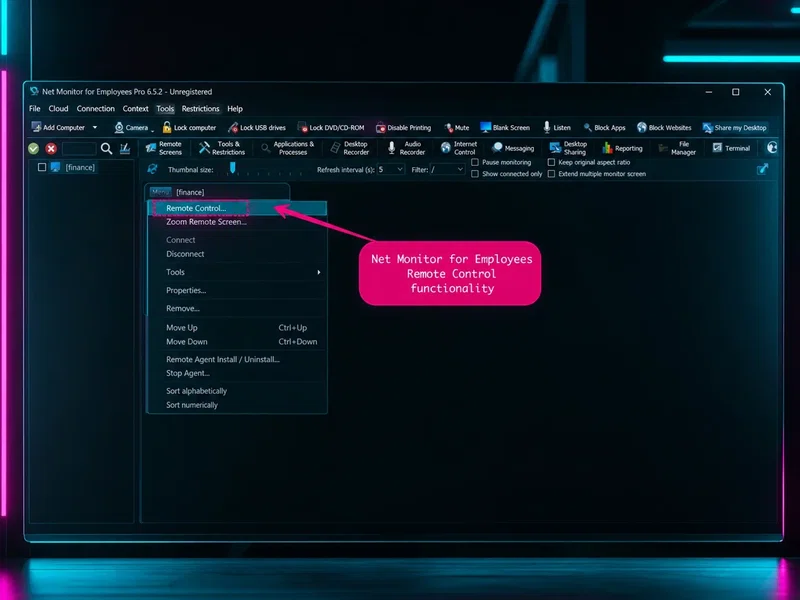
Tools built to monitor employees and support remote workers are being repurposed for ransomware operations. Net Monitor for Employees and SimpleHelp are the latest to be abused — here's how.
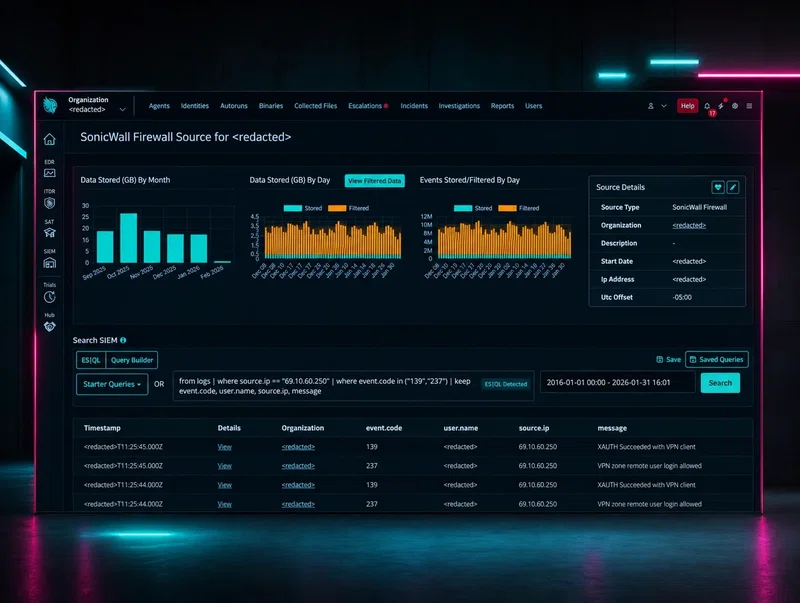
They got in through SonicWall, then deployed a forensic tool's signed driver to kill endpoint security from kernel mode. Huntress disrupted the attack before ransomware deployed. Here's the full breakdown.
The AI-powered cyberattack apocalypse didn't happen in 2025. What did happen was quieter and more dangerous: attackers got faster and cheaper at the tradecraft they were already running.
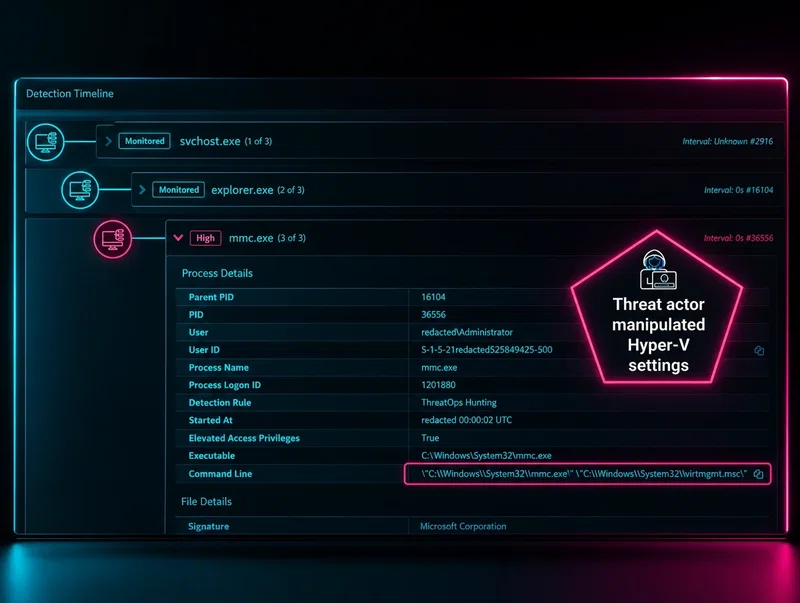
A single breach at the hypervisor layer puts every virtual machine at risk simultaneously and most security tools are blind to it. Here's how to actually harden ESXi against ransomware.
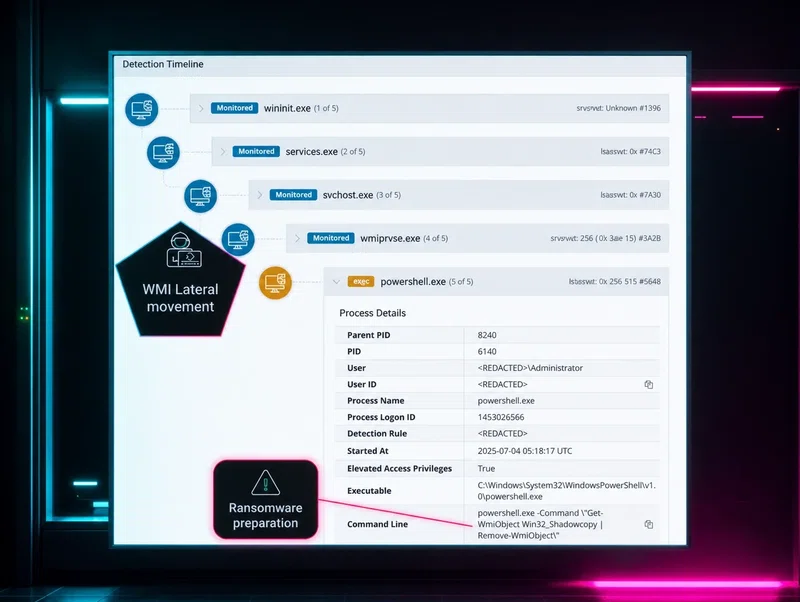
During a ransomware intrusion, Huntress found a script full of clear English comments walking through each step. Old playbooks don't die. Attackers just keep running them.
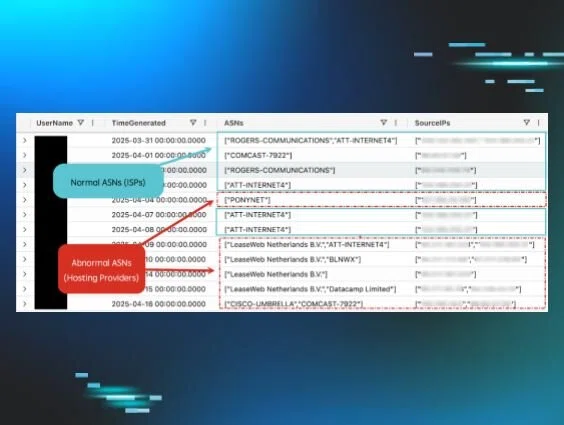
IP addresses are useful in investigations. Autonomous System Numbers give you the full picture: origin, ownership, and network context. Here's how Huntress uses ASNs to accelerate hunting and response.
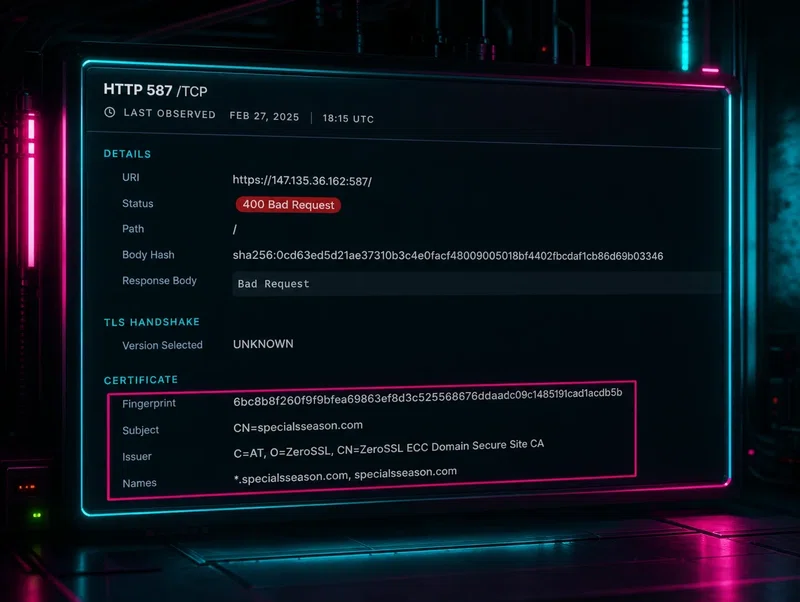
What started as a brute force investigation turned into something more interesting. Huntress documents how ransomware initial access brokers operate and what they look like in real-world telemetry.
Most incident write-ups present a clean timeline. This one doesn't — it takes the analyst's perspective, including the dead ends, the surprises, and the moments of genuine uncertainty. Here's what really happened.
200 million Americans buy tech products during the holidays, and a lot of those go to kids. Here's the practical guide to securing children's devices before they connect to the internet for the first time.
User agents in Microsoft 365 security telemetry can reveal BEC in ways that credential-based detection misses. This kept a Huntress SOC analyst up at 3am — here's what they found.
When Microsoft blocked macros in downloaded Office documents, threat actors adapted quickly. Huntress tracks how initial access methods evolved in 2022 and what defenders need to watch for now.
A vague antivirus alert is only as useful as the analyst investigating it. Huntress walks through a real Managed AV investigation, showing the tools, techniques, and thinking behind turning a single Defender alert into a clear picture of potential lateral movement.
Part three of Huntress' defense evasion series gets spicy. Attackers have to get in and run code somewhere, and defenders can catch them. Here's exactly how to spot evasion techniques in action.

