

Blog Post
Threat Advisory: Uptick in Bomgar RMM Exploitation
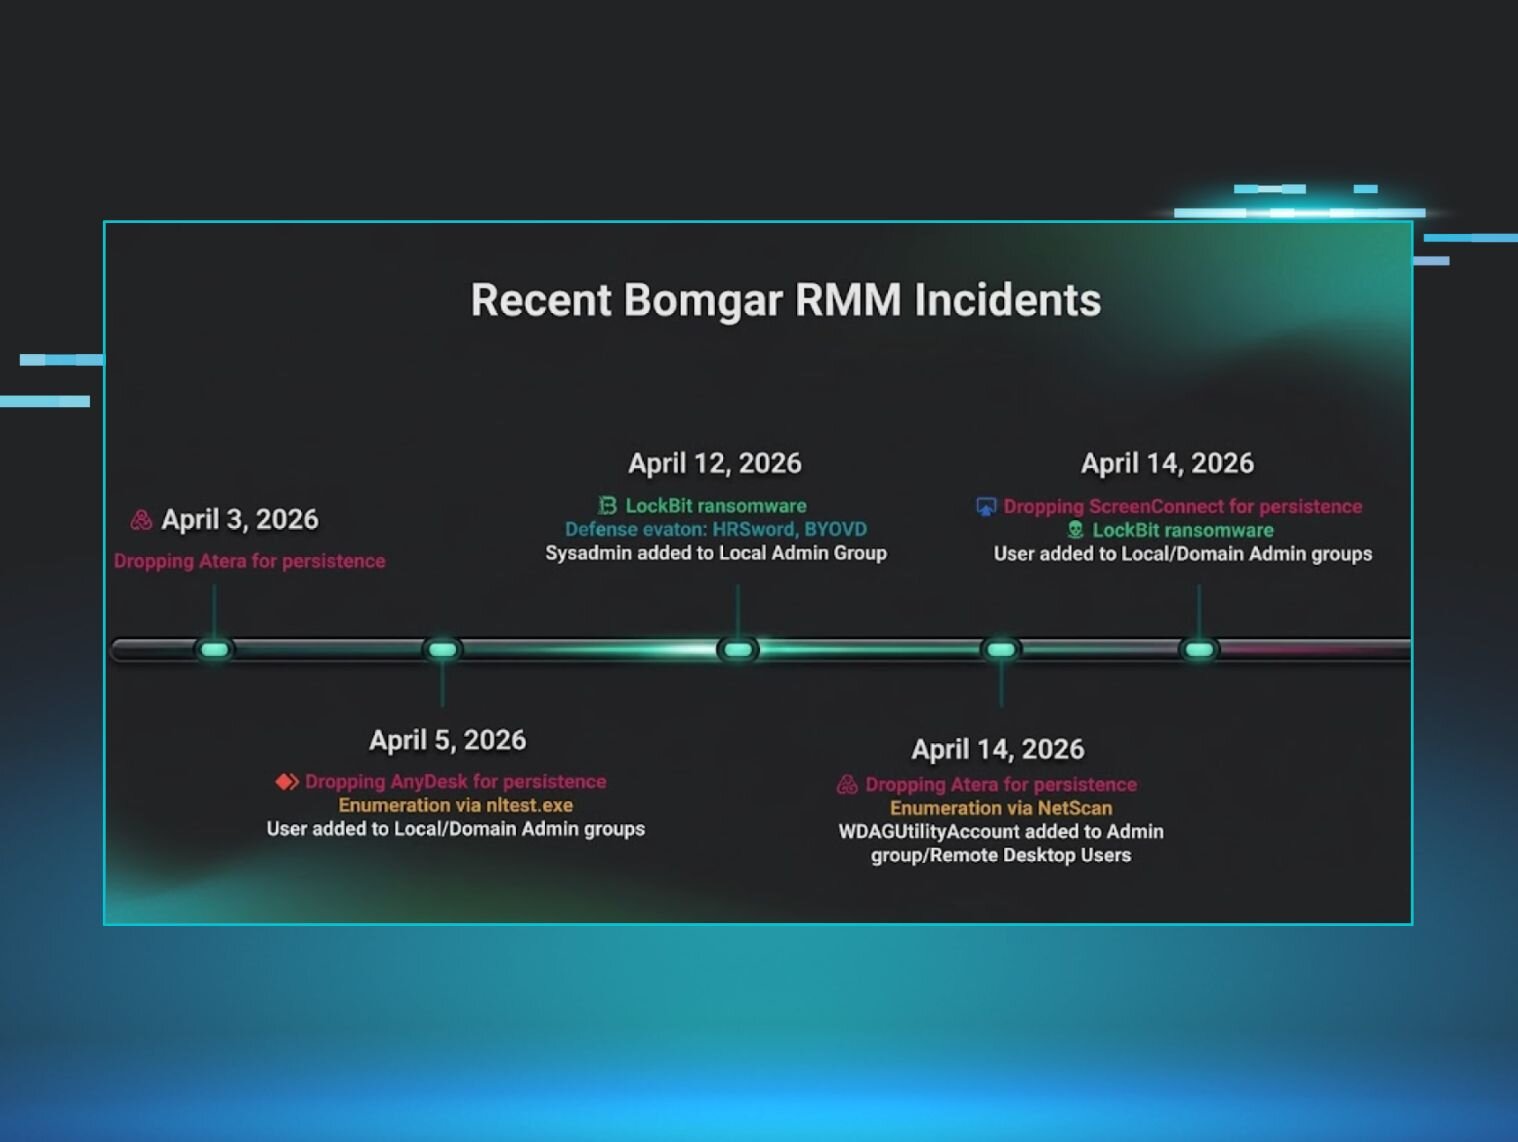
The Huntress SOC has seen a recent uptick in incidents involving compromised Bomgar remote monitoring and management (RMM) instances.
The Huntress SOC has seen a recent uptick in incidents involving compromised Bomgar remote monitoring and management (RMM) instances.
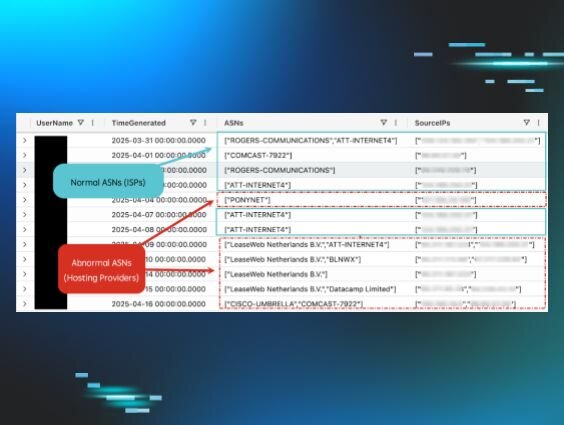
IP addresses are useful in investigations. Autonomous System Numbers give you the full picture: origin, ownership, and network context. Here's how Huntress uses ASNs to accelerate hunting and response.
What started as a brute force investigation turned into something more interesting. Huntress documents how ransomware initial access brokers operate and what they look like in real-world telemetry.
Most incident write-ups present a clean timeline. This one doesn't — it takes the analyst's perspective, including the dead ends, the surprises, and the moments of genuine uncertainty. Here's what really happened.
Threat actors rarely innovate. This one did. A November 2024 Huntress SOC investigation uncovered novel tradecraft for persistence and remote access that hadn't been documented before.
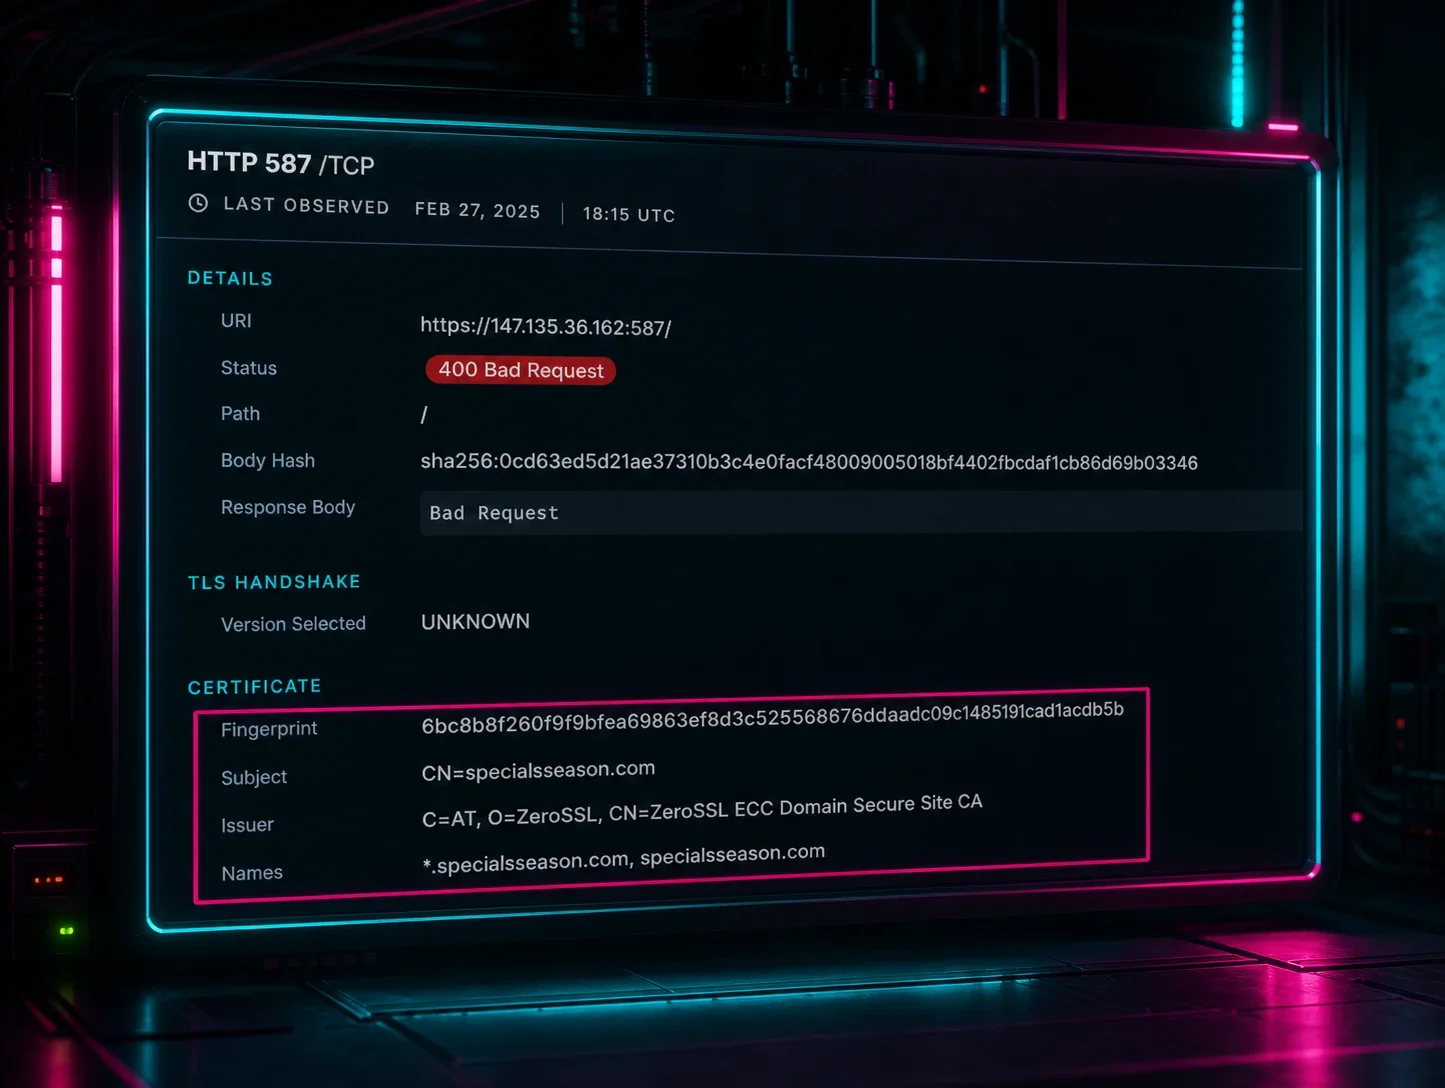
Shodan.io is more than a search engine for exposed services. Here's how Huntress uses Shodan banner data and screenshots to track down and map ransomware group infrastructure.
The Huntress Security Operations Center (SOC) will walk you through every heart-pounding moment of a recent major cyber incident—from the vulnerability that kicked it off, to the moment they kicked the threat actors out. They’ll also answer your questions about threat hunting, incident response, and anything else.
