

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
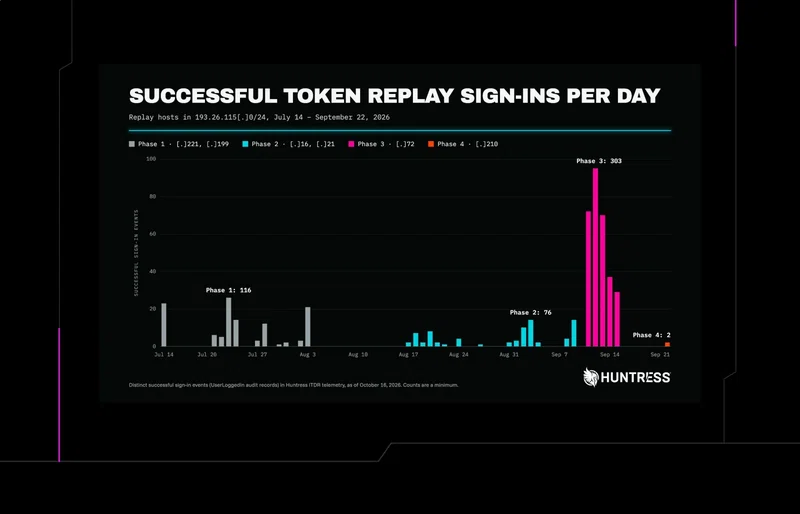
Huntress tracked a 10-week Microsoft 365 campaign pairing AiTM relays with token replay, rogue Entra devices, MFA tampering, and hidden inbox rules.
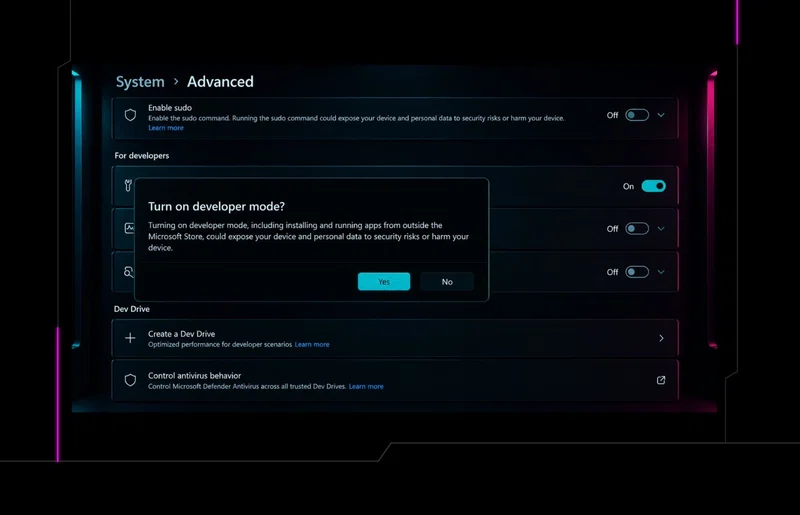
A sideloaded package turns a Microsoft-signed binary into an OAuth token theft tool. No phishing domain, no spoofed UI, no browser. Here's how to detect it.
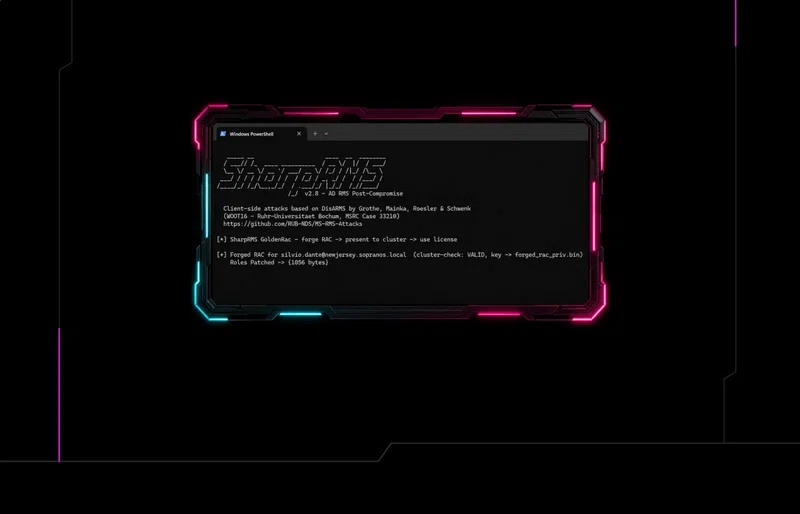
An AD RMS Service Group account exports the AD RMS Server Licensor Certificate private key. That 1172-byte key decrypts every document the deployment ever protected, offline, and keeps doing so after the deployment is rebuilt.
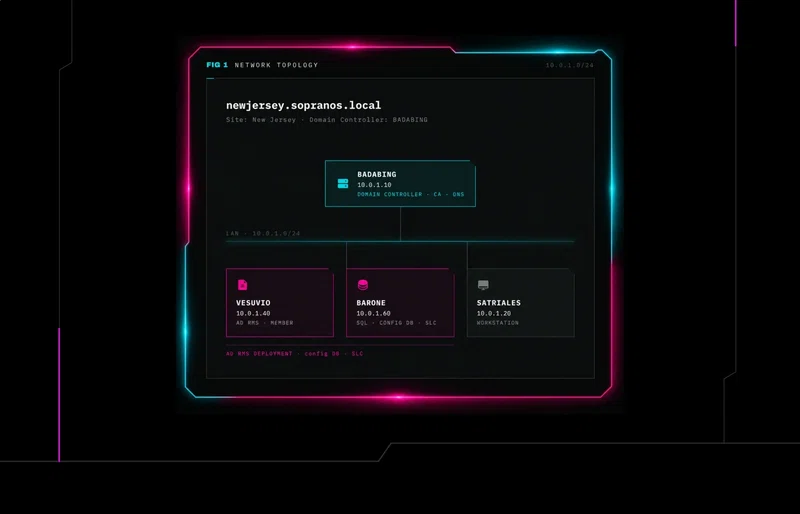
Active Directory Rights Management Services still ships in Windows Server 2025, years after Microsoft began steering customers to the cloud, and it remains fully supported on-premises. Part 1 maps the AD RMS trust model (the Server Licensor Certificate, the license flow, the SOAP surface) and shows how to discover an RMS deployment, fingerprint an AD RMS-protected file, and trace the path to that certificate's private key.
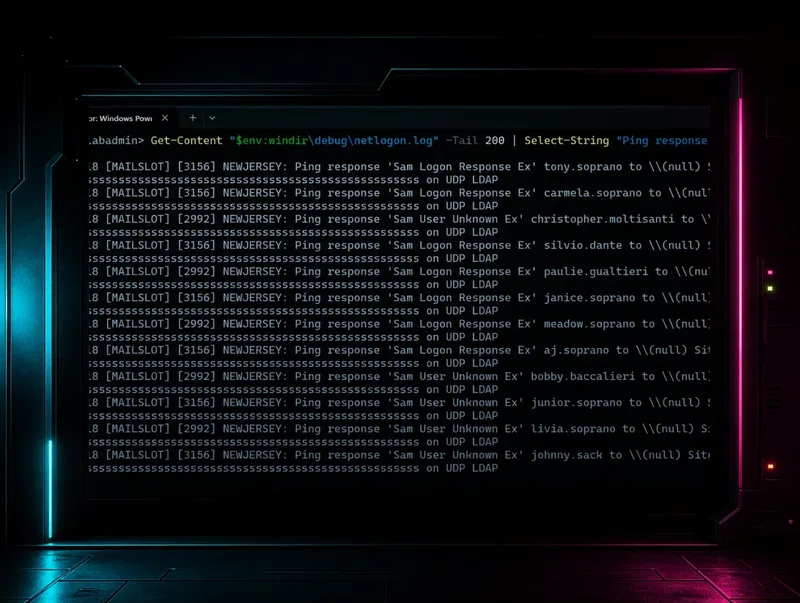
ldapnomnom claims it leaves no Windows audit logs. This post shows why Event 1644 misses LDAP Ping and where defenders can still catch it.
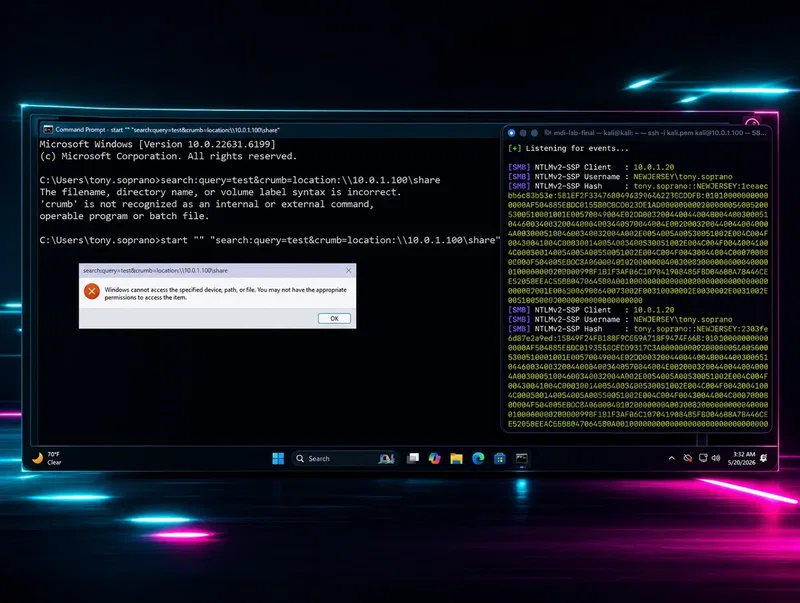
The same NTLM leakage primitive that got patched in the Snipping Tool exists in Windows Explorer's search: handler. No CVE. No fix. If your patching relies on CVE coverage, you have a blind spot.
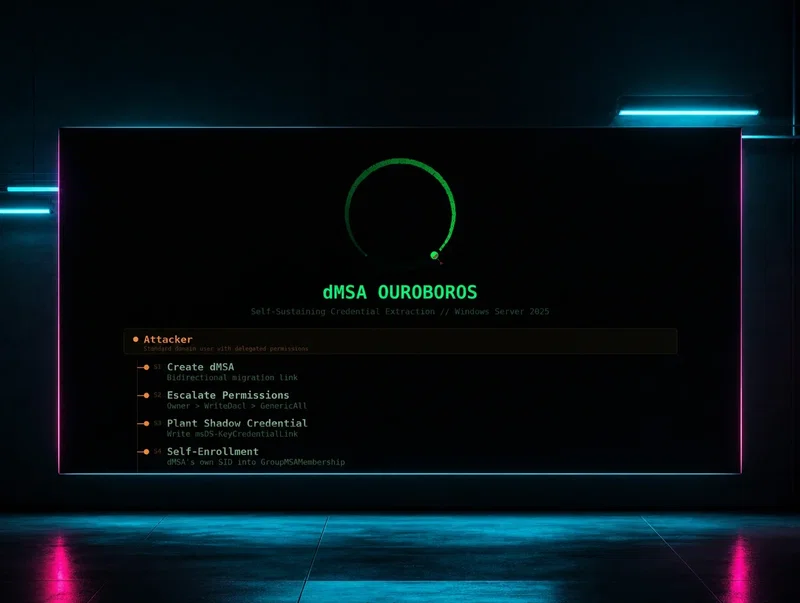
A fully patched Windows Server 2025 domain is vulnerable to dMSA Ouroboros—a self-sustaining credential extraction technique requiring only standard delegated permissions. Learn how it works, why remediation fails, and how to detect it.
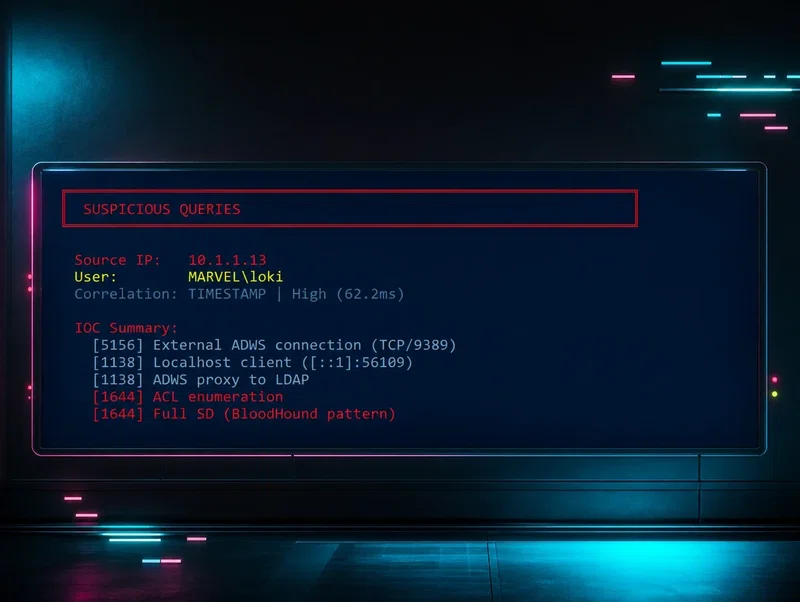
Discover a method for attributing Active Directory Web Services (ADWS) queries, which normally appear to originate from "localhost" in Event 1644 logs, back to the attacker's true source IP address. This is accomplished by correlating the timing of the inbound network connection event (Event 5156), which contains the real source IP, with Event 1644 within a consistent 60–80ms window.
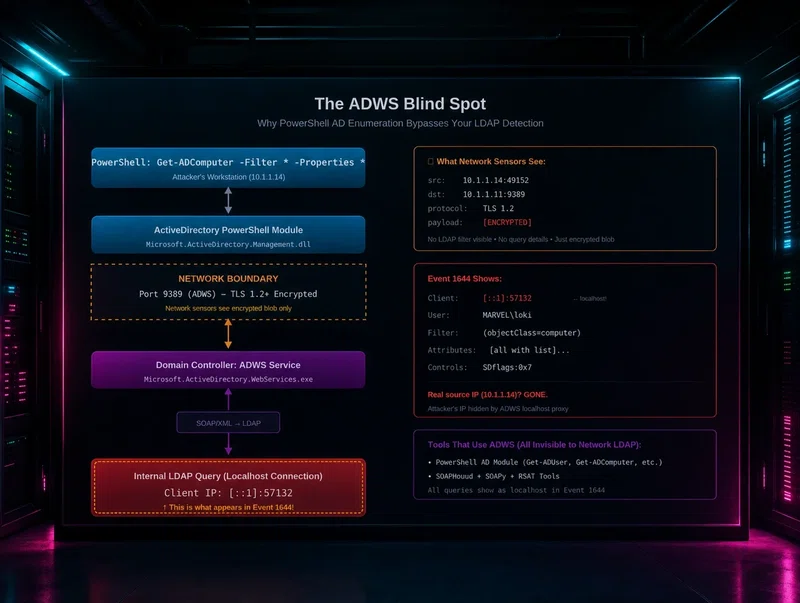
PowerShell AD enumeration bypasses network detection by using ADWS (port 9389), logging the LDAP query (Event 1644) as localhost (::1). High-fidelity detection requires correlating Event 1644 with ADWS connection events by Operation ID to reveal the remote source and spot bulk property dumps indicated by [all_with_list].
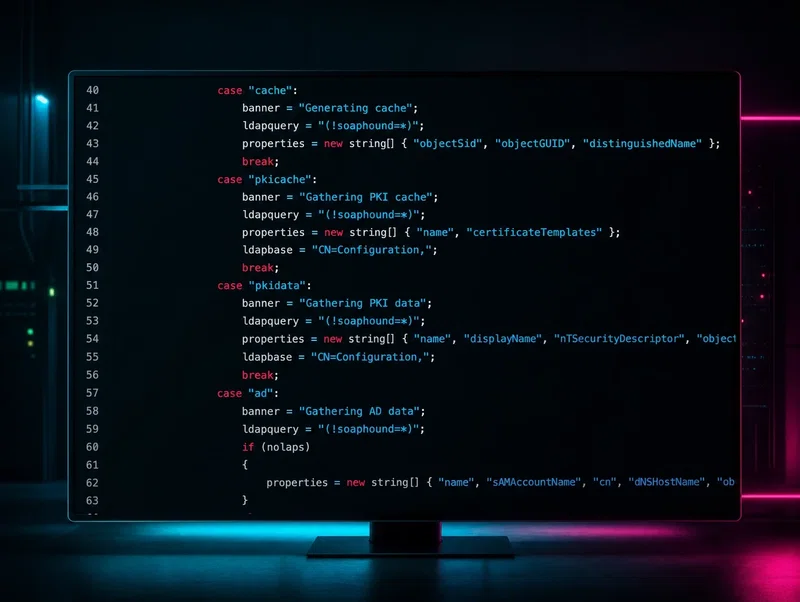
SOAPHound uses a (!FALSE) LDAP filter pattern that breaks most detection rules. Part 4 of our detection engineering series shows exactly how to hunt for it before attackers use the blind spot.
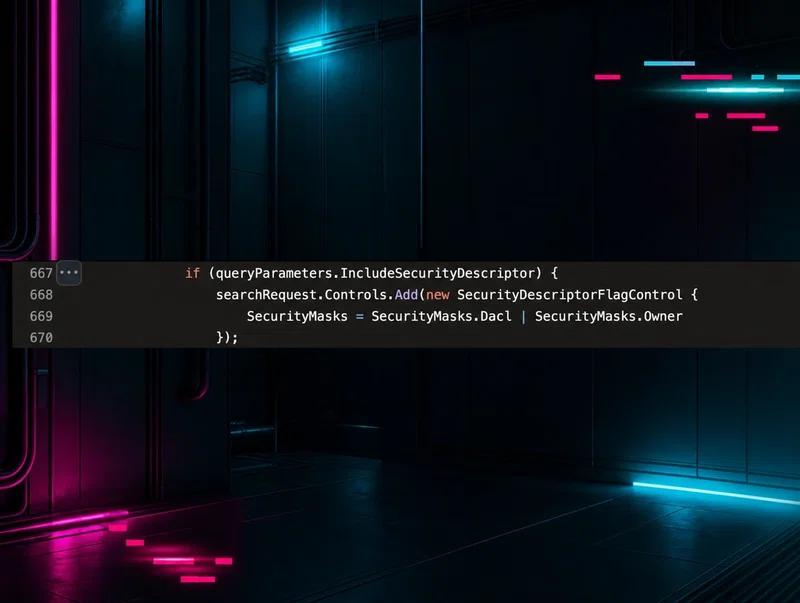
SDFlags is an LDAP parameter most defenders walk right past in their logs. It's also how attackers enumerate permissions while evading detection. Part 3 of our series covers what Huntress found.
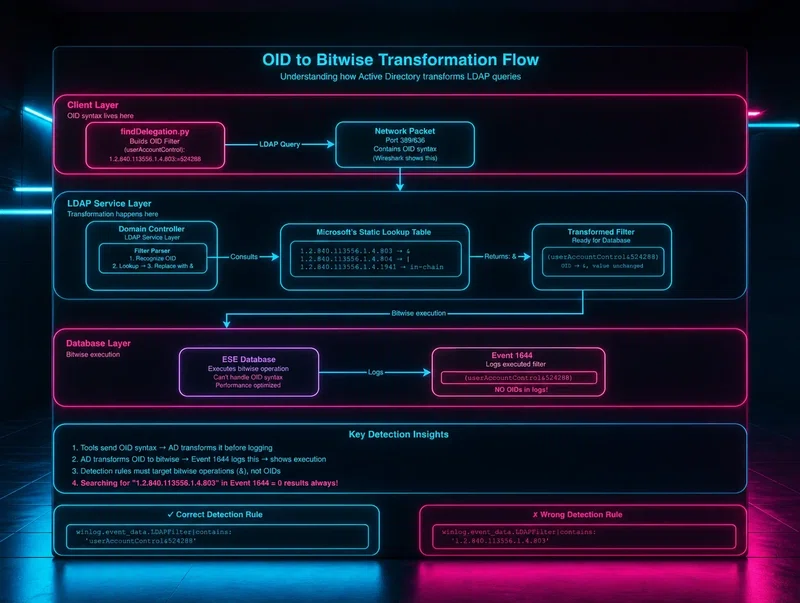
The detection logic was solid, the rules were deployed, and then a 2am Slack message revealed that whitespace variations in LDAP filters were breaking everything. Read Part 2 of our detection engineering series.
The gap between what attacker code looks like and what it actually logs is where most detections fail. Part 1 starts by reading the attacker's own source code.
The Kerberos Diamond Ticket has been undervalued since its original proof of concept. Huntress gives it the analysis it deserves, and explains why attackers are starting to take it seriously.
A tool called 'defendnot' disables Windows Defender by registering a fake antivirus through undocumented Windows Security Center APIs. Huntress covers the technique and how to detect it.

