

Threat Research
Threat Research is where the Huntress SOC shows its work. We cover real intrusion investigations, malware and ransomware analysis, threat actor profiles, and the tradecraft attackers lean on: persistence, defense evasion, and living-off-the-land techniques. Whether it broke this week or has been around for years, this is where you see how attacks unfold and how we stop them.

The Latest Threat Research Blog Posts

Beyond the clipboard: The evolving tradecraft of ClickFix
Beyond the clipboard: The evolving tradecraft of ClickFix
Nov 10, 2026
Inside an AhsayCBS Intrusion: Hidden Webshells, a CryptoMiner, and a C2 Implant
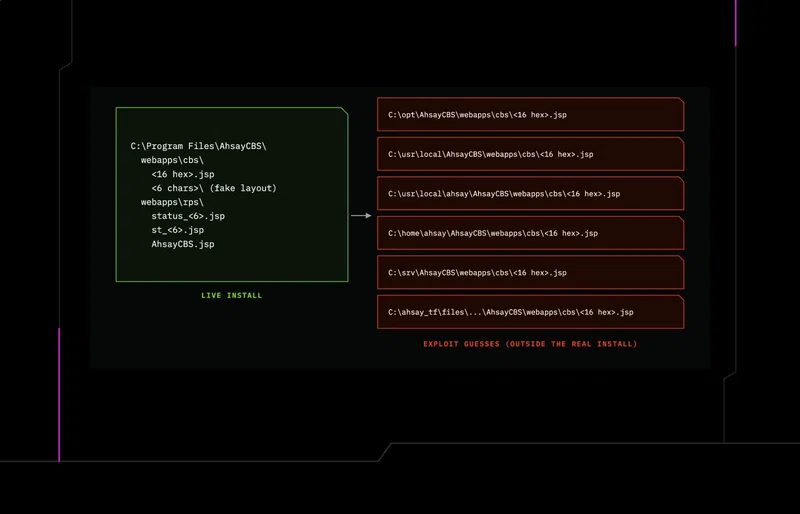
Inside an AhsayCBS Intrusion: Hidden Webshells, a CryptoMiner, and a C2 Implant
Nov 9, 2026
Managed for Malice: How Attackers Turn MDM into Remote Access
Managed for Malice: How Attackers Turn MDM into Remote Access
Oct 28, 2026
AI, Scripts, Operator - Inside the ConnectWise Attack
AI, Scripts, Operator - Inside the ConnectWise Attack
Oct 26, 2026
Unboxing Phishing Kits: Advanced Cred Theft for Entry-Level Hackers
Unboxing Phishing Kits: Advanced Cred Theft for Entry-Level Hackers
Oct 22, 2026
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Oct 22, 2026
Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Oct 21, 2026
ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Oct 16, 2026
Clean Install, Stolen Creds: Fake WatchGuard VPN Site Serves Genuine Signed Client
Clean Install, Stolen Creds: Fake WatchGuard VPN Site Serves Genuine Signed Client
Oct 13, 2026
Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Oct 7, 2026
Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack
Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack
Oct 6, 2026
