Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Attackers are using cloud-hosted and on-premise ScreenConnect panels to install rogue clients on hundreds of managed endpoints.
UPDATE: N-able took N-central offline after 33 critical flaws were disclosed, including chains enabling remote code execution and privilege escalation.
Two critical PHP RCEs, CVE-2026-109618 and CVE-2026-109619, leaked before the patch. Learn what's known, who's exposed, and how to prepare now.
Threat actors are exploiting AhsayCBS flaws, including CVE-2026-105133 and CVE-2026-105134, to deploy webshells and XMRig cryptominers. Update to 10.3.4 and restrict access now.
UPDATED: Critical vulnerability in N-able N-central gives attackers unauthenticated, "god-mode" access to the RMM console.
UPDATED: PaperCut NG and PaperCut MF are under active exploitation. Huntress reproduced a pre-auth RCE chain and shares urgent patching, exposure, and detection guidance.
Huntress has observed a series of strikingly similar intrusions beginning with CitrixBleed 2 exploitation, employing novel local privilege escalation techniques, and ending in Dragonforce ransomware.
Huntress was one of many vendors impacted by a recent incident at Klue. We dug into the incident to figure out what happened.
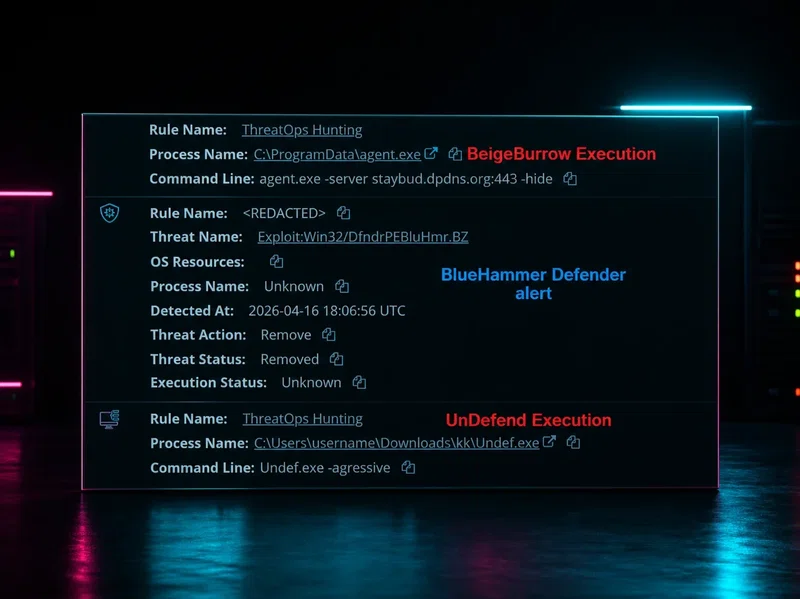
Huntress observed in-the-wild use of Nightmare-Eclipse tooling, including BlueHammer, RedSun, and UnDefend, in a live intrusion involving FortiGate VPN compromise as the initial access, reconnaissance commands, and likely tunneling activity.
An NPM supply chain attack struck the ubiquitous open-source axios library and Huntress has observed over a hundred affected devices.
Huntress observed active exploitation of SolarWinds Web Help Desk across three customers — with attackers deploying Cloudflare tunnels and Velociraptor for persistence immediately after getting in.
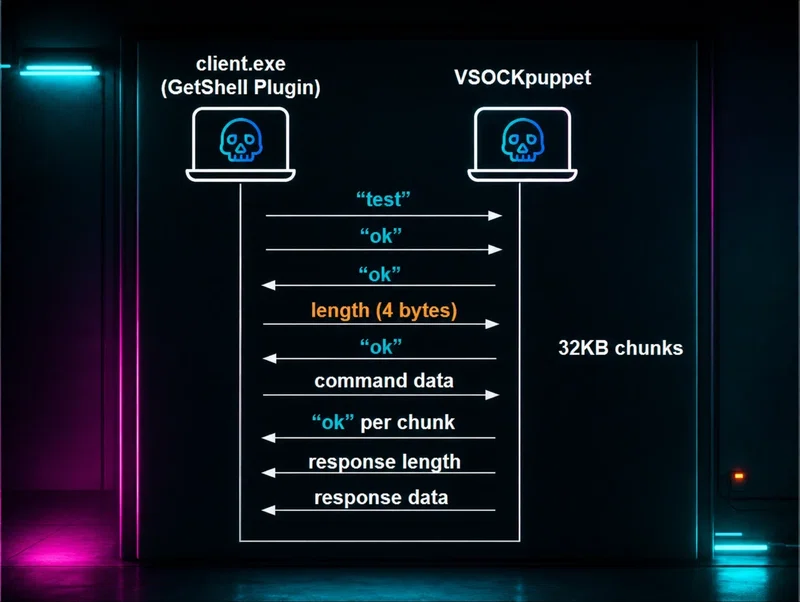
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.
Gladinet CentreStack is being actively exploited, with the cl0p ransomware group now reportedly targeting internet-facing servers. Huntress has been tracking this from the start and has the latest updates.
Huntress is seeing threat actors exploit React2Shell (CVE-2025-55182) to deploy a Linux backdoor, a reverse proxy tunnel, and a Go-based post-exploitation implant.
Huntress observed threat actors exploiting a Microsoft WSUS remote code execution vulnerability across four customers within days of disclosure. Here's the timeline, the TTPs, and why you need to patch now.