

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Threat actors are now using AI to generate custom PowerShell scripts for Active Directory attacks. Our team analyzed real vibe-coded malware and what it means for defenders.
Tools built to monitor employees and support remote workers are being repurposed for ransomware operations. Net Monitor for Employees and SimpleHelp are the latest to be abused — here's how.
They got in through SonicWall, then deployed a forensic tool's signed driver to kill endpoint security from kernel mode. Huntress disrupted the attack before ransomware deployed. Here's the full breakdown.
The AI-powered cyberattack apocalypse didn't happen in 2025. What did happen was quieter and more dangerous: attackers got faster and cheaper at the tradecraft they were already running.
During a ransomware intrusion, Huntress found a script full of clear English comments walking through each step. Old playbooks don't die. Attackers just keep running them.
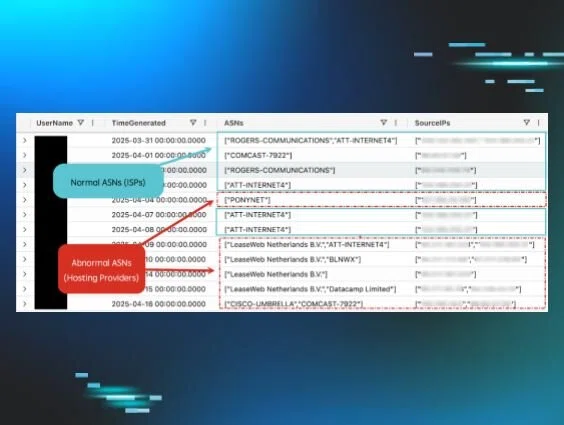
IP addresses are useful in investigations. Autonomous System Numbers give you the full picture: origin, ownership, and network context. Here's how Huntress uses ASNs to accelerate hunting and response.
What started as a brute force investigation turned into something more interesting. Huntress documents how ransomware initial access brokers operate and what they look like in real-world telemetry.
Most incident write-ups present a clean timeline. This one doesn't — it takes the analyst's perspective, including the dead ends, the surprises, and the moments of genuine uncertainty. Here's what really happened.
When Microsoft blocked macros in downloaded Office documents, threat actors adapted quickly. Huntress tracks how initial access methods evolved in 2022 and what defenders need to watch for now.
Part three of Huntress' defense evasion series gets spicy. Attackers have to get in and run code somewhere, and defenders can catch them. Here's exactly how to spot evasion techniques in action.
While investigating an intrusion, Huntress found a technique that doesn't dump stored credentials. It captures them in real time as users type their passwords. Here's how NPPSpy does it.
One of the earliest lessons in incident response: a polished report that can't be defended under pressure isn't actually a good report. Here's how Huntress thinks about triangulating evidence to make claims that hold.
Defense evasion is stressful when you're on the receiving end. Part two of Huntress' series goes deep on the mechanics, using real cases from the Huntress SOC to show how evasion actually plays out.
Catching an attacker mid-campaign is only half the battle. Here's the part most incident response guides skip: what to actually do once you've found them and how to make sure they don't come back.
Staying hidden is just as important to an attacker as getting in. Defense evasion is the broad category of techniques that help them do it, and most security stacks aren't watching for it directly.

