

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
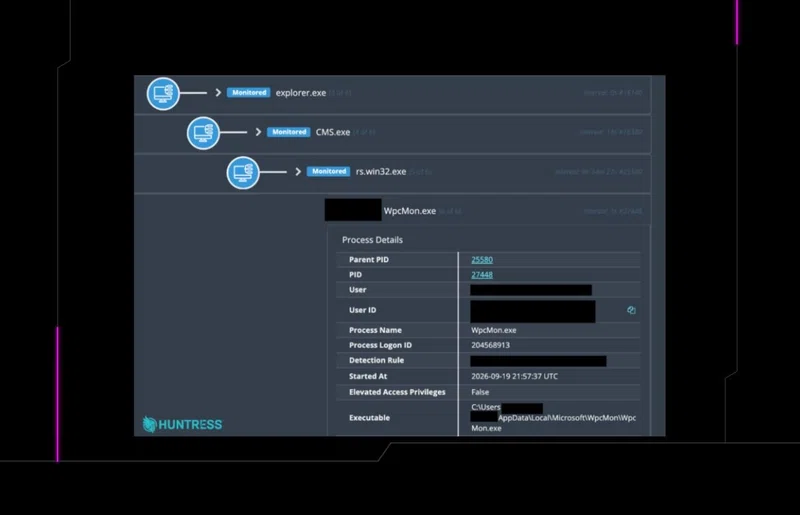
Attackers compromised camera management software to deploy malware, establish persistence, and beacon to C2. Huntress breaks down the attack chain and IOCs.
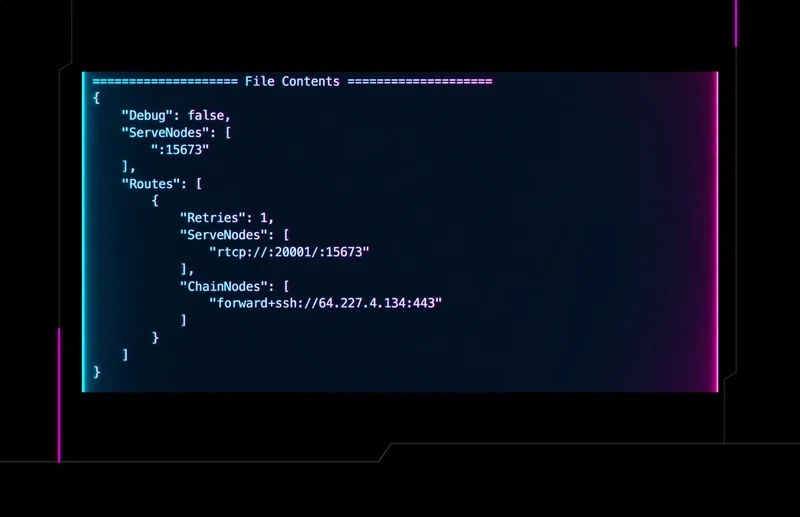
How Huntress researchers reconstructed an Akira ransomware attack using Registry artifacts, Akira logs, and other post-compromise evidence.
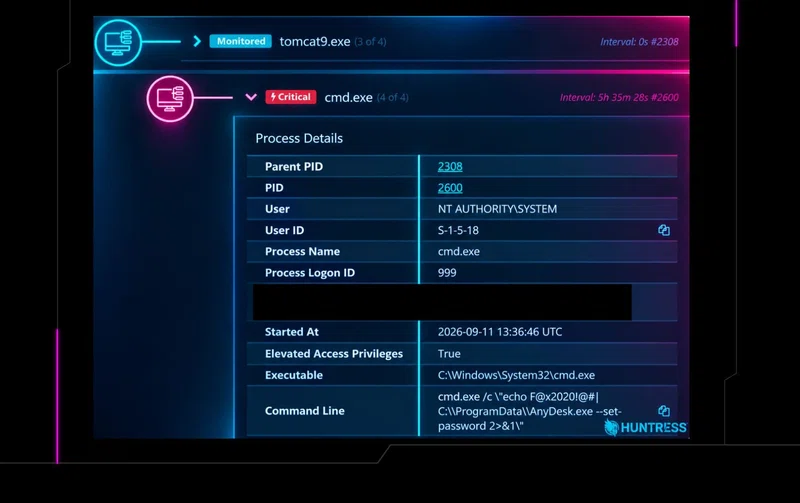
Threat actors exploited Samsung MagicINFO to install AnyDesk, disable Defender, and compile a Monero miner directly on a victim endpoint. Learn the detection signals.
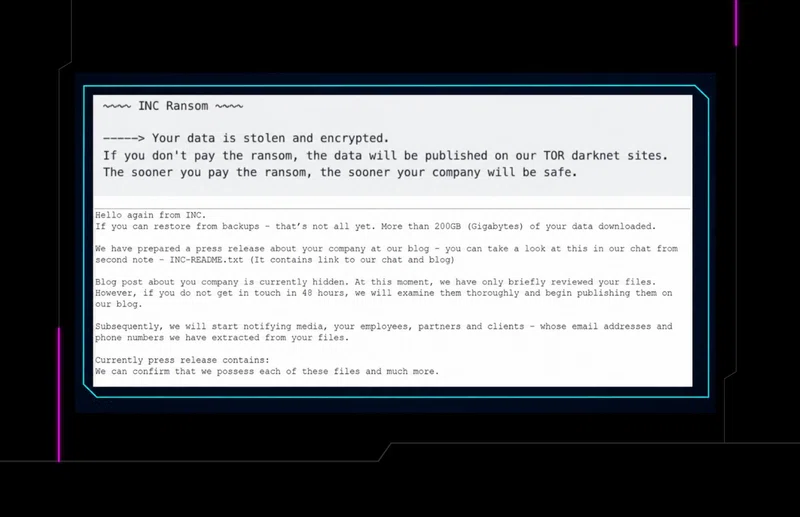
Huntress analysts reconstructed a three-week INC ransomware attack from endpoint data, uncovering a 17-day lull despite missing process telemetry.
Huntress has recently seen two incidents involving Settra, a ransomware variant that was first publicly reported in June 2026.
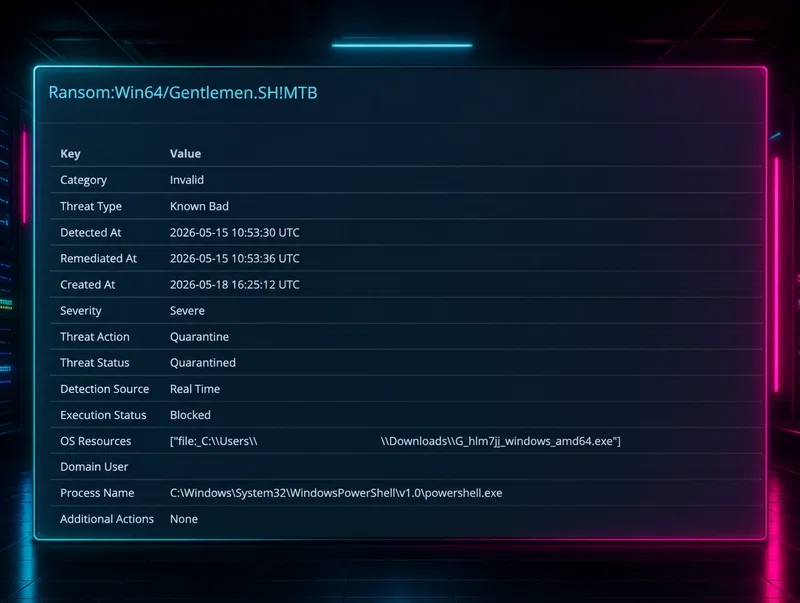
Two recent incidents involving The Gentlemen ransomware show the use of defense evasion tactics, including logs being cleared and attempts to add antivirus exclusions.
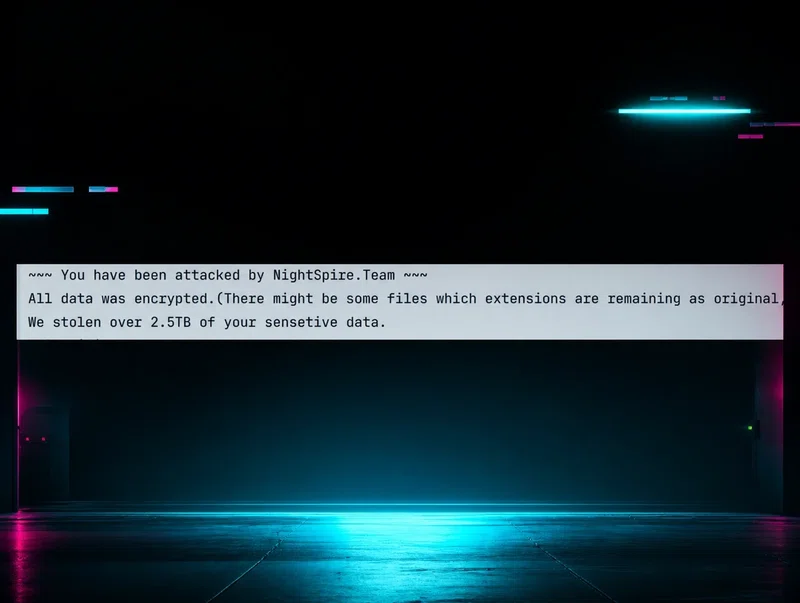
A recent investigation into a NightSpire ransomware incident found significant variations in TTPs—including the use of "trucked-in" non-native tools like Chrome Remoting Desktop and MEGASync—which suggests affiliate involvement and demonstrates that IoCs aren't static, regardless of the group's RaaS status.
Threat actors got creative with data staging and exfiltration — and in doing so, left their entire infrastructure exposed. Here's what Huntress SOC analysts documented.
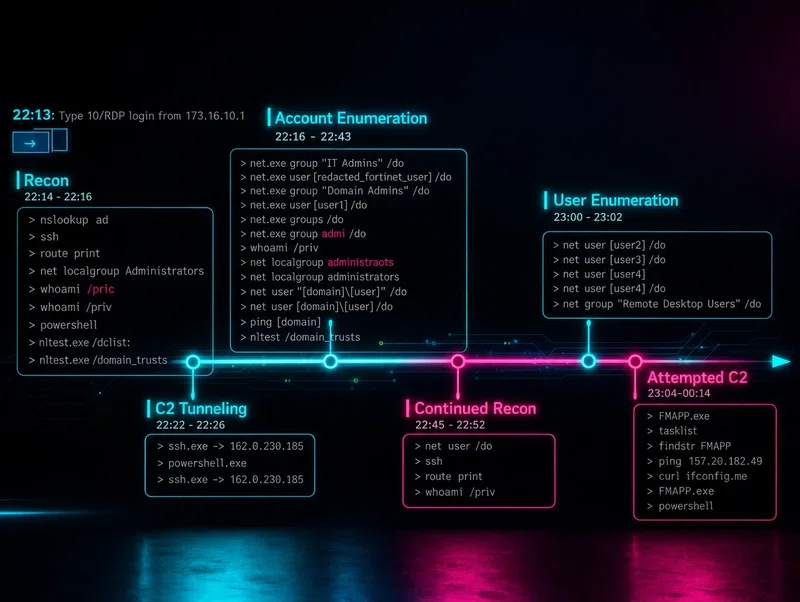
Huntress traced a full Iranian-linked APT intrusion from RDP initial access through DLL side-loading and C2 communications. This is the complete MuddyWater attack chain, step by step.
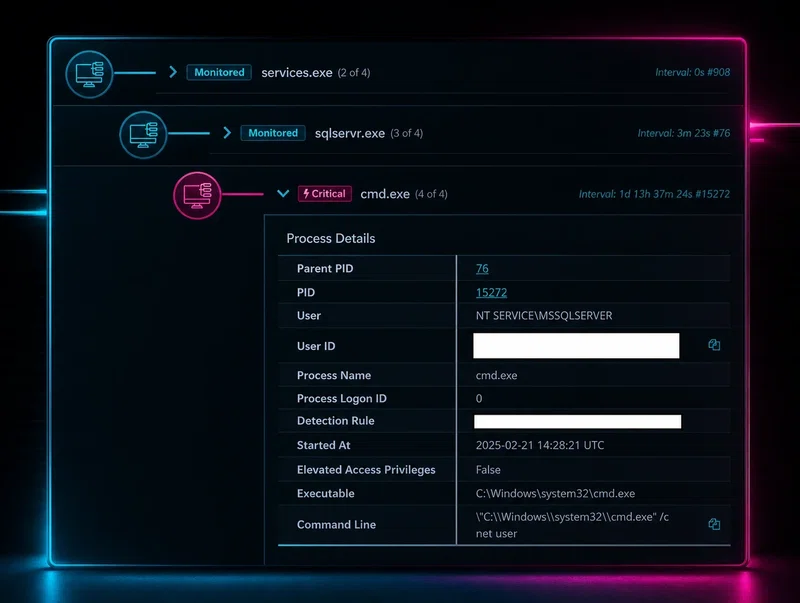
A business-critical construction accounting app quietly installed additional software alongside itself — and that software became an attack vector. Here's what the Huntress SOC team found.
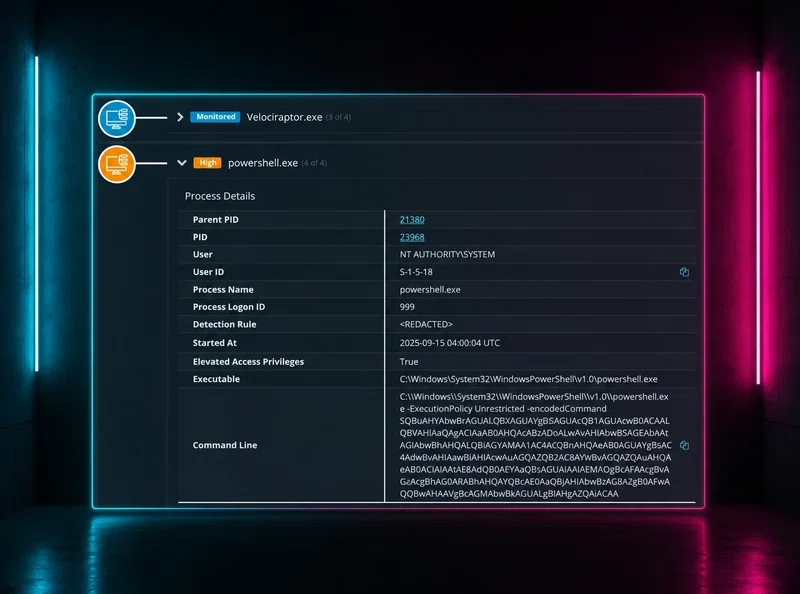
The threat actors from Part I weren't done. Part II tracks what happened after WSUS exploitation put a legitimate forensic tool in the wrong hands and how Huntress responded.
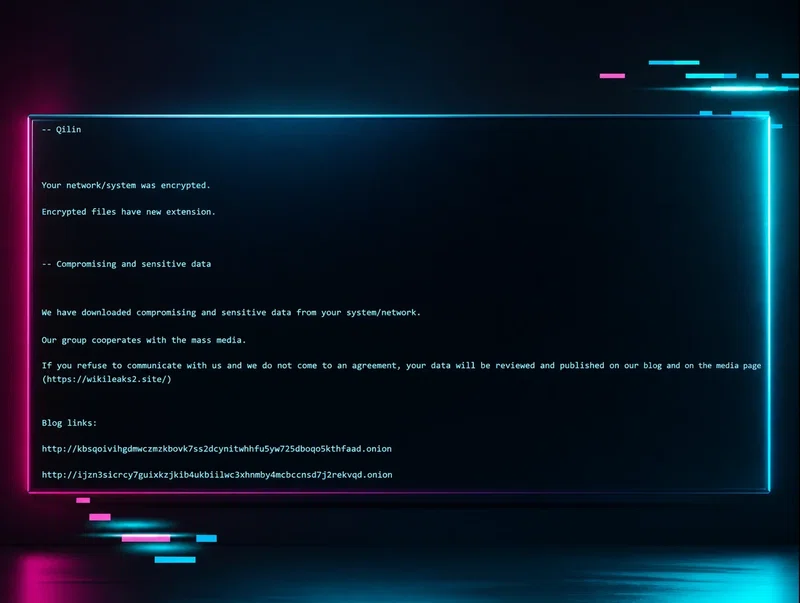
Investigating a Qilin ransomware attack with limited visibility is like piecing together a crime scene through a pinhole. Huntress shows what you can still figure out and what you'll miss.
Huntress analysts found a ransomware variant no one had documented before. Obscura hit multiple hosts across a network before anyone had a name for it. Here's the full breakdown.
Huntress came across a ransomware variant no one had documented. Cephalus hit two environments via RDP and compromised accounts without MFA. Here's what analysts found inside.
Before ransomware encrypts files, attackers stage and exfiltrate data for double extortion. Huntress breaks down the living-off-the-land binaries and TTPs threat actors use to do it quietly.

