

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Huntress has observed a series of strikingly similar intrusions beginning with CitrixBleed 2 exploitation, employing novel local privilege escalation techniques, and ending in Dragonforce ransomware.
Tools built to monitor employees and support remote workers are being repurposed for ransomware operations. Net Monitor for Employees and SimpleHelp are the latest to be abused — here's how.
The AI-powered cyberattack apocalypse didn't happen in 2025. What did happen was quieter and more dangerous: attackers got faster and cheaper at the tradecraft they were already running.
Real incident investigations don't look like the polished threat reports. Logs are missing, timing is off, and analysts have to work with gaps. This is about doing good IR with imperfect data.
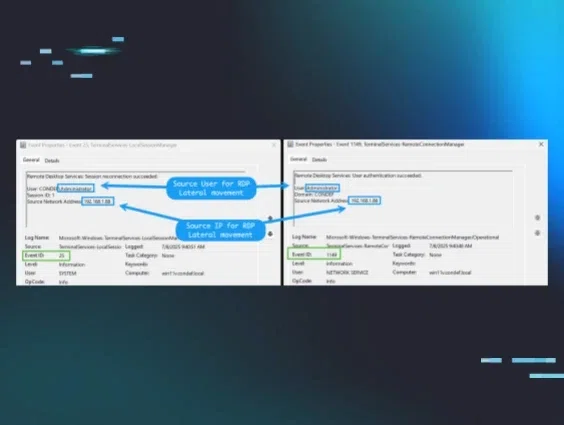
Hundreds of Windows event IDs across thousands of endpoints — most write-ups tell you which ones matter. This post is about developing a methodology for finding the needle in the haystack.
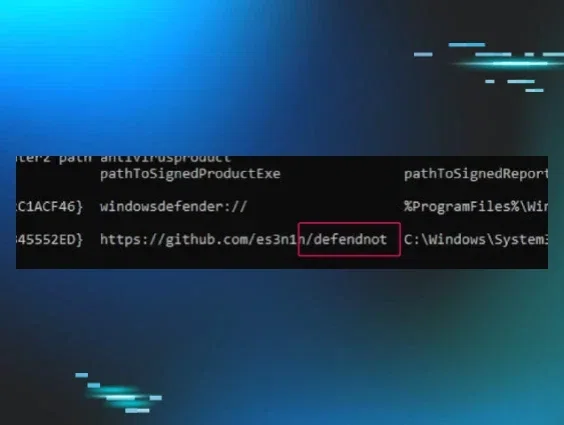
A tool called 'defendnot' disables Windows Defender by registering a fake antivirus through undocumented Windows Security Center APIs. Huntress covers the technique and how to detect it.
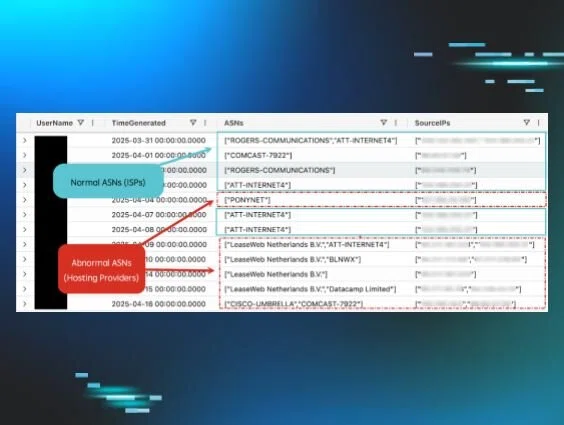
IP addresses are useful in investigations. Autonomous System Numbers give you the full picture: origin, ownership, and network context. Here's how Huntress uses ASNs to accelerate hunting and response.
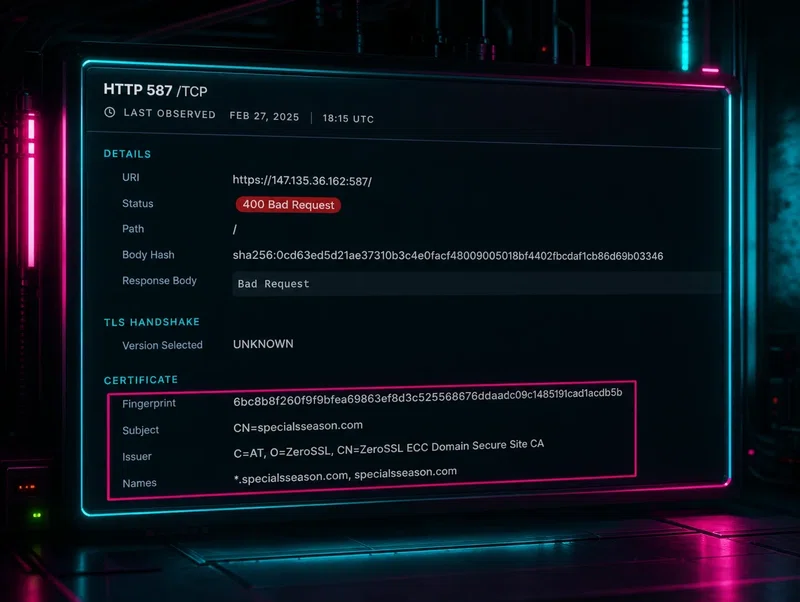
What started as a brute force investigation turned into something more interesting. Huntress documents how ransomware initial access brokers operate and what they look like in real-world telemetry.
Most incident write-ups present a clean timeline. This one doesn't — it takes the analyst's perspective, including the dead ends, the surprises, and the moments of genuine uncertainty. Here's what really happened.
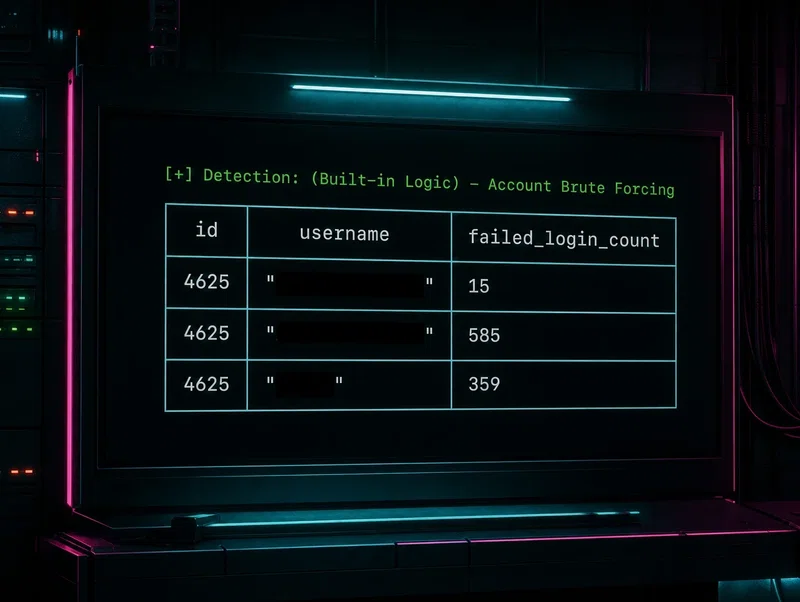
Initial access is the most important phase of any attack. Nothing else happens without it. Huntress analyzes MITRE ATT&CK's 10 initial access techniques and what to actually instrument.
Microsoft itself was hit by Midnight Blizzard's password spraying. Huntress covers what the technique looks like in Microsoft 365 telemetry, and how to hunt for it in your own environment.

