

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
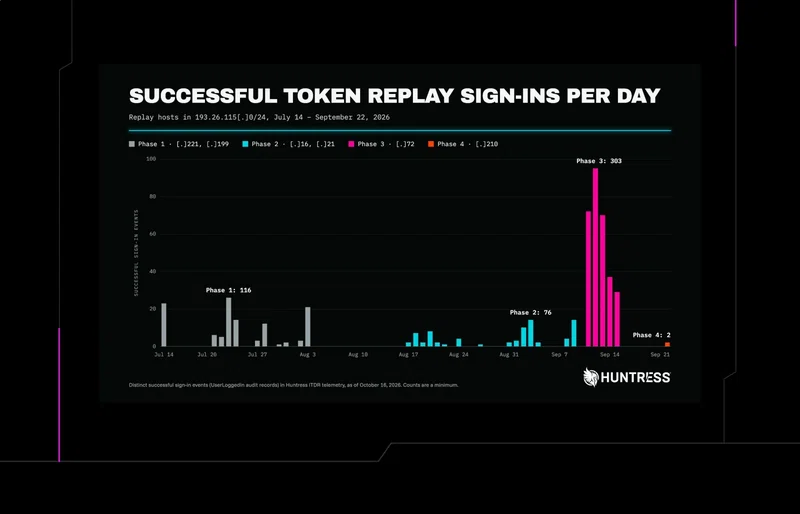
Huntress tracked a 10-week Microsoft 365 campaign pairing AiTM relays with token replay, rogue Entra devices, MFA tampering, and hidden inbox rules.
A sideloaded package turns a Microsoft-signed binary into an OAuth token theft tool. No phishing domain, no spoofed UI, no browser. Here's how to detect it.
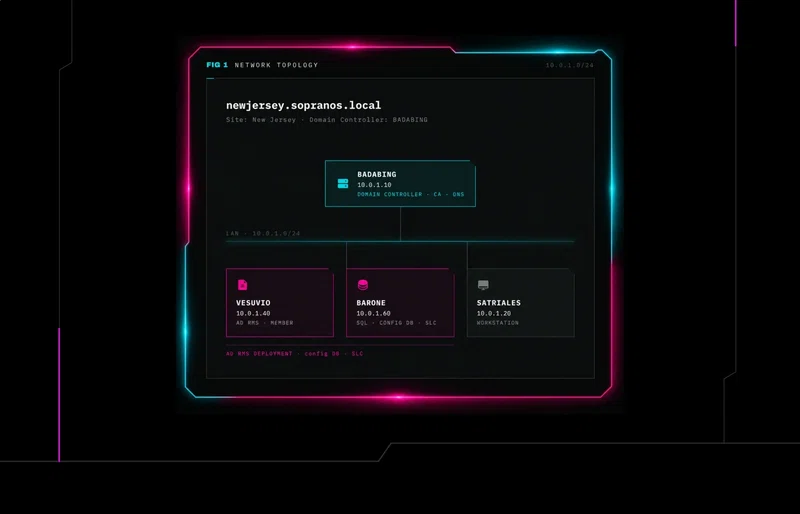
Active Directory Rights Management Services still ships in Windows Server 2025, years after Microsoft began steering customers to the cloud, and it remains fully supported on-premises. Part 1 maps the AD RMS trust model (the Server Licensor Certificate, the license flow, the SOAP surface) and shows how to discover an RMS deployment, fingerprint an AD RMS-protected file, and trace the path to that certificate's private key.
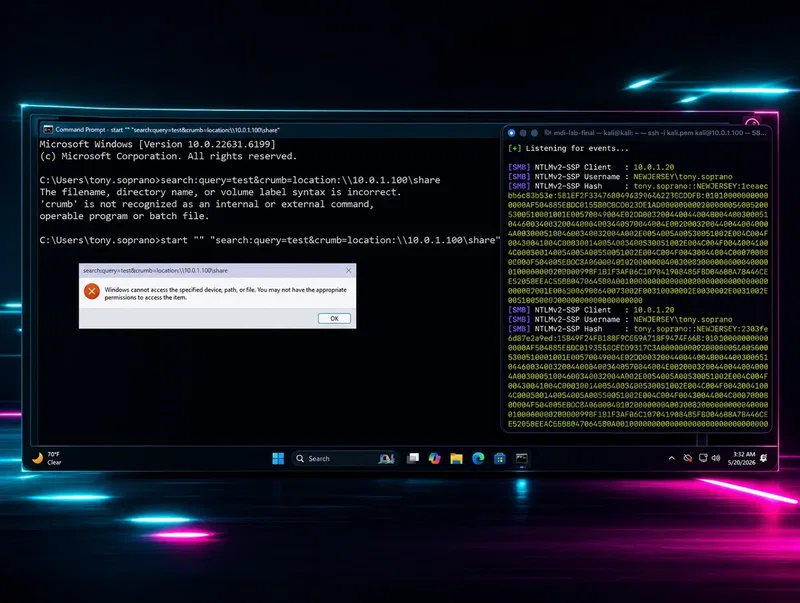
The same NTLM leakage primitive that got patched in the Snipping Tool exists in Windows Explorer's search: handler. No CVE. No fix. If your patching relies on CVE coverage, you have a blind spot.
A fully patched Windows Server 2025 domain is vulnerable to dMSA Ouroboros—a self-sustaining credential extraction technique requiring only standard delegated permissions. Learn how it works, why remediation fails, and how to detect it.
The Kerberos Diamond Ticket has been undervalued since its original proof of concept. Huntress gives it the analysis it deserves, and explains why attackers are starting to take it seriously.
A tool called 'defendnot' disables Windows Defender by registering a fake antivirus through undocumented Windows Security Center APIs. Huntress covers the technique and how to detect it.
A Huntress purple teamer asked what Windows Performance Monitor is good for — then found a way to use it for Kerberos telemetry that detection vendors hadn't considered. Spoiler: PerfMon is not useless.

