
Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
Welcome to the Huntress Cybersecurity Blog, where we cut through the noise with real-world tradecraft to help you stay ahead of today’s threat actors. Our authors bring diverse backgrounds and hands-on experience to make cybersecurity education engaging, accessible, and grounded in the threats you actually face.
Threat Research is where the Huntress SOC shows its work. We cover real intrusion investigations, malware and ransomware analysis, threat actor profiles, and the tradecraft attackers lean on: persistence, defense evasion, and living-off-the-land techniques. Whether it broke this week or has been around for years, this is where you see how attacks unfold and how we stop them.
No posts found.
When a vulnerability starts getting exploited, the clock starts. Rapid Response & Vulnerabilities covers CVE disclosures, vulnerability advisories, the exploitation activity we see in the wild, patch guidance, and disclosure timelines. Timely, focused, and built around what to do next.
No posts found.
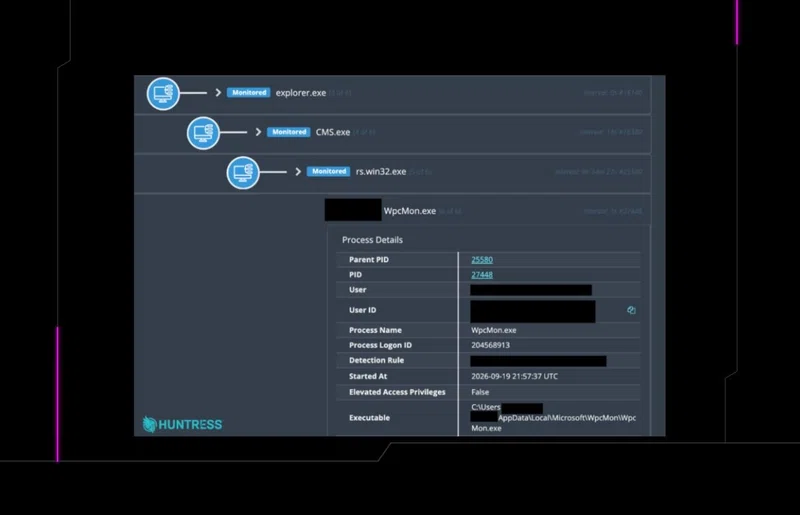
Attackers compromised camera management software to deploy malware, establish persistence, and beacon to C2. Huntress breaks down the attack chain and IOCs.
Microsoft says an AI agent drove the ConnectWise attack. Huntress telemetry is consistent with that: scripted tooling, steered by an operator.
Huntress examines 3 phishing kits that hand beginner attackers everything they need to steal tokens. See what the attacks look like from the inside.
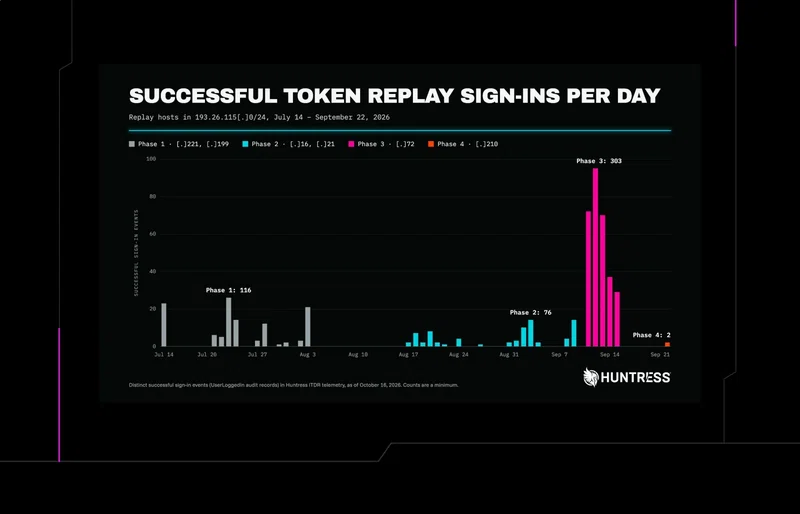
Huntress tracked a 10-week Microsoft 365 campaign pairing AiTM relays with token replay, rogue Entra devices, MFA tampering, and hidden inbox rules.
A Google search for Amazon business led to a ClickFix lure that dropped multiple malicious payloads onto the victim machine, including versions of Lumma Stealer and NetSupport Client RMM.
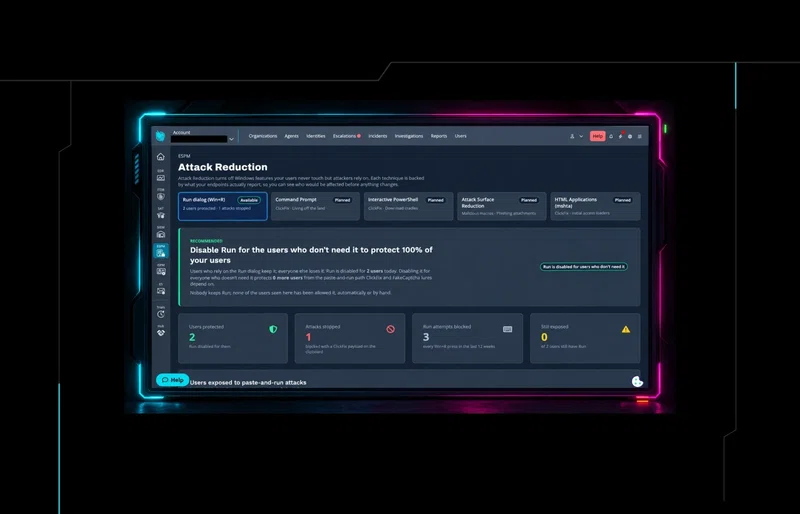
ClickFix tricks users into pasting malicious commands into the Windows Run dialog. See how Attack Reduction in Huntress ESPM helps prevent that from happening.