

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Huntress was one of many vendors impacted by a recent incident at Klue. We dug into the incident to figure out what happened.
SonicWall VPN exploitation is active, widespread, and moving fast toward Akira ransomware deployment. Huntress has been tracking this campaign in real time. Here's the full advisory with live updates.
Huntress analyzed the malware being delivered through Cleo exploitation and named it Malichus. We discuss the full technical breakdown — what Malichus does, how it persists, and how to detect it.
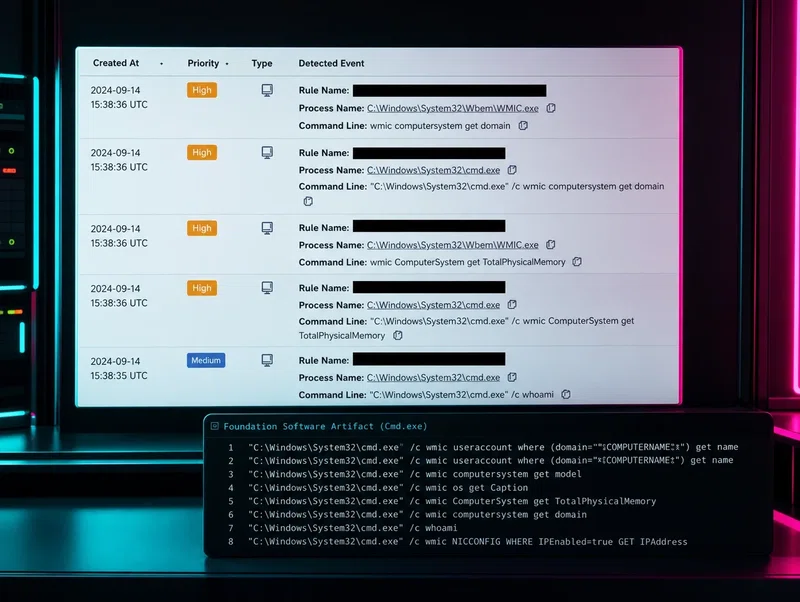
FOUNDATION Accounting Software, used widely in construction, was being brute-forced at scale using the product's default credentials. Huntress observed active intrusions across plumbing, HVAC, and concrete contractors.
Managed file transfer tools keep getting targeted, and CVE-2023-43117 in CrushFTP is the latest example. Huntress covers what MFT exploitation looks like in the wild and what defenders need to do.
Huntress has confirmed active exploitation of an improper authorization vulnerability in Atlassian Confluence, which attackers used to deploy Cerber ransomware. The report breaks down how the attack unfolded across affected environments.
A HelloKitty ransomware attack led Huntress to confirm active exploitation of CVE-2023-46604 in Apache ActiveMQ. Here's what the vulnerability allows, how it's being used, and what to do now.
Progress disclosed seven WS_FTP vulnerabilities, two of which scored above 9 on the CVSS scale. Huntress is tracking active exploitation and outlines what organizations should do right now.
CVE-2023-4863 is a critical heap buffer overflow in the libwebp library, affecting nearly every application that processes images. Huntress is tracking active exploitation in the wild. Here's what's known so far.
Huntress SOC analysts traced a cryptocurrency miner back through a TeamViewer installation. Here's how XMRig was delivered, the wallet address it was reporting to, and what organizations should check.

