

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Where do identity attacks actually come from? Not where you think. The answer isn't a country, a VPN, or a data center — and getting that wrong leaves you exposed.
If you administer a Microsoft 365 tenant, audit your OAuth applications right now. Huntress spent six months researching how malicious apps persist inside M365. Statistically, yours may already be infected.
OAuth 2.0 is everywhere, and its different implementations in Google Cloud and Azure have radically different attack surfaces. Huntress walks through a device code phishing case study across both platforms.
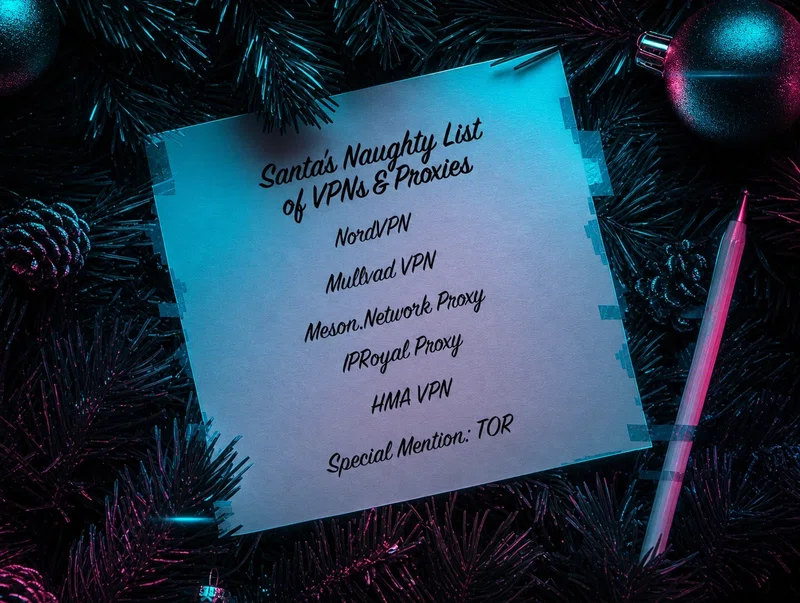
Santa's workshop has a strict policy against the Naughty List. Some VPNs and proxies are on it. Here's how businesses can tell the difference between secure network tools and ones that create risk.
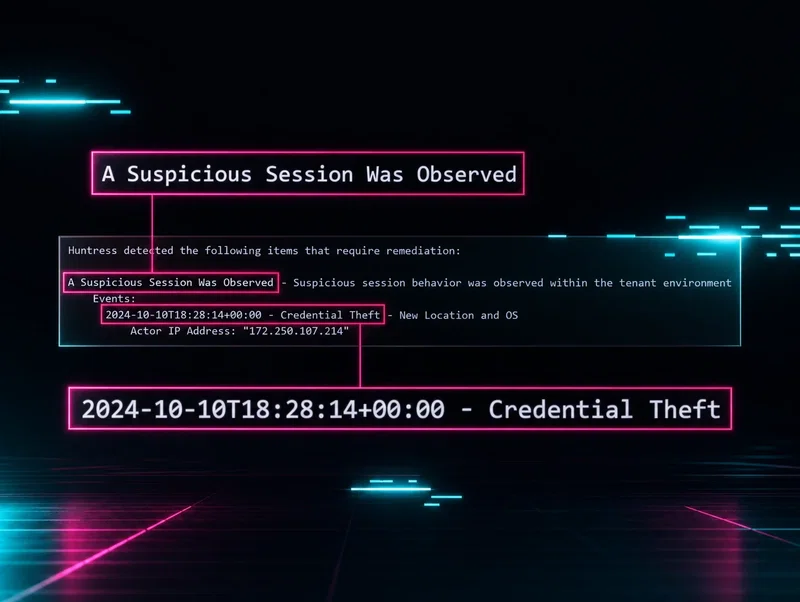
MFA feels like a Mostly Fruitless Annoyance until you understand how cleanly it divides the identity attack surface. Here's what happens to account takeover attempts when MFA is — and isn't — in place.
Six thousand people opened Calculator at the same time — and none of them were doing math. Here's the behind-the-scenes story of how Huntress turned real attacker TTPs into CTF 2024 challenges.
In every martial arts movie, the last opponent is the quiet one. AiTM attacks work the same way — unassuming until they've already won. Huntress unmasks how adversary-in-the-middle attacks actually work.
Huntress uncovered a mass phishing campaign using HTML smuggling, injected iframes, and session theft to bypass MFA. Read the full technical breakdown of a technique that's genuinely novel.
RMMs and command-and-control are the same thing from a hacker's perspective. The Huntress SOC director breaks down RMM abuse at scale — including the wackiest ScreenConnect attack chain they've ever seen.
Huntress wakes up every morning asking how to turn cybercriminals into examples. Lately, that means tracking emerging Microsoft 365 initial access tradecraft. Here's what the team found and built.
An attacker has valid credentials but MFA is standing in the way. How does the story end? The Huntress CTF retrospective walks through the challenges that made players earn every single flag.

