

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Huntress has observed a series of strikingly similar intrusions beginning with CitrixBleed 2 exploitation, employing novel local privilege escalation techniques, and ending in Dragonforce ransomware.
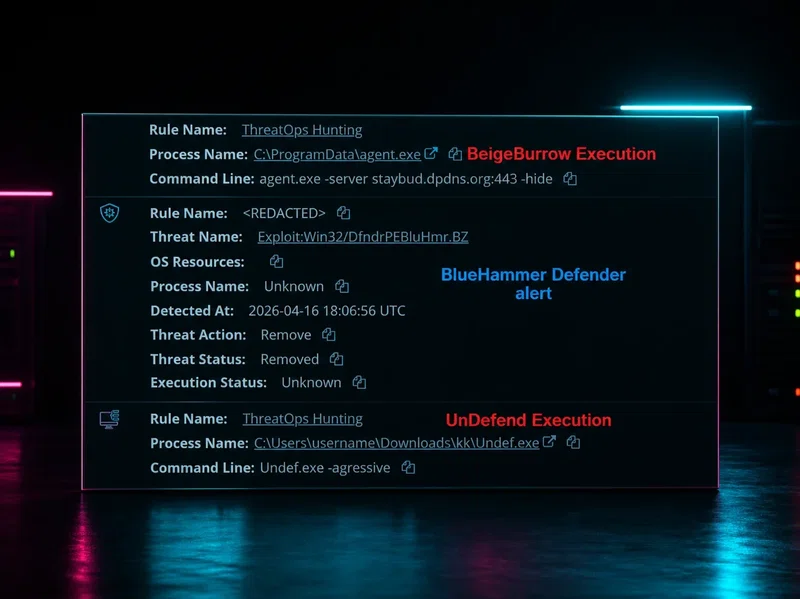
Huntress observed in-the-wild use of Nightmare-Eclipse tooling, including BlueHammer, RedSun, and UnDefend, in a live intrusion involving FortiGate VPN compromise as the initial access, reconnaissance commands, and likely tunneling activity.
Huntress observed active exploitation of SolarWinds Web Help Desk across three customers — with attackers deploying Cloudflare tunnels and Velociraptor for persistence immediately after getting in.
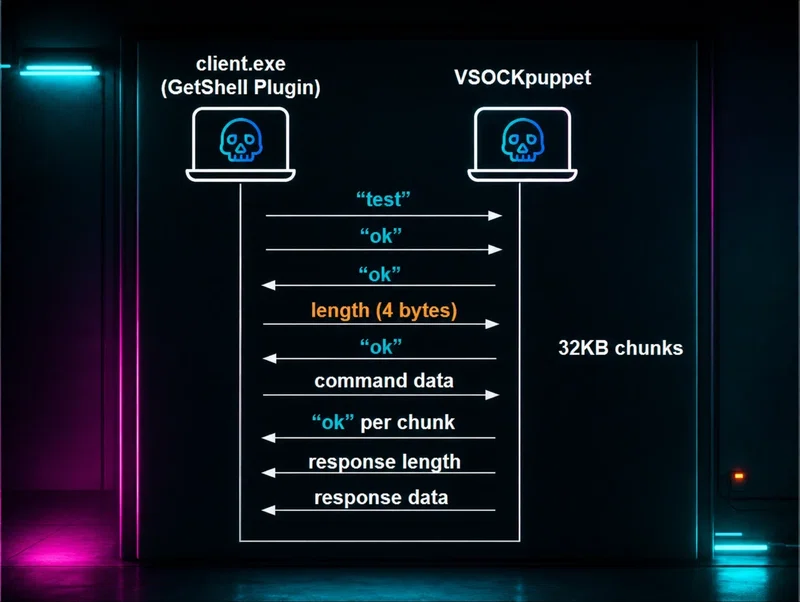
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.
Huntress is seeing threat actors exploit React2Shell (CVE-2025-55182) to deploy a Linux backdoor, a reverse proxy tunnel, and a Go-based post-exploitation implant.

