What if a threat actor accidentally handed you 90 days of their own playbook?
That's exactly what happened. A cybercriminal clicked a Google ad, signed up for a free trial, and installed our endpoint agent on their own attack box — giving us a fly-on-the-wall seat to watch a live offensive operation unfold.
We're talking real browser history, real tooling, real AI-assisted phishing pipelines targeting banks, real estate firms, and crypto exchanges. Automated bots. Proxy evasion. Cookie harvesting. All of it, accidentally self-documented.
This is the rarest kind of threat intel — and we're walking through all of it.
Don't miss it.
August 5 | 4:25pm | Theater B
What a Threat Actor Taught Us About Their Operations and Going Viral Security Marketing
Jamie Levy
Senior Director, Adversary Tactics
Stop by Booth 1845
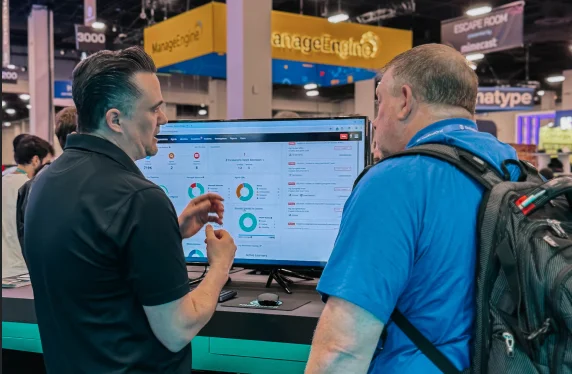
Most security tools don't talk to each other. That’s why Huntress built a managed platform that weaves together your endpoints, identities, logs, and threat data into one view. And it’s all backed by a 24/7 AI-centric SOC actively working in your environment. Stop by the booth to see it in action. While you’re there, ask your hardest questions and grab a few giveaways.
Booth Theater Sessions
Stop by Booth 1845
- 5:00pm-5:15pm - Nasty OAuth Attacks: Session Hijacking, Phishing, SSO Abuse and more
- 5:30pm-5:45pm - Your Malware Infection is Just Three RMMs in a Trenchcoat
- 6:00pm-6:15pm - Agentic Log Ingestion and Automated Malware Triage
- 6:30pm-6:45pm - From the Darknet to Your Network
3:00pm-3:15pm - Five Security Myths Attackers Love
3:30pm-3:45pm - BYOVD - Bring Your Own Vulnerable Driver
4:00pm-4:15pm - Beyond the Inbox: The New Wave of Phishing
4:30pm-4:45pm - From the Darknet to Your Network
5:00pm-5:15pm - Caffeinated Adversaries
5:30pm-5:45pm - Nasty OAuth Attacks: Session Hijacking, Phishing, SSO Abuse and more
11:00am-11:15am - Your Malware Infection is Just Three RMMs in a Trenchcoat
11:30am-11:45am - Caffeinated Adversaries
12:00pm-12:15pm - Beyond the Inbox: The New Wave of Phishing
12:30pm-12:45pm - Agentic Log Ingestion and Automated Malware Triage
1:00pm-1:15pm - Five Security Myths Attackers Love
1:30pm-1:45pm - BYOVD - Bring Your Own Vulnerable Driver
Better defense against hidden threats
Our 24/7 AI-Centric SOC pairs elite threat analysts with AI to help you catch and contain LOTL attacks before they spread. We provide the agile detection and fast response you need to maintain business operations, protect your reputation, and keep your mind at ease.
Book a Meeting
Lock in 20 minutes with a Huntress expert or Cybersecurity Advisor at Black Hat to get face-to-face time, knock out your biggest questions, and walk away with a clear, actionable plan for your security stack.