

Blog Post
Panic at the Distro
Learn how critical Linux kernel flaws in CopyFail, Dirty Frag, and Fragnesia let unprivileged users escalate to root access. See what security teams can do to remediate.
Learn how critical Linux kernel flaws in CopyFail, Dirty Frag, and Fragnesia let unprivileged users escalate to root access. See what security teams can do to remediate.
Linux powers most of the internet and most of the enterprise — which makes it a high-value target most security teams underestimate. Here's what the threat landscape looks like heading into 2026.
Feature parity across Windows, macOS, and Linux sounds simple on a product roadmap. Actually building it means reconciling fundamentally different operating systems. Here's how Huntress is approaching it.
Huntress CEO and founder Kyle Hanslovan will spin up real attack techniques and show you just how fast modern tradecraft goes from idea to execution.
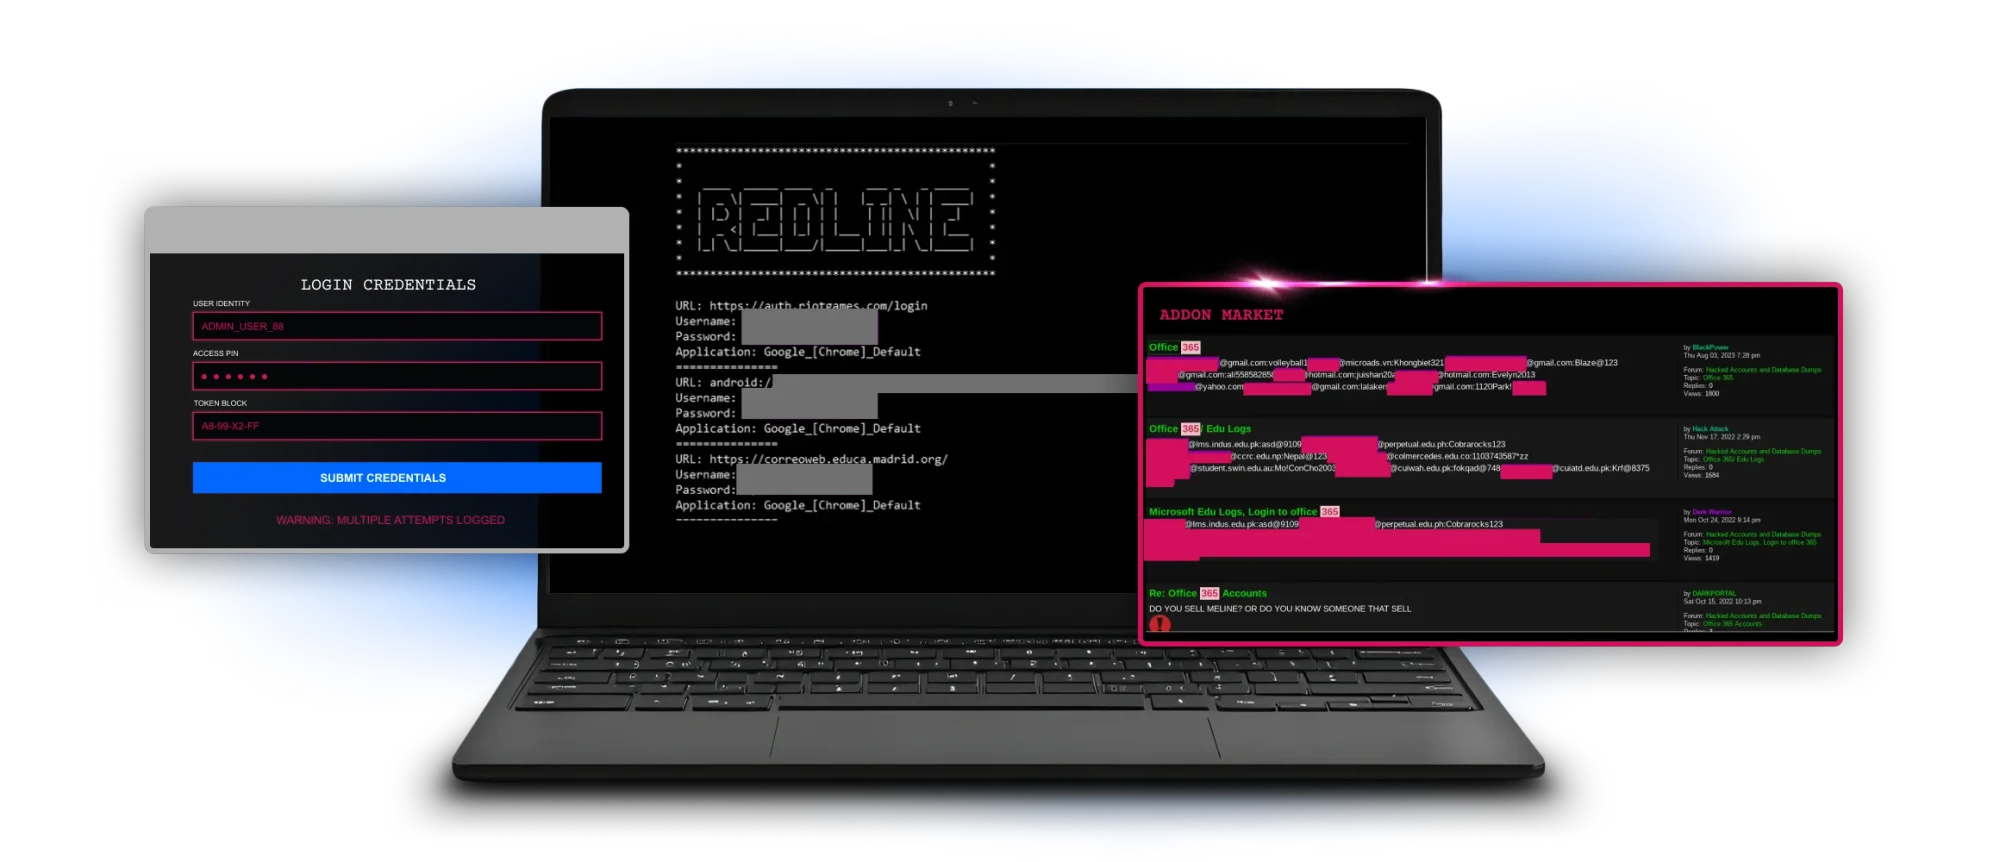
It seems like a new infostealer variant hits the market and starts stealing people’s info every day. Although crypto is one of their biggest targets, it doesn’t stop ‘em from going after everything in sight. Today’s infostealers are doing more than stealing passwords. They’ll take your VPN configurations, browser autofills, even your AI configurations—anything that’s not nailed down. And it doesn’t stop there; this info is passed on and used for ransomware and other criminal activity ( à la initial access brokers). If you’ve seen any security news in the last year, you’ll know infostealers have been talked about non-stop. But here’s why we HAVE to talk about ‘em again. We’re exposing the infostealer underground: stolen info at scale, anatomy of a bot, how infostealer logs are packaged, sold, and marketed, threat actor engagement, and initial access brokerage, as well as “malware-as-a-service”.
