

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Attackers exploit Volume Shadow Copy for credential theft and ransomware defense evasion. See how Huntress spots the difference from routine IT activity.
Before delegating work to AI, ask one question: can you check the output? A detection engineer on why verification, not trust, decides what tasks you hand over.
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.
During a ransomware intrusion, Huntress found a script full of clear English comments walking through each step. Old playbooks don't die. Attackers just keep running them.
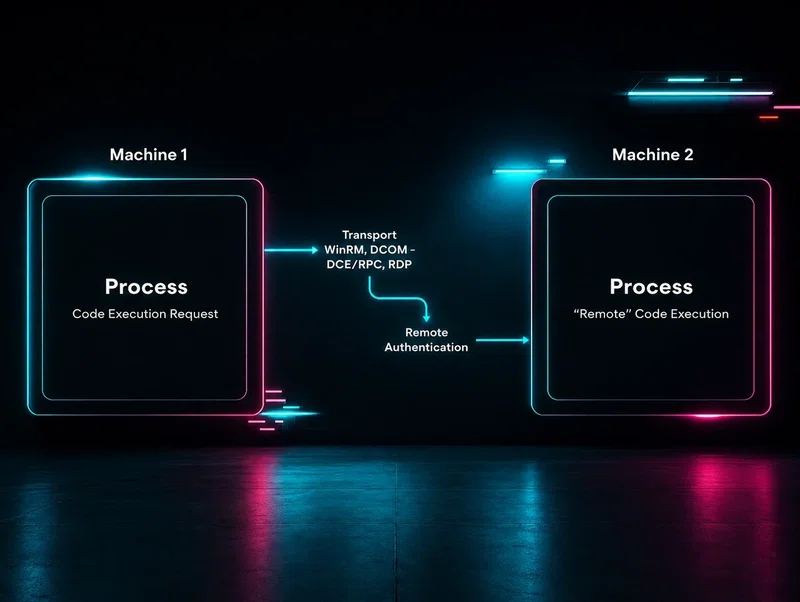
Once attackers are inside, lateral movement is how they deepen a compromise and make removal much harder. Here's exactly how Huntress detects and disrupts it before it spreads.
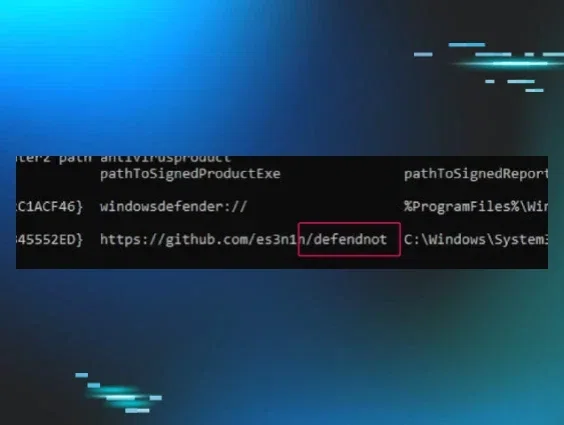
A tool called 'defendnot' disables Windows Defender by registering a fake antivirus through undocumented Windows Security Center APIs. Huntress covers the technique and how to detect it.
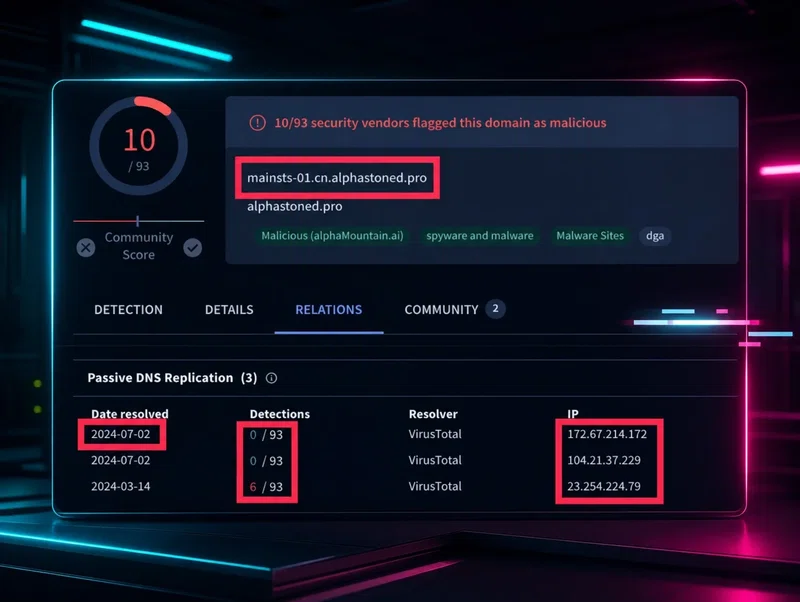
RedCurl is an APT known for cyberespionage that goes undetected for months. In late 2024, Huntress uncovered RedCurl activity across multiple Canadian organizations. Read about the full investigation.
SocGholish's newest campaign started July 4, 2024, and ended in something unexpected: BOINC volunteer computing software being silently installed. Huntress tracks the infection chain from fake update to payload.
Huntress Managed Microsoft Defender, Process Insights, and Open Port Detection working together in real time. Here's a behind-the-scenes look at how the platform caught threats as they happened.

