

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Bad actors are abusing Faronics Deploy in phishing campaigns to run PowerShell, deploy ScreenConnect, and evade detection by using trusted tools.
Attackers aren't just abusing one RMM tool — they're chaining them together for layered persistence that's hard to detect and harder to remove. Every tier of threat actor is doing this now.
Huntress observed threat actors exploiting a Microsoft WSUS remote code execution vulnerability across four customers within days of disclosure. Here's the timeline, the TTPs, and why you need to patch now.
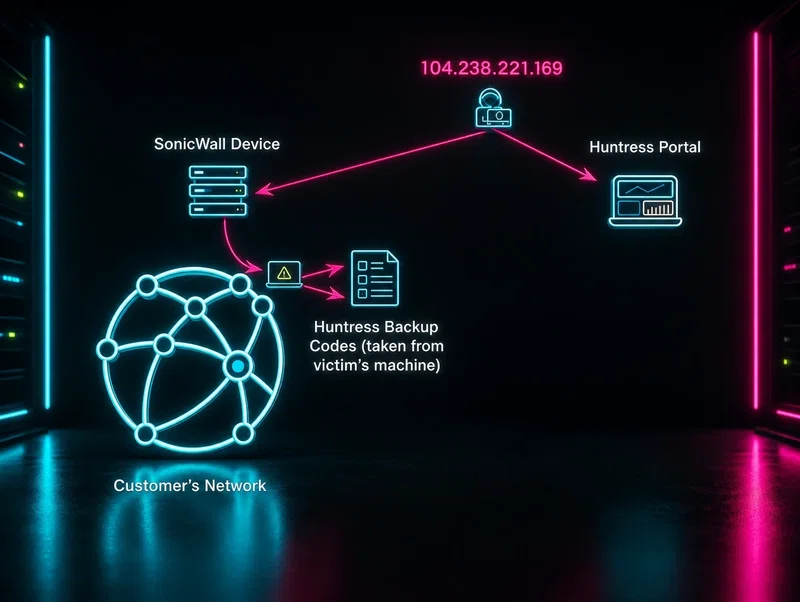
A threat actor got in through SonicWall, then found a plaintext password file sitting on someone's desktop. This companion post to the SonicWall advisory is a cautionary tale in one screenshot.
A large wave of PowerShell malware hit on a Friday afternoon and Huntress analysts dove in immediately. What they found was a Warzone RAT infection chain that tested their detectors in real time.

