

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
A $30 AI toy dog led Mastercard to 250+ scam sites. See how small charges and ransomware payouts follow the same money trail, and how to cut it off.
Doris searched for ChatGPT and ended up in a BEC scam. See how ClickFix, a stolen session cookie, and a hidden inbox rule chain into an OH $#!T moment.
The Huntress Tragic Quadrant ranks the cyber threats hitting businesses most, from RMM abuse to AiTM, ClickFix, using real SOC data.
Learn what good privilege hygiene looks like, from local admin sprawl to accidental access, plus least privilege best practices you can start today.
AI hasn't changed attacker tradecraft, just the speed. See how Huntress built Athena, an agentic SOC partner, to help analysts keep pace.
An incident response plan only works if it's tested. Learn the 5 pillars of operational resilience and how to turn your plan into muscle memory before an attack hits.
Learn what endpoint hardening is, why it matters, and best practices to reduce attack surface, control access, & stop common intrusion paths.
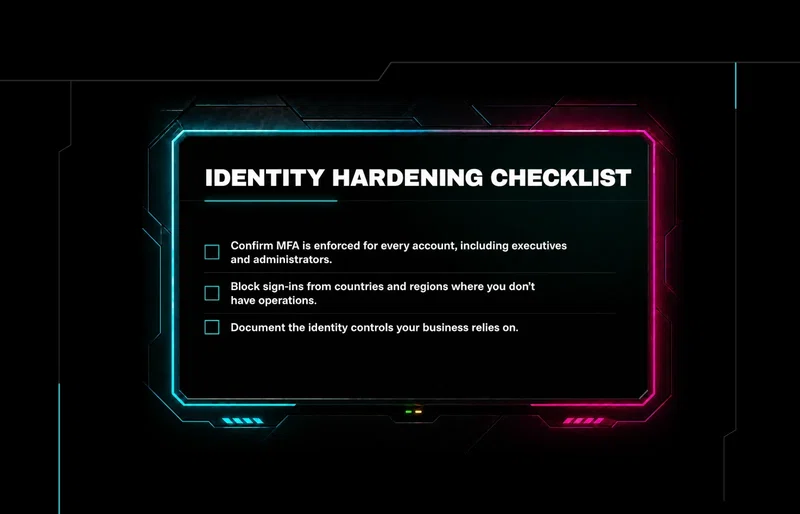
MFA is just the starting line. Learn what mature identity hardening actually looks like, from closing MFA exceptions to catching drift before attackers do.
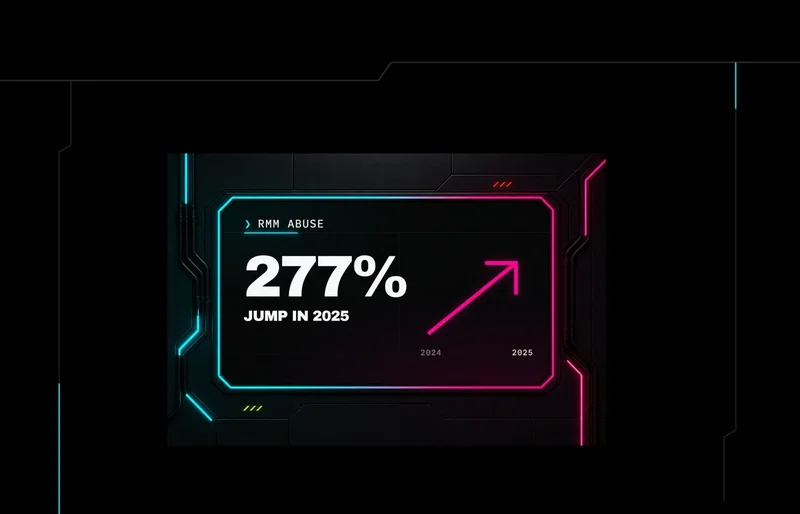
RMM abuse jumped 277% & now shows up nearly 40% of Huntress investigations. See how attackers exploit trusted remote access tools, and how to stop it.
Go inside Huntress and the FBI’s five-year pursuit of Silk Typhoon, from 88,000 Exchange backdoors to an arrest and a wider fight against cybercrime.
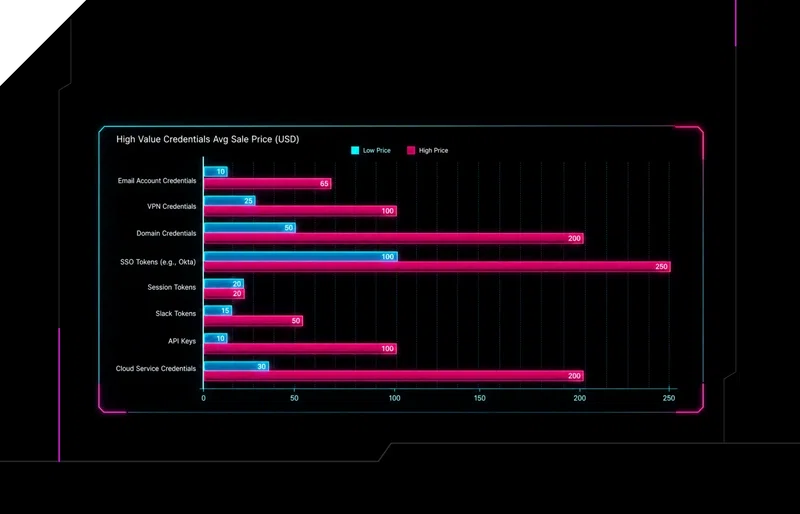
Discover what initial access brokers (IABs) are, how they compromise networks to sell their access to other attackers, and how to protect your business.
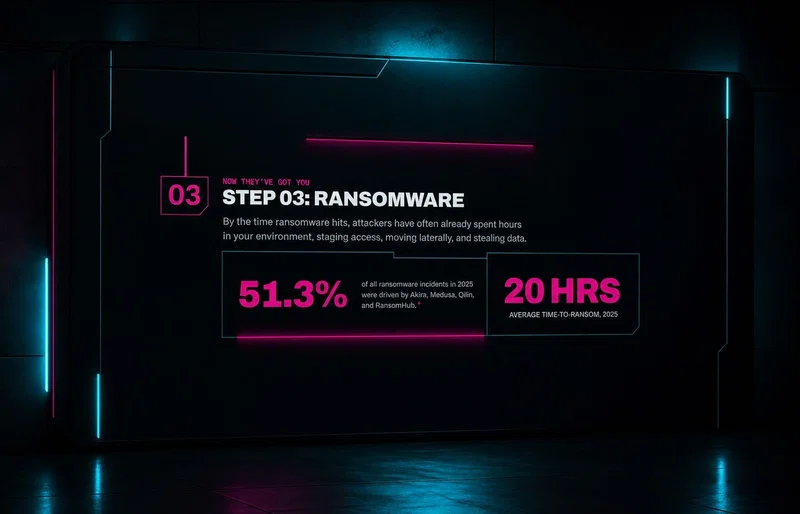
Ransomware is the final act, not the first move. Learn how attackers use access brokers and trusted tools to infiltrate your environment—and how to stop them early.
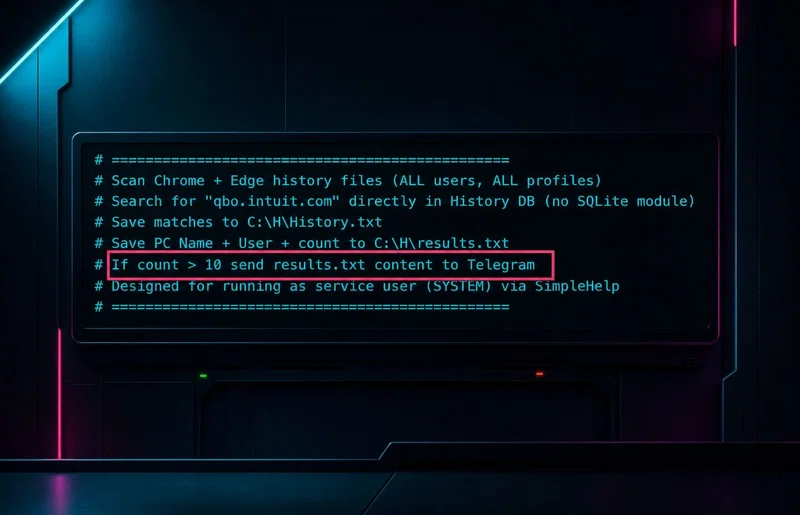
LoTL abuse hides in plain sign, using legit tools like PowerShell and RMM software. Learn how to spot the warning signs that separate from routine IT work.
Ransomware-as-a-Service turned ransomware into a scalable criminal business. Learn how the model works, why it creates so much disruption, and where defenders can shut attacks down before encryption starts.
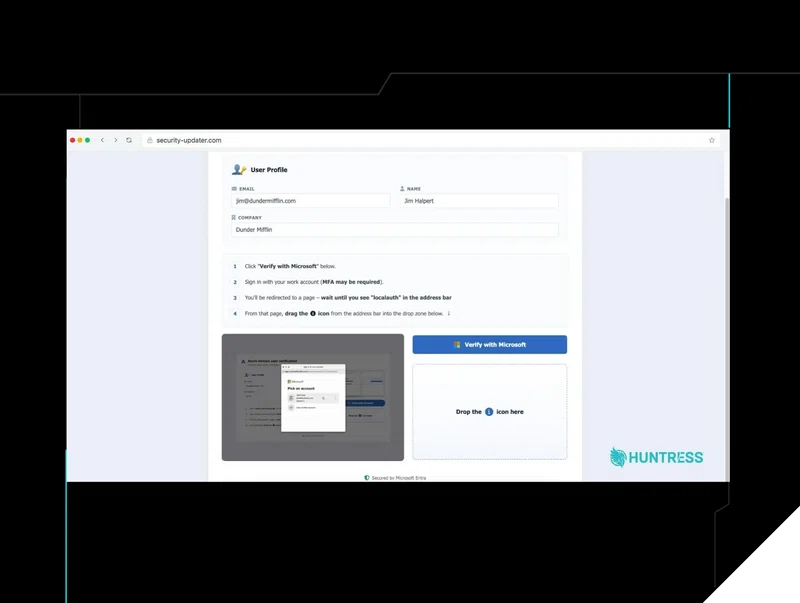
Cybercriminals are hijacking Microsoft 365 accounts in seconds. Learn the 2026 hacker tactics, including ConsentFix, that bypass security training and exploit normal user behavior.

