AI-Centric SOC vs. Fully Autonomous AI SOC: What's the Difference?

Key Takeaways:

  • An AI-centric security operations center (SOC) puts AI at the center of the work: it investigates, correlates, and acts on high-confidence threats, while SOC analysts own the guardrails and the judgment calls.
  • A fully autonomous AI SOC lets AI own the whole loop, including the call to dismiss an alert, with people supervising afterward instead of reviewing the verdict.
  • The dividing line is who makes the final call, especially when that call is "this is benign."
  • Five plain questions will tell you which model a vendor runs, whatever they call it.

Every SOC vendor says "AI" now. Very few say who decides when an alert is nothing.

That question matters more than any feature list. When something odd fires at 2 a.m. on a Saturday, someone or something decides whether it's a threat or noise. A wrong call in one direction costs you an hour, and a wrong call in the other leaves an attacker in your environment.

This guide covers what an AI-centric SOC is, how it differs from an AI-augmented SOC and a fully autonomous AI SOC, and what to ask a provider before you trust them with your business.

What is an AI-centric SOC?

An AI-centric SOC is a security operations center where AI does most of the investigation work, and people own the judgment calls. "AI-centric SOC" is the term we use for our own 24/7 SOC.

Here's how that plays out day to day: AI agents pull telemetry, correlate activity, and flag suspicious behavior. When a threat is confirmed and clears a confidence threshold that people set, the AI acts on it. When a signal is ambiguous or new, it goes to a SOC analyst.

SOC analysts write the playbooks, set the thresholds, and can override the AI at any time. The word that matters is central: the AI carries the weight, and people hold the controls.

What is a fully autonomous AI SOC?

A fully autonomous AI SOC is a security operations model where AI investigates, decides, and responds to threats end to end, with no human review required.

The AI closes the case, including the ones it decides are benign. People still tune the system, audit it, and handle exceptions, but they aren't reviewing each verdict before it becomes final.

Vendors use different labels for this, so ask questions about validation. The test is simple: can the AI close an investigation without a person looking at it?


AI-augmented, AI-centric, and autonomous SOCs compared

Plenty of SOCs have AI in them, and they don't all work the same way. Here's how the three common models stack up, with the AI-centric column showing how we run ours.

AI-augmented SOC

AI-centric SOC

Fully autonomous AI SOC

What AI does

Summarizes and enriches for analysts

Does most of the investigation work and acts on high-confidence cases within guardrails

Investigates, decides, and responds end to end

Who runs the investigation

SOC analysts

AI and SOC analysts, depending on confidence

AI

Who closes a case as benign

SOC analysts

SOC analysts review before closure

AI

Ambiguous signals

An analyst handles them

Routed to a SOC analyst

Varies by vendor, so ask

Who sets the rules

People

SOC analysts own playbooks and thresholds

People configure, then supervise

Where people spend their time

Most of the investigation

Judgment calls, edge cases, new tradecraft

Oversight, audits, exceptions

These three sit on a spectrum, and the spectrum is defined by where a person sits in the decision.


The dividing line is who owns the verdict

It's tempting to compare these models by speed or by how much AI is under the hood. The better comparison is who owns the verdict.

A SOC makes two kinds of calls: "this is a confirmed threat, act now" and "this is nothing, close it." The second one carries more risk. A false positive costs you time. A false negative, a malicious case wrongly closed, leaves an attacker in your environment.

So the closure decision is the one to watch. In an AI-centric SOC, AI moves fast on confirmed threats, and a SOC analyst reviews the benign closure. In a fully autonomous SOC, the AI makes that call too.


A worked example: Athena's guardrails

Here's what an AI-centric model looks like when it's written down as rules.

Athena is Huntress' agentic investigation system, made up of over 40 specialized AI agents. It works inside our 24/7 SOC alongside SOC analysts, and the guardrails around it are specific.

What Athena can do

  • Investigate, act, and report on confirmed threats automatically when human-defined confidence thresholds are met
  • Pull telemetry, correlate signals, and speed up investigations that SOC analysts lead
  • Draft incident reports once a threat is confirmed

What Athena can't do

  • Close an investigation as benign without a SOC analyst reviewing it
  • Make the final call on a case that goes to an analyst for review. When an investigation goes to an analyst, the analyst decides

What happens when Athena isn't sure

  • A signal that's ambiguous or below the confidence threshold routes automatically to a Huntress SOC analyst for review and finalization
  • SOC analysts can review, revise, or override any Athena output

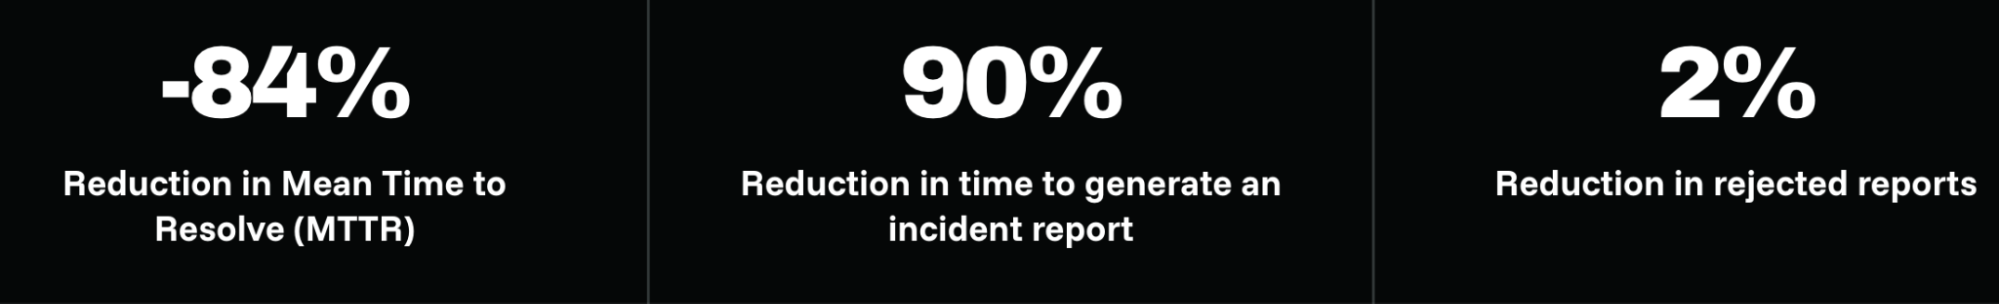
Athena outcomes: -84% Mean Time to Resolve (MTTR), 90% reduction in time to generate an incident report, and 2% reduction in rejected reports

Athena outcomes, by the numbers

Athena moves at full speed on confirmed, high-confidence threats. On the decision with the most downside—closing something as harmless—a person signs off.

SOC analysts own the playbooks and the thresholds. They adjust them as threats evolve, and they review the cases where Athena isn't confident. That's the practical difference between AI-centric and autonomous: who has the last word.


How speed and human review fit together

A common worry is that keeping people in the loop slows everything down. In an AI-centric SOC, it mostly doesn't, because AI acts on its own where confidence is high. Our guide on automated threat remediation shows how Managed Response contains confirmed threats in seconds.

People earn their place on the cases that don't fit a playbook. New tradecraft, odd edge cases, and signals that could go either way need a SOC analyst's judgment and context. Our guide on incident response automation and why human SOC review still matters goes deeper on that.

Attackers move at machine speed, so AI belongs at the center of the SOC. The question is which decisions you hand it.


Vendor checklist: five questions to ask any SOC provider

Use these when you're evaluating a managed SOC, ours or anyone else's. They work whether a vendor says "AI-centric," "agentic," or "fully autonomous."

1. Who decides when an alert is dismissed? Get a straight answer. If it's "the AI," ask what safeguards sit behind that decision.

2. Can the AI close a case as benign on its own? This question separates the models. A yes means the AI owns closure, and a no means a person reviews it first.

3. Who sets and adjusts the confidence thresholds? Thresholds decide what the AI acts on and what it hands off. Find out whether experienced SOC analysts own them and how often they change.

4. What happens to ambiguous or novel signals? Does the AI make its best guess, or does it route the signal to a person? Ask what "below threshold" means in practice.

5. Can analysts override the AI, and can you see what it did? Look for human override and a clear report on every automated action. If you can't see what happened and why, you can't trust it.

If you can't get a plain answer to all five, keep looking.


Ready to see an AI-centric SOC in action?

The Huntress Agentic Security Platform is backed by a 24/7 AI-centric SOC where AI handles the legwork and a SOC analyst owns the hard calls. It's built for businesses of all sizes, and you don't need a security team of your own to use it.

Faster threats get handled, and a person stays accountable for the decisions that matter. That's the deal.

See how the Huntress 24/7 AI-centric SOC works

Frequently Asked Questions

An AI-centric SOC uses AI for most of the investigation work and acts automatically on high-confidence threats, while SOC analysts review ambiguous cases and decisions to close an investigation as benign. A fully autonomous AI SOC lets the AI investigate, decide, and close cases end to end, with people supervising instead of reviewing each verdict.

No. In an AI-augmented SOC, AI assists analysts who still run the investigations. In an AI-centric SOC, AI does most of the investigation work and acts on high-confidence cases, while SOC analysts own the guardrails and the judgment calls.

Yes. When a threat is confirmed and the confidence threshold set by people is met, AI-driven actions can run automatically. SOC analysts step in when a signal is ambiguous or falls below the threshold.

Huntress SOC analysts and platform experts own the playbooks and set the confidence thresholds. They adjust them as threats evolve, and they can override Athena at any time.

It can be faster on routine decisions, because nobody reviews them. That's also where the downside sits: the closure decision. An AI-centric SOC keeps its speed on confirmed threats and keeps a SOC analyst on the closure decision.

Ask them. The five questions in the checklist cover who dismisses alerts, whether the AI can close a case alone, who sets thresholds, how ambiguous signals are handled, and whether analysts can override the AI. The answers will tell you more than any label.

Continue Reading

What Are SOC Services?


Protect What Matters

Secure endpoints, email, and employees with the power of our 24/7 SOC. Try Huntress for free and deploy in minutes to start fighting threats.
Try Huntress for Free

You May Also Like

Read more about MSP Compliance: The Complete Guide to Meeting Security and Regulatory Standards in 2027
MSP Compliance: The Complete Guide to Meeting Security and Regulatory Standards in 2027
Resource Guide

Simplify compliance for your MSP with continuous monitoring, centralized logging, and audit-ready evidence. Learn how Huntress helps you meet security and regulatory standards across clients and frameworks.

Read more about What are the Main Reasons Why MSPs Get Hacked?
What are the Main Reasons Why MSPs Get Hacked?
Resource Guide

Get a candid look at why MSPs are prime targets for ransomware and supply-chain attacks, plus tips for defending against them.

Read more about How MSPs Can Support HIPAA Compliance for Healthcare Clients?
How MSPs Can Support HIPAA Compliance for Healthcare Clients?
Resource Guide

Learn how MSPs can support HIPAA compliance by protecting patient data, managing access controls, and ensuring continuous monitoring. Discover strategies to meet healthcare security standards effectively.