

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Four university breaches, one root cause: misconfiguration. See the pattern behind 2026's higher ed cyberattacks and how to fix the gap.
Ransomware, BEC, and social engineering attacks increasingly start with a simple login, not malware. See the five threat patterns IT and security teams need to watch for, and how to catch them early.
Huntress was one of many vendors impacted by a recent incident at Klue. We dug into the incident to figure out what happened.
See how session hijacking reshaped cyber threats. Learn how stolen tokens enable rapid breaches, bypass security, and impact enterprise protection.
Attackers are building workflows around AI—fake tools, spoofed answers, and machine-speed phishing. See how Huntress is tracking this shift and what it means for defenders.
Mohammad believed he was flying to Laos for a legitimate IT job. Instead, he was trapped, coerced into scamming vulnerable people out of their life savings — hear the story directly from him.
A little-known .NET feature lets attackers execute malicious code inside trusted, Microsoft-signed applications without exploiting a single vulnerability - see exactly how it works.
Hackers don't need elite exploits when Microsoft 365 has built-in features they can chain together to bypass your entire security stack. Kyle Hanslovan shows exactly how it's done.
Think Microsoft 365 is secure because you have MFA? Huntress CEO Kyle Hanslovan, a former NSA hacker, will show you exactly how attackers walk right through it anyway.
Every year during Cybersecurity Awareness Month, someone in your office does something that makes IT want to throw a laptop. This is that list — and what to do about it.
Over 100 SonicWall SSLVPN devices compromised across multiple customer environments in days. Attackers weren't brute-forcing — they had valid credentials. Here's the scope and the activity Huntress observed.
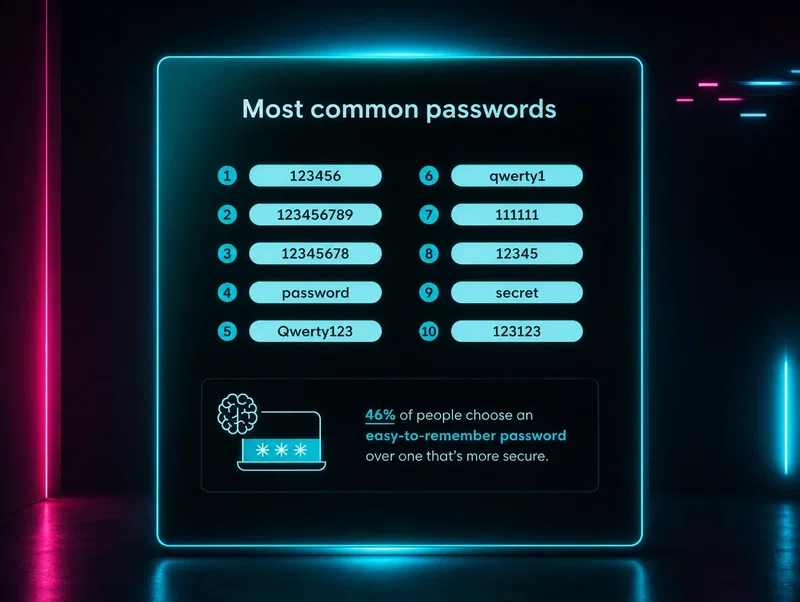
You know the advice: use strong passwords, don't click links, patch your systems. You've tuned it out, and that's understandable. Here's what actually works.
Twenty-one years of Cybersecurity Awareness Month and we're still talking about password hygiene. It's time to get offensive — see what proactive security actually looks like.
Ransomware, zero-days, supply chain attacks — the last decade pushed defenders harder than ever. Huntress looks back at the most influential cyber threats and what they taught the security community.
SonicWall VPN exploitation is active, widespread, and moving fast toward Akira ransomware deployment. Huntress has been tracking this campaign in real time. Here's the full advisory with live updates.

