

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Attackers turned Railway.com's free cloud platform into a Microsoft 365 token-stealing machine, hitting 268+ organizations and 100+ MSPs. Here's the full infrastructure breakdown.
A threat actor exploited SolarWinds Web Help Desk, then ran victim triage from a free Elastic Cloud SIEM trial. The infrastructure they left behind told us everything.
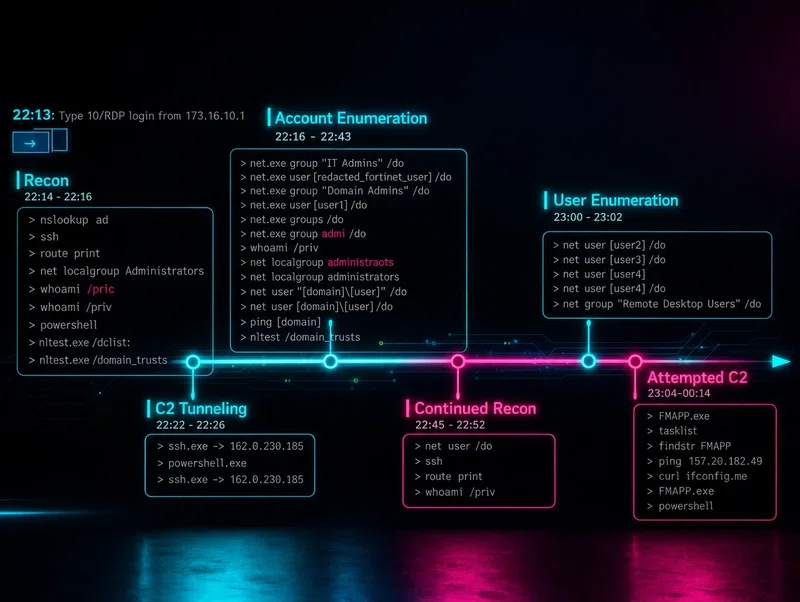
Huntress traced a full Iranian-linked APT intrusion from RDP initial access through DLL side-loading and C2 communications. This is the complete MuddyWater attack chain, step by step.
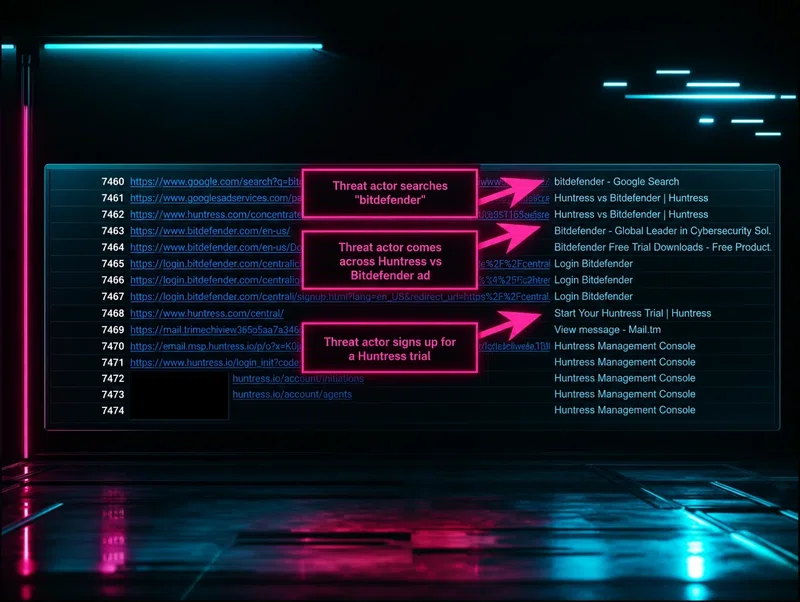
An attacker's mistake gave Huntress an unusually clear window into how a real cybercriminal operation runs day-to-day. Here's the full investigation, including the timeline they didn't want us to see.
Huntress observed active exploitation of Wing FTP Server CVE-2025-47812 — a null byte and Lua injection flaw leading to root-level remote code execution. If you're running it, update now.
A proof-of-concept for the Samsung MagicINFO 9 Server vulnerability went public and exploitation followed quickly. Huntress observed limited in-the-wild activity and documents what attackers did after.

