This isn't a niche, highly technical attack. It's a mainstream technique that adversaries use precisely because it works against the security controls most businesses have already deployed.
Consider what you're up against:
MFA is table stakes—and attackers know it. Most organizations have rolled out MFA. Adversaries responded by shifting their focus from stealing passwords to stealing sessions. They didn't break MFA; they just moved one step downstream.
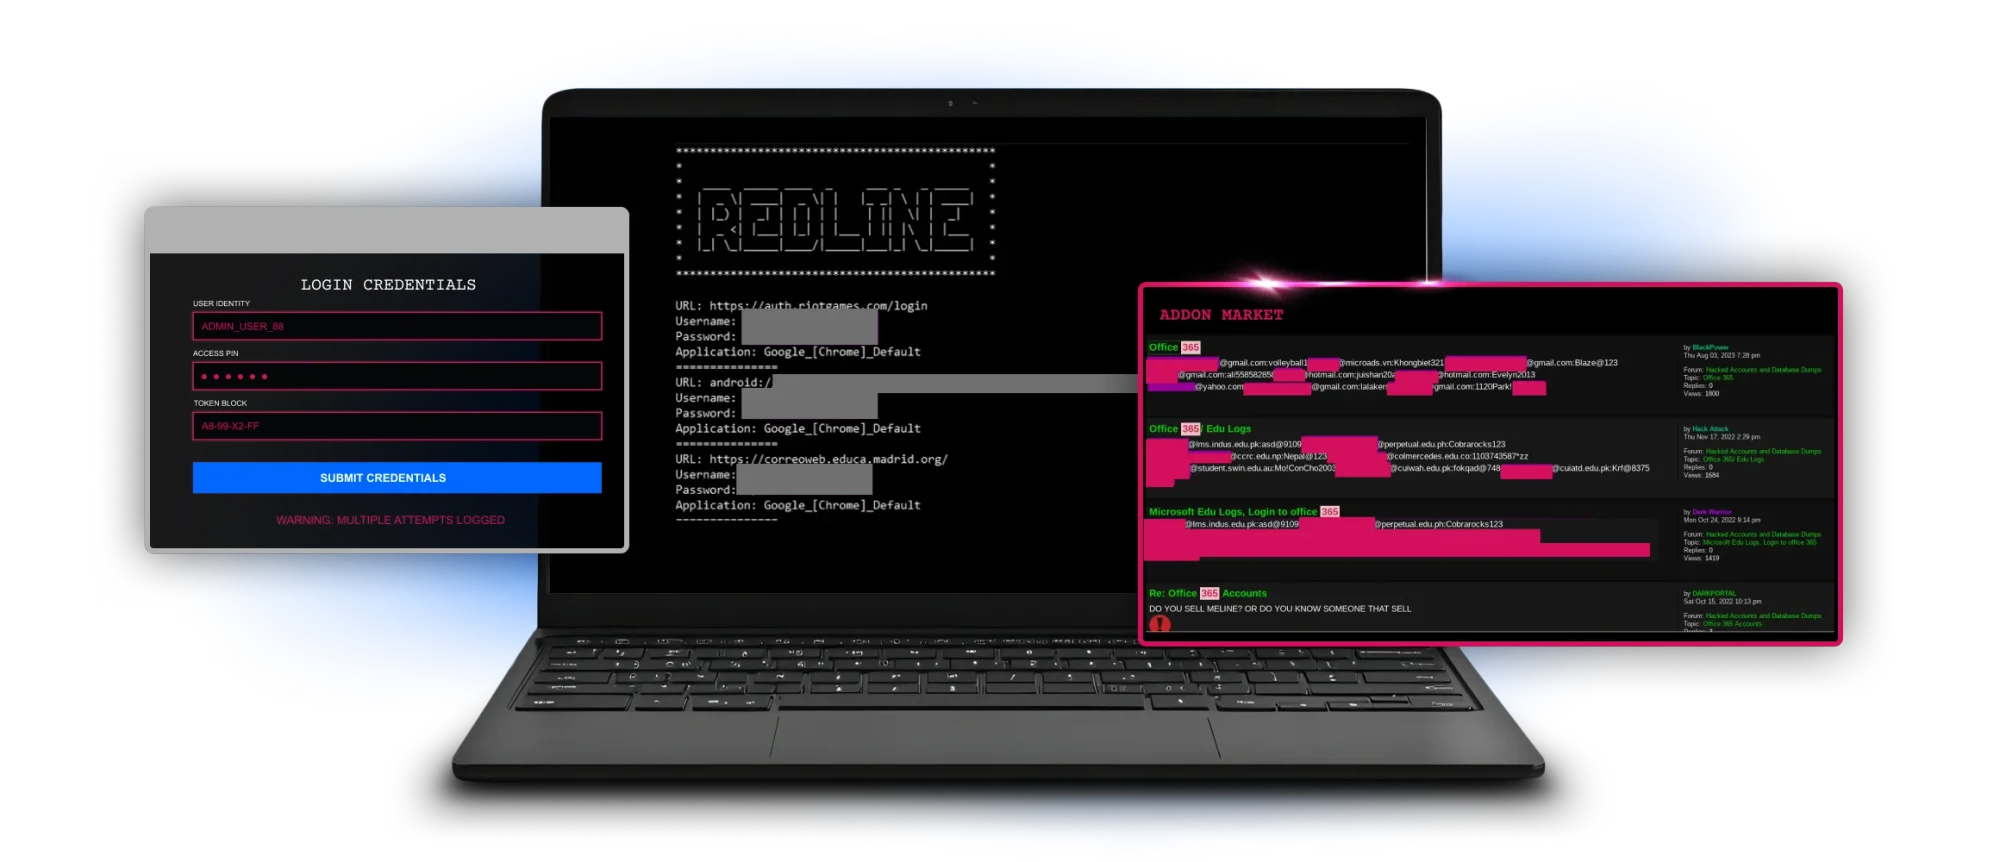
Infostealer malware is cheap and commoditized. You don't need to be a nation-state actor to deploy a cookie-stealing infostealer. Malware-as-a-service offerings make these tools available to anyone willing to pay a monthly subscription. The Huntress 2026 Cyber Threat Report found infostealer activity among the most common malware categories observed across managed environments.
Cloud apps make stolen sessions more valuable. Ten years ago, stealing a session cookie might have gotten you into a single web application. Today, a valid Microsoft 365 session can open email, Teams, SharePoint, OneDrive, Azure AD, and every connected SaaS integration—in one shot.
Many applications issue tokens that can remain valid for days or longer, especially when refresh tokens are in play. If you don't actively monitor for session anomalies, a stolen cookie can provide persistent, undetected access long after the initial theft.
What attackers target
Any SaaS application using cookie-based session authentication is in scope. In practice, the highest-value targets are:
Application
| Why it's targeted
|
Microsoft 365
| Email, Teams, SharePoint, OneDrive, Azure AD—the keys to the kingdom for most organizations
|
Google Workspace
| Gmail + Drive access; often connected to dozens of third-party SaaS tools
|
Salesforce
| Customer data, deal flow, and often a bridge to finance/legal communications
|
HR and payroll systems
| Direct path to fraudulent direct-deposit changes
|
VPN and remote access portals
| Can open the door to internal network access
|
For organizations running Microsoft 365, this is your highest-risk surface. Microsoft Entra ID sign-in logs are your first line of visibility—if you're not monitoring them, you're flying blind.