

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
Microsoft says an AI agent drove the ConnectWise attack. Huntress telemetry is consistent with that: scripted tooling, steered by an operator.
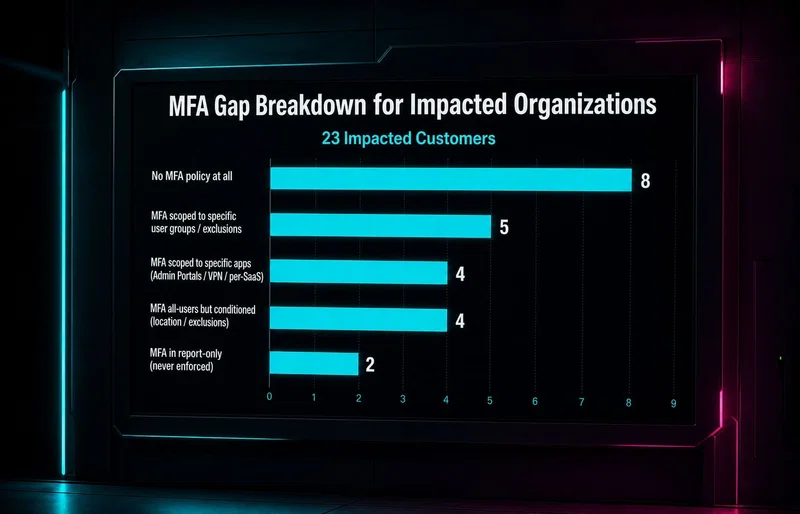
Two Microsoft 365 attacks got through Conditional Access policies that seemed fully configured. Learn what went wrong and how Huntress Managed ISPM catches these gaps first.
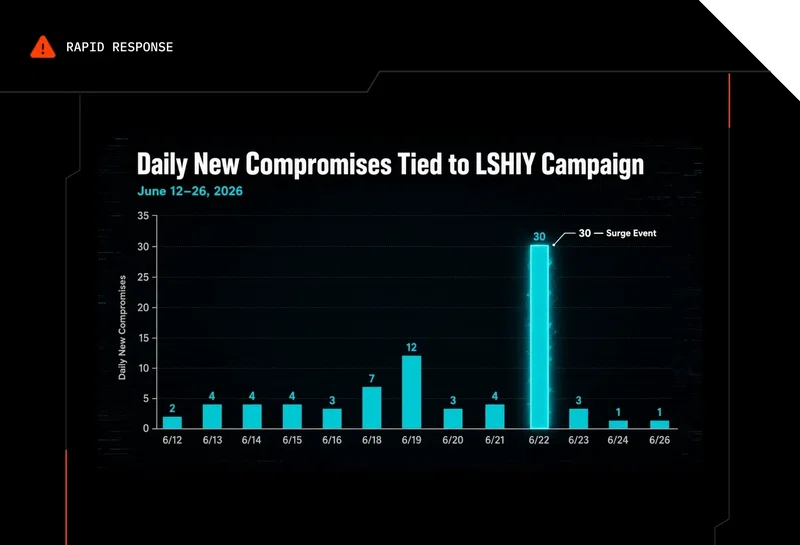
Huntress is seeing an ongoing password spray attack against Microsoft Azure CLI that originates from an IPv6 address range controlled by LSHIY LLC.
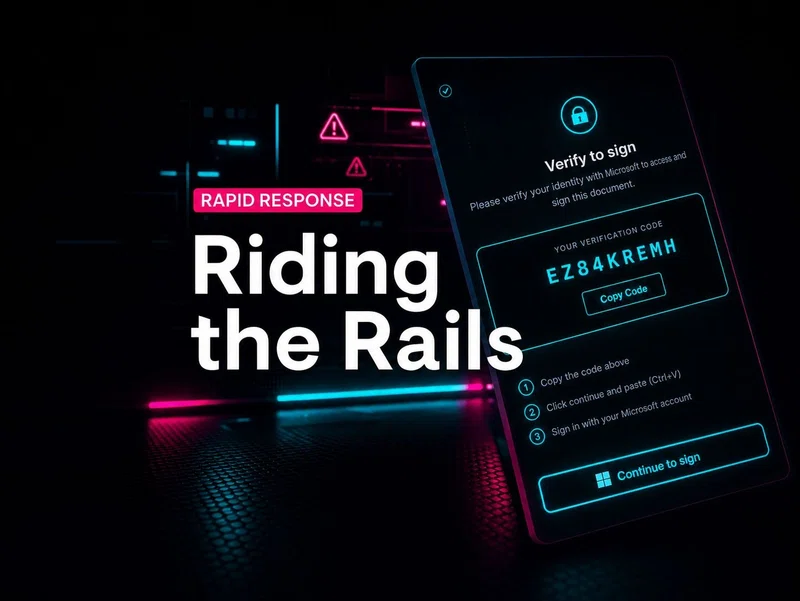
Attackers turned Railway.com's free cloud platform into a Microsoft 365 token-stealing machine, hitting 268+ organizations and 100+ MSPs. Here's the full infrastructure breakdown.

