

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
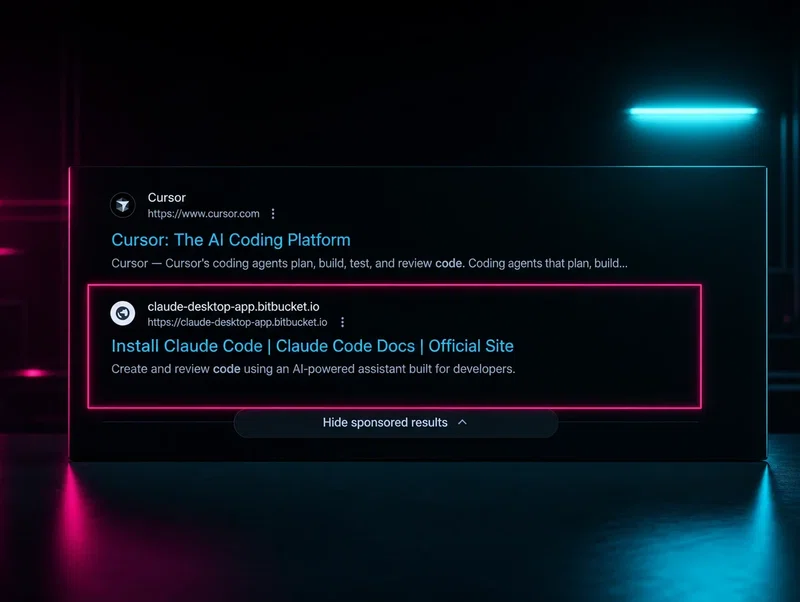
Even a prominent security engineer was successfully targeted by a fake Claude download, proving that a resilient security program relies on fast incident response and a culture of immediate reporting rather than assuming people won't make mistakes.
CMMC isn't just another compliance checkbox — it's a market shift that will sort MSPs into winners and losers. If the EMR mandate taught you anything, it's that early movers win.
The CMMC final rule is live. DoD subcontractors who aren't certified will start losing contracts. Here's what's actually required, when, and what prime contractors will soon be asking their subs to prove.
CMMC compliance is now a real requirement for defense contractors. Huntress explains exactly how the platform supports your CMMC journey, including Sensitive Data Mode and the Shared Responsibility Matrix.
Huntress is now a CVE Numbering Authority. Here's what that actually means, how the CVE program works, what CNA status enables, and why it matters for how Huntress handles vulnerability disclosure.
Annual compliance training isn't improving security posture. Phishing simulations are different — here's the strategy behind making them useful, and how to structure one that actually changes behavior.
Huntress completed its SOC2 Type 1 audit, confirming compliance with security, availability, and confidentiality trust service criteria. Here's what that means for partners and their customers.

