Huntress vs. Zscaler (formerly Red Canary)
Red Canary was acquired by Zscaler and this acquisition creates reasonable questions about future packaging, support, service, ownership and pricing. That uncertainty is one of the many reasons why more businesses are choosing Huntress over Red Canary:
-
Enterprise-grade, purpose-built EDR, ITDR, and SIEM technologies
-
Human-led response with technology ownership that reduces operational burden.
-
Managed Defender Antivirus included for free with EDR. No DIY headaches.
-
No vendor juggling. One partner. One contract. Start to finish, we’ve got it.
-
Transparent pricing. One package, one price. No surprises.
Experience what real managed security should look like–fully integrated, human-led, and hassle-free. Request a demo or start your free trial today.


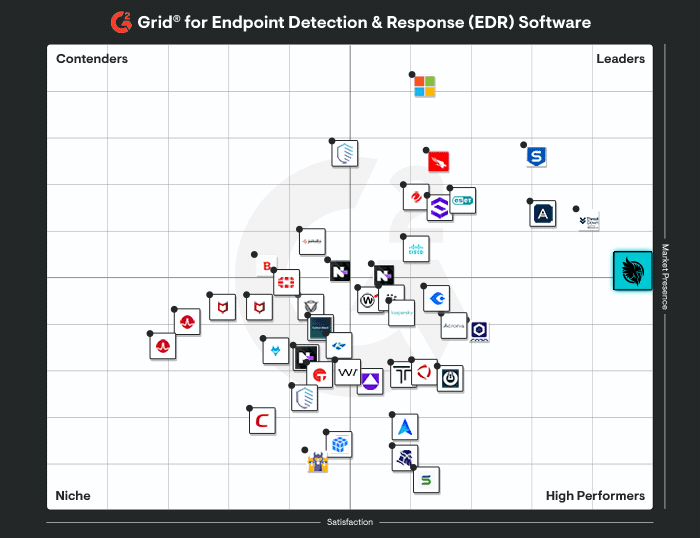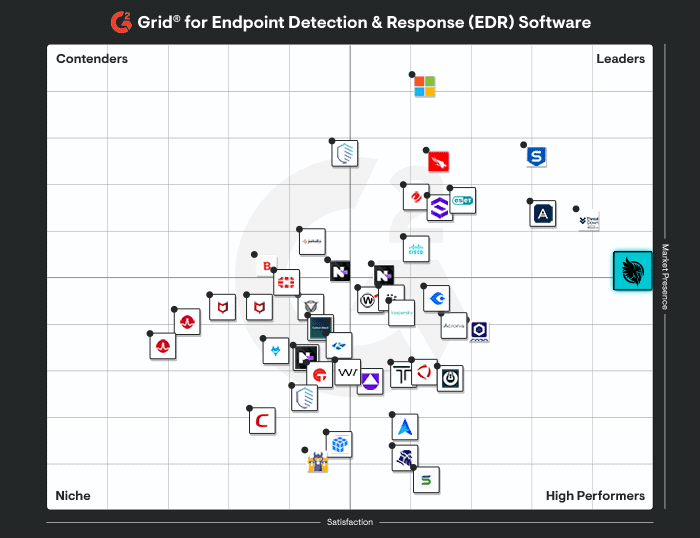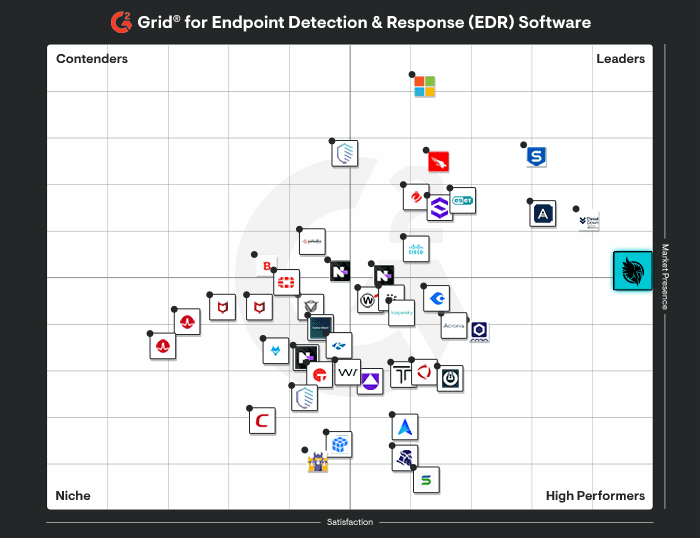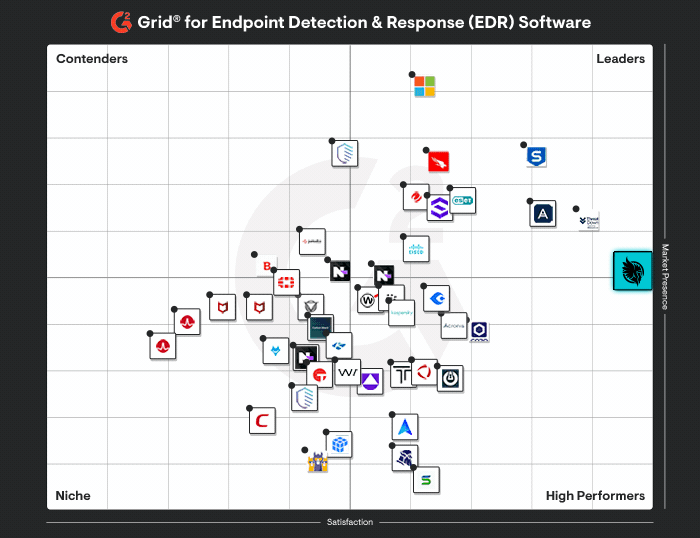
Purpose-Built, Expert-Backed Cybersecurity For All Businesses


Huntress has the back of all businesses. Hyper-focused on every customer with 24/7 SOC Support and our Tactical Response team. Customer satisfaction score of 98.9%.

Built for large enterprises who have the budgets and teams to augment their MDR services. Acquisition by ZScaler raises uncertainty for existing customers.
We own the tech stack, so detection and response are smarter, faster, and built for your needs.
They bolt onto someone else’s tech that could lead to slower detections and unpredictable response outcomes.
We handle everything: onboarding, 24/7 monitoring, AV, hunting, containment, and more. You stay focused on your business. We manage the threats.
You bring the EDR, manage AV, then pay extra for full coverage. Multiple tools, vendors, and gaps.
One price. Everything included. No surprises, no tiers, and no missing features when you need us most.
Buy your own EDR, add services, and tech stack costs. Want full coverage? That’s extra. Those “extras” wreck your budget.
Lower overhead, fully-managed solutions, and real response built-in. Less spend, less stress, better security outcomes
Higher costs, scattered tools, and hidden charges with unpredictable protection. You’ll spend more, do more, and still be at risk.
Enterprise-grade, purpose-built EDR solution that delivers high-accuracy threat detection and a 24/7 SOC.
Customers provide and manage the underlying EDR and related security technologies.
Identity threat detection and response for Microsoft 365 and Google Workspace with human-validated alerts and SOC response.
Delivers ITDR through a blend of identity solution integrations, AI-driven detections, and real-time human threat hunting, all built into their MDR offerings.
Training that is simple to manage with engaging, expert-backed training content built on real-world threat intelligence to reduce human risk, while helping build a security culture.
No awareness training offering. Readiness Exercises is a learning experience platform designed to help teams continuously train for real-world cyber threats.
Built from the ground up to reduce the complexity and cost of log collection, analysis, and storage. Simple pricing per log source backed by our 24/7 SOC.
Security Data Lake product offers SIEM functionality. Ability to enhance MDR planned in Q2.
Why Organizations Choose Huntress Over Red Canary
Challenges with Red Canary
Red Canary built a real reputation as a focused MDR provider. But in August 2025, Zscaler acquired Red Canary and that changes what you're actually buying into.
The service you signed up for may not be the service you renew. Red Canary is running as its own business unit inside Zscaler for now, but Zscaler has been upfront that Red Canary's technology is getting folded into its own Data Fabric for Security and its broader agentic AI SOC roadmap. If you chose Red Canary for a specific team, a specific support model, or a specific level of human expertise, get it in writing before you renew — who owns detection, investigation, containment, remediation, and support once the integration lands.
MDR is about to be one feature in a much bigger platform. Red Canary's whole business was managed detection and response. Zscaler's business is zero trust, cloud security, and AI-driven SecOps at a much larger scale. If you want a partner who lives and breathes MDR — not one capability inside a platform built for something else — that's the tradeoff on the table now.
You're still on the hook for the tech stack underneath. Red Canary's MDR wraps around EDR you already own, license, deploy, and tune. That's a lot of vendor juggling before Red Canary's SOC ever gets involved, and none of it gets simpler under new ownership.
Coverage gets split across tools, and so does accountability. Detection is one piece. Endpoint protection, identity monitoring, log management, containment, and remediation guidance need an owner too. When full response requires a separate product or a higher tier, you get gaps — and a bill that's harder to predict than the quote you started with.
Pricing, contracts, and account coverage are all in play. Any acquisition can shake up packaging and renewal terms, and Zscaler hasn't spelled out what changes for existing Red Canary customers. Before you sign anything new, run your full current cost — Red Canary's fee plus whatever EDR, AV, and SIEM you're paying for on top of it — against a platform that already includes the stack and the SOC in one price.
Testimonials
- “I sleep better when my clients are being protected with Huntress. Huntress helps us by looking for persistent footholds in a network that antivirus just doesn't catch. We're getting a lot of the benefits of a bigger EDR platform for an extremely reasonable price."
- “When Huntress calls, we answer because we know that’s the call that matters. We don’t have the luxury of having team members comb through logs and events all day. We need to be able to focus our attention on other priorities, and Huntress enables us to do that.”
- “Huntress isn’t a ‘set it and forget it’ kind of tool; Huntress is set it and know it works, and when it finds something we’re notified. I don’t need to train my team how to look for that stuff—we have access to talent beyond what we’ve been able to bring onto our team ourselves."


FAQs
Zscaler acquired Red Canary and is integrating the brand and staff into its broader MDR and Agentic SecOps direction. The MDR product is expected to continue, but the exact future packaging, service model, customer fit, and timing of changes may vary. Existing customers should confirm the details of their own renewal and service agreement.
Zscaler’s acquisition creates some near-term uncertainty around how Red Canary’s MDR product will be packaged, supported, and delivered going forward, but there’s no indication the product itself will be discontinued.
Huntress can replace Red Canary for organizations that want a more integrated, managed-first security model. Huntress owns the core EDR technology, operates a 24/7 SOC, and provides managed EDR, ITDR, SIEM, SAT, and related security services through one platform. The right choice depends on your current tools, coverage requirements, and preferred operating model.
Yes. Huntress uses AI to assist its SOC analysts, while humans investigate incidents and determine the appropriate response. This human-led, AI-centric model is designed to combine the speed of automation with the judgment of experienced security professionals.
Huntress is built specifically for MSPs and lean IT teams. It combines multi-tenant management, volume-based partner pricing, managed security technologies, and a 24/7 SOC so partners can deliver detection and response without building a full security operations team in-house.
Compare who owns the technology, who investigates alerts, what response actions are included, how identity and SIEM coverage work, and what you’ll pay for the complete service. Also confirm whether the provider’s future roadmap and customer-support model align with your expectations—not just whether the current feature checklist looks similar.