Huntress vs. Petra Security
See why businesses choose Huntress over Petra Security
Real-time identity threat detection, validated by a 24/7 human-led AI-centric SOC
Full platform coverage across identity, endpoint, and email — not just Microsoft 365
Built for the long haul, with a decade of protecting businesses at scale
Experience the difference of enterprise-grade security and expertise. Request a demo today or experience it yourself with our free trial.
Purpose-Built, Expert-Backed Cybersecurity
24/7 identity monitoring, session hijacking detection, malicious OAuth detection, and now AI-orchestrated investigation through Athena for both Microsoft 365 and Google Workspace.
Microsoft 365-only detection with no endpoint agent and no Google Workspace coverage
AI investigates every detection alongside our 24/7 SOC. High-confidence threats can be resolved at machine speed. While ambiguous or new activity is escalated to human experts—so you act on confirmed threats, not noise.
Automated SOC with limited human oversight; a fast alert isn’t the same as a validated one
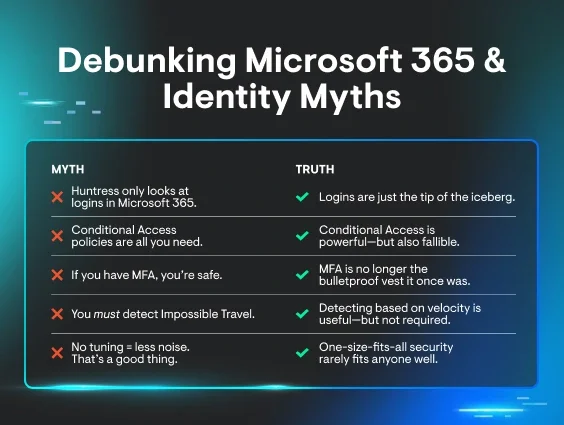
Fine-grained control with access rules, travel exceptions, and alert suppression
No tuning available; one-size-fits-all approach
Purposeful roadmap driven by customer needs and threat landscape
Frequent innovative changes, but little evidence of real-world efficacy
Timeline for ITDR provides an investigation report for each incident, with context, summary, incident timeline, and remediation details.
Strong report polish today, but reporting alone doesn’t tell you whether what’s in it is a real incident or background noise
Huntress ITDR includes Lookback with a six-month Microsoft 365 login history, including detections for credential theft, token theft, and unwanted access.
Petra's Incidents report includes a threat overview, attack timeline with a six-month lookback report, activity-log viewer, and remediation actions.
Athena, our AI orchestration layer, runs 14+ agents trained on Huntress data and SOPs, overseen by security experts, plus fleet-wide adversary infrastructure blocking across 60,000+ tenants
ML-based detection on Microsoft logs only, with no endpoint or cross-platform correlation
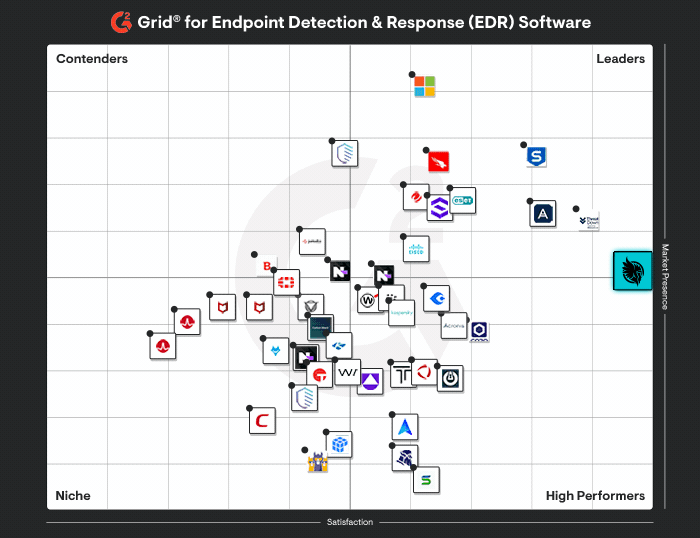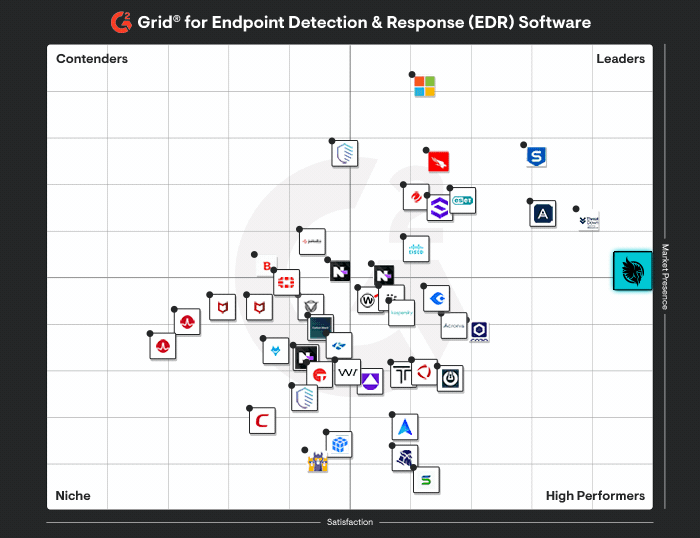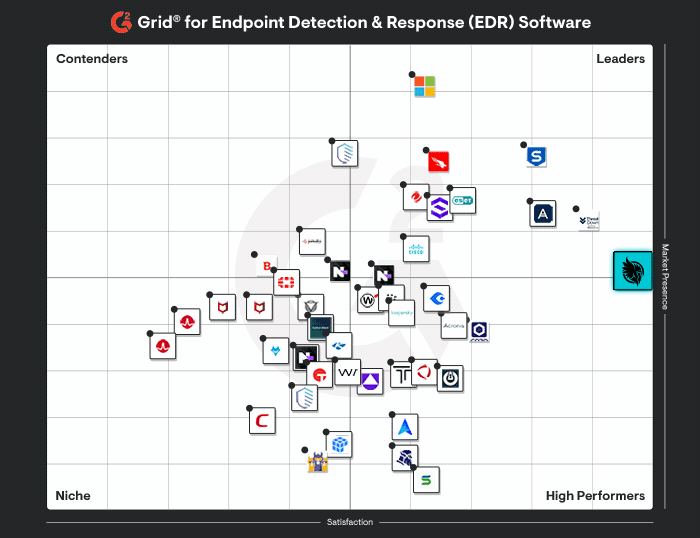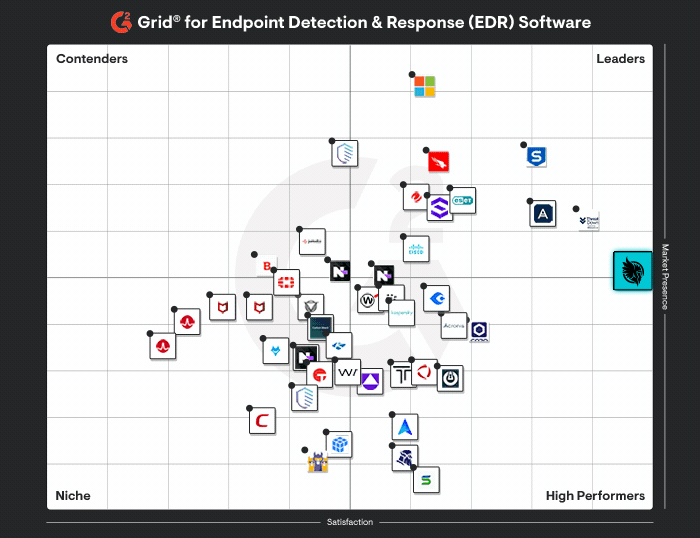
Purpose-built EDR that delivers high-accuracy threat detection, 24/7 monitoring with fast response
Do not have their own Endpoint Detection and Response (EDR) solution
Built from the ground up to reduce the complexity and cost of log collection, analysis, and storage. ITDR data stored in SIEM at no extra cost for one year
Limited SIEM offering with limited source ingestion.
Training that is simple to manage with engaging, expert-backed training content built on real-world threat intelligence to reduce human risk, while helping build a security culture
No security awareness training offering
SOC spanning the US, UK, and Australia — real security experts who call you back
Limited scope SOC with a small team.
Managed Microsoft 365 identity hardening — Huntress Managed ISPM finds gaps in posture, builds and maintains policies to address the latest attacker tactics, deploys them on a guided schedule, and continuously enforces policies to remediate drift within minutes so attackers don’t get a foothold.
Emerging posture management offering.