
Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
Welcome to the Huntress Cybersecurity Blog, where we cut through the noise with real-world tradecraft to help you stay ahead of today’s threat actors. Our authors bring diverse backgrounds and hands-on experience to make cybersecurity education engaging, accessible, and grounded in the threats you actually face.
Threat Research is where the Huntress SOC shows its work. We cover real intrusion investigations, malware and ransomware analysis, threat actor profiles, and the tradecraft attackers lean on: persistence, defense evasion, and living-off-the-land techniques. Whether it broke this week or has been around for years, this is where you see how attacks unfold and how we stop them.
No posts found.
When a vulnerability starts getting exploited, the clock starts. Rapid Response & Vulnerabilities covers CVE disclosures, vulnerability advisories, the exploitation activity we see in the wild, patch guidance, and disclosure timelines. Timely, focused, and built around what to do next.
No posts found.
Timeroasting leaves no authentication log, but it is not invisible. I reverse MS-SNTP's two authenticator forms to build detection that packet size cannot fool.
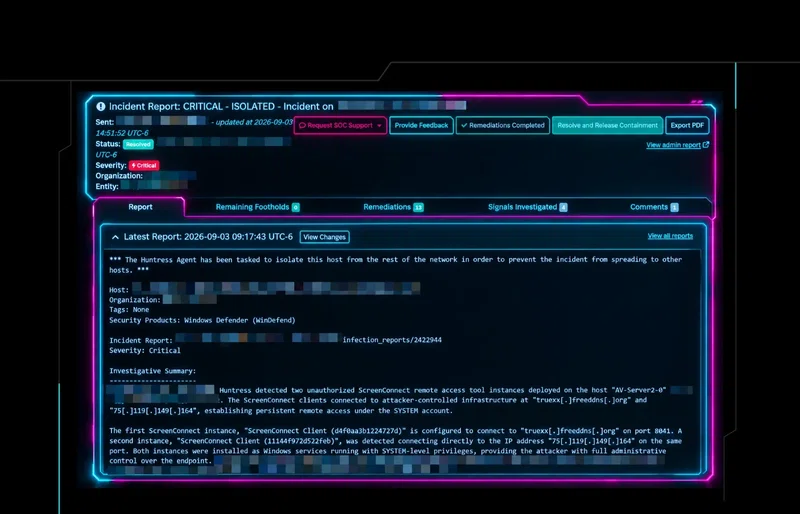
One compromised account, two rogue ScreenConnect deployments, and $3M in downtime. See how TruePath IT and the Huntress SOC handled RMM alerts at 2am.
BEC hides in the vendor and billing threads you already trust. See how a Huntress team caught one, and the inbox rules and signs to watch for.
The Huntress Agentic Security Platform now sees incidents from Defender for Identity, Defender for Office 365, Defender for Cloud Apps, and Entra ID Protection. The new data already helped uncover a token-replay campaign that hit 97 accounts at 79 organizations.
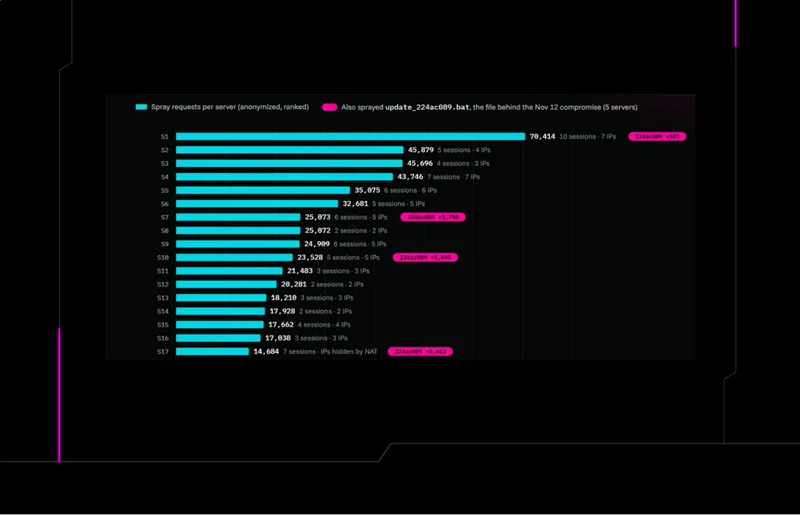
Huntress confirmed CVE-2026-84869 exploitation against MSP technicians via ScreenConnect. See the attack chain, IOCs, and how to protect your team.
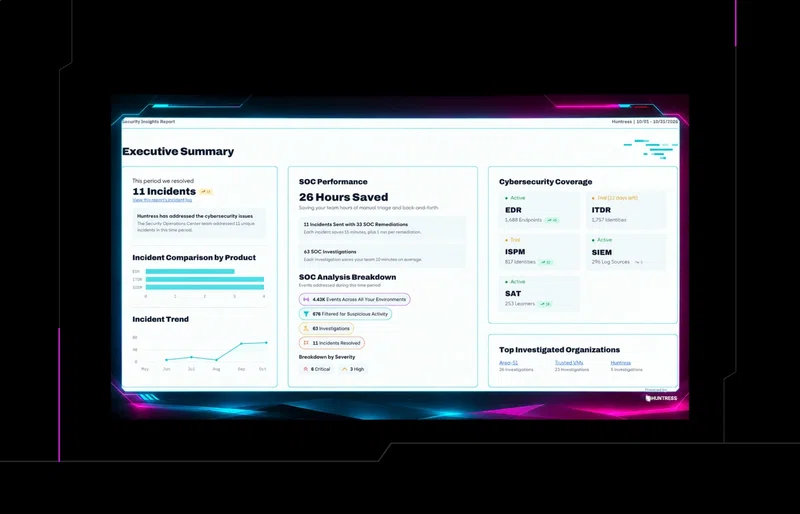
Meet the redesigned Huntress Security Insights Report (formerly known as Threat Report), a one-page summary in an updated reporting center.