




Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
Welcome to the Huntress Cybersecurity Blog, where we cut through the noise with real-world tradecraft to help you stay ahead of today’s threat actors. Our authors bring diverse backgrounds and hands-on experience to make cybersecurity education engaging, accessible, and grounded in the threats you actually face.
Threat Research is where the Huntress SOC shows its work. We cover real intrusion investigations, malware and ransomware analysis, threat actor profiles, and the tradecraft attackers lean on: persistence, defense evasion, and living-off-the-land techniques. Whether it broke this week or has been around for years, this is where you see how attacks unfold and how we stop them.
No posts found.
When a vulnerability starts getting exploited, the clock starts. Rapid Response & Vulnerabilities covers CVE disclosures, vulnerability advisories, the exploitation activity we see in the wild, patch guidance, and disclosure timelines. Timely, focused, and built around what to do next.
No posts found.
ClickFix techniques are evolving. Huntress breaks down four attack chains: lateral movement, hidden PNG payloads, Node.js RATs and cache seeing.

N-able took N-central offline after 33 critical flaws were disclosed, including chains enabling remote code execution and privilege escalation.
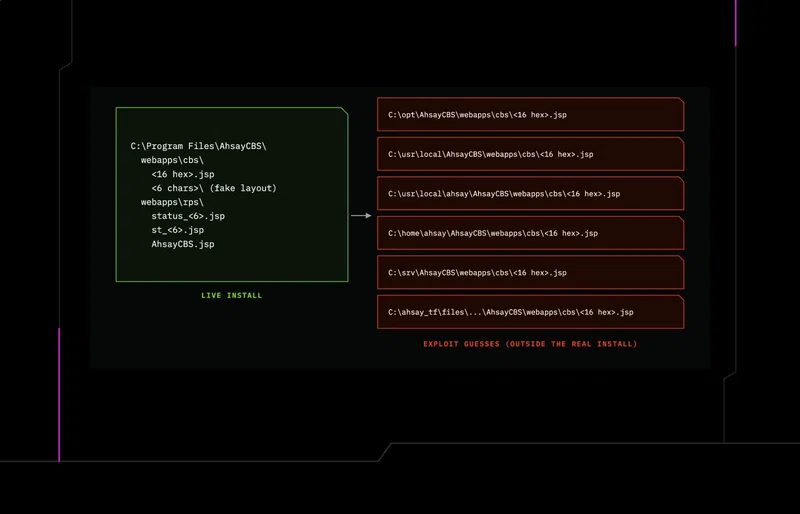
Follow-up on AhsayCBS intrusion: new webshells, a second miner, and a host-bound Python implant found on exploited backup servers.
Meet Sasha Roshan, Senior Sales Engineer at Huntress, a passionate advocate for cybersecurity. See how he makes a difference every day.
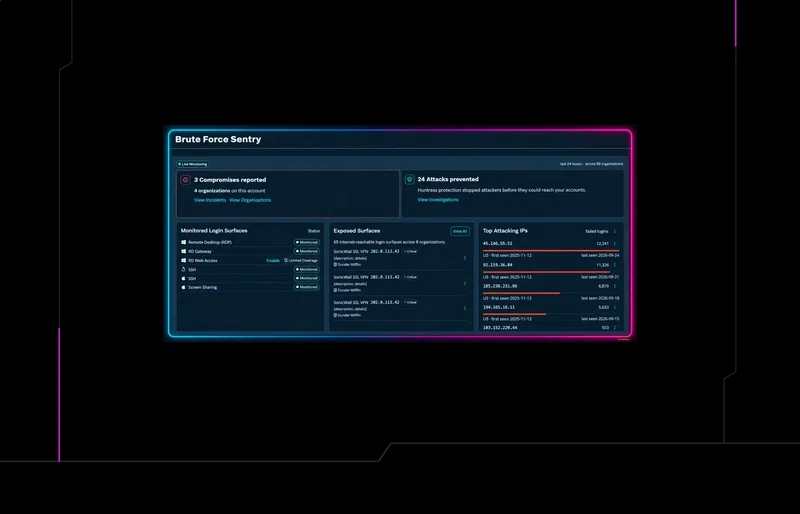
Huntress Managed SIEM's Brute Force Sentry turns the brute force attacks our SOC sees in the field into detections that fire earlier, with the evidence and hardening guidance partners need to close the gap.
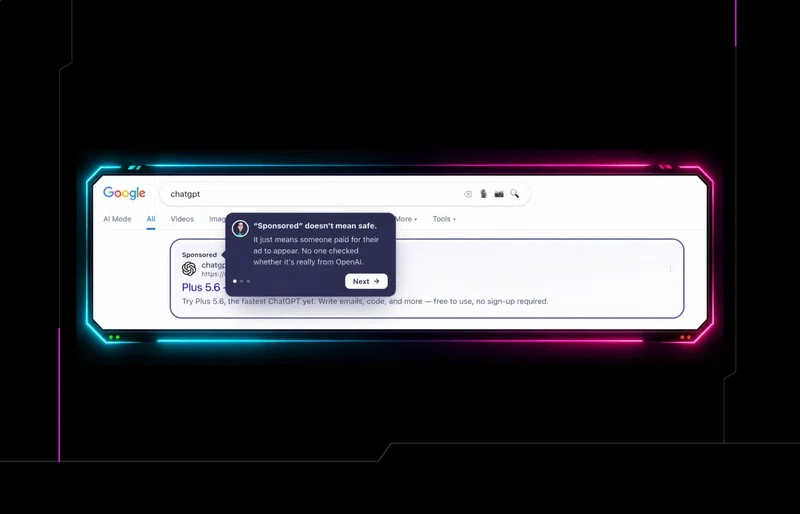
Defense Drill Interventions pair Managed EDR with just-in-time SAT training, so users learn the moment they fall for ClickFix.

