Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
If you administer a Microsoft 365 tenant, audit your OAuth applications right now. Huntress spent six months researching how malicious apps persist inside M365. Statistically, yours may already be infected.
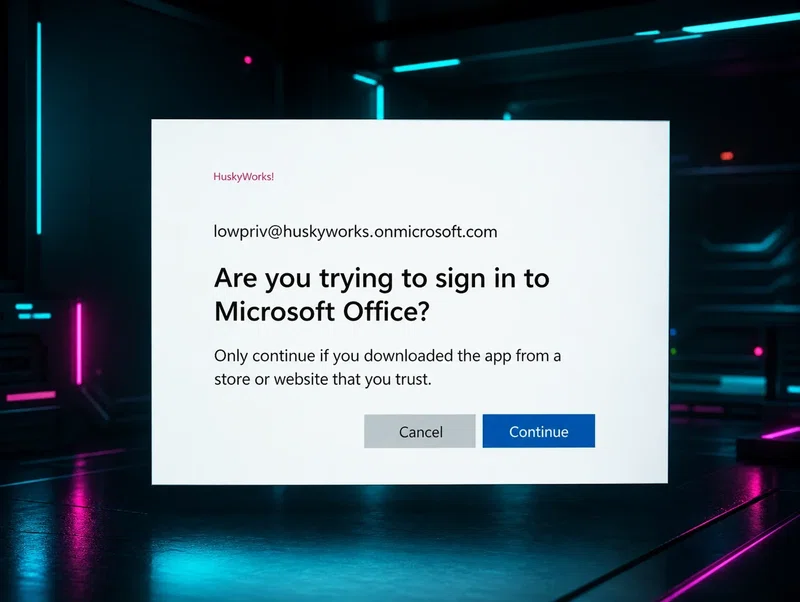
OAuth 2.0 is everywhere, and its different implementations in Google Cloud and Azure have radically different attack surfaces. Huntress walks through a device code phishing case study across both platforms.
In every martial arts movie, the last opponent is the quiet one. AiTM attacks work the same way — unassuming until they've already won. Huntress unmasks how adversary-in-the-middle attacks actually work.
Huntress uncovered a mass phishing campaign using HTML smuggling, injected iframes, and session theft to bypass MFA. Read the full technical breakdown of a technique that's genuinely novel.
Huntress wakes up every morning asking how to turn cybercriminals into examples. Lately, that means tracking emerging Microsoft 365 initial access tradecraft. Here's what the team found and built.