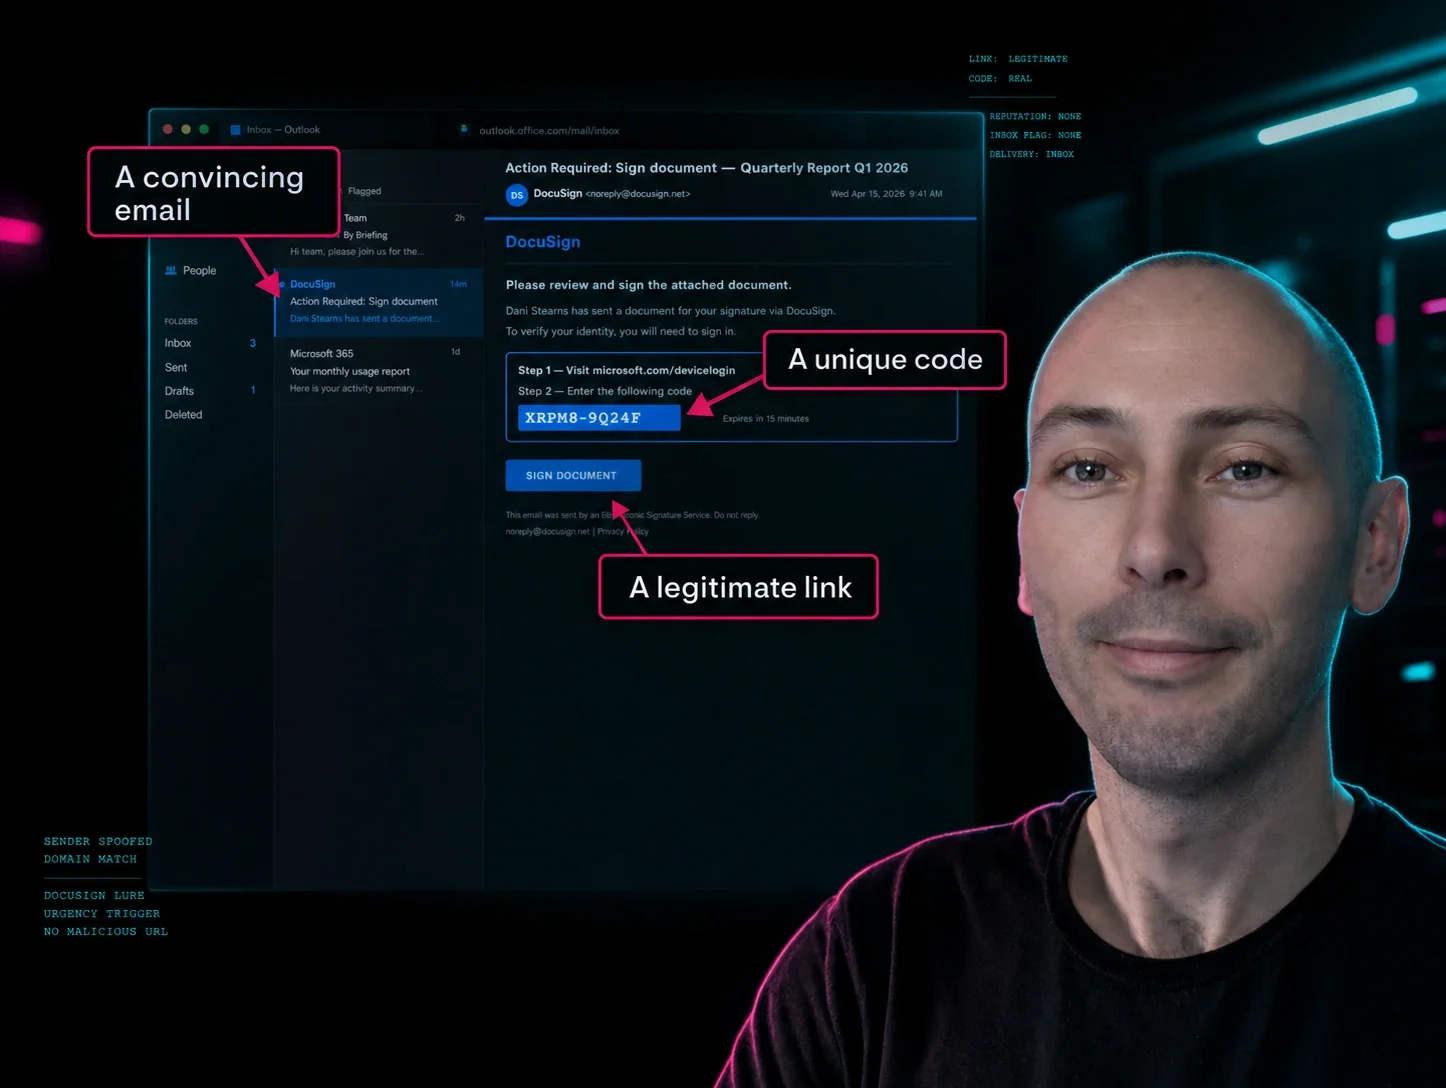
What is Device Code Phishing?
Device code phishing doesn’t hack its way in. It uses a legitimate authentication flow to walk right through the front door, with no password required, MFA bypassed, and session tokens handed straight to the attacker.
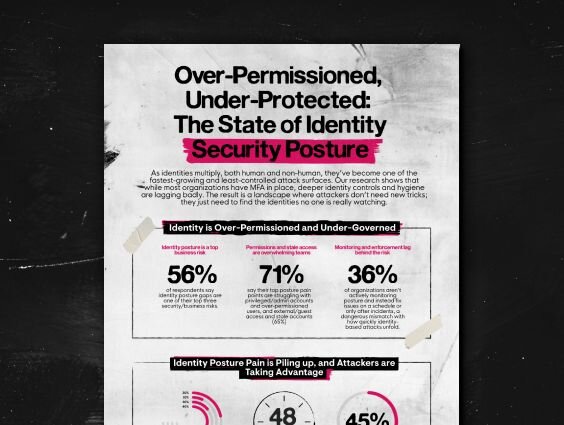
Attackers don't need new techniques. They just need to find the well-known gaps that teams haven't closed yet. Misconfigurations, overpowered users, unpatched vulnerabilities, and unauthorized applications give them exactly that – most organizations are discovering these issues too slowly to do anything about it.
Get the full story in the Known Gaps, Open Doors report. Or use this infographic to quickly understand why posture gaps are now one of the top business risks security teams are managing.
Related Resources
Device code phishing doesn’t hack its way in. It uses a legitimate authentication flow to walk right through the front door, with no password required, MFA bypassed, and session tokens handed straight to the attacker.
This report, based on research from 521 security and IT professionals, examines why endpoint and identity security keeps breaking down, and why the answer isn't to add more self-managed point solutions.
74% of all data breaches involve people—regular, well-meaning users, who accidentally click on a malicious link, inadvertently share a password, or fall victim to social engineering. Thankfully, there’s a way to give your users the tools to protect themselves and make security-minded decisions: Huntress Security Awareness Training (SAT).
Managed ISPM finds the identity gaps attackers look for, and closes them for you.
Identities have become one of the fastest-growing and least-controlled attack surfaces. Human accounts, service accounts, guest access, OAuth applications — they multiply faster than most teams can govern them, and the gaps compound quietly until something goes wrong.
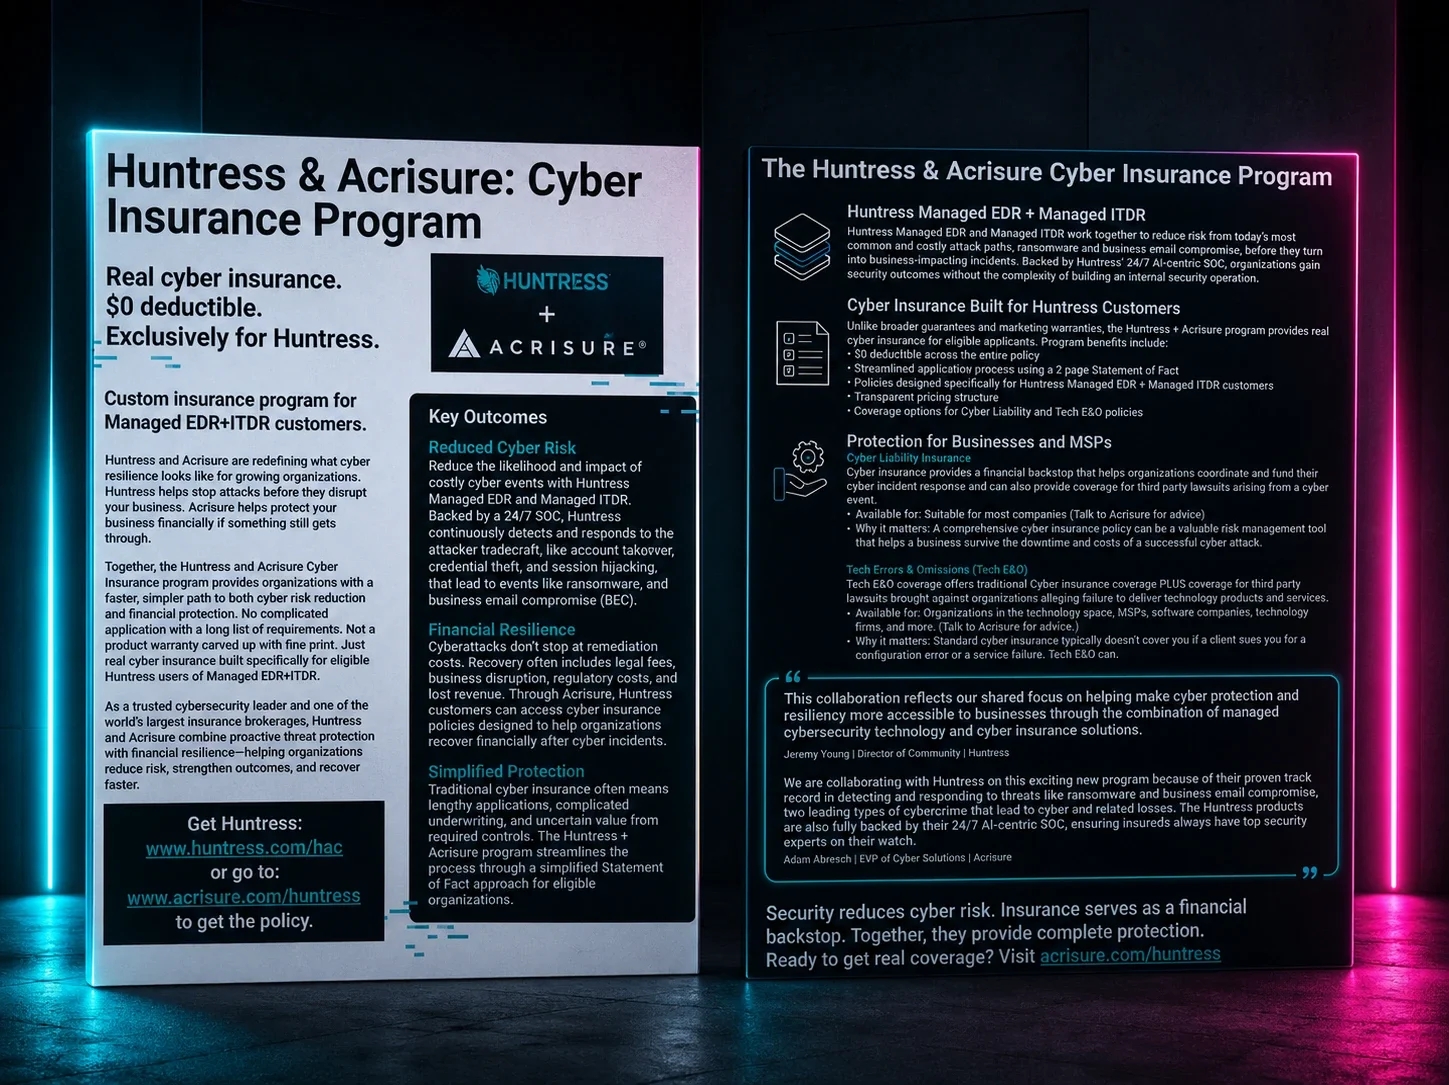
Huntress and Acrisure have teamed up to give growing organizations a simpler path to cyber resilience that combines proactive protection with financial security.
Join us for an exclusive livestream where we’ll review the latest Huntress product updates, plus give you a sneak peek at the exciting changes coming soon to our platform.
Watch our ANZ virtual event on Huntress Managed ITDR for Microsoft 365, featuring real attack examples, attacker tactics, and 24/7 SOC response.
In this exclusive online event, we'll redefine the concept of competitive analysis, pull back the curtain on the day-to-day operations of modern cybercriminal groups, and reveal how they use the same productivity suites, cloud platforms, collaboration tools, and even AI-driven solutions that legit businesses like yours depend on. You'll see real-world attack demos, get expert tips, and see how attackers structure their teams, manage projects, and innovate at speed.
[Summary text goes here]