

Datasheet
Your Business Needs Expert-Level Endpoint Protection
Huntress Managed Endpoint Detection and Response (EDR) finds and stops endpoint attacks for businesses of all sizes.
Actionable steps to stop being the easy target
Attackers aren't picky. They scan the internet for whoever's easiest to infiltrate. Endpoint hardening closes the gaps that put you in their crosshairs.
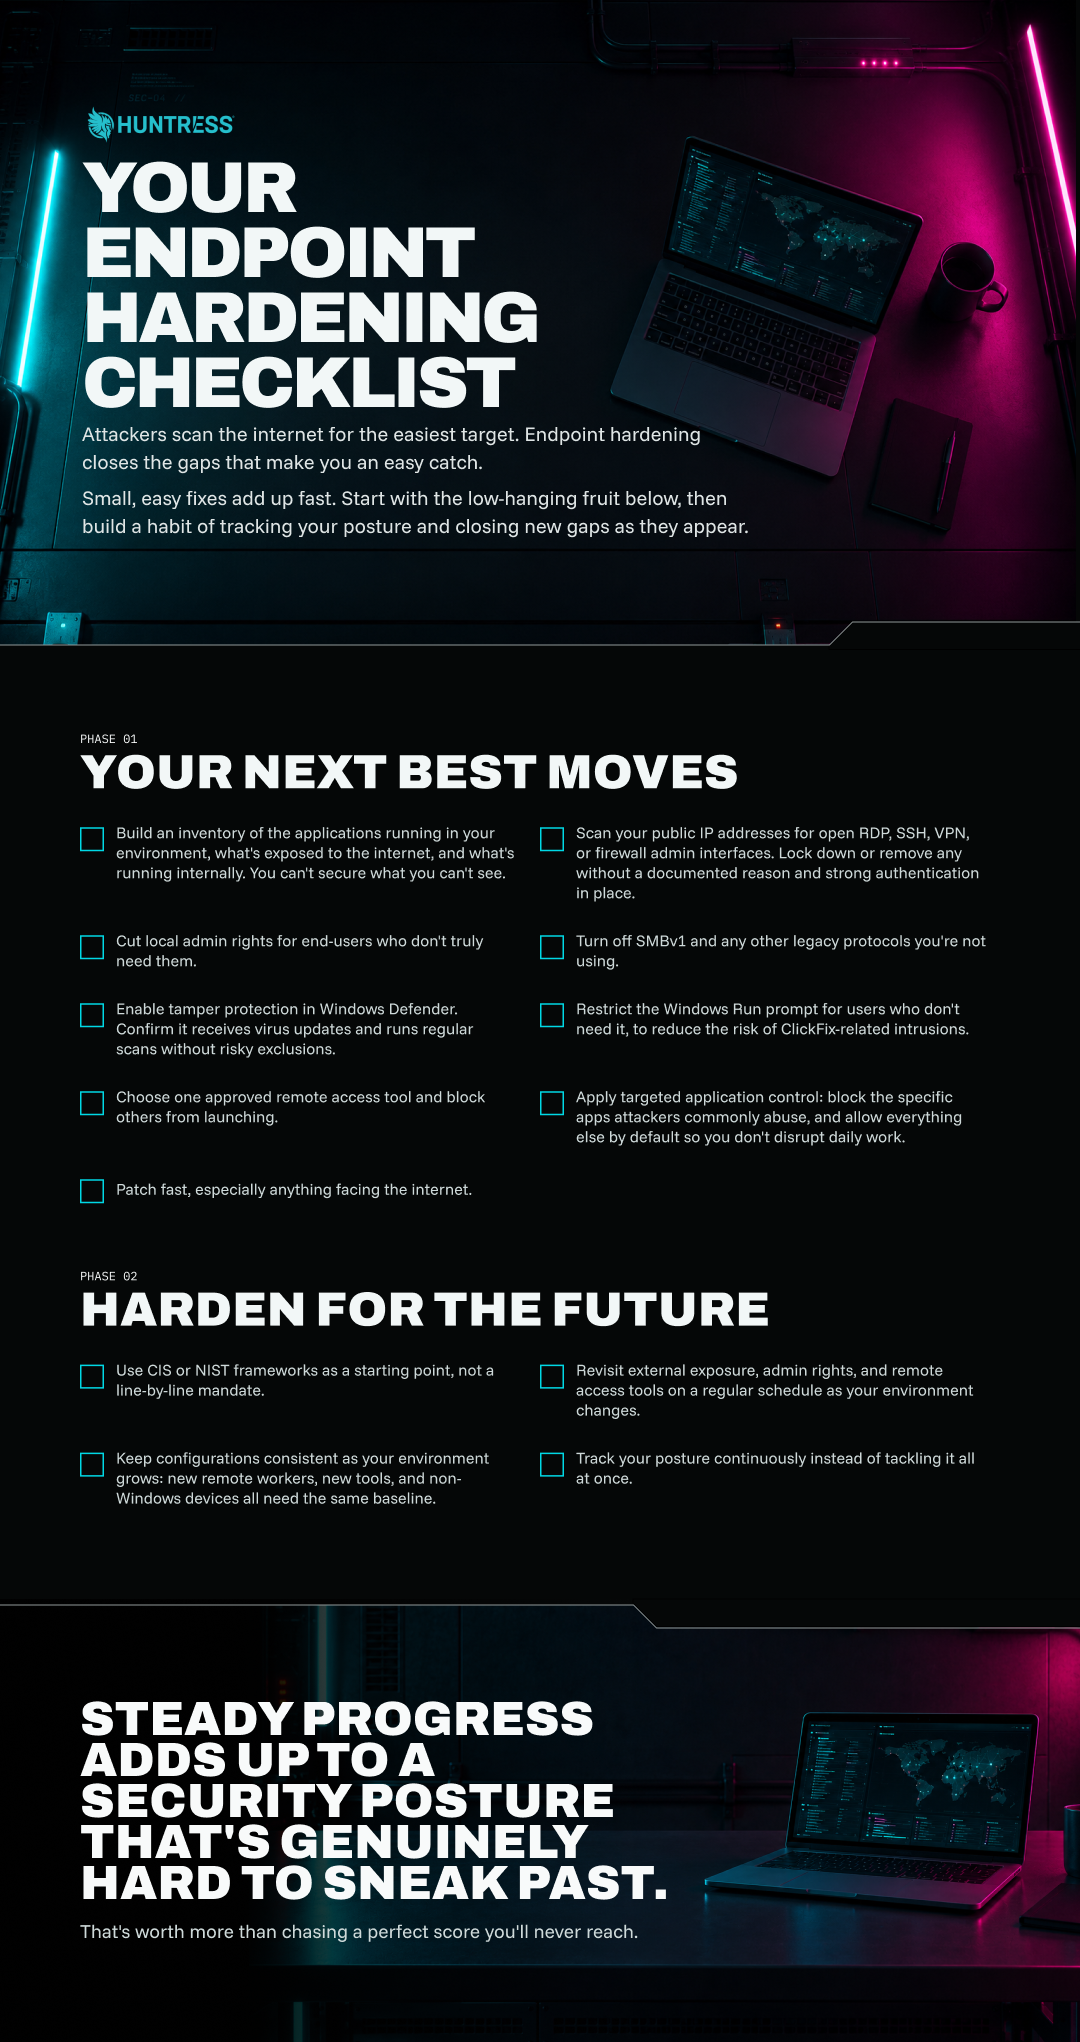
This checklist gives you a clear, practical path forward to get started on endpoint hardening. It starts with the low-hanging fruit you can fix now, then builds toward the ongoing habits that keep new gaps from opening.
Inside, you'll find steps to:
Build visibility into the applications and exposure across your environment
Find and lock down exposed entry points like RDP, SSH, VPN, and admin interfaces
Cut unnecessary local admin rights and other legacy protocols
Apply targeted application control without disrupting daily work
Get your ready-to-use checklist and give your team a clear framework for hardening your endpoint and closing the gaps attackers are counting on, one fix at a time.


Related Resources
Huntress Managed Endpoint Detection and Response (EDR) finds and stops endpoint attacks for businesses of all sizes.
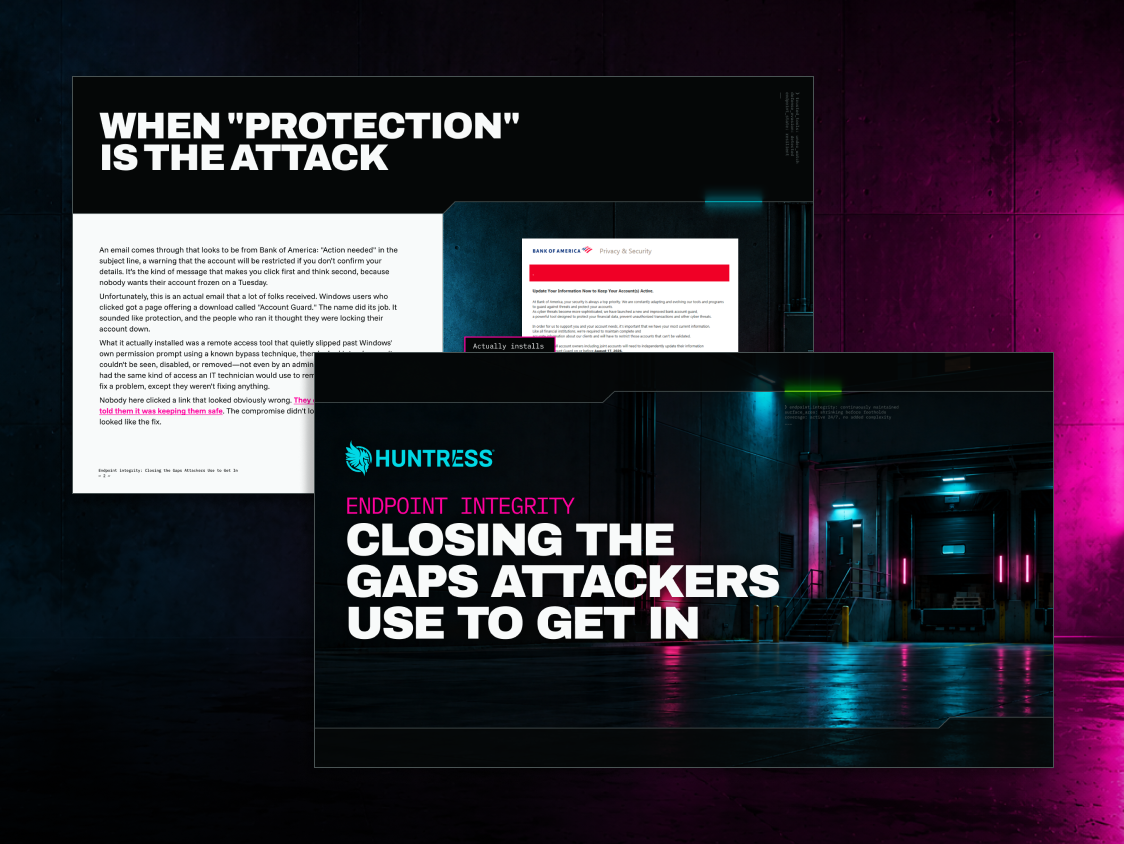
Endpoints are at risk from modern threats. Read the Huntress eBook to learn tactics attackers use to bypass defenses and how endpoint integrity closes the gaps.
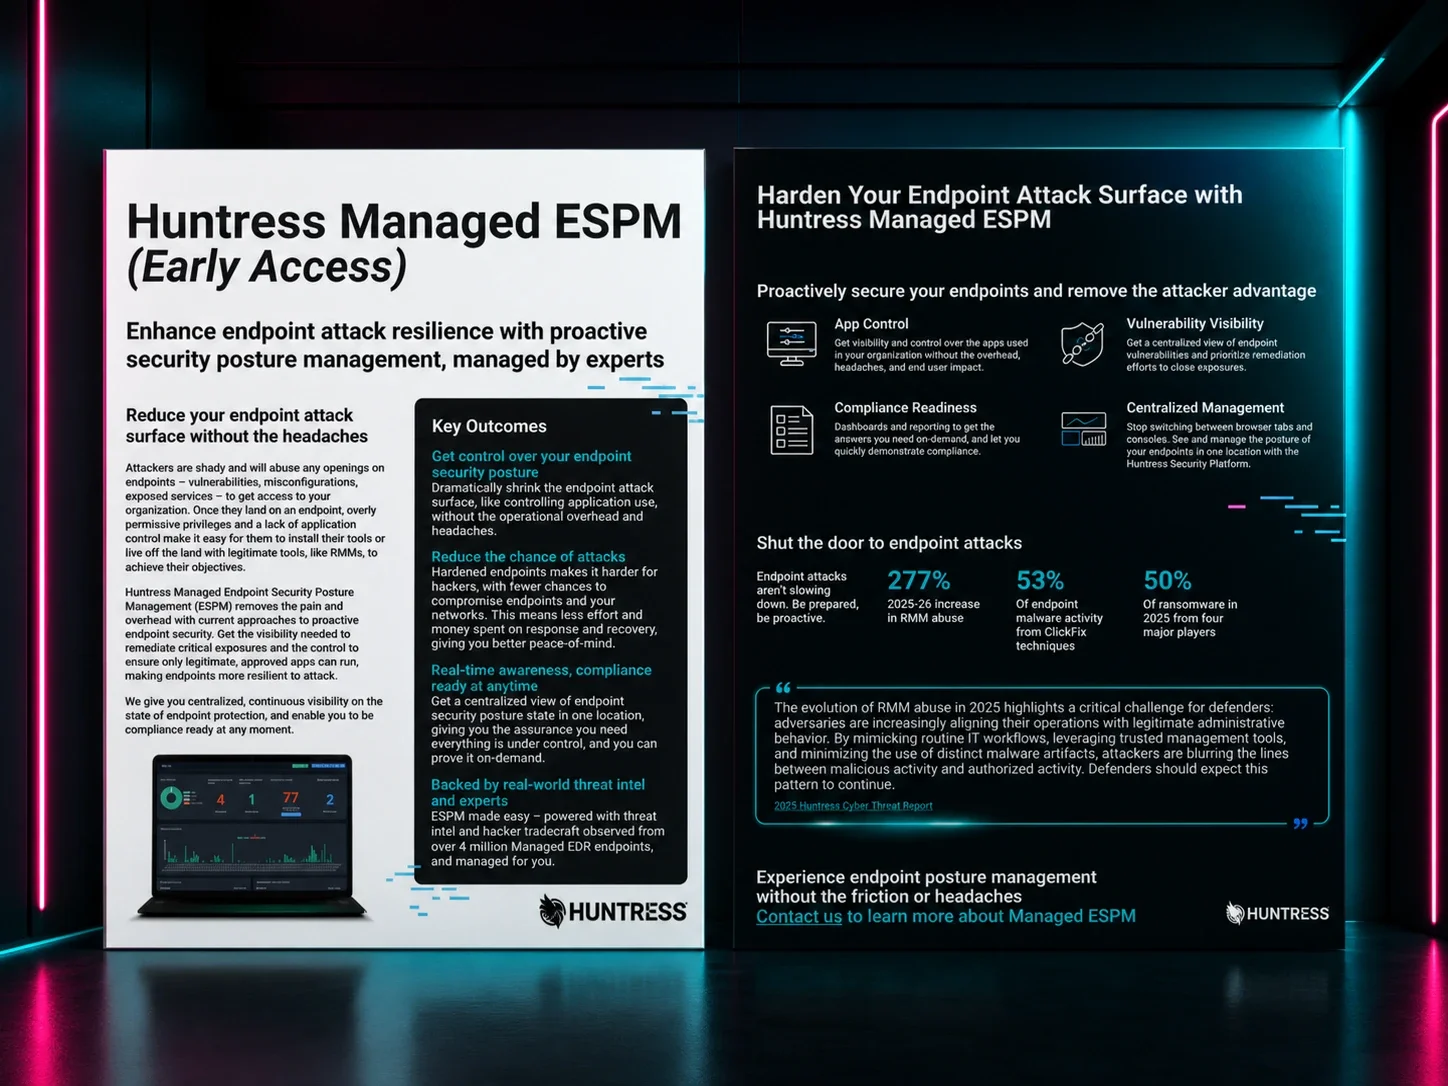
Proactive security to harden endpoints and defend against attacks like ransomware and infostealers, and prevent breaches.
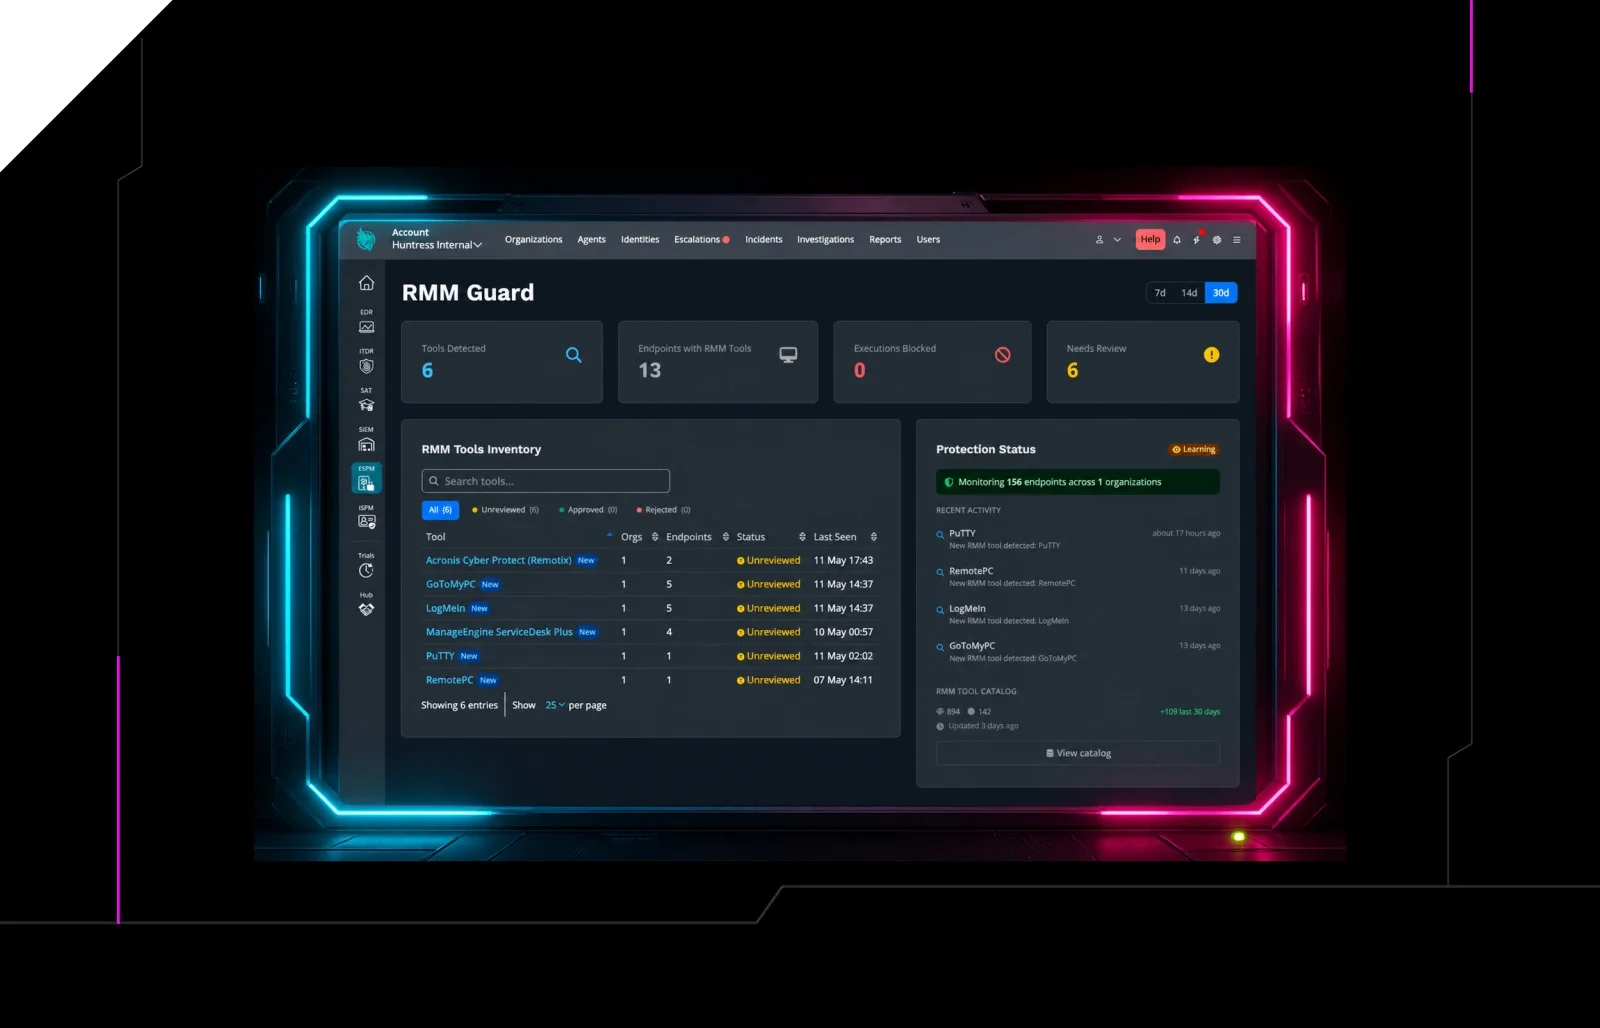
App control works, but most solutions are built for enterprise budgets and headcount. See how Huntress Managed ESPM makes proactive endpoint hardening accessible for MSPs and small IT teams.
Are hackers hiding in your network? Download our Persistence Knowledge Kit to access a collection of resources to help you learn about persistence and why it’s a hacker favorite.
Picking the right EDR solution just got easier. Here is your all-encompassing guide to EDR that suits your needs.
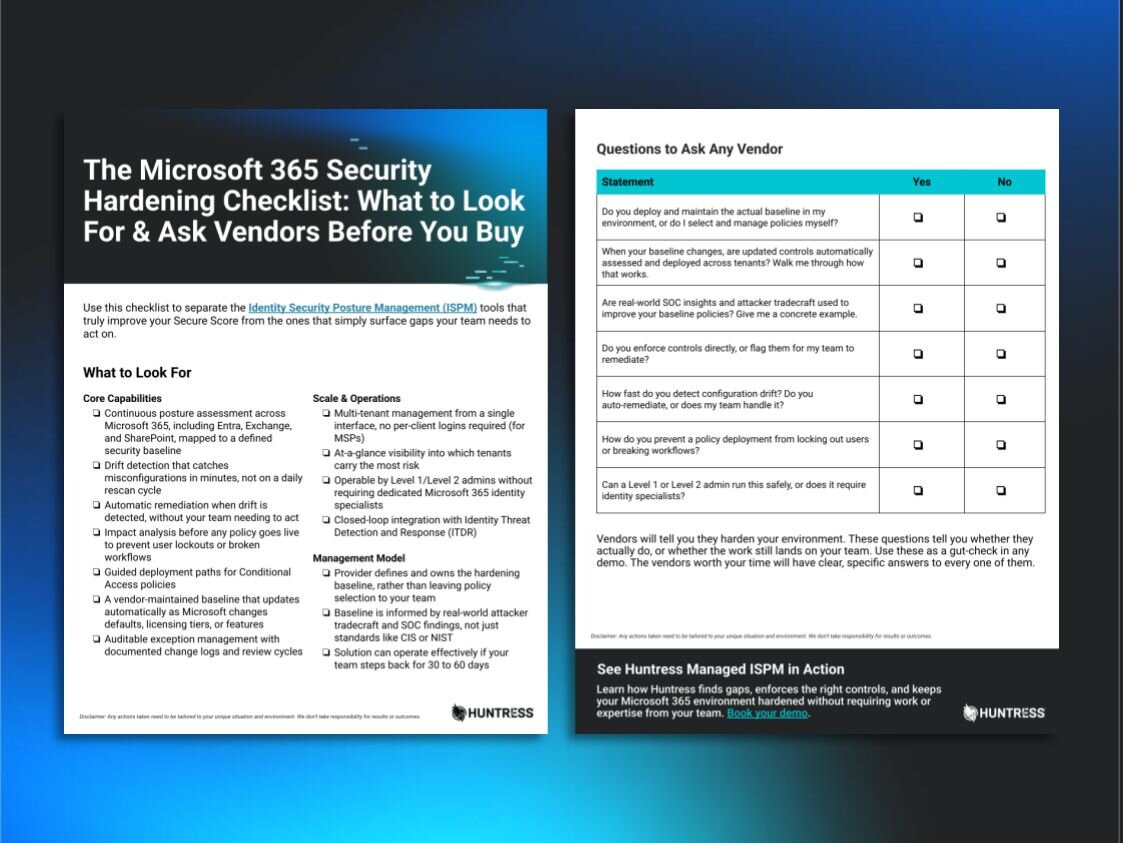
Close gaps, don't just find them. Before you invest in another tool that only surfaces problems, download this checklist to cut through the vendor noise. Discover the core capabilities, ideal management model, and critical questions you need to ask to find an Identity Security Posture Management (ISPM) solution that automatically enforces controls and hardens your Microsoft 365 environment.
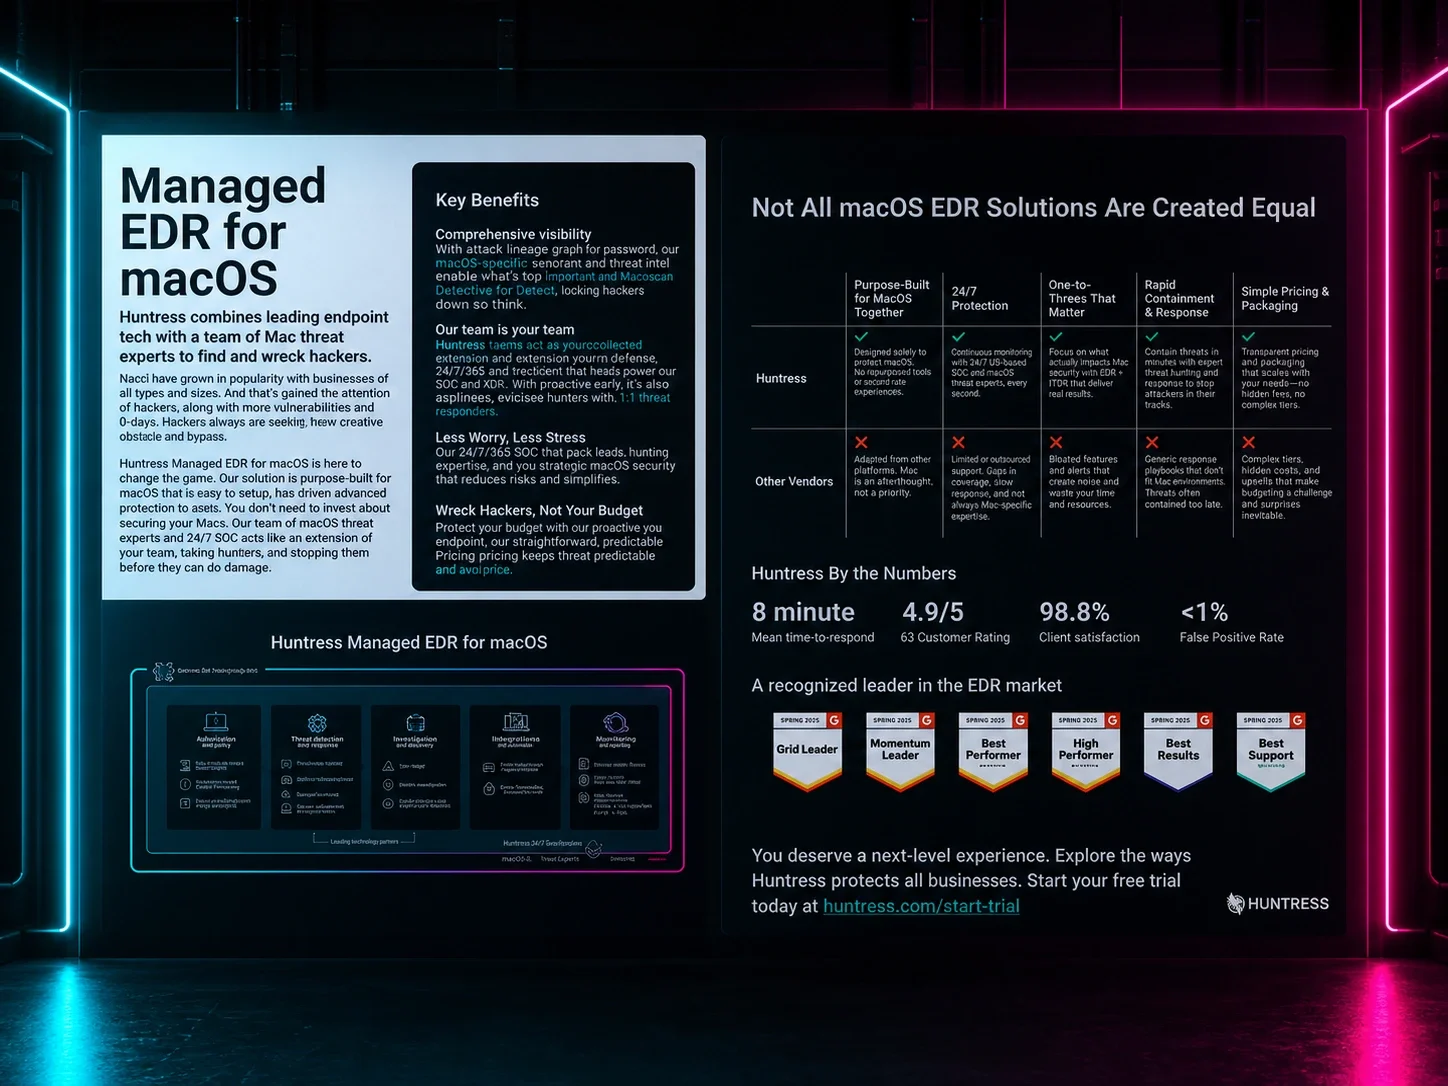
Explore Huntress' guide on how to achieve next-level threat protection from today’s emerging threats for your macOS endpoints.
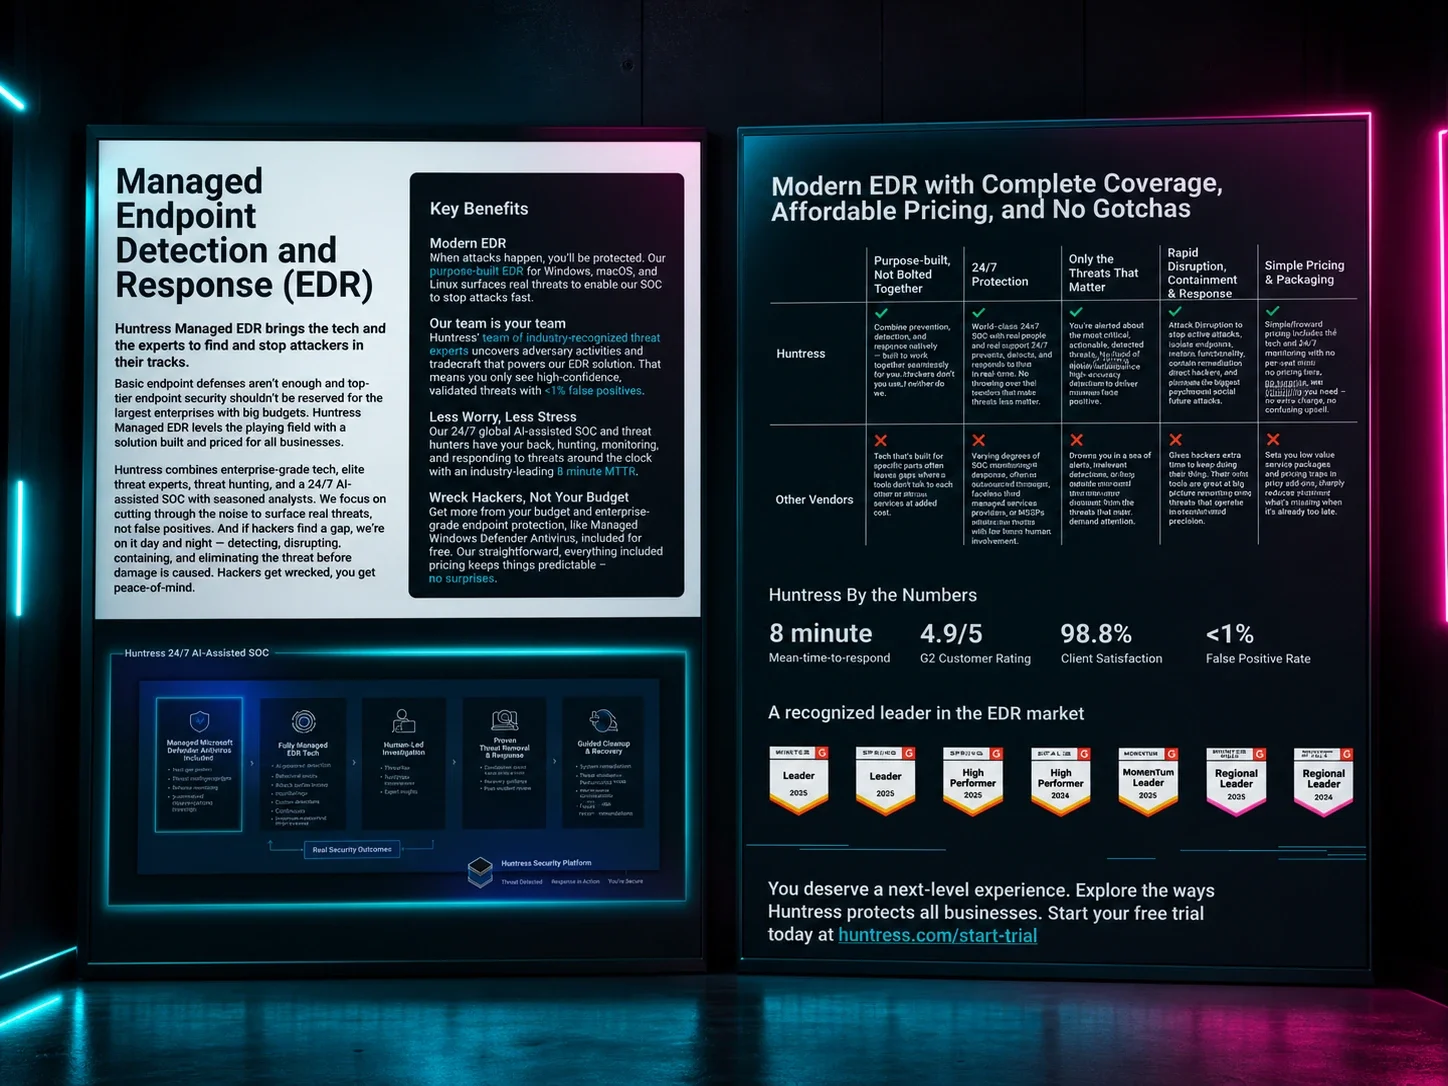
Huntress Managed EDR provides fully-managed, enterprise-grade endpoint protection that’s backed by our team of industry-recognized threat experts and the global 24/7 Huntress SOC.
