
Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
Welcome to the Huntress Cybersecurity Blog, where we cut through the noise with real-world tradecraft to help you stay ahead of today’s threat actors. Our authors bring diverse backgrounds and hands-on experience to make cybersecurity education engaging, accessible, and grounded in the threats you actually face.
Threat Research is where the Huntress SOC shows its work. We cover real intrusion investigations, malware and ransomware analysis, threat actor profiles, and the tradecraft attackers lean on: persistence, defense evasion, and living-off-the-land techniques. Whether it broke this week or has been around for years, this is where you see how attacks unfold and how we stop them.
No posts found.
When a vulnerability starts getting exploited, the clock starts. Rapid Response & Vulnerabilities covers CVE disclosures, vulnerability advisories, the exploitation activity we see in the wild, patch guidance, and disclosure timelines. Timely, focused, and built around what to do next.
No posts found.
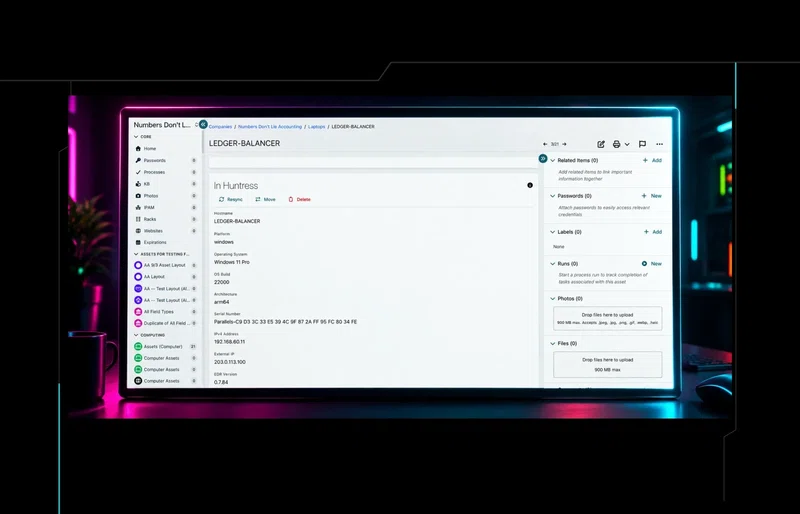
Hudu's new Huntress integration brings your Huntress organizations, agents, memberships, and identities into Hudu. See what it does, how to set it up, and how Hudu built it on the Huntress API.
A $30 AI toy dog led Mastercard to 250+ scam sites. See how small charges and ransomware payouts follow the same money trail, and how to cut it off.
SIEM isn't dead... its bloated pricing model is. Discover why legacy models need to go, how AI fits in, and how to build a smarter, cost-effective security logging strategy.
Attackers abuse legitimate MDM platforms to deploy rogue RMM tools, turning device management into a pathway for remote access and persistence.
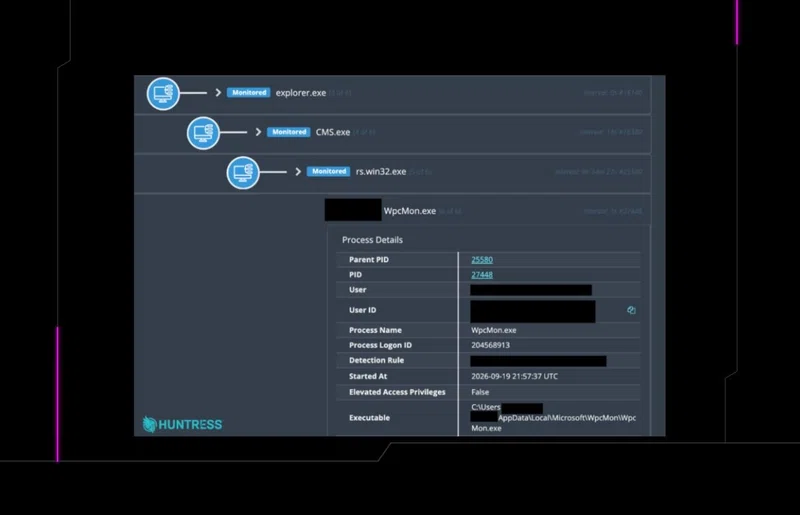
Attackers compromised camera management software to deploy malware, establish persistence, and beacon to C2. Huntress breaks down the attack chain and IOCs.
Microsoft says an AI agent drove the ConnectWise attack. Huntress telemetry is consistent with that: scripted tooling, steered by an operator.