

Ebook
The AI-Powered Adversary
Learn how today’s AI-powered adversary weaponizes phishing and social engineering with real incidents Huntress has investigated. Get the download.
It seems like a new infostealer variant hits the market and starts stealing people’s info every day. Although crypto is one of their biggest targets, it doesn’t stop ‘em from going after everything in sight.
Today’s infostealers are doing more than stealing passwords. They’ll take your VPN configurations, browser autofills, even your AI configurations—anything that’s not nailed down. And it doesn’t stop there; this info is passed on and used for ransomware and other criminal activity ( à la initial access brokers).
If you’ve seen any security news in the last year, you’ll know infostealers have been talked about non-stop. But here’s why we HAVE to talk about ‘em again. We’re exposing the infostealer underground: stolen info at scale, anatomy of a bot, how infostealer logs are packaged, sold, and marketed, threat actor engagement, and initial access brokerage, as well as “malware-as-a-service”.
You’ve heard us talk about infostealers before—but never like this. Don’t miss out.

Related Resources
Learn how today’s AI-powered adversary weaponizes phishing and social engineering with real incidents Huntress has investigated. Get the download.
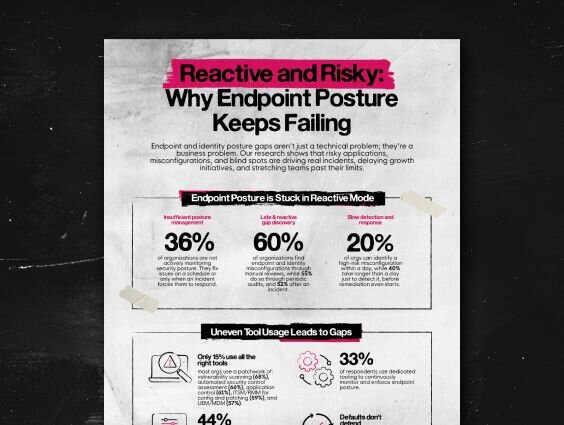
Endpoint security isn't failing because teams lack knowledge. It's failing because manual reviews, periodic audits, and post-incident fixes can't keep pace with the speed and scale of modern threat actors. By the time a misconfiguration surfaces, it's often already been open for too long.
Watch how hackers steal credentials, bypass Microsoft 365 MFA, and completely wreck enterprise systems in under 10 minutes.
[Summary text goes here]
