


Ebook
Picking the right EDR solution just got easier. Here is your all-encompassing guide to EDR that suits your needs.
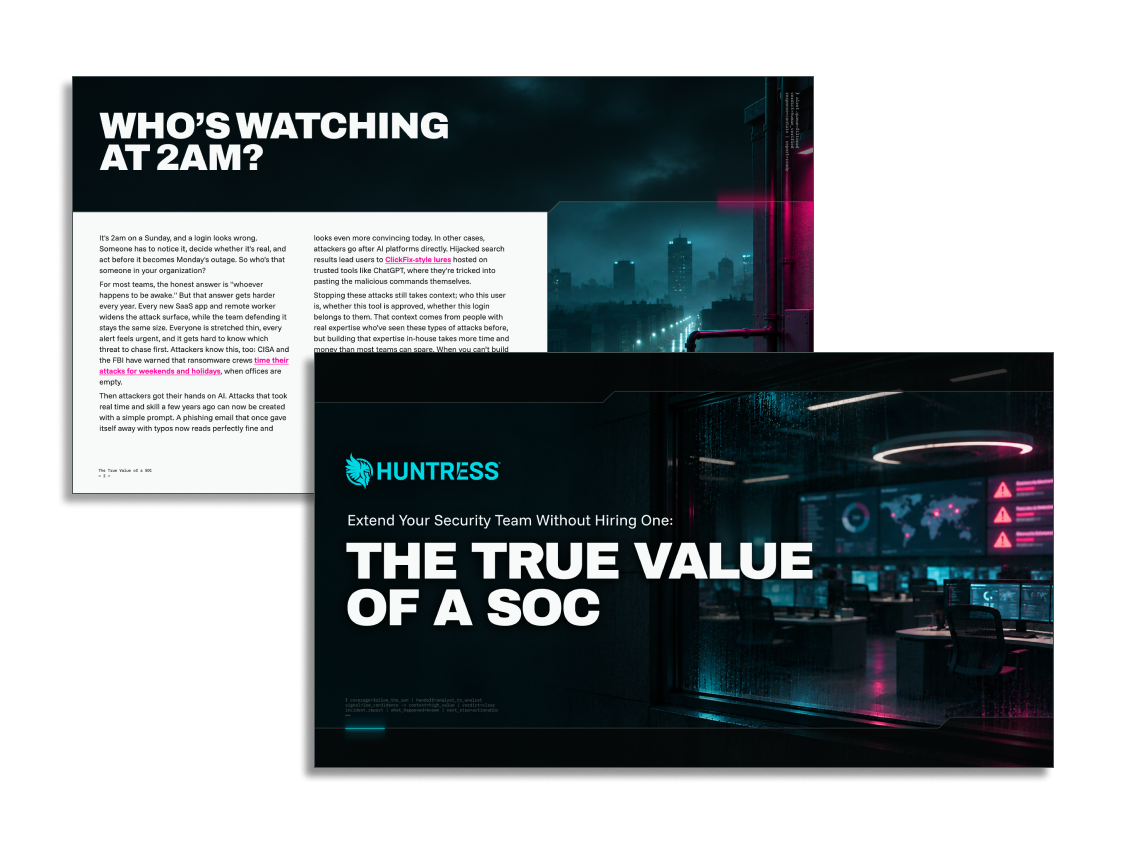
It’s 2am on a Sunday when a suspicious login shows up. Someone has to triage that alert, understand what’s really happening, and decide what to do before it becomes Monday’s outage. In many organizations, that responsibility falls on just a few people who are already stretched thin.
SaaS sprawl and remote work keep expanding the footprint you have to protect, while AI-driven attacks keep adding more to alert queues that are already full. This ebook breaks down how a 24/7, human-led, AI-centric security operations center (SOC) can extend your team with round-the-clock coverage across your endpoints and identities.
Inside, you’ll find:
How limited time, expertise, and headcount put stress on alert queues
What a SOC does to support your organization from detection through response
Key questions to help you find fully managed SOC services versus alert forwarding
Real incidents the Huntress SOC has caught and disrupted
Picking the right EDR solution just got easier. Here is your all-encompassing guide to EDR that suits your needs.
Watch Kyle Hanslovan and other members of the Huntress team dive into the story of Huntress Managed Antivirus.
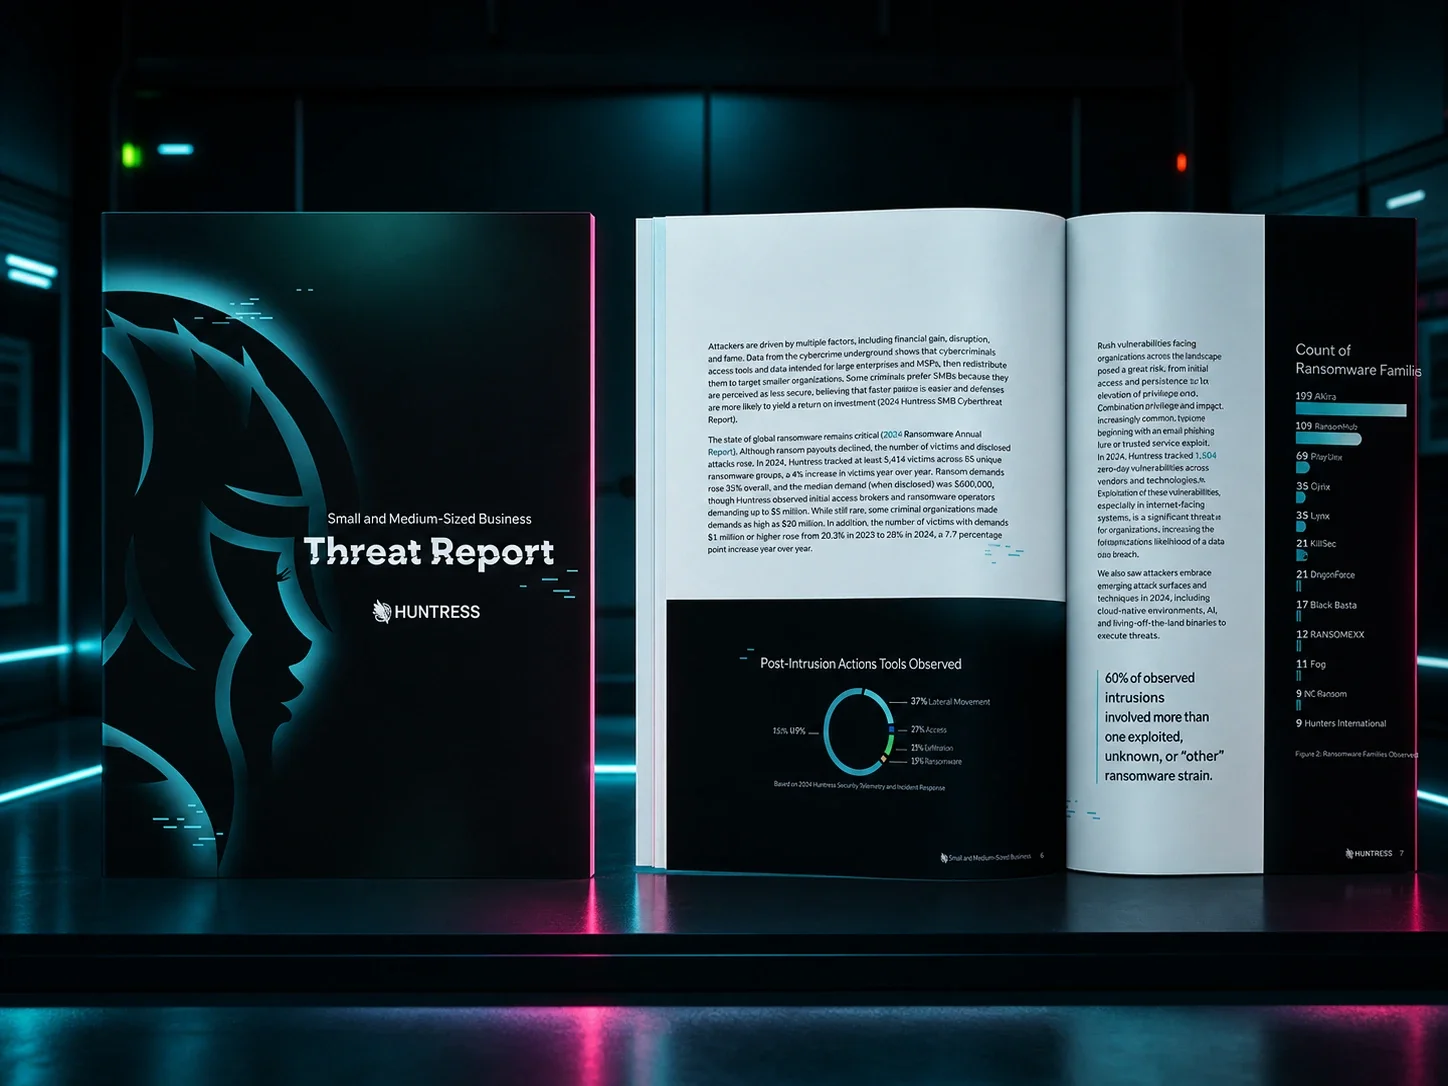
Download Huntress’ SMB Threat Report for insight into the latest adversary trends and behaviors, specifically tailored for SMBs.
